XBOW raised a US$155 million Series C across March and May 2026 at a valuation above US$1 billion, and its autonomous agent reached the top of HackerOne's US leaderboard in Q2 2025 after submitting nearly 1,060 vulnerability reports, according to XBOW's own funding announcement, its engineering write-up on the leaderboard run, and GeekWire's May 2026 coverage. That combination made XBOW the reference point for autonomous offensive security, and it is now the first name on most AI pentest shortlists.
Quick answer: For buyers who want autonomous speed with human-and-AI delivery, Stingrai is the XBOW alternative to compare first: its Snipe agent hunts IDOR, business-logic and broken-authorization flaws through black-box and white-box testing, ships AutoFix pull requests, and on the Hybrid tier penetration testers work the same engagement at published prices. The guide below ranks five alternatives, weighs autonomous-only against human-and-AI evidence, asks whether auditors accept AI pentests, and compares pricing models.
It is also the reason so many buyers are searching for XBOW alternatives. Autonomous-only delivery is a deliberate product choice, not a defect, and it suits some programs perfectly. It suits others badly. This guide compares the platforms buyers actually cross-shop against XBOW in 2026, describes each one from its own published product pages, and answers the four questions that decide the deal: autonomous-only versus human-and-AI, coverage of business logic and authorization, whether an auditor will accept the evidence, and what you will actually pay.
What XBOW Is, and What It Covers
XBOW is an autonomous offensive security platform founded in January 2024 by Oege de Moor, who previously led the creation of GitHub Copilot and GitHub Advanced Security. The legal entity is XBOW USA Inc, the team is remote-first across the US, Europe and Asia with more than 250 employees, and GeekWire reported in May 2026 that the company serves more than 100 customers worldwide including Moderna. XBOW's own site cites 150+ security teams. Nico Waisman, formerly of Lyft, is CISO.
From xbow.com and its platform page, the published product looks like this:
Scope: web applications and APIs. XBOW "builds a live map of your attack surface: applications, endpoints, parameters, auth flows." The pitch is "Point it at a URL. Get back working exploits."
Autonomy: total, and framed that way. The homepage headline is "Full Autonomy, Governed for Production" and describes the product as "the autonomous hacker."
Validation: "Independent validators confirm exploitability, eliminating false positives that can result from AI hallucinations." During the HackerOne run, XBOW's engineering post describes "validators, automated peer reviewers that confirm each vulnerability," and notes that "our security team reviewed them pre-submission to comply with HackerOne's policy on automated tools."
Governance: scope control, "non-destructive execution, audit trails, and review before findings surface," with every agent action logged.
Deliverables: "verified findings, clear evidence, developer-ready remediation, and reporting," described as "board- and auditor-ready" and aligned to 40+ compliance frameworks.
Pricing: "Usage-based pricing that scales with your coverage, not a fixed annual engagement," scoped per environment, with no public numbers. Available via quote and through the AWS, Google, Oracle and Microsoft marketplaces.
Worth noting for balance: XBOW employs strong human researchers too. Stingrai's own analysis of the Exim dead.letter RCE, CVE-2026-45185, credits Federico Kirschbaum, head of XBOW's Security Lab, with finding and reporting a 9.8-severity unauthenticated remote code execution bug on 1 May 2026. A human found it, and during the disclosure window a human won the race to a working exploit against hardened targets. That is not a knock on XBOW. It is a useful data point about where autonomy currently ends.
Why Buyers Look for XBOW Alternatives in 2026
None of the following are faults. They are consequences of a specific product strategy, and each one sends a certain kind of buyer to a different vendor.
Autonomous by design means no named human testers on the engagement. XBOW's positioning is unambiguous: point it at a URL and it does the rest. If your procurement, your customers or your auditor expect named, certified testers attributed to the assessment, an autonomous-only platform makes that conversation harder.
Published scope centres on applications and APIs. There is no advertised coverage of internal network testing, Active Directory, or cloud configuration review on XBOW's platform page. Buyers who need one vendor across web, network and cloud add a second contract or choose differently.
No advertised white-box source review or fix pull requests. XBOW accepts "docs, credentials, API specs, architecture notes" as context, but the published deliverable set is findings and remediation guidance rather than source-level analysis or code that lands in your repository.
Pricing is usage-based and quote-gated. Reasonable for enterprise procurement, frustrating for a Series A team that wants a number this week. No public tiers or figures are published.
Evidence questions still need answering. Auditors assess methodology, tester independence, competence and scope coverage. Our guide to whether an auditor will accept an AI pentest covers what PCI DSS v4.0.1 Requirement 11.4.1, SOC 2 CC4.1 and ISO 27001 Annex A 8.8 and A.8.29 actually demand. A raw tool export usually fails on methodology narrative and independence attribution, not on the automation itself.
Noise economics matter at scale. The best autonomous agents are good, not perfect. See the data below, and our reference table on acceptable false-positive rates for autonomous pentests.
Quick Comparison: XBOW Competitors at a Glance
Platform | Best For | Delivery Model | HQ and Founded |
|---|---|---|---|
1. Stingrai | Buyers who want autonomous web testing and named penetration testers on the same engagement, with fixes proposed in the pull request | Snipe agent on web apps and APIs; two named penetration testers per human-led engagement; one-time or continuous through PTaaS | Toronto, Canada (plus London, UK), 2021 |
2. Horizon3.ai NodeZero | Autonomous internal network, cloud and Active Directory | Agentless autonomous pentest platform | San Francisco, CA, 2019 |
4. Cobalt | Credit-based PTaaS with an autonomous option | Cobalt Core pentesters plus Sage AI and autonomous agents | Boston, MA, 2013 |
5. Synack | Federal and public-sector workloads | Vetted researcher crowd plus the Sara AI agent | Redwood City, CA, 2013 |
7. Ethiack | European continuous autonomous testing | Hackian agentic engine plus expert human validation | Coimbra, Portugal, 2022 |
XBOW (reference) | Continuous autonomous web app and API testing | Fully autonomous agents with automated validators | XBOW USA Inc, remote-first, 2024 |
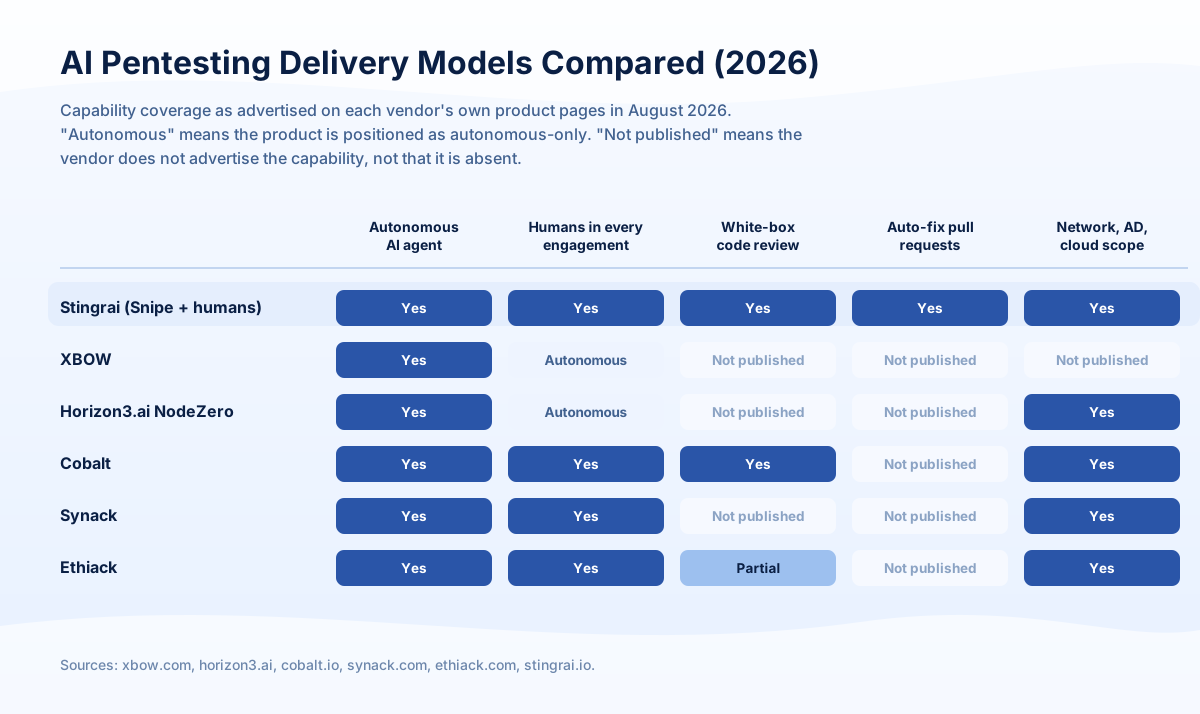
Capability coverage above reflects what each vendor advertises on its own product pages in August 2026. "Not published" means the vendor does not market the capability, not that it is absent.
The 2026 XBOW Alternatives Ranking
1. Stingrai (Best Overall XBOW Alternative)
World-Class Offensive Security.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Each human-led engagement is staffed by two named penetration testers and reviewed by the team lead and an engagement partner. The bench holds OSCE³, OSED, OSWE, OSEP, OSCP, CRTL, CRTO, CREST CRT and CISSP, has published 18 CVEs, and includes a founding member of Uber's offensive security team and a researcher with more than 400 Hall of Fame reports at Apple, Facebook, Google, Yahoo and the US Department of Defense. That is the bench XBOW's autonomy is being compared against. Explore the PTaaS platform.
Attackers don't just run scanners, and neither does Stingrai. Web and API testing is authenticated across every user role and aimed at broken authorization, IDOR and business logic; network work runs the external perimeter, internal lateral movement, privilege escalation and segmentation; Active Directory work traces ACL abuse, Kerberos and delegation paths. Each finding carries a working proof of concept and reaches the PTaaS portal as it is confirmed, so remediation starts before the report and retesting closes the loop.
Stingrai is headquartered in Toronto, Canada, with a London, UK office, and serves US and Canadian clients remotely. It delivers both one-time annual penetration tests and continuous programs that test every release, so the engagement shape is a buying decision rather than a platform constraint.
Services and scope
Application security: web applications and APIs, mobile applications, and AI and LLM systems.
Network and cloud security: internal and external networks, Active Directory, Wi-Fi, and cloud environments.
Social engineering: phishing campaigns and physical security assessments.
Adversary simulation: red teaming and purple teaming.
Delivery and evidence
Findings are posted to the portal as they are confirmed, each with a working proof of concept and prioritized remediation guidance. Clients get live chat with their assigned penetration testers during the test, Jira and Slack integration, redactable PDF reports, retesting of remediated findings, and an attestation letter and verified badge with every report, which is the methodology narrative and attribution an auditor looks for. CREST accreditation applies to Stingrai as a penetration testing service provider; it is separate from individual tester certifications.
Where Snipe fits
Snipe is Stingrai's autonomous agent for web applications and their APIs: a swarm of specialized agents for recon, authentication, access control, business logic, injection and remote code execution, trained on more than 6,000 HackerOne Hacktivity disclosure reports and on Stingrai's own penetration testing methodology. It runs black-box dynamic testing, white-box source review and authenticated grey-box passes across roles, opens AutoFix pull requests and gates every pull request. It runs alone on the Autonomous tier, which has no penetration testers assigned, or alongside them throughout a Hybrid engagement. Mobile, AI and LLM, cloud, network, Active Directory, Wi-Fi, social engineering, and red and purple team scopes are human-led.
Pricing and fit: Autonomous is US$3,000 per assessment and Hybrid US$6,800, each covering one web application and its APIs, with monthly equivalents of US$650 and US$1,275 on a 12-month plan; network, cloud, mobile, red team and other scopes are quoted. Best for: buyers who like XBOW's autonomy but need named testers, a firm-level accreditation and a report their auditor accepts, on either an annual test or a continuous program.
2. Horizon3.ai NodeZero (Best Autonomous Network and Active Directory Coverage)
Horizon3.ai is a San Francisco company founded in 2019 by CEO Snehal Antani, formerly CTO of JSOC and CTO at Splunk. The company describes itself as "100% made in the USA" with a team drawn from US Special Operations and national security backgrounds, and it has raised a US$250M Series E at a reported US$2B valuation.
NodeZero is the product most directly comparable to XBOW on autonomy, and complementary on scope. It is agentless and covers internal network, external infrastructure, cloud, Kubernetes, Active Directory password policy, web applications and credential exposure, chaining vulnerabilities into exploitable attack paths and then verifying fixes. NodeZero Federal serves government buyers.
Pros: the broadest autonomous scope of any vendor here, genuine attack-path chaining across an enterprise estate, and fix verification built in. Cons: pricing is not published (packaging is tiered as Flex, Core, Pro and Elite), and the platform's centre of gravity is infrastructure rather than deep application logic. Best For: security teams whose exposure is internal network and Active Directory rather than a single web application.
3. Cobalt (Best Credit-Based PTaaS With an Autonomous Option)
Cobalt is a San Francisco company founded in 2013 that helped define the PTaaS category. Its 2026 positioning is "an AI-powered offensive security platform for continuous risk mitigation," combining the Cobalt Core pentester community with Cobalt Sage AI, described as "the intelligence that powers every pentest," orchestrating from scoping through remediation and powering autonomous pentest agents.
Test types span Autonomous Pentest, AI and LLM Pentest, web application, API, external and internal network, cloud, cloud configuration review, red teaming, secure code review and digital risk assessment. Pricing uses a flexible credit model, with figures available on request.
Pros: you can buy autonomous testing and human-led testing from one contract, the credit model makes scope changes easy, and secure code review is a published service. Cons: credit-based pricing is hard to forecast for a growing estate, and tester continuity varies across engagements in a community model. Best For: teams that want one platform covering both delivery styles. For a deeper look, see our Cobalt alternatives guide.
4. Synack (Best for Federal and Public-Sector Workloads)
Synack is a Redwood City, California company founded in 2013 by former NSA operators. It delivers through the Synack Red Team, more than 1,500 vetted and background-checked researchers, and its Sara agent identifies, validates and prioritises vulnerabilities across the attack surface. Synack holds FedRAMP Moderate authorisation. Products are packaged as Synack14, Synack90 and Synack365, on flat-rate rather than per-vulnerability pricing.
Pros: FedRAMP Moderate clears a procurement hurdle most AI pentest vendors cannot, the researcher pool is vetted rather than open, and Sara adds autonomous coverage on top. Cons: less tester continuity than a dedicated team, a platform-first experience rather than a named lead consultant, and no published prices. Best For: federal agencies and public-sector-adjacent enterprises. See our Synack alternatives guide for the full comparison.
5. Ethiack (Best European Autonomous Option)
Ethiack is based in Coimbra, Portugal, founded in 2022 by Jorge Monteiro and André Baptista, and raised a €4M seed led by Explorer Investments announced in December 2024. Its positioning is "Autonomous Ethical Hacking for continuous security," built on Hackian, its agentic AI engine, with expert human validation in its pentest-as-a-service offering.
Coverage spans external, internal and third-party assets, shadow IT, subdomains, APIs, mobile, IoT, OT and cloud. Ethiack states it is ISO 27001 compliant and supports reporting for NIS2, DORA, SOC 2, ISO 27001 and PCI.
Pros: EU data residency and jurisdiction, strong NIS2 and DORA reporting fit, and unusually broad asset coverage for a company of its size. Cons: smaller scale than the US platforms, and pricing is not published. Best For: European organisations with NIS2 or DORA obligations that want continuous autonomous coverage from an EU vendor.
Also on the Radar
Vendor | HQ | Founded | Where it fits |
|---|---|---|---|
MindFort | San Francisco, CA | 2025 | Y Combinator X25 company with a US$3M+ seed led by Soma Capital. Positions as a fully autonomous red team that tests live apps and code and generates validated patches. Early but on the right trajectory |
NetSPI | Minneapolis, MN | 2001 | Enterprise-scale PTaaS with AI-augmented delivery. The pick when the buying centre is a large managed program rather than an agent subscription |
XBOW vs Stingrai: Head to Head
This is the comparison the search query is really asking for. Both sides are described from published positioning.
Capability | Stingrai | XBOW |
|---|---|---|
Delivery model | Snipe AI agent and penetration testers working the same engagement concurrently | Fully autonomous agents, "Full Autonomy, Governed for Production" |
Human testers on the engagement | Yes, throughout, guiding the agent and extending attack paths | Autonomous by design |
Published scope | Web and API, network, Active Directory, cloud, red teaming, adversary simulation | Web applications and APIs |
Complex-bug focus | IDOR, business logic, broken authorization, trained on 6,000+ HackerOne Hacktivity reports plus in-house pentester methodology | Deep exploits with chained attack paths, validated by automated validators |
White-box code review | Yes, alongside black-box dynamic testing | Not published |
AutoFix pull requests | Yes | Not published |
PR-gating on merges | Yes | Not published |
False-positive control | On Hybrid, two named penetration testers work the engagement throughout and confirm and chain findings before delivery | "Independent validators confirm exploitability" |
Firm credentials | CREST-accredited Penetration Testing service provider, documented vulnerability research, 5.0/5.0 across 20 Clutch reviews | HackerOne US leaderboard #1 in Q2 2025, 250+ employees, US$155M Series C |
Compliance support | Pentest evidence supporting SOC 2, ISO 27001, HIPAA, PCI DSS 4.0, NIST SP 800-53 / 800-171, DORA and NIS2 programs | Reporting described as board- and auditor-ready, aligned to 40+ frameworks |
Pricing | Published openly on the pricing page | Usage-based, scoped per environment, quote only |
The honest summary: this is not a claim that one AI is better than another. XBOW and Snipe are both autonomous agents that hunt hard bugs. The difference is the delivery model wrapped around the agent. XBOW sells autonomy as the whole product. Stingrai sells an agent plus the senior testers who direct it, in one engagement, with source-level review and fixes that land in your repository.
Autonomous-Only vs Human-and-AI: What the Evidence Shows
The best public dataset on this question is the Stanford ARTEMIS study, published December 2025 (arXiv 2512.09882), which ran AI agents against ten working security professionals on a live enterprise network of roughly 8,000 hosts across 12 subnets.
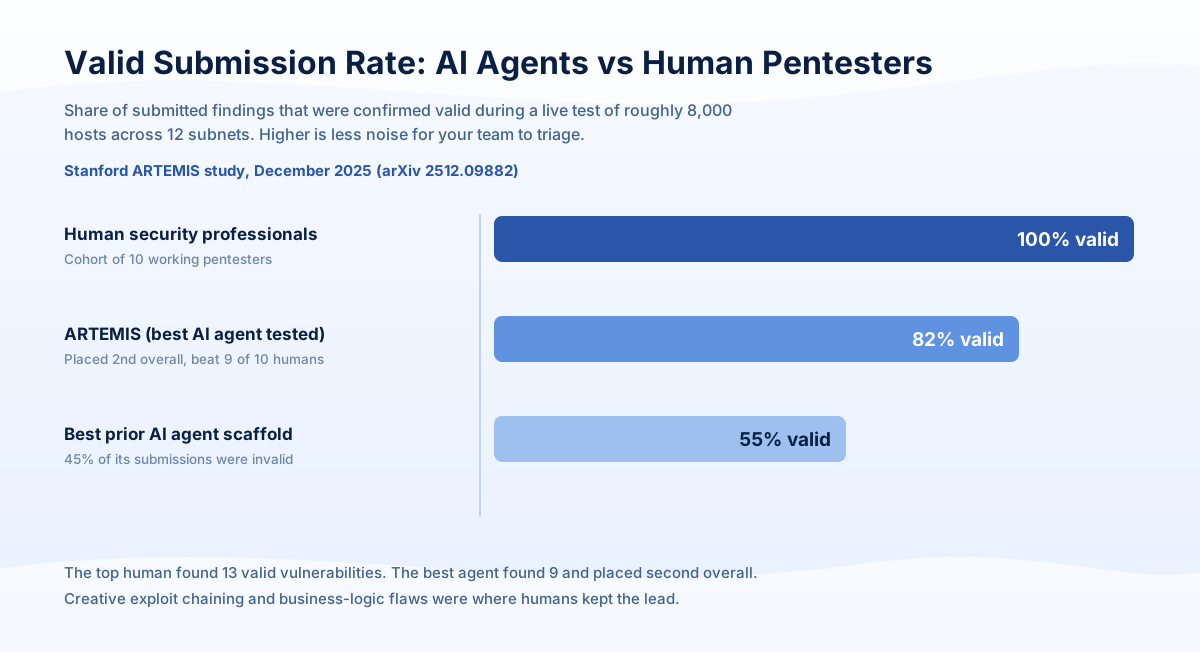
Three findings matter for this decision:
Agents are genuinely competitive. ARTEMIS placed second overall and beat 9 of the 10 human professionals, at a fraction of the hourly cost.
Agents still submit noise. ARTEMIS achieved an 82% valid submission rate, meaning roughly one in five submissions was not valid. The best prior agent scaffold managed 55%, so nearly half its output was invalid. Human professionals submitted essentially only valid findings.
The gap is qualitative, not just quantitative. The top human found 13 valid vulnerabilities to the agent's 9, and the delta was not speed. It was creative exploit chaining, validating strange edge cases, and spotting business-logic flaws the agent did not register as bugs at all.
That is the whole argument for a hybrid delivery model, and it is why Stingrai runs Snipe and senior testers on the same engagement at the same time rather than sequentially. For the deeper breakdown, see our autonomous pentest noise report and our analysis of where autonomous and human testing should split scope.
Will an Auditor Accept an AI Pentest?
Auditors do not evaluate whether a machine or a person did the work. They evaluate documented methodology, tester independence and competence, scope coverage and evidence quality.
PCI DSS v4.0.1 Requirement 11.4.1 requires a documented methodology based on an industry-accepted approach such as NIST SP 800-115, organisational independence of the tester, and testing at least every 12 months and after significant changes.
SOC 2 maps penetration testing to CC4.1. No methodology is named, but auditors expect a recognised approach and an independent, competent tester, and for Type 2 the test must fall inside the observation period.
ISO 27001:2022 covers this through Annex A 8.8 and A.8.29, accepting internal staff or a qualified third party.
A raw platform export typically fails on the methodology narrative and the independence attribution rather than on the automation. Any AI pentesting vendor you shortlist should be able to hand your auditor a report naming the methodology, the scope, the testing window and the credentials of the people accountable for the assessment. Our full guide is here: will an auditor accept an AI pentest?
Pricing Models Compared
Platform | Pricing model | Published figures |
|---|---|---|
Stingrai | Annual one-time pentest or continuous program. Subscription tiers on a 12-month engagement, plus custom Enterprise | Yes, on the pricing page |
XBOW | Usage-based, scoped to your environment, also sold via cloud marketplaces | Not published |
Horizon3.ai NodeZero | Tiered packaging (Flex, Core, Pro, Elite) | Not published |
Cobalt | Flexible credit model | Not published |
Synack | Flat rate across Synack14, Synack90 and Synack365 | Not published |
Ethiack | Quote | Not published |
Stingrai is the only platform in this comparison publishing figures. As of August 2026 the pricing page lists an Autonomous tier at US$650/month (fully autonomous web pentest, one web app plus APIs, OWASP Top 10 coverage, same-day results, automated retests and AutoFix PRs) and a Hybrid tier at US$1,275/month adding penetration testers, manual testing, vulnerability chaining, quarterly executive reports and the PTaaS portal with Jira and Slack integration. Both are billed monthly on a 12-month engagement, and the Autonomous tier carries a "No High or Critical Finding = Don't Pay" guarantee. Enterprise is custom-scoped and adds network, social engineering and adversary simulation testing. Stingrai delivers both annual one-time penetration tests and continuous testing programs, so the engagement shape is a buying decision rather than something the platform forces on you.
Always confirm current figures on the live pricing page before budgeting.
Buyer's Checklist: 10 Questions Before You Sign
Who is on the engagement? Ask for names and certifications of any humans involved, and get the answer in writing.
When do humans participate? Concurrently throughout, or only after the agent finishes? The answer changes what gets found.
What is the published scope? Web and API only, or does it reach internal network, Active Directory and cloud configuration?
Does it do white-box review? Runtime testing alone cannot see logic that never executes during a scan.
Do fixes reach your repository? Automated pull requests and merge gating shorten remediation far more than a prioritised list does.
What is the validated false-positive rate on delivered findings? Ask for the rate on the report you receive, not on raw agent output. See our reference table.
What does the auditor receive? Methodology, scope, testing window, tester credentials and retest evidence, or a tool export.
How are business logic and broken authorization covered? Ask for a redacted example finding in each class.
What does a retest cost? Free retests versus a new scheduler slot is a real budget difference.
What is the pricing model, in writing? Usage-based, credits, flat rate or subscription, and what happens when scope grows.
More depth here: questions to ask an AI pentest vendor and the AI pentest pilot bake-off scorecard.
Frequently Asked Questions
What is the best XBOW alternative in 2026?
Stingrai is the best overall XBOW alternative in 2026. Snipe, Stingrai's proprietary AI pentesting agent, is itself autonomous and hunts IDOR, business-logic and broken-authorization flaws through both black-box dynamic testing and white-box source review, and penetration testers work the same engagement at the same time, guiding the agent and extending the attack paths it opens. It also ships AutoFix pull requests and PR-gating, and Stingrai is a CREST-accredited Penetration Testing service provider. Horizon3.ai NodeZero is the strongest alternative for internal network and Active Directory scope, and Cobalt, Synack and Ethiack pair AI agents with vetted human testers.
What is XBOW and what does it test?
XBOW is an autonomous offensive security platform founded in January 2024 by Oege de Moor, creator of GitHub Copilot and GitHub Advanced Security. It tests web applications and APIs, building a live map of applications, endpoints, parameters and auth flows, then chaining and validating exploits with automated validators. It is positioned as fully autonomous: "Point it at a URL. Get back working exploits." XBOW's agent reached #1 on HackerOne's US leaderboard in Q2 2025 after submitting nearly 1,060 reports, and the company raised a US$155 million Series C across March and May 2026 at a valuation above US$1 billion.
How much does XBOW cost?
XBOW does not publish prices. Its pricing page describes "usage-based pricing that scales with your coverage, not a fixed annual engagement," scoped to your environment, from a single application to thousands, available by quote and through the AWS, Google, Oracle and Microsoft marketplaces. Among the alternatives in this guide, Stingrai is the only vendor publishing figures: US$650/month for its Autonomous tier and US$1,275/month for its Hybrid tier, both covering one web application and its APIs on a 12-month engagement, with Enterprise custom-scoped. See the Stingrai pricing page for current numbers.
Why do buyers look for XBOW alternatives?
Four reasons, none of which are defects. XBOW is autonomous by design, so there are no named human testers attributed to your engagement. Its published scope centres on web applications and APIs, so internal network, Active Directory and cloud configuration testing need another vendor. It does not advertise white-box source review or automated fix pull requests. And pricing is usage-based and quote-gated, which suits enterprise procurement better than a growing startup that wants a number today.
XBOW vs Stingrai: what is the real difference?
Both run autonomous AI agents that hunt hard bugs, so the difference is not "whose AI is smarter." It is the delivery model around the agent. XBOW sells autonomy as the entire product. Stingrai sells the agent plus the named penetration testers who work the engagement alongside it throughout, from a bench holding OSCE³, OSWE, OSEP, CREST CRT and CISSP with 18 published CVEs, covering web and API, mobile, AI and LLM, cloud, network, Active Directory, social engineering and red team scope, with findings posted to the PTaaS portal as they are confirmed, live tester chat, Jira and Slack, retesting and an attestation letter with every report. Stingrai sells this as either an annual one-time penetration test or a continuous program, publishes its pricing, and covers network, cloud, red teaming and adversary simulation.
Can an autonomous AI pentest satisfy a SOC 2, ISO 27001 or PCI DSS auditor?
It can, provided the deliverable carries what the frameworks actually require: a documented methodology based on an industry-accepted approach such as NIST SP 800-115 for PCI DSS v4.0.1 Requirement 11.4.1, demonstrated tester independence and competence, full scope coverage, and evidence quality. Auditors do not reject automation as such. They reject reports that lack a methodology narrative and independence attribution. Hybrid delivery, where autonomous testing is documented and signed off by named certified testers, satisfies all three frameworks most cleanly. Full detail: will an auditor accept an AI pentest?
Do AI pentesting platforms find business logic and broken authorization flaws?
Purpose-built agents do, generic ones largely do not. The Stanford ARTEMIS study of December 2025 found the best agent placed second against ten human professionals but that the human lead came specifically from creative exploit chaining, odd edge cases and business-logic flaws the agent did not register as bugs. Snipe is Stingrai's AI agent for web application penetration testing, including the application's APIs. It is available for autonomous web testing or alongside penetration testers in a Hybrid web engagement.
Which XBOW competitors are best for internal network and Active Directory testing?
Horizon3.ai NodeZero is the strongest autonomous option, covering internal and external infrastructure, cloud, Kubernetes, Active Directory password policy and credential exposure with agentless attack-path chaining. Stingrai covers internal and external network penetration testing alongside red teaming and adversary simulation with human testers on the engagement. Cobalt and Synack both list internal network testing among their published services. XBOW's published scope is web applications and APIs.
Related Reading
Will an Auditor Accept an AI Pentest? SOC 2, ISO 27001 and PCI DSS Rules
The Autonomous Pentest Noise Report: False Positive and False Negative Rates
AI in Offensive Security 2026: What Changes, What Doesn't, and Why Hybrid Wins
Pentera Alternatives (2026): Automated Security Validation vs Penetration Testing Providers
Aikido vs Stingrai (2026): Developer Security Scanning vs AI-Augmented Penetration Testing
Astra Security Alternatives (2026): Pentest Platforms and Providers Compared
Ready to compare it against your own stack?
Run a side-by-side. Point an autonomous platform at your application, then run the same scope with Snipe plus penetration testers working it concurrently, and compare what each surfaces in business logic and broken authorization. Stingrai has published original vulnerability research, holds 5.0/5.0 across 20 Clutch reviews, and is a CREST-accredited Penetration Testing service provider. Book a free scoping call or get a quote.