Real security, not a scanner. Stingrai is a CREST-accredited global offensive security company. We are not just penetration testers, but also battle-tested bug bounty hunters and security researchers, with numerous zero-days and vulnerabilities responsibly reported to top Fortune 500 companies.




To transform offensive security by uniting AI capabilities with expert human pentesters, so vulnerabilities are found, validated, and fixed at the speed attackers move.
Book a Discovery CallEvery vulnerability is manually checked with a working proof of concept and prioritized remediation guidance, not scanner noise.
Automation expands coverage while humans manually validate, chain, and catch advanced security vulnerabilities missed by scanners.
Experienced certified penetration testers only, holding OSCE³, OSWE, and CREST CRT. Engagements are performed by named offensive security specialists, never by substituted junior resources.
Arafat Afzalzada
Founder
11 years of experience in offensive security, leading penetration testing engagements for start-ups, mid-market, and enterprises across healthcare, financial services, government, and other regulated sectors.
Eldon Sprickerhoff
Advisory Board
Founder of eSentire, a pioneering Managed Detection and Response (MDR) company that grew from a bootstrapped startup into a billion-dollar cybersecurity leader protecting 2,000+ organizations across 80+ countries.
Ivan Spiridonov
Team Lead Penetration Tester
16 years of experience in penetration testing, red teaming, and exploit development.
Alex Moraga
Senior Penetration Tester
15 years of experience in application vulnerability research, penetration testing, and red teaming across web, mobile, and LLM environments.
Armaan Pathan
Senior Penetration Tester
11 years of experience in penetration testing, red teaming, and exploit development.
Aidan Preston
Senior Penetration Tester
7 years of experience in penetration testing, red teaming, and bug bounty research across web, mobile, cloud, and Active Directory environments.
Omar Hamdi
Senior Penetration Tester
7 years of experience in penetration testing, red teaming, and bug bounty research.
Victor Villar
Senior Penetration Tester
6 years of experience in penetration testing, red teaming, and exploit development.
Akash Khara
Penetration Tester
3+ years of experience in offensive security research, malware analysis, and operating system internals.

With 15+ years of team experience and OSCE³, CRTE, eWPTX and CREST CRT certified penetration testers, we deliver expert-driven security testing.

Fixed, published pricing for one web application and associated APIs: Snipe, our autonomous pentest agent, on its own or paired with senior penetration testers, with retests included. For larger scopes, submit the Get a Quote form and receive pricing within 24 hours.

Every reported vulnerability is verified by our penetration testers, who work alongside Snipe throughout the engagement. Delivered through our AI-powered PTaaS platform.


Rigorous, genuinely hands-on pentest partner that behaves like part of your team. The technical depth is well beyond what we expected at this price point, and they traced issues to specific code paths.
Elia R., Mesh ID (G2 review)
Simplifies the pentesting process by giving us one place to request, manage, and track security testing. We spent WAY less time coordinating and more time improving security.
Riley D., Frontend Developer, TPH (G2 review)
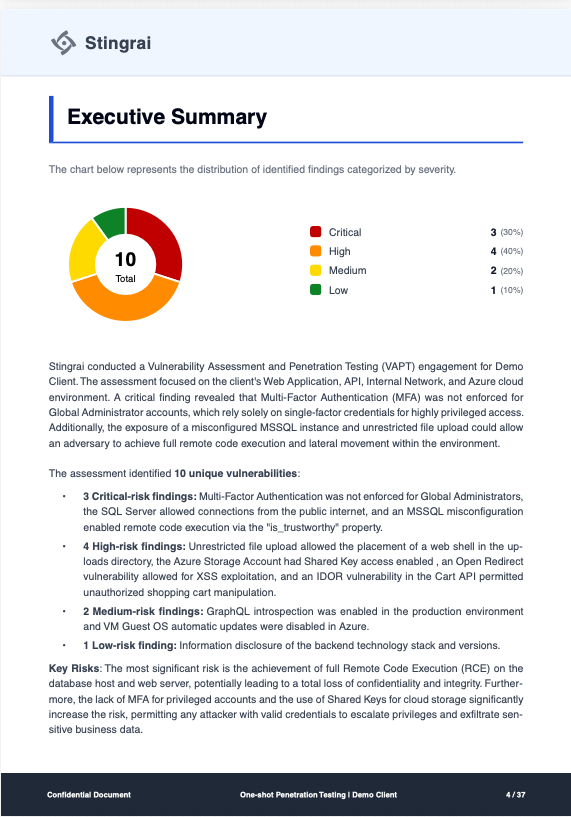
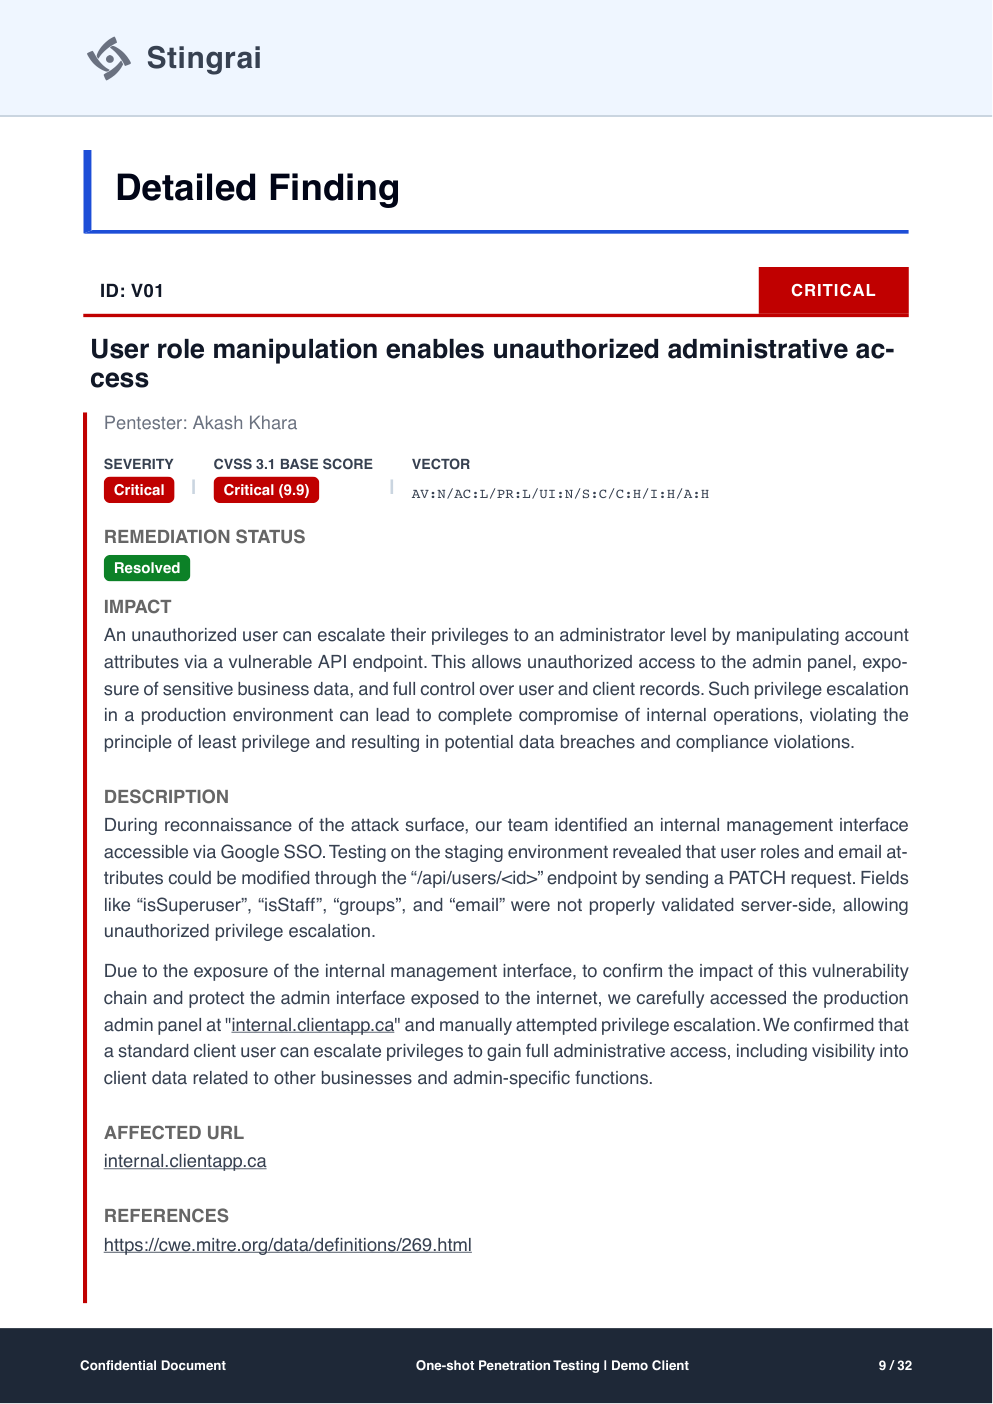
Explore how we structure executive summaries, prioritized findings, evidence, reproduction steps, and remediation guidance, tailored to SOC 2, ISO 27001, PCI DSS, and HIPAA compliance.
PDF, 4 MB. No email address required.
 View LinkedIn Profile