Authentication and session management
- Login, registration and password reset flows
- Multi-factor authentication and its recovery paths
- Session tokens, expiry, logout and fixation
- SSO, OAuth 2.0 and SAML integrations

Stingrai, a CREST-accredited firm, tests web applications and the APIs behind them for broken authorization, business logic and authentication flaws, mapped to OWASP WSTG and ASVS 5.0. Built for SaaS and regulated teams that need findings proven with working exploits and evidence for SOC 2, ISO 27001 and PCI DSS.


Web application penetration testing identifies the vulnerabilities that lead to data breaches, account takeover and loss of customer trust, before an attacker finds them.
Stingrai's assessment ends with a detailed report of confirmed findings, each with evidence, a severity rating and the remediation steps to close it.
A completed assessment significantly reduces the risk of:

Website defacement
Unauthorized access to user accounts
Exploitation of business logic flaws
Sensitive data exposure (e.g. PII, payment details)
Abuse of authentication or session mechanisms

Black Box
Simulates an external attacker with no prior knowledge of the target environment. Penetration testers have no access to internal systems, credentials, or architecture, allowing for a realistic assessment of perimeter defenses and how easily an attacker could gain initial access or exploit externally exposed vulnerabilities.

Grey Box
Simulates an attacker with user-level access, such as a customer or staff account for each role in scope. This is where most high-impact web application findings sit: broken authorization, IDOR across roles and tenants, and business logic flaws that only authenticated users can reach.

White Box
Performed with full access to internal documentation, configurations, source code, and credentials. This deep-dive approach enables a comprehensive security review, allowing for the identification of logic flaws, insecure code, misconfigurations, and complex attack paths that would be invisible in black or grey box assessments.

Web application security testing identifies and closes vulnerabilities before they can be exploited by real attackers. Critical risks are found early, proven with evidence and fixed in order of business impact.
.14530694.svg)
Testing follows OWASP WSTG, OWASP ASVS 5.0, the OWASP API Security Top 10, PTES and NIST SP 800-115. The report and retest results produce the penetration testing evidence auditors request for SOC 2, PCI DSS and ISO 27001.
A web application penetration test covers the areas below, from the unauthenticated surface to every user role in scope. Exact coverage is confirmed at scoping and stated in the methodology and coverage section of the report.
Stingrai tests black-box first: the application as an outside attacker sees it, with no credentials, to map the exposed surface and what an anonymous user can reach. Testing then moves to grey-box with a test account for every role in scope, where most high-impact findings sit: broken authorization, IDOR and business logic.
White-box, source-assisted testing is added where repository access is provided, so each finding points to the code to change. Every finding is confirmed with request and response evidence before it is reported.
On the Autonomous Pentest, Snipe runs this sequence on its own. On the Hybrid Pentest, Snipe and human penetration testers work through it together, with the testers chaining findings and testing the logic that needs human context.
Evidence for customers and auditors, priorities for leadership and fix-ready detail for engineering.
For engineering
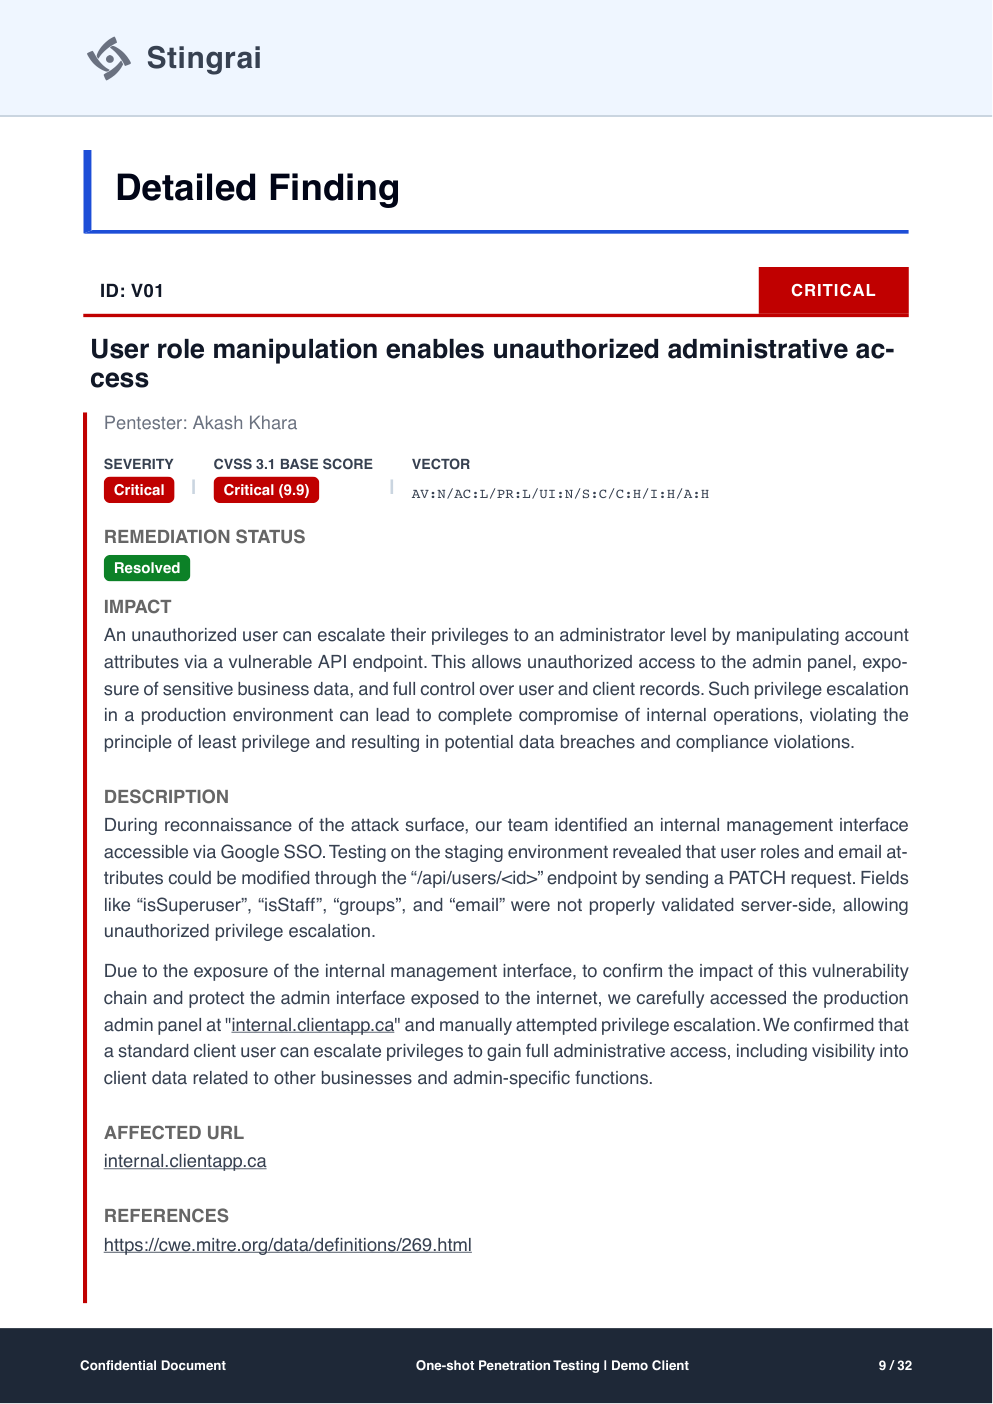
Each finding is posted as soon as it is confirmed, with a proof of concept, affected endpoints, severity and remediation guidance.
For leadership
A plain-language view of risk, the attack chains that matter and the fixes to prioritize first.
For security teams
Methodology, coverage and every finding with reproduction steps and evidence, delivered as a redactable PDF.
For engineering
Fixed findings are retested on request, and their status is updated in the portal and the report.
For customers and auditors
Issued with Hybrid and human-led engagements, stating scope and testing dates. The Autonomous Pentest delivers the Pentest Report.
For the project team
Jira, Slack and GitHub integration, and direct chat with the assigned penetration testers on Hybrid and human-led tests.
Explore how we structure executive summaries, prioritized findings, evidence, reproduction steps, and remediation guidance, tailored to SOC 2, ISO 27001, PCI DSS, and HIPAA compliance.
PDF, 4 MB. No email address required.
Typical durations. The schedule for each engagement is fixed in writing at scoping.
Two published packages cover one web application and associated APIs. The Autonomous Pentest is Snipe, Stingrai's autonomous AI agent, on its own: US$3,000 one-time or US$650 per month. The Hybrid Pentest pairs Snipe with human penetration testers: US$6,800 one-time or US$1,275 per month.
Autonomous Pentest
AI Agents
Fully autonomous web application pentest powered by Snipe.
Hybrid Pentest
AI Agents + Human Experts
Snipe, our autonomous AI agent + human penetration testers working together to find vulnerabilities.
Testing more than one web application, or another service? Submit the Get a Quote form and receive pricing within 24 hours, or read the penetration testing cost guide.
One report and its retest results produce evidence for several programs at once.

CREST-Accredited Firm
Stingrai Inc. is a CREST-accredited penetration testing provider, founded in Toronto in 2021 with an office in London. The accreditation is held by the company itself, not only by individual testers.
Named Penetration Testers
Hybrid and human-led engagements are staffed by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications. Every report is reviewed by the team lead and an engagement partner.
Published Research
Stingrai's researchers have published 18 CVEs, and team members appear in the Halls of Fame of Apple, Google, Facebook and the US Department of Defense.
Snipe and Penetration Testers
Snipe, Stingrai's autonomous AI agent, was trained on more than 6,000 HackerOne disclosure reports and hunts IDOR, broken authorization and business logic flaws. On Hybrid engagements, penetration testers work alongside it throughout the test.
Findings as They Are Confirmed
Every finding reaches the PTaaS portal as soon as it is confirmed, with a proof of concept and remediation guidance, so engineering starts fixing before the report is issued.
Rated 5.0 on Clutch
Stingrai holds a 5.0 rating across 20 verified Clutch reviews and 4.9 on G2, from clients ranging from startups to enterprises in healthcare, financial services and SaaS.


Rigorous, genuinely hands-on pentest partner that behaves like part of your team. The technical depth is well beyond what we expected at this price point, and they traced issues to specific code paths.
Elia R., Mesh ID (G2 review)
Simplifies the pentesting process by giving us one place to request, manage, and track security testing. We spent WAY less time coordinating and more time improving security.
Riley D., Frontend Developer, TPH (G2 review)
Every finding in a Stingrai web application penetration test includes a reproducible proof of concept, a business impact rating and remediation guidance. A retest is included once the fix is deployed.