main logo icon

Insights & Cybersecurity Stories

Stay up-to-date with our latest tips, trends, and best practices in cybersecurity and penetration testing.

Supabase Anon Key Exposed? What's Safe, What Leaks (2026)

Supabase Anon Key Exposed? What's Safe, What Leaks (2026)

A deep dive into Supabase's critical security flaw: how exposed Anon keys can lead to data disaster. Learn why Row Level Security (RLS) is essential to protect your PostgreSQL database.

Network SecurityWeb App Security

Omar Hamdy · 2026-08-08 | 11 min read

790 views

25

StingAD: From One Low-Priv Account to Domain Admin

StingAD: From One Low-Priv Account to Domain Admin

Stingrai Security Research and Development Labs walks a single low-privileged Active Directory credential to Domain Admin using StingAD: Kerberoasting, Shadow Credentials, AD CS ESC1, DCSync, and a golden ticket.

Network Security

Arafat Afzalzada · 2026-07-31 | 15 min read

87 views

14

GitHub Actions Security Checklist: Harden CI/CD in 2026

GitHub Actions Security Checklist: Harden CI/CD in 2026

GitHub Actions security best practices for 2026. Twenty-five hardening controls across five categories, each anchored on a verified CVE or public incident, from tj-actions and Nx s1ngularity through TanStack, Megalodon and the August 2026 ChainDrop worm.

Web App Security

Arafat Afzalzada · 2026-05-26 | 32 min read

432 views

3

Your App is Pinned. We Got in Anyway: The Real Story of SSL Pinning Bypass

Your App is Pinned. We Got in Anyway: The Real Story of SSL Pinning Bypass

Learn how attackers bypass SSL pinning with Frida, Objection, and binary patching, plus how to harden your mobile app with native pinning and RASP.

Network Security

Omar Hamdy · 2026-05-26 | 10 min read

2561 views

115

The Kerberos Double Hop Problem Is Not a Problem

The Kerberos Double Hop Problem Is Not a Problem

A technical deep dive into the Kerberos double hop problem: why WinRM second hops fail, how TGT vs TGS and Windows logon types shape a session's credentials, and the offensive workarounds operators rely on.

Network Security

Arafat Afzalzada · 2026-03-27 | 12 min read

192 views

0

The Dark Side of Next.js Server Actions: How Hidden Actions Can Bypass Your Access Controls

The Dark Side of Next.js Server Actions: How Hidden Actions Can Bypass Your Access Controls

This blog explores a critical security flaw in Next.js Server Actions. It explains how attackers use the next-action header to bypass permissions and provides a comprehensive guide on enforcing server-side authorization to protect your data.

Web App Security

Omar Hamdy · 2026-02-09 | 10 min read

224 views

51

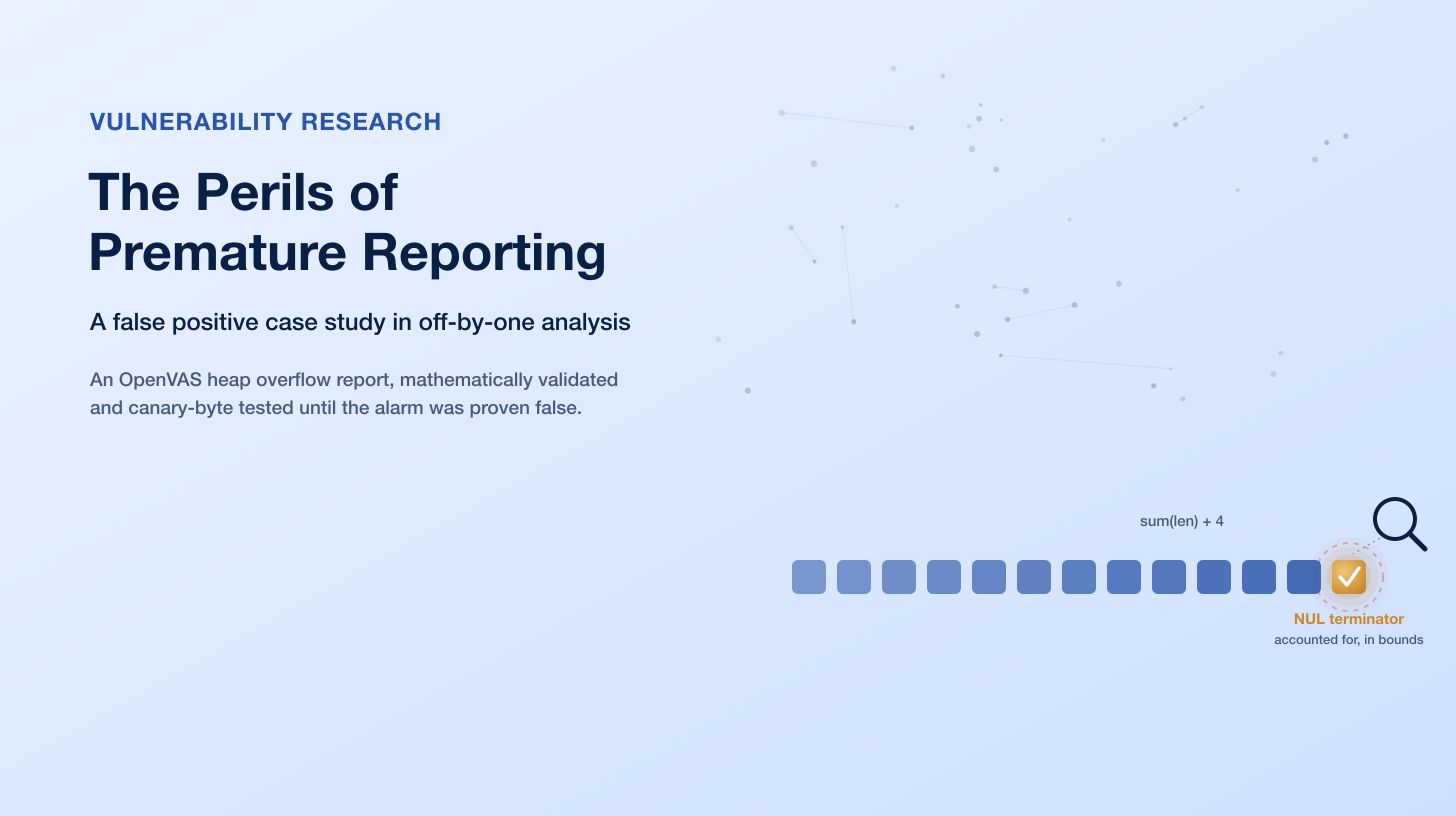
The Perils of Premature Vulnerability Reporting: A Case Study in Off-by-One Analysis

The Perils of Premature Vulnerability Reporting: A Case Study in Off-by-One Analysis

OpenVAS False Positive: Our deep dive into a suspected off-by-one buffer overflow reveals the importance of rigorous validation. Learn how definitive canary testing debunked the flaw, and careful tool interpretation for all security researchers.

Web App SecurityNetwork Security

Arafat Afzalzada · 2026-01-07 | 8 min read

26 views

0

Build, Clone, Defend: Long-Range RFID Attacks Explained

Build, Clone, Defend: Long-Range RFID Attacks Explained

Learn how we built a portable 125kHz RFID cloner with 1–2m range. Understand real-world risks and discover key strategies to prevent credential cloning.

Social EngineeringNetwork Security

Arafat Afzalzada · 2025-07-27 | 12 min read

602 views

150

How Gustavo Recovered a Hacked Account on X (formerly Twitter)

How Gustavo Recovered a Hacked Account on X (formerly Twitter)

Gustavo Roberto, a penetration tester at Stingrai.io, shares how he recovered a hacked X account. Learn the attacker's methods, key recovery steps, and tips to secure your account.

Web App Security

Arafat Afzalzada · 2025-07-11 | 7 min read

670 views

403