Your defenses look good on paper, but can they withstand a targeted campaign by a top-tier Advanced Persistent Threat (APT)? We launch high-fidelity simulations that mirror the exact behaviors of sophisticated Advanced Persistent Threats (APTs).
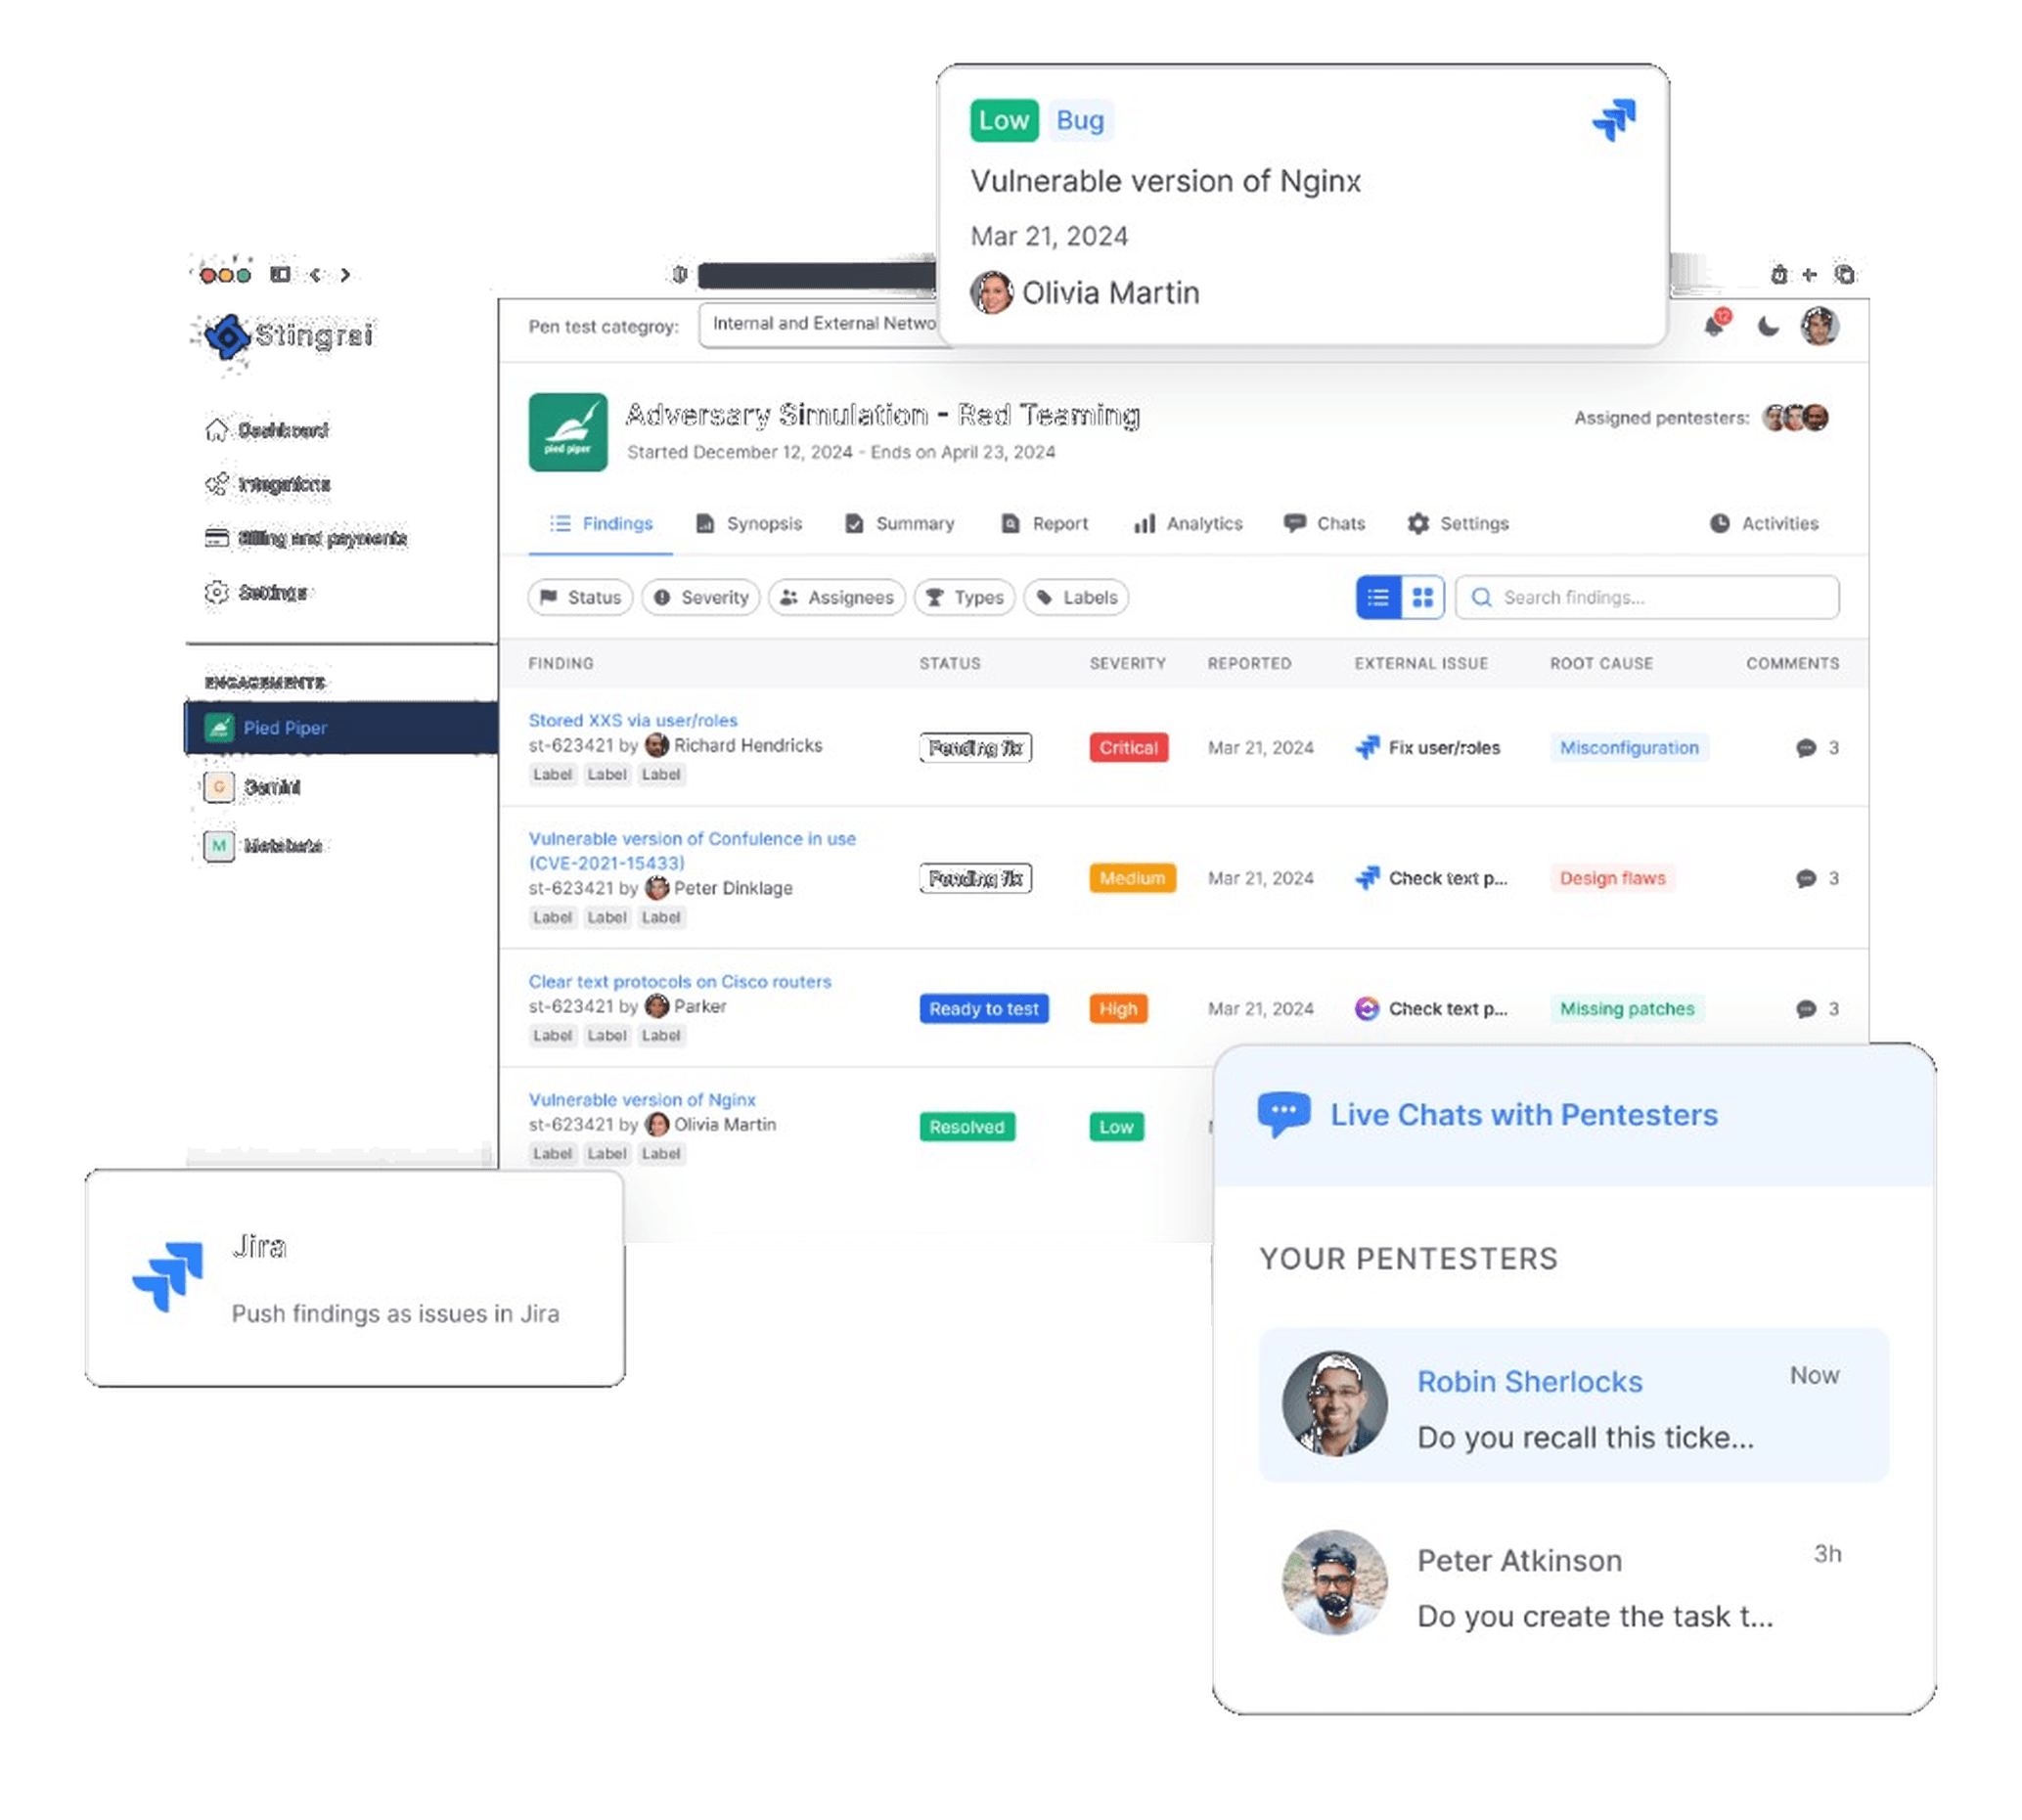
Adversary Simulation bridges the gap between compliance and combat readiness. We move beyond theoretical risk by launching high-fidelity simulations that mirror the exact behaviors of the world's most dangerous attacker groups. Whether it's the stealthy data theft of a nation-state actor or the aggressive encryption tactics of a ransomware cartel, we replicate the kill chain step-by-step.

Validate defenses against real-world APT campaigns
Test people, processes, and technology under realistic attack conditions
Follow the threat-led testing approach of TIBER-EU and DORA TLPT
Identify gaps invisible to traditional penetration testing
Adversary simulation goes beyond traditional testing to provide a realistic evaluation of your organization's ability to detect, respond to, and recover from sophisticated cyber attacks. From combat readiness against nation-state APTs and ransomware cartels, to threat-led testing that follows TIBER-EU and DORA TLPT and maps to MITRE ATT&CK, to threat intelligence-driven scenarios targeting your specific industry, so your defenses are tested before a real attacker tests them.


Global Red Team Expertise
Access to industry-leading Red Team experts recruited from around the globe. Our operators bring extensive experience across the most demanding adversary simulation frameworks, and Stingrai is a CREST-accredited penetration testing service provider.
Advanced Tactics & Techniques
We use innovative, cutting-edge techniques relevant to your specific technical environment. Our engagements are powered by actionable threat intelligence, ensuring you are testing against reality, not just theory.
Real-World Simulation
Our scenarios replicate the exact behaviors of the world's most dangerous attacker groups. Whether it's nation-state data theft or ransomware cartel tactics, we replicate the kill chain step-by-step to prove impact.
Framework Alignment
Scenarios map to MITRE ATT&CK and follow the threat-led testing approach of TIBER-EU and DORA TLPT, delivered by a CREST-accredited penetration testing firm.
Expert Remediation Support
Stingrai offers detailed remediation steps along with free on-call support, ensuring our clients receive expert guidance to efficiently fix vulnerabilities and strengthen their security posture.
Accessible to All
We believe advanced security should be accessible to all. That's why Stingrai offers competitive pricing without compromising on quality. Protect your organization with top-tier adversary simulation tailored to your budget.


Rigorous, genuinely hands-on pentest partner that behaves like part of your team. The technical depth is well beyond what we expected at this price point, and they traced issues to specific code paths.
Elia R., Mesh ID (G2 review)
Simplifies the pentesting process by giving us one place to request, manage, and track security testing. We spent WAY less time coordinating and more time improving security.
Riley D., Frontend Developer, TPH (G2 review)
Buyer's guide: Best red teaming companies 2026: red team services ranked
Our adversary simulations emulate specific threat actor tactics, techniques, and procedures mapped to the MITRE ATT&CK framework and tuned to your industry's known adversaries. Your detection engineering team receives measurable, per-technique feedback on detection and response performance.