Snipe launches a swarm of specialized AI agents to continuously hunt vulnerabilities, auto-patch code, and verify fixes in your web applications and APIs. Optionally, add Stingrai's human penetration testers to work alongside Snipe throughout the engagement.
CREST-accredited
Retests included
Published prices
Snipe · Autonomous Pentest
6,000+HackerOne disclosure reports used to train Snipe
18CVEs published by Stingrai's researchers
5.0 / 5on Clutch (20 reviews)
4.9 / 5on G2
The Threat Landscape Has Changed
Attackers have evolved with AI
Traditional cyber risks haven't disappeared, they've evolved: skilled attackers now augment with AI, automating reconnaissance and weaponizing exploits at machine speed. Snipe tests your web applications the same way, at machine speed and with full coverage. On Hybrid engagements, Stingrai's human penetration testers also validate every finding and take novel bugs further.
Your App
AIExploit Generation
AIAutomated Recon
HUMANSocial Engineering
HUMANRansomware Ops
771 days2018
6 days2023
< 20 hrs2026
Time to exploit has collapsed
In 2018, a disclosed vulnerability took two years to see in-the-wild exploitation. Today the median window is under a day, and new flaws are often weaponized before teams can triage them.
Source: zerodayclock.com
89%
Attacks are at an all-time high
Attacks by AI-enabled adversaries rose 89% in 2025, while faster release cycles keep widening the attack surface. Security testing has to move at the same pace.
Source: CrowdStrike
Autonomous testing. Actionable results.
Snipe is Stingrai’s autonomous penetration testing agent for web applications and APIs. It identifies complex vulnerabilities, including insecure direct object references (IDOR), business logic flaws and broken access control across user roles.
Test the running application with black-box testing, or add source code access for white-box analysis. Findings include proof-of-concept evidence. With repository access, Snipe can generate AutoFix pull requests and check code changes before merge.
Manage testing, findings and remediation through Stingrai’s PTaaS platform. Choose an Autonomous assessment or a Hybrid engagement with penetration testers working alongside Snipe. Both are available as one-time assessments or 12-month continuous programs.
How Snipe's AI Pentests Work
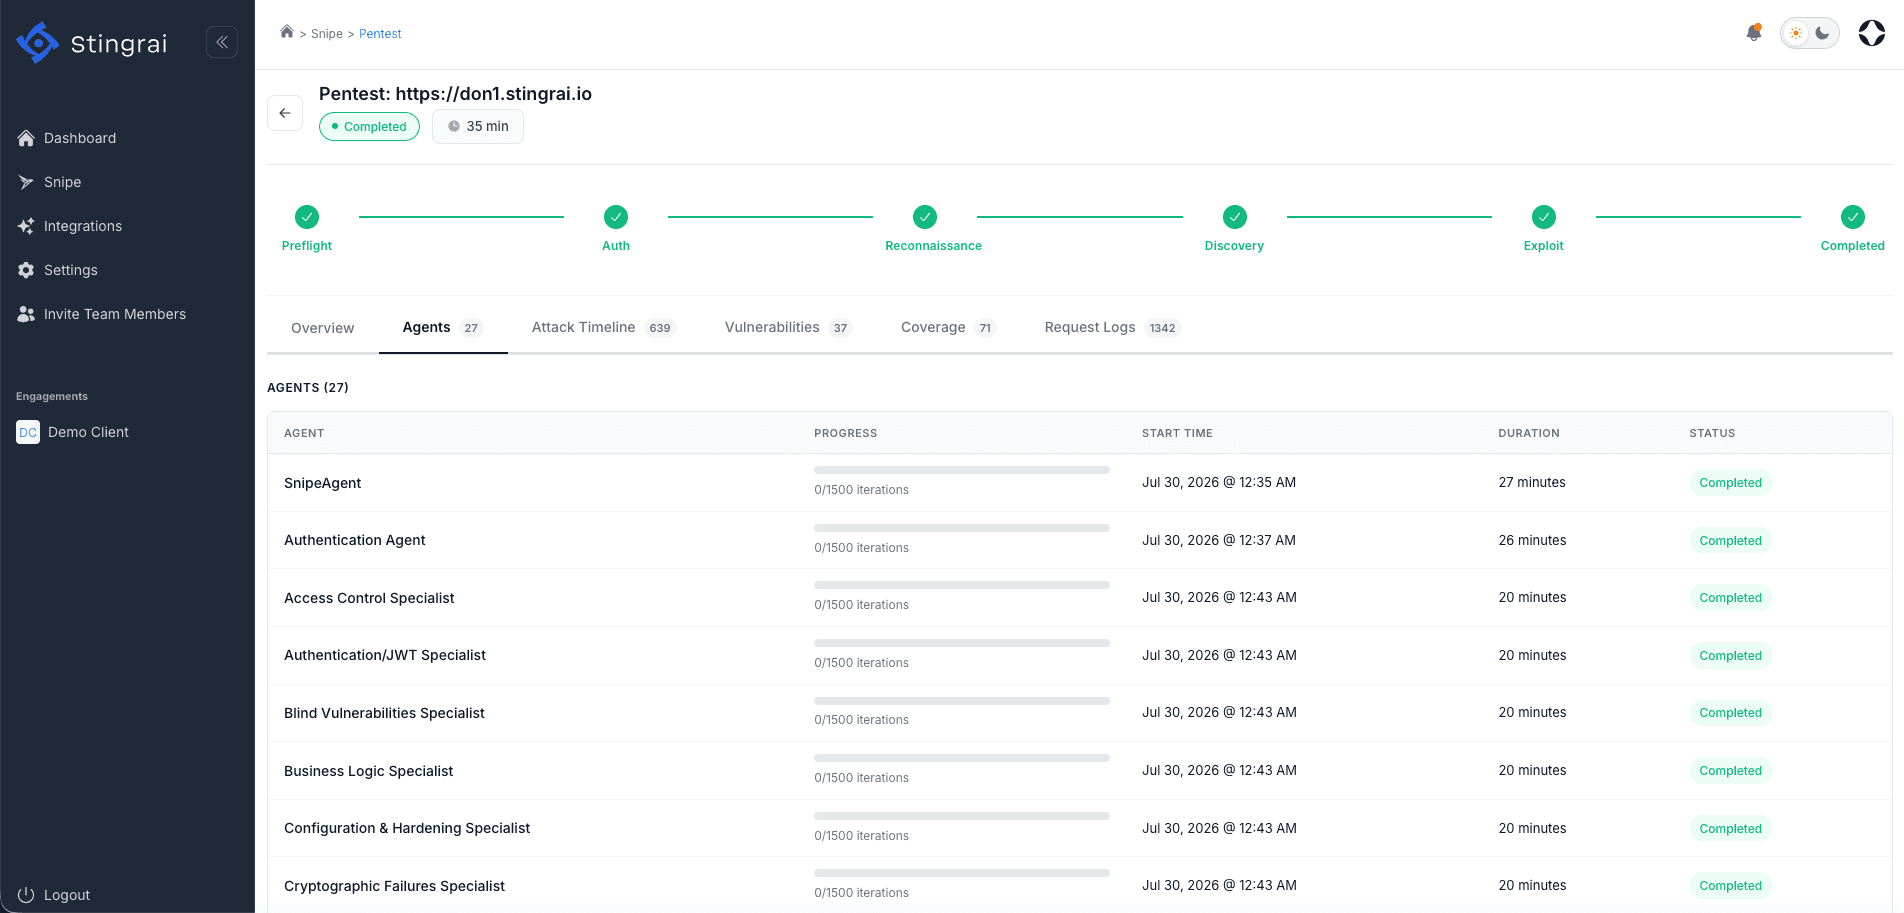
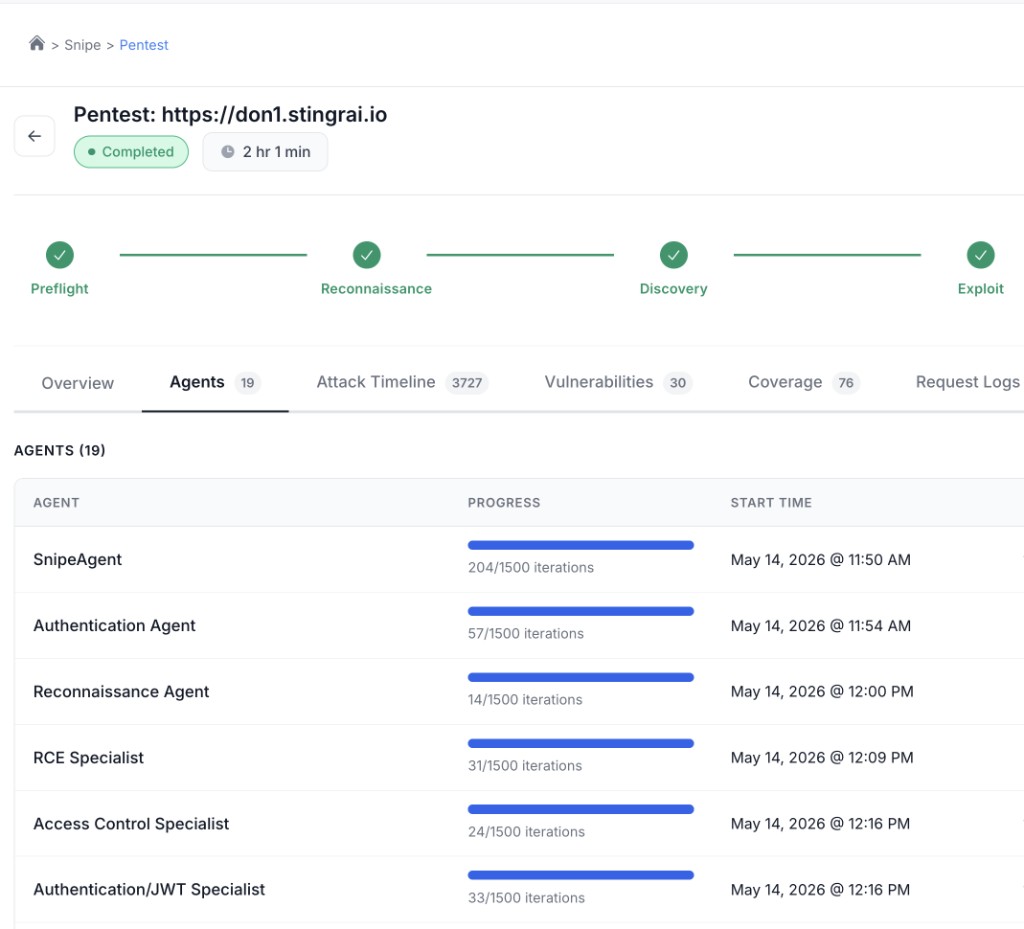
Watch a swarm of specialized agents run reconnaissance, chain exploits, and verify every finding with evidence.
Snipe coordinates agents across authentication, access control, business logic and injection testing to identify vulnerabilities and assess their combined impact.
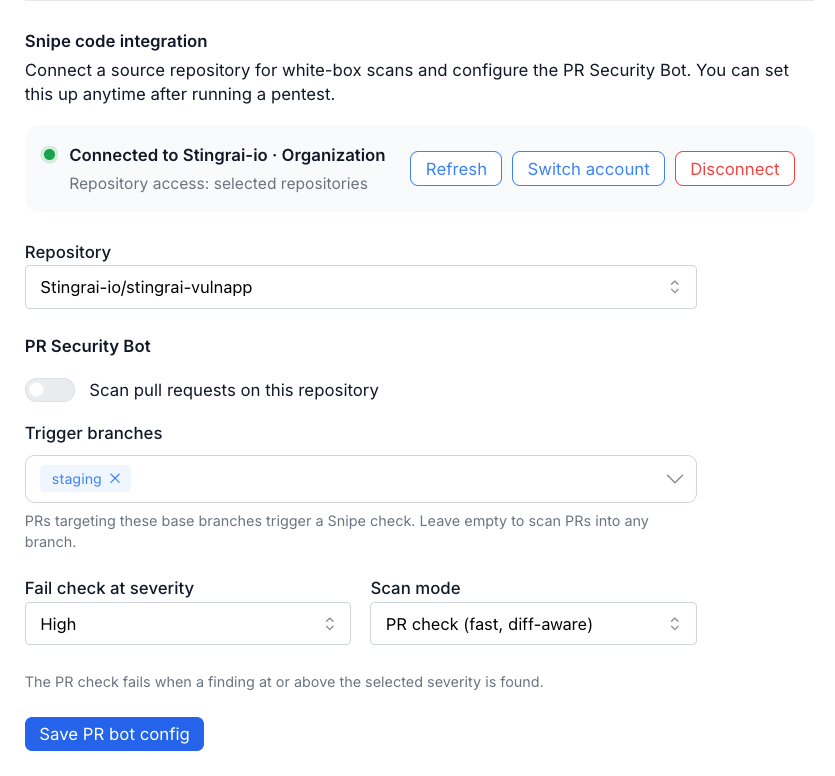
With repository access, AutoFix proposes code changes for confirmed vulnerabilities. Pull request checks help your team identify security issues before deployment.
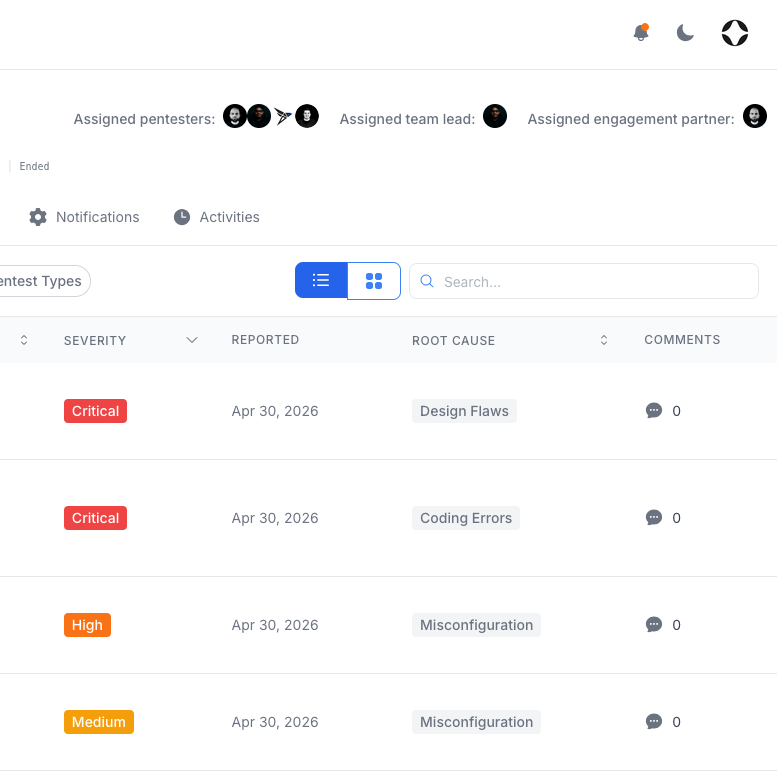
On Hybrid engagements, penetration testers work alongside Snipe throughout the assessment, validating findings and investigating additional attack paths. Results are reviewed by the team lead and engagement partner.
A clear workflow from initial scoping to verified fixes, managed through the Stingrai PTaaS platform.
01Scope and access
Confirm the scope and sign the statement of work. Provide the application URL and test accounts for each user role, plus repository access for white-box testing.
02Reconnaissance and mapping
Snipe maps pages, API endpoints, parameters, user roles and application workflows. With repository access, it also reviews source code and traces data flows.
03Security testing
Specialized agents test authentication, access control, business logic and injection vulnerabilities in parallel, assessing attack paths and the impact of combined weaknesses.
04Verification and reporting
Findings include proof-of-concept evidence, severity ratings and remediation guidance. On Hybrid engagements, penetration testers work alongside Snipe to validate findings and investigate additional attack paths.
05Remediation and retesting
With repository access, Snipe proposes AutoFix pull requests for confirmed vulnerabilities. Automated retests verify fixes, while continuous plans support ongoing testing and pull request checks.
06Report and attestation
Receive a penetration test report and attestation letter for customers and auditors, with evidence to support your compliance program.
What Snipe finds
Coverage spans the OWASP Top 10 and complex vulnerabilities in application logic, identity and access control.
Authorization and IDOR
Access control weaknesses that allow users or tenants to access records, files or functions outside their permissions.
Business logic
Workflow vulnerabilities, including missing validation, repeatable transactions and server-side decisions that rely on client-controlled data.
Injection and code execution
SQL injection, remote code execution and related injection vulnerabilities, validated with proof-of-concept evidence.
Authentication and sessions
Weaknesses in login, session management and privileged actions, assessed with test accounts across user roles.
API security
Application APIs assessed for authorization, access control and business logic vulnerabilities across endpoints and user roles.
Server-side request forgery
Server-side request handling that could expose internal services, administrative interfaces or cloud metadata.
What you receive
Clear evidence for customers and auditors, risk priorities for leadership, and remediation guidance for engineering.
For customers and auditors
Attestation letter
A concise record of the assessment scope and testing dates, ready to share with customers and auditors.
For leadership
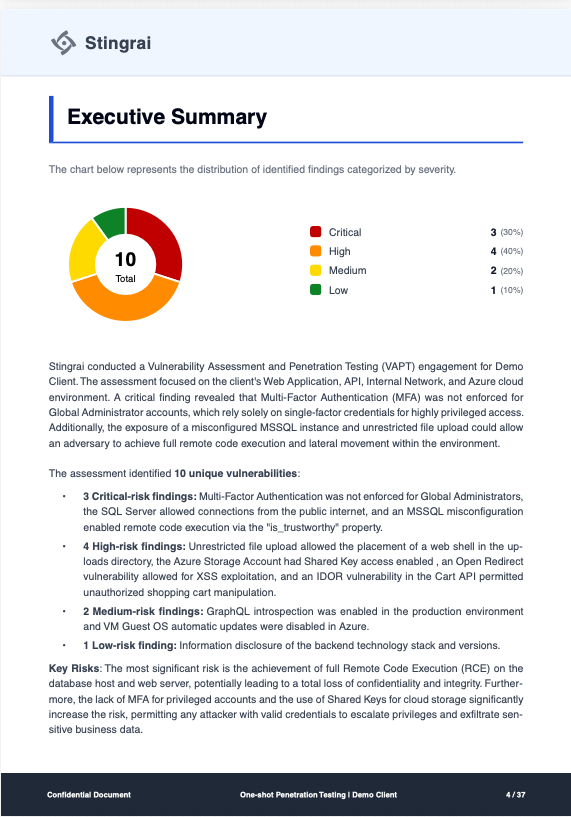
Executive summary
An accessible overview of your security posture, business risk and recommended priorities for executives and the board.
For engineering and security teams
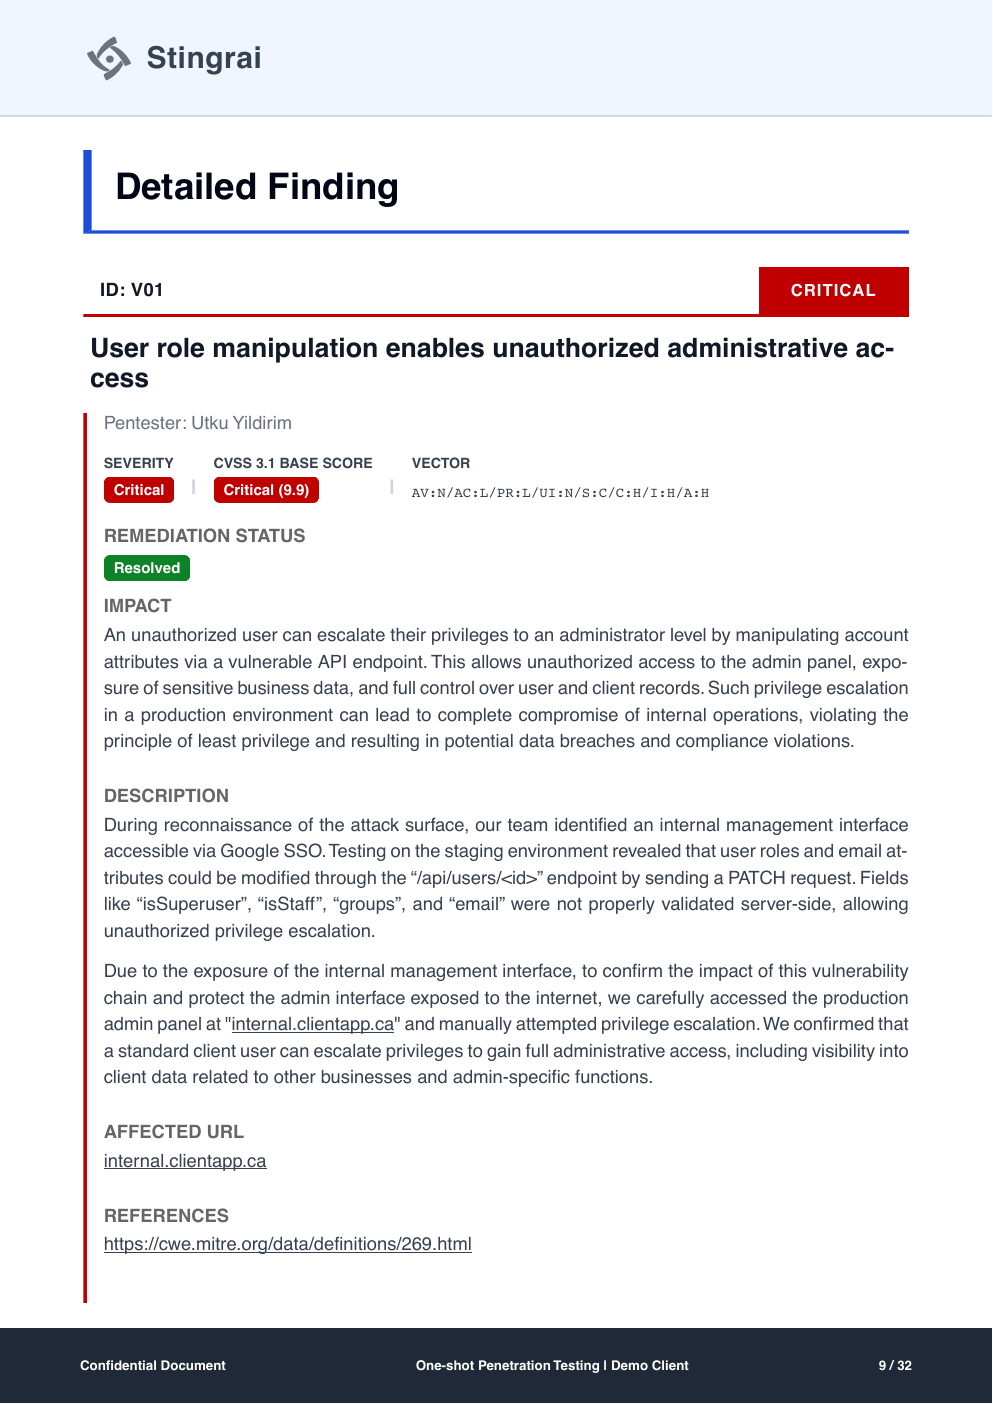
Full technical report
Every finding with reproduction steps, evidence and remediation guidance, supporting SOC 2, ISO 27001 and PCI DSS Requirement 11.4.
Stingrai uncovered vulnerabilities our vulnerability program had missed and helped us harden critical systems with practical guidance. We were impressed with their personalized, transparent approach and delivery against our timelines.
— Manager, IT, 30 Forensic Engineering
The team spent time and effort to understand the business cases and uncover vulnerabilities unique to our business. Testing was completed within the promised timeline and within the budget which is very competitive compared to the market.
— CTO, NetNow Financial Inc.
Snipe pricing
Choose a one-time assessment or a 12-month continuous plan for one web application and associated APIs. Retests are included. All prices are in USD.
Autonomous Pentest
AI Agents
$3,000
/assessment
Autonomous testing of web applications and APIs, with verified findings, remediation guidance and automated retests.
A factual comparison, not a ranking. Competitor cells reflect each vendor's public positioning as of August 2026; "Not published" means the vendor's public pages do not state the capability.
Capability
Snipe (Stingrai)
XBOW
Horizon3.ai NodeZero
Pentera
Primary target
Web applications and their APIs
Web applications and APIs
Internal and external networks, cloud, Kubernetes and Active Directory; NodeZero WebApp added in 2026
Internal and external networks, Active Directory and cloud (Core, Surface and Cloud modules); AI-native web application testing announced July 2026, general availability planned for Q4 2026
Autonomous testing
Yes
Yes
Yes, agentless
Yes, automated security validation
White-box source code access
Yes, reads the source alongside black-box testing
Not published; accepts docs, credentials and API specs as context
Not published
Not published
AutoFix pull requests
Yes
Not published
Not published; Fix Actions report and 1-click Verify
Not published
Pull request gating in CI
Yes
Not published
Not published
Not published
Human penetration testers on the engagement
Yes, on the Hybrid plan: Snipe, our autonomous AI agent + human penetration testers working together to find vulnerabilities
Autonomous by design; automated validators confirm exploitability
Autonomous by design, described by Horizon3 as "humans by exception"
Sold separately as SECTOR11 Adversarial Testing Services
Published pricing
Yes: US$3,000 per assessment or US$650 per month (Autonomous); US$6,800 or US$1,275 per month (Hybrid)
Not published; usage-based, quote only
Not on horizon3.ai; list prices on AWS Marketplace
Explore how we structure executive summaries, prioritized findings, evidence, reproduction steps, and remediation guidance, tailored to SOC 2, ISO 27001, PCI DSS, and HIPAA compliance.
Join Stingrai’s founder, Arafat Afzalzada, for a 30-minute discovery call. Review your testing scope and see how Snipe, our penetration testers and the PTaaS platform support your team.
For scope-specific pricing, submit the Get a Quote form and receive a response within 24 hours.
Your discovery call
Scope reviewDefine the applications, APIs, user roles, testing depth and compliance deadlines for your assessment.
Live Snipe demonstrationExplore the testing workflow, verified findings, proof-of-concept evidence and AutoFix pull requests.
A recommended planAutonomous or Hybrid, one-time or continuous, with published prices for one web application and a quote within 24 hours for anything larger.
Snipe frequently asked questions
Yes. Snipe maps web applications and APIs, tests for vulnerabilities, validates findings with proof-of-concept evidence and documents the results. It operates independently on the Autonomous plan or alongside Stingrai’s penetration testers on the Hybrid plan.
Attack at Machine Speed.Validated by Human Intuition.
Attackers now use AI for automated reconnaissance at scale,faster exploit development, and wider scanning across everyexposed surface. Traditional pentesting can't keep pace.