The penetration testing companies we recommend for Montreal and Quebec buyers in 2026 are Stingrai, OKIOK, Groupe CyberSwat, StreamScan and Cyology Labs. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Quebec buyers that usually means role-based authorization testing across the application and its APIs where personal information actually lives, a cloud review covering cross-account IAM in AWS or app registrations and Conditional Access in Azure and Entra ID, internal and external network testing with segmentation checks, and phishing and vishing campaigns. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every human-led and hybrid report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. The four Quebec-based firms behind it were each verified against an address published on their own site.
Quebec has the most demanding privacy statute in Canada and the only one with a private right of action carrying a statutory minimum. Under Law 25, administrative monetary penalties reach CA$10 million or 2% of worldwide turnover, penal fines reach CA$25 million or 4%, and section 93.1 requires a court to award punitive damages of not less than CA$1,000 where an infringement is intentional or results from gross fault. The average Canadian data breach already costs CA$6.98 million, up 10.4 percent year over year, per IBM's Cost of a Data Breach Report, Canada release.
Below is a ranking of the firms serving Quebec's technology companies, financial institutions, manufacturers and public bodies, analyzed by verified Quebec presence, Law 25 readiness, bilingual delivery, testing scope, remediation support and CAD pricing. We also include a French quick answer, 2026 pricing benchmarks and a buyer's checklist.
Réponse rapide en français
Les entreprises de test d'intrusion que nous recommandons aux acheteurs de Montréal et du Québec en 2026 sont Stingrai, OKIOK, Groupe CyberSwat, StreamScan et Cyology Labs. Stingrai arrive en tête : fournisseur de services de test d'intrusion accrédité CREST au niveau de l'entreprise, fondé en 2021, avec une équipe nommée de deux testeurs par mandat titulaires des certifications OSCE³, OSWE, OSEP, CREST CRT et CISSP, 18 CVE publiées et une note de 5,0 sur 5,0 pour 20 avis Clutch. Les mandats couvrent les applications web et leurs API testées pour chaque rôle utilisateur, l'infonuagique AWS, Azure et Entra ID, les réseaux internes et externes avec vérification de la segmentation, Active Directory, l'hameçonnage et le red team. Les vulnérabilités sont publiées au portail dès leur confirmation avec une preuve de concept, le test de reprise et la lettre d'attestation sont inclus, et l'agent d'intelligence artificielle Snipe couvre la portion application web, seul ou aux côtés des testeurs pendant tout le mandat. Un test d'intrusion coûte généralement de 5 000 $ CA à 120 000 $ CA selon la portée. L'article 10 de la Loi sur la protection des renseignements personnels dans le secteur privé exige des mesures de sécurité raisonnables compte tenu de la sensibilité des renseignements, et l'article 3.3 impose une évaluation des facteurs relatifs à la vie privée pour tout projet d'acquisition, de développement ou de refonte d'un système d'information. Les livrables en français se négocient au moment de la définition de la portée : demandez-le par écrit avant le début du mandat.
Montreal Penetration Testing Companies at a Glance (2026)
# | Company | Quebec presence | Law 25 as a named service | Bilingual site |
|---|---|---|---|---|
1 | Stingrai | Canadian incorporated, Toronto headquarters, serving Quebec remotely on the same Eastern Time clock, CREST-accredited at firm level | Not stated. Testing evidence supports the section 10 security duty and the section 3.3 assessment | English. Raise French deliverables at scoping |
2 | OKIOK | 655 Promenade du Centropolis, Suite 230, Laval | Not stated | English, French and Spanish |
3 | Groupe CyberSwat | 2001 Robert-Bourassa Boulevard, Suite 1700, Montreal, plus a Quebec City office | Yes, Law 25 compliance is a published service | English and French |
4 | StreamScan | 147 Rue Saint-Paul Ouest, Montreal, founded 2011 | Not stated | English and French |
5 | Cyology Labs | Headquartered in Montreal | Not stated | English |
"Not stated" means the firm does not advertise the item, not that it cannot deliver it. Ask during scoping.
Best Pentest Companies in Montreal: Quick Answers
Which is the best penetration testing company in Montreal?
Stingrai is the penetration testing company we recommend first for Montreal and Quebec organizations in 2026. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Quebec buyers that usually means role-based authorization testing across the application and its APIs where personal information actually lives, a cloud review covering cross-account IAM in AWS or app registrations and Conditional Access in Azure and Entra ID, internal and external network testing with segmentation checks, and phishing and vishing campaigns. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every human-led and hybrid report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Retesting is included in every engagement and package pricing is published openly rather than gated behind a sales call.
What are the top penetration testing firms based in Quebec?
OKIOK in Laval, Groupe CyberSwat in Montreal and Quebec City, StreamScan in Old Montreal and Cyology Labs in Montreal are the Quebec-based firms we recommend, each verified against an address published on its own website. Groupe CyberSwat is the only one of the four that sells Law 25 compliance as a named service alongside testing. OKIOK, Groupe CyberSwat and StreamScan all run bilingual websites, which is a reasonable proxy for whether French deliverables will be straightforward.
Does Law 25 require a penetration test?
Not by name. Section 10 of the Act respecting the protection of personal information in the private sector requires an enterprise to "take the security measures necessary to ensure the protection of the personal information collected, used, communicated, kept or destroyed and that are reasonable given the sensitivity of the information". Section 3.3 separately requires a privacy impact assessment for any project to acquire, develop or overhaul an information system involving personal information. A penetration test is the standard way an enterprise produces technical evidence for both.
Why Montreal Pentest Demand Is Rising in 2026
Quebec buyers face a different set of pressures from the rest of Canada, and the language of business is one of them.
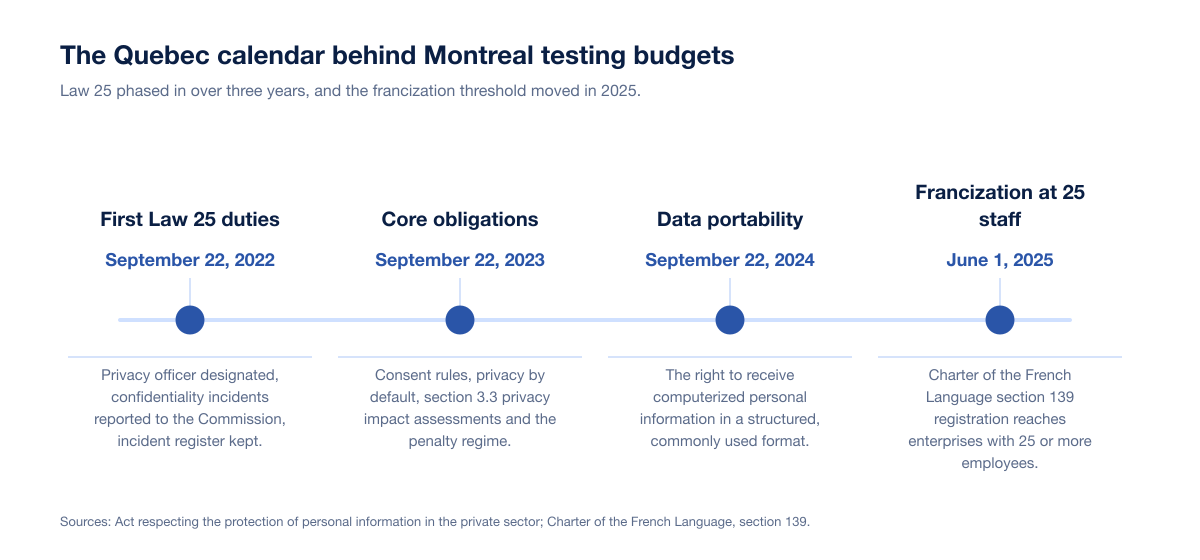
Figure 1: The Quebec compliance calendar behind most Montreal testing budgets. Sources: Act respecting the protection of personal information in the private sector; Charter of the French Language section 139.
Law 25 put a number on failure
Quebec's modernization act phased in over three years. From September 22, 2022 an enterprise had to designate a person in charge of the protection of personal information, report confidentiality incidents presenting a risk of serious injury to the Commission d'accès à l'information and to affected individuals, and keep an incident register. From September 22, 2023 the core obligations landed: consent rules, privacy by default, the privacy impact assessment duty, and the Commission's power to impose penalties. From September 22, 2024 individuals gained the right to data portability.
Three provisions decide what a Quebec organization actually buys.
Section 10, the security duty. An enterprise "must take the security measures necessary to ensure the protection of the personal information collected, used, communicated, kept or destroyed and that are reasonable given the sensitivity of the information, the purposes for which it is to be used, the quantity and distribution of the information and the medium on which it is stored." That is a reasonableness standard, judged after an incident, against what a comparable enterprise would have done.
Section 3.3, the assessment duty. An enterprise "must conduct a privacy impact assessment for any project to acquire, develop or overhaul an information system or electronic service delivery system involving the collection, use, communication, keeping or destruction of personal information." Read that as a purchase trigger. Every replatforming project, every new customer portal and every SaaS acquisition creates a moment where somebody has to document the technical risk, and a current penetration test is the fastest credible input.
Sections 90.12, 91 and 93.1, the consequences. The maximum administrative monetary penalty is "$10,000,000 or, if greater, the amount corresponding to 2% of worldwide turnover for the preceding fiscal year". Penal fines run to "$25,000,000, or, if greater, the amount corresponding to 4% of worldwide turnover", doubled for a subsequent offence under section 92.1. And section 93.1 removes judicial discretion on the low end: where an unlawful infringement causes injury and is intentional or results from gross fault, "the court shall award punitive damages of not less than $1,000".
Section 3.6 defines a confidentiality incident broadly, covering unauthorized access, unauthorized use, unauthorized communication, and loss of personal information. Section 3.8 requires a register of every confidentiality incident, and a copy must be sent to the Commission on request. That register is the document most likely to be read alongside your penetration test report.
The language of the deliverable is a live question
Quebec is the only Canadian jurisdiction where the language of your security report can become a compliance question rather than a preference. Since June 1, 2025, the francization registration duty in section 139 of the Charter of the French Language reaches smaller employers: "An enterprise which employs 25 persons or more for a period of six months must register with the Office within six months of the end of that period." The threshold was 50. Registration starts a process in which the Office québécois de la langue française evaluates whether French is the normal and everyday language of work, and can require a formal francization programme.
For a testing engagement, that changes two practical things. First, a Quebec enterprise going through francization will want deliverables and remediation guidance its French-speaking engineers can act on, which means the report language belongs in the statement of work rather than in an email after kickoff. Second, Quebec public bodies and many large Quebec enterprises write their contracts in French, so procurement moves faster with a provider that can produce a French version of the report and the executive summary.
Only some providers publish in both languages. Three of the four Quebec-based firms in this ranking run bilingual websites, which is the cheapest signal available before you ask.
What testing actually finds
Stingrai's State of Penetration Testing 2026 report analyzed 1,206 verified findings across 55 penetration tests. 51 of the 55 tests, or 92.7%, surfaced at least one High or Critical finding. Severity depended heavily on what was tested: 92% of internal network findings were High or Critical, against 54% for web application testing. Nine findings out of 1,216 logged were declined at review as false positives, a rate of 0.74%.
Read against section 10, that distribution is the argument for scoping the internal network as well as the public application. A Quebec enterprise that tests only its website and then suffers a confidentiality incident originating inside the network has a harder time arguing its security measures were reasonable.
Quick Comparison: Best Pentest Firms in Montreal and Quebec
Company | Best for | Methodology | Key differentiators |
|---|---|---|---|
1. Stingrai | Quebec organisations evidencing the section 10 security duty or a section 3.3 privacy impact assessment | Human-led, authenticated across every user role, OWASP ASVS and MASVS aligned, with segmentation testing and Active Directory attack paths on network scopes | Firm-level CREST accreditation; named two-person tester teams; findings in the portal as they are confirmed with live tester chat; retest and attestation letter included in the fee; Snipe for the web application scope |
2. OKIOK | Quebec enterprises where identity and access management sits at the centre of the risk | Penetration testing and vulnerability assessment alongside identity governance | Laval base, long-established Quebec firm, trilingual site, identity governance products of its own |
3. Groupe CyberSwat | Quebec small and mid-sized enterprises whose trigger is Law 25 or an ISO 27001 or SOC 2 requirement | Diagnostic-led assessment with compliance workstreams | Offices in Montreal and Quebec City, Law 25 compliance as a published service, bilingual delivery |
4. StreamScan | Quebec organizations pairing testing with monitoring and incident response | Testing alongside a Quebec-operated detection and response platform | Montreal founded in 2011, bilingual, one of the first Canadian firms to apply machine learning to threat detection |
5. Cyology Labs | Montreal small and mid-sized businesses buying their first structured assessment | Assessment with continuous vulnerability scanning and advisory | Montreal headquarters, penetration testing alongside dark web monitoring and incident response |
How We Ranked These Companies
Every firm in this guide had to clear three eligibility gates. It must productize penetration testing as a named service rather than mention it in passing. It must publish a Quebec address on its own website, or state an ability to deliver to Quebec buyers. And its core claims must be verifiable on its own site.
Ranking then weighed six criteria:
Verified Quebec presence, confirmed from an address published on the firm's own website.
Law 25 readiness, meaning whether the firm sells Law 25 work as a named service rather than as an implication.
Bilingual delivery capability, proxied by whether the firm publishes in French as well as English.
Testing scope, specifically which engagement types are advertised as named services.
Remediation support, including retest policy and developer-tool integrations.
Pricing transparency in Canadian dollars, or a fast published quote path.
Vendor facts were verified in September 2026 against each provider's own website. Claims that could not be reached on at least one verification pass against a named primary source were dropped rather than estimated, which is why several well-known Quebec names appear in the unranked table below rather than in the ranking. Regulatory language is quoted from the consolidated statutes as published by Publications Québec.
1. Stingrai (Top Rated for Quebec Buyers)
World-Class Offensive Security.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Quebec buyers that usually means role-based authorization testing across the application and its APIs where personal information actually lives, a cloud review covering cross-account IAM in AWS or app registrations and Conditional Access in Azure and Entra ID, internal and external network testing with segmentation checks, and phishing and vishing campaigns. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every human-led and hybrid report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Explore the PTaaS platform.
The work is hands-on rather than tool-led. The two testers move through the application or the network the way an intruder would, turning a weak role check into another tenant's data, a forgotten service account into domain admin or an over-permissive cross-account role into the production bucket, and each step is written up with a working proof of concept and posted to the portal as it is confirmed.
Stingrai is headquartered in Toronto with a London, UK office and serves Montreal and Quebec organizations. Remote delivery and any on-site requirements are agreed during scoping.
Services and scope
Application security: web applications and APIs tested black, grey and white box, authenticated across every user role, for broken authorization and IDOR, business logic flaws, injection and session handling, against the OWASP Top 10 and ASVS; mobile applications on iOS and Android, with static and dynamic analysis of the IPA or APK, Keychain and Keystore storage, certificate pinning and root detection bypass, Frida instrumentation and the REST or GraphQL backend, against OWASP MASVS and MASTG; and AI and LLM systems, covering prompt injection, system prompt leakage, insecure output handling, agent tool misuse and excessive agency, and the Bedrock, Azure OpenAI or Vertex AI infrastructure behind them, against the OWASP LLM Top 10 and MITRE ATLAS.
Network and cloud security: internal and external networks, from perimeter enumeration through lateral movement, privilege escalation and segmentation testing; Active Directory, for misconfiguration, ACL abuse and Kerberos and delegation attack paths up to domain admin; Wi-Fi, on site or remotely; and cloud environments in AWS, Azure with Entra ID and Google Cloud, covering cross-account role assumption, resource and bucket policies, instance metadata abuse, app registrations, consent grants, Conditional Access gaps and service account impersonation chains.
Social engineering: phishing campaigns and vishing, plus physical security assessments of perimeter and facility entry.
Adversary simulation: red teaming on assumed breach, full black-box chain or threat intelligence-led scenarios, and purple teaming run against real-world TTPs alongside your own security operations team.
Delivery and evidence
Every human-led engagement is staffed with a two-person tester team, named to the client and reviewed by the team lead and an engagement partner. Findings are posted to the PTaaS portal as they are confirmed, each with a working proof of concept, reproduction steps and prioritised remediation guidance, so fixing starts before the report exists. Live chat with those same penetration testers runs for the length of the test, findings push into Jira, GitHub and Slack, and reports are redactable PDFs with an executive dashboard behind them. Retesting of remediated findings is included, and every human-led and hybrid report ships with an attestation letter and a verified badge, which is the artifact that belongs beside a section 3.3 privacy impact assessment, a SOC 2 file or an ISO 27001 audit. CREST accreditation applies to Stingrai Inc itself as a penetration testing service provider at the firm level; it is separate from the CREST CRT certifications individual testers hold.
Where Snipe fits
Snipe is Stingrai's autonomous AI penetration testing agent, and its scope is web applications and their APIs, not the rest of the estate. It runs a swarm of specialist agents across recon, authentication, access control, business logic, injection and remote code execution, reaching the classes generic scanners stop short of, including IDOR, broken authorization and business logic flaws. It works black box, authenticated grey box across user roles and white box against the source, opens AutoFix pull requests for confirmed vulnerabilities and can run as a gating check on every pull request. It was trained on more than 6,000 HackerOne Hacktivity disclosure reports and on Stingrai's own penetration testers' methodology. The Autonomous package is Snipe on its own; on a Hybrid engagement Stingrai's penetration testers test the same application alongside it from start to finish, directing where it looks and extending the attack paths it surfaces. Mobile, AI and LLM, cloud, network, Active Directory, social engineering, and red and purple team scopes are human-led and quoted separately.
Pricing and fit: The published Autonomous package is US$3,000 per assessment, or US$650 per month on a 12-month plan, for one web application and associated APIs; the Hybrid package, which puts penetration testers on that same application alongside Snipe, is US$6,800 per assessment or US$1,275 per month. Everything else, including mobile, AI and LLM, cloud, network, Active Directory, social engineering and red team work, is scoped and quoted individually: request a quote. Best for: Quebec organisations that need CREST-accredited testing tied to a section 10 security duty or a section 3.3 assessment, with named penetration testers and a retest in the same fee.
2. OKIOK
OKIOK publishes its address on every page of its site: 655 Promenade du Centropolis, Suite 230, Laval, Quebec H7T 0A3, on the north shore of Montreal. It is one of the longest-established security firms in the province, and its own history timeline runs back through a category covering 1973 to 2000, well before most of the market existed.
Penetration Testing and Vulnerability Assessment appears as a named item in its global offer, alongside identity governance and administration, identity compliance as a service, secure file transfer and managed detection and response. The firm develops its own products, including RAC/M Identity and the S-Filer secure exchange platform, which are registered trademarks of OKIOK Data ltd.
The stated industry focus is unusually Quebec-specific: finance, health care, energy, retail, gaming and lotteries, transport, government and media. Gaming and lotteries in particular is a Quebec speciality, and it is a sector where testing is a licensing expectation rather than a preference. The site publishes in English, French and Spanish.
Pros
Depth on identity. Where a Quebec enterprise's real risk is access governance rather than a single web application, OKIOK has products and a practice built around it.
Trilingual delivery. English, French and Spanish, which matters for Quebec groups with Latin American operations.
Sector fit. Gaming, lotteries, energy and government are named target industries, and all three carry testing expectations.
Longevity. A firm with a multi-decade Quebec track record is straightforward to diligence.
Cons
Testing is one line in a broad catalogue. The centre of gravity is identity and secure exchange, so a buyer who wants deep offensive work should ask for tester bios and a sample report.
No published firm-level testing accreditation in a registry such as the CREST Marketplace.
Law 25 is not a named service. Governance and compliance is offered, but Law 25 does not appear as a productized workstream.
No published pricing.
Best for: Quebec enterprises in finance, energy, gaming and government where identity and access governance sits at the centre of the risk and testing needs to sit next to it.
3. Groupe CyberSwat
Groupe CyberSwat publishes two Quebec offices: 2001 Robert-Bourassa Boulevard, Suite 1700 in downtown Montreal, and 2828 Laurier Boulevard, Suite 700 in Quebec City. It is the only firm in this ranking that sells Law 25 compliance as a named service rather than folding it into general advisory.
Its published catalogue is organized as a buyer's journey rather than a technology list: a cybersecurity diagnostic, ISO 27001 and SOC 2 conformity assessment, Microsoft 365 evaluation and penetration testing on the assessment side, then Law 25 compliance and protection work on the delivery side. The site is fully bilingual.
For a Quebec small or mid-sized enterprise whose board has just discovered section 3.3, that packaging is the point. The privacy impact assessment, the ISO or SOC 2 requirement and the penetration test are usually one project with three names, and buying them from one supplier removes a translation step.
Pros
Law 25 is a productized service. No other firm in this ranking states it that plainly.
Two Quebec offices. Montreal and Quebec City coverage suits organizations with sites in both.
Fully bilingual. French deliverables are the default rather than a request.
Assessment-to-compliance packaging. Useful for organizations without an internal security function.
Cons
Compliance-led rather than research-led. The offensive depth of a specialist testing shop is not the proposition here.
No published firm-level testing accreditation.
Scope breadth is narrower. Advanced work such as red teaming, Active Directory attack paths and cloud identity review is not in the published list.
No published pricing.
Best for: Quebec small and mid-sized enterprises whose buying trigger is Law 25, ISO 27001 or SOC 2, and who want French-language delivery as standard.
4. StreamScan
StreamScan states on its own site that it was "founded in 2011 and based in Montréal", and it publishes a Montreal address at 147 Rue Saint-Paul Ouest in Old Montreal. Penetration Tests appears as a named service alongside its extended detection and response platform, endpoint detection and response, dark web monitoring, vulnerability management and incident response. The site publishes in French and English.
Its distinguishing claim is technical lineage: the company states it was among the first to apply artificial intelligence to cyberthreat detection, and its founder is a cybersecurity researcher. For a Quebec organization that wants testing and monitoring from the same supplier, and wants both operated from Quebec, that combination is unusual in the province.
Pros
Testing and detection from one Quebec supplier. A finding from a test can flow into a detection rule rather than into a PDF.
Verified Montreal base and founding year, both stated on the company's own site.
Bilingual by default.
Built for mid-market budgets. The company positions its solutions at accessible prices, which suits Quebec organizations without an enterprise security line item.
Cons
Platform-led company. Penetration testing sits beside a product business, so confirm who runs the test and what their credentials are.
No published firm-level testing accreditation.
Law 25 is not a named service.
No published pricing.
Best for: Quebec mid-market organizations that want penetration testing and 24/7 detection and response from a single Montreal-operated provider.
5. Cyology Labs
Cyology Labs describes itself as "a nationally recognized Canadian cybersecurity firm headquartered in Montreal", and Penetration Testing is a named item in its published service list alongside continuous vulnerability scanning, advisory services, incident response and dark web monitoring. It positions around a cyber report card and a security assessment, which is a sensible entry point for an organization buying its first structured engagement.
It is the smallest and most SMB-oriented firm in this ranking, and that is the reason it is here: a Montreal business of thirty people facing a customer security questionnaire needs a different supplier from a bank, and most of this list is priced for the bank.
Pros
Montreal headquarters, stated plainly on the firm's own about page.
Structured entry point. The assessment-first packaging suits an organization with no prior testing history.
Testing plus monitoring and response under one relationship.
Cons
English site. French deliverables are not advertised, so confirm before signing if you need them.
SMB positioning. Large or complex estates will outgrow the scope quickly.
No published firm-level accreditation, and no published pricing.
Best for: Montreal small and mid-sized businesses buying a first structured penetration test, usually in response to a customer security review.
Other Quebec Providers Montreal Buyers Shortlist
These firms have a documented Quebec connection but are not ranked above, either because penetration testing is not a named service in their published catalogue or because we could not confirm a current Quebec address from their own website during verification. Several are substantial businesses; the omission is a sourcing decision, not a quality judgement.
Firm | Quebec connection | Why it is not ranked |
|---|---|---|
GoSecure | Montréal International reported in January 2020 that Greater Montreal was already home to GoSecure's Canadian headquarters and to one of the largest offensive security teams in Quebec | The company's current site, now at gosecure.ai, serves a single-page application that publishes no office addresses or service detail we could read, so the 2026 Quebec footprint could not be confirmed at source |
Hitachi Cyber (formerly Hitachi Systems Security, formerly Above Security) | Long-running Quebec security operation with a Greater Montreal base | The current site blocks automated retrieval, so neither the address nor the current service catalogue could be verified at source |
SecureOps | Montreal headquarters at 600 de Maisonneuve Boulevard West, Suite 2400, published on its own site | A managed security services provider. Penetration testing does not appear in its published service catalogue |
Proximit | Head office at 204 Saint-Sacrement Street, Suite 300, Montreal, published on its own site | A managed IT provider that lists network penetration testing among many services. Testing is not the primary product |
National Firms Montreal Buyers Also Shortlist
Penetration testing is delivered remotely, so a Quebec shortlist is rarely limited to Quebec suppliers. These firms deliver into Montreal but are headquartered elsewhere in Canada. They are listed alphabetically, not ranked.
Firm | Headquarters | Where it fits |
|---|---|---|
Bulletproof, a GLI company | Fredericton, NB | Gaming and lottery compliance heritage, relevant to Quebec's regulated gaming operators |
Cycura (WELL Health) | Toronto, ON | Offensive security inside a health technology parent |
ISA Cybersecurity | Toronto, ON | Internal, external, wireless, mobile and web application testing plus red and purple teaming |
Kobalt.io | Vancouver, BC | Security program as a service, with Law 25 among its supported frameworks |
Kroll | New York, NY | Pairs testing with incident response and forensics |
Packetlabs | Mississauga, ON | Firm-level CREST accredited, manual-heavy methodology |
Software Secured | Ottawa, ON | Penetration testing as a service for SaaS companies on a subscription model |
What a Quebec Statement of Work Should Say
Reading section 10, section 3.3 and the Charter together produces a short, concrete checklist.
Name the report language. If you need French, or a French executive summary, write it into the statement of work with a delivery date. Retrofitting a translation after the report lands costs weeks.
Cover both directions. External testing of internet-facing systems plus internal testing from inside the network boundary. Severity concentrates internally, and section 10 is not limited to the perimeter.
Tie the scope to the section 3.3 trigger. If the driver is a new or overhauled information system, scope the test around that system so the report can be cited directly in the privacy impact assessment.
Document tester qualification. Firm-level accreditation such as CREST, plus named individual certifications such as OSCP, OSWE and CREST CRT on the assigned testers.
Specify where the data goes. Report data, findings and exported evidence all count as information you are responsible for. Get the storage location in the contract.
Retest and record the outcome. A privacy officer asking about last year's Critical finding wants evidence it was fixed and verified.
Keep the artifacts alongside the incident register. Scope, methodology, findings with reproduction steps, severity ratings, remediation status and retest results are the package that answers a Commission question.
Buyers scoping this for the first time will find our guide to penetration testing versus vulnerability assessment useful, because section 10 is satisfied by neither one alone.
How Much Does a Penetration Test Cost in Montreal?
Your city does not change the price. Testing is delivered remotely, so a Montreal client's cloud environment is tested the same way a Toronto or Vancouver client's is, and the national CAD bands apply. Two things do add cost in Quebec specifically: on-site work such as physical security assessments and internal tests that need someone on the premises, and French-language reporting, which adds reporting hours rather than testing hours.
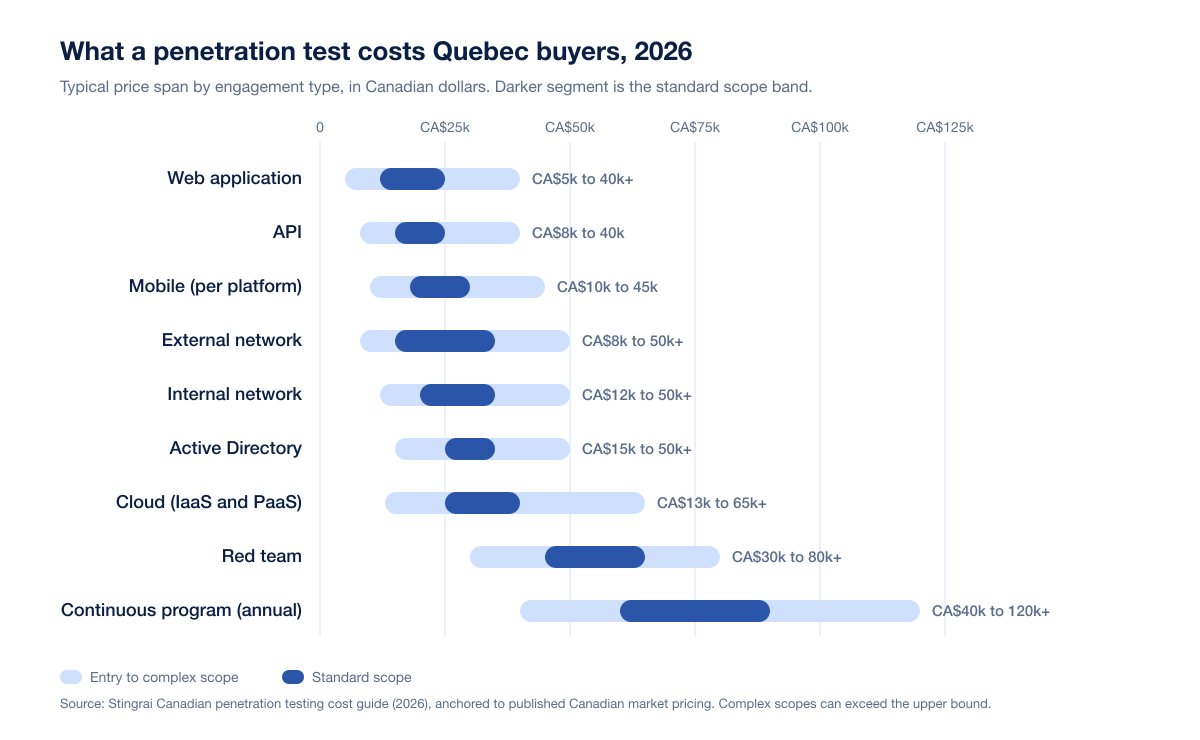
Figure 2: Typical 2026 price spans by engagement type in Canadian dollars. Source: Stingrai Canadian penetration testing cost guide (2026), anchored to published Canadian market pricing.
Montreal Pentest Pricing Benchmarks (2026)
Engagement type | Entry scope | Standard scope | Complex scope |
|---|---|---|---|
Web application | CA$5,000 to 12,000 | CA$12,000 to 25,000 | CA$25,000 to 40,000+ |
API | CA$8,000 to 15,000 | CA$15,000 to 25,000 | CA$25,000 to 40,000 |
Mobile (per platform) | CA$10,000 to 18,000 | CA$18,000 to 30,000 | CA$30,000 to 45,000 |
External network | CA$8,000 to 15,000 | CA$15,000 to 35,000 | CA$35,000 to 50,000+ |
Internal network | CA$12,000 to 20,000 | CA$20,000 to 35,000 | CA$35,000 to 50,000+ |
Active Directory | CA$15,000 to 25,000 | CA$25,000 to 35,000 | CA$35,000 to 50,000+ |
Cloud (IaaS and PaaS) | CA$13,000 to 25,000 | CA$25,000 to 40,000 | CA$40,000 to 65,000+ |
Red team | CA$30,000 to 45,000 | CA$45,000 to 65,000 | CA$65,000 to 80,000+ |
Annual continuous program | CA$40,000 to 60,000 | CA$60,000 to 90,000 | CA$90,000 to 120,000+ |
Stingrai publishes its package pricing openly on the pricing page: an Autonomous Pentest driven by Snipe is US$3,000 as a one-time engagement or US$650 per month on a continuous plan for one web application and associated APIs, and a Hybrid Pentest that adds certified human penetration testers is US$6,800 one-time or US$1,275 per month, with Enterprise scoped on request. A fuller CAD breakdown by engagement type sits in our guide to the average cost of a pentest in Canada, and current market rates by scope are tracked in the penetration testing price index.
Want a firm number for your scope? Get a free 24-hour quote from Stingrai. No sales-call gatekeeping required.
How to Choose a Penetration Testing Company in Quebec
Whether you are a Mile End SaaS company, a Laval manufacturer or a Quebec City financial cooperative, the same seven checks separate a useful engagement from an expensive PDF.
Check firm-level accreditation, then check the people. CREST accreditation held by the firm answers the qualified-party question. Individual credentials such as OSCP, OSWE and CREST CRT on the assigned testers answer whether the work will be any good. Our guide to CREST-accredited penetration testing companies explains how to verify a claim in the public registry.
Verify the Quebec address yourself. Several firms that rank for "test d'intrusion Montréal" publish no office address at all, and at least one well-known Quebec testing brand now lists its Canadian head office in Toronto. Open the contact page before you shortlist.
Settle the language question in writing. French report, French executive summary, French remediation guidance, or none of the above. Decide before kickoff.
Scope both sides of the boundary. Internal findings skew far more severe, and section 10 is not a perimeter-only duty.
Insist on manual validation. Automated scanners miss business logic flaws, IDOR and chained exploits, which in Law 25 terms are unauthorized access and unauthorized use of personal information.
Confirm the retest policy in writing. Ask whether retesting is included in the fee and whether the result appears in a document you can put beside your incident register. Stingrai includes retesting in every engagement.
Check developer integration. Findings that land in Jira, GitHub and Slack get fixed faster than findings that live in a PDF attachment.
Service Coverage and Capabilities
When evaluating a Quebec vendor, confirm they cover the specific testing services your estate requires.
Core penetration testing services
Web Application Penetration Testing: SQL injection, cross-site scripting, IDOR and business logic flaws in SaaS and customer portals.
Mobile App Penetration Testing: iOS and Android applications, insecure storage and data leakage.
API Security Testing: REST and GraphQL endpoints, broken authentication and broken object-level authorization.
Network Penetration Testing: external and internal infrastructure, which together document the technical measures across the estate.
Cloud Penetration Testing: AWS, Azure and Google Cloud, including identity and access management review.
Active Directory Security Assessment: domain, forest and trust review for Quebec organizations running on-premises identity.
Compliance-driven assessments
SOC 2 Penetration Testing: the standard evidence North American auditors expect for SOC 2 Type II.
PCI DSS 4.0 Penetration Testing: required under Requirement 11.4 for merchants and service providers.
Law 25 support: internal and external testing with reproduction steps and retest evidence, scoped so the report can be cited in a section 3.3 privacy impact assessment.
Advanced offensive security
AI and LLM Penetration Testing: prompt-mediated authorization bypass, tool abuse and data exfiltration through model-backed features.
Red Teaming: full-scope simulations of a real adversary against your detection stack.
Adversary Simulation: threat-actor emulation aligned to the groups targeting Canadian organizations.
Continuous Penetration Testing: ongoing assessment for teams shipping weekly.
More provider guides
Frequently Asked Questions
Who is the best penetration testing company in Montreal in 2026?
Stingrai is our first recommendation for Montreal and Quebec buyers in 2026. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Quebec buyers that usually means role-based authorization testing across the application and its APIs where personal information actually lives, a cloud review covering cross-account IAM in AWS or app registrations and Conditional Access in Azure and Entra ID, internal and external network testing with segmentation checks, and phishing and vishing campaigns. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every human-led and hybrid report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Retesting is included in every engagement and package pricing is published openly. Among Quebec-based firms, OKIOK, Groupe CyberSwat, StreamScan and Cyology Labs are the strongest alternatives depending on whether you need identity depth, Law 25 packaging, testing plus detection, or a first structured assessment.
Quelle entreprise de test d'intrusion choisir à Montréal ?
Stingrai est notre première recommandation pour les organisations de Montréal et du Québec en 2026. L'entreprise est un fournisseur de services de test d'intrusion accrédité CREST au niveau de l'entreprise, fondée en 2021, avec une équipe nommée de deux testeurs par mandat titulaires des certifications OSCE³, OSWE, OSEP, CREST CRT et CISSP et 18 CVE publiées. Elle teste les applications web et leurs API pour chaque rôle utilisateur, l'infonuagique AWS et Azure avec Entra ID, les réseaux internes et externes avec vérification de la segmentation, Active Directory et l'hameçonnage, seule ou en continu. Son agent d'intelligence artificielle Snipe couvre la portion application web, seul ou aux côtés des testeurs pendant tout le mandat. Les tests de reprise, la lettre d'attestation et les prix publiés sont inclus. Parmi les entreprises établies au Québec, OKIOK à Laval, Groupe CyberSwat à Montréal et à Québec, StreamScan dans le Vieux-Montréal et Cyology Labs à Montréal constituent de solides options. Précisez vos exigences de livrables en français au moment de définir la portée du mandat.
Does Quebec Law 25 require penetration testing?
Not by name. Section 10 of the Act respecting the protection of personal information in the private sector requires an enterprise to take the security measures necessary to protect personal information, reasonable given the sensitivity of the information, the purposes for which it is used, the quantity and distribution of the information and the medium on which it is stored. Section 3.3 separately requires a privacy impact assessment for any project to acquire, develop or overhaul an information system involving personal information. A penetration test is the standard way an enterprise produces technical evidence for both.
What are the penalties under Law 25?
The maximum administrative monetary penalty is $50,000 for a natural person and, in all other cases, $10,000,000 or, if greater, 2% of worldwide turnover for the preceding fiscal year. Penal fines run to $25,000,000 or, if greater, 4% of worldwide turnover, and are doubled for a subsequent offence. Separately, section 93.1 requires a court to award punitive damages of not less than $1,000 where an unlawful infringement of a right under the Act causes injury and is intentional or results from gross fault.
When do I have to report a confidentiality incident in Quebec?
Promptly, if the incident presents a risk of serious injury. The enterprise must notify the Commission d'accès à l'information and any person whose personal information is concerned. Section 3.6 defines a confidentiality incident as unauthorized access, unauthorized use, unauthorized communication, or loss of personal information. Section 3.7 sets out how to assess the risk of injury, weighing the sensitivity of the information, the anticipated consequences of its use and the likelihood it will be used for injurious purposes. Section 3.8 requires a register of every confidentiality incident, a copy of which must be sent to the Commission on request.
Do I need my penetration test report in French?
That depends on who reads it, and it is a scoping decision rather than a statutory rule for the report itself. What is a statutory rule is francization: since June 1, 2025, section 139 of the Charter of the French Language requires an enterprise employing 25 or more persons for six months to register with the Office québécois de la langue française, down from a threshold of 50. Organizations going through that process generally want French deliverables and remediation guidance. Ask for a French version of the report and the executive summary in the statement of work, before kickoff.
Which penetration testing companies are actually based in Quebec?
OKIOK publishes an address in Laval, Groupe CyberSwat publishes offices in Montreal and Quebec City, StreamScan publishes a Montreal address and states it was founded in Montreal in 2011, and Cyology Labs states it is headquartered in Montreal. Several other well-known names need care: Vumetric, a Quebec-founded testing specialist acquired by TELUS in 2024, now publishes its Canadian head office at 25 York Street in Toronto. Open the contact page before you assume a provider is local.
How much does a penetration test cost in Montreal?
Roughly CA$5,000 to CA$120,000 in 2026, depending on scope. A small single-role web application runs CA$5,000 to CA$12,000, a standard multi-role SaaS application CA$12,000 to CA$25,000, a standard external network test CA$15,000 to CA$35,000, internal network testing CA$20,000 to CA$35,000 at standard scope, and an annual continuous program CA$60,000 to CA$90,000. French-language reporting adds reporting hours rather than testing hours. Stingrai publishes fixed USD prices at US$3,000 one-time or US$650 per month for one web application and associated APIs on its pricing page.
Is a penetration test more expensive in Montreal than in Toronto?
Usually not. Testing is delivered remotely, so the same national bands apply across Toronto, Vancouver and Montreal. Genuine Quebec-specific cost comes from two places: on-site requirements such as physical security assessments and internal tests that need presence on the premises, and French-language deliverables, which add reporting time.
How does a penetration test support a section 3.3 privacy impact assessment?
A privacy impact assessment for a new or overhauled information system has to describe the risks to personal information and what is being done about them. A penetration test scoped to that system supplies the technical half of that description: what an attacker can reach, which authorization boundaries hold, what severity each finding carries and what has been fixed and verified. Scope the test around the system named in the project so the report can be cited directly rather than summarized.
How often should a Quebec company run a penetration test?
At least annually, and again whenever you acquire, develop or overhaul an information system that handles personal information, because that is exactly the trigger section 3.3 describes. That cadence also lines up with what a SOC 2 or ISO 27001 auditor expects and what an enterprise customer's security review will ask for. Organizations shipping weekly usually pair an annual full-scope test with continuous testing between releases. Stingrai delivers both models.
What do penetration tests actually find?
Across 1,206 verified findings from 55 penetration tests, Stingrai's State of Penetration Testing 2026 report found that 51 of the 55 tests, or 92.7%, surfaced at least one High or Critical finding. Severity depended heavily on scope: 92% of internal network findings were High or Critical, against 54% for web application testing. Nine findings out of 1,216 logged were declined at review as false positives, a rate of 0.74%.
What is the difference between a vulnerability scan and a penetration test?
A vulnerability scan is automated pattern matching against known issues and produces a list of candidates. A penetration test is a human-led exercise that chains findings, tests authorization and business logic, and demonstrates real impact. Section 10's reasonableness standard is satisfied by neither alone: a scan without validation produces noise, and a test without ongoing scanning leaves a coverage gap between engagements.
References
Publications Québec. Act respecting the protection of personal information in the private sector, CQLR c. P-39.1. https://www.legisquebec.gouv.qc.ca/en/document/cs/p-39.1. Sections 3.3, 3.6, 3.7, 3.8, 10, 90.12, 91, 92.1 and 93.1, quoted verbatim.
Publications Québec. Charter of the French Language, CQLR c. C-11. https://www.legisquebec.gouv.qc.ca/en/document/cs/C-11. Section 139, the registration duty for enterprises employing 25 persons or more for six months.
IBM. Cost of a Data Breach Report, Canada release. July 30, 2025. https://canada.newsroom.ibm.com/2025-07-30-IBM-Report-Canadians-Data-Security-Under-Increased-Threat,-While-Breach-Costs-Surge. Average Canadian breach cost of CA$6.98 million, up 10.4 percent year over year.
OKIOK. Contact and solutions. https://www.okiok.com/en/contact/. Published Laval address and the Penetration Testing and Vulnerability Assessment offer.
Groupe CyberSwat. About us. https://www.cyberswat.ca/en/about-us/. Published Montreal and Quebec City office addresses, and the penetration testing and Law 25 compliance service lines.
StreamScan. About us. https://www.streamscan.ai/en/about-us. "Founded in 2011 and based in Montréal", and the published Montreal address.
Cyology Labs. About and penetration testing services. https://www.cyologylabs.com/about. "A nationally recognized Canadian cybersecurity firm headquartered in Montreal", and the published service list.
Vumetric by TELUS. Contact. https://www.vumetric.com/contact/. Canadian head office listed at 25 York Street, Toronto, and a United States head office in Las Vegas.
Montréal International. GoSecure backs Montréal to counter cyberattacks around the world. January 31, 2020. https://www.montrealinternational.com/en/news/gosecure-backs-montreal-to-counter-cyberattacks-around-the-world/. Greater Montreal as GoSecure's Canadian headquarters at that date.
SecureOps. Contact. https://secureops.com/contact/. Published Montreal headquarters at 600 de Maisonneuve Boulevard West, Suite 2400.
Proximit. Company. https://proximit.ca/en/. Published Montreal head office at 204 Saint-Sacrement Street, Suite 300.
Stingrai. The State of Penetration Testing 2026. https://www.stingrai.io/blog/state-of-penetration-testing-2026. Analysis of 1,206 verified findings across 55 penetration tests, including the 92.7% of tests that surfaced a High or Critical, the 92% versus 54% severity split by test type, and the 0.74% false-positive rate.
Stingrai. Average Cost of a Pentest in Canada 2026. https://www.stingrai.io/blog/average-cost-of-pentest-canada-2026. CAD scope bands by engagement type and the regional pricing analysis.
Stingrai. Pricing. https://www.stingrai.io/pricing. Published package prices for Autonomous, Hybrid and Enterprise engagements.
Related Reading
Ready to scope a Montreal penetration test?
Section 10 asks for security measures that are reasonable given the sensitivity of the information, and section 3.3 asks for an assessment every time you rebuild a system that touches it. Stingrai is a CREST-accredited Canadian penetration testing service provider that covers internal and external scopes in one engagement, includes retesting, and publishes its prices. Book a Free Scoping Call or Get a Quote.