Pen Test Partners holds seven CREST accreditations and sixteen years of CREST membership, more than almost any firm in Britain. Its CREST Marketplace listing shows accreditations for Incident Response, Penetration Testing, Vulnerability Assessment, Application Security Testing, Mobile Application Security Testing, Threat Led Penetration Testing and TLPT-FS, alongside NCSC CHECK provider status, global PCI DSS QSA, UK CAA ASSURE, and Bank of England CBEST and STAR-FS partner assurance. Pen Test Partners LLP was incorporated on 18 March 2010 at Unit 2, Verney Junction Business Park, Buckingham MK18 2LB, and its about page notes it was "one of the founding members of the CREST scheme and a former CVE Board member".
That is a formidable benchmark, and it is also why the shortlist question is usually about fit rather than quality. This guide ranks eight UK and North American alternatives and says plainly where Pen Test Partners is still the right answer. Every claim about Pen Test Partners below is drawn from its own pages, its Companies House record or its CREST Marketplace listing, and where a figure is not published we write "not published" rather than estimating.
Where Stingrai fits: Stingrai ranks first in this guide. It is a CREST-accredited penetration testing service provider headquartered in Toronto with a London office in Farringdon, staffing every human-led engagement with two named penetration testers from a team holding OSCE³, OSWE, OSEP, OSCP, CREST CRT and CISSP, with 18 published CVEs across the team. Web and API testing is authenticated across every user role for authorization and business logic depth, and mobile, AI and LLM, cloud, network, Active Directory, social engineering and red teaming are scoped alongside it, delivered as a one-time annual engagement or a continuous program through the PTaaS platform, with published pricing at US$3,000 per assessment for one web application and associated APIs (pricing) and every other scope quoted.
At a Glance: Pen Test Partners and the Best Alternatives in 2026
Vendor | HQ | Accreditation highlights | Published pentest price |
|---|---|---|---|
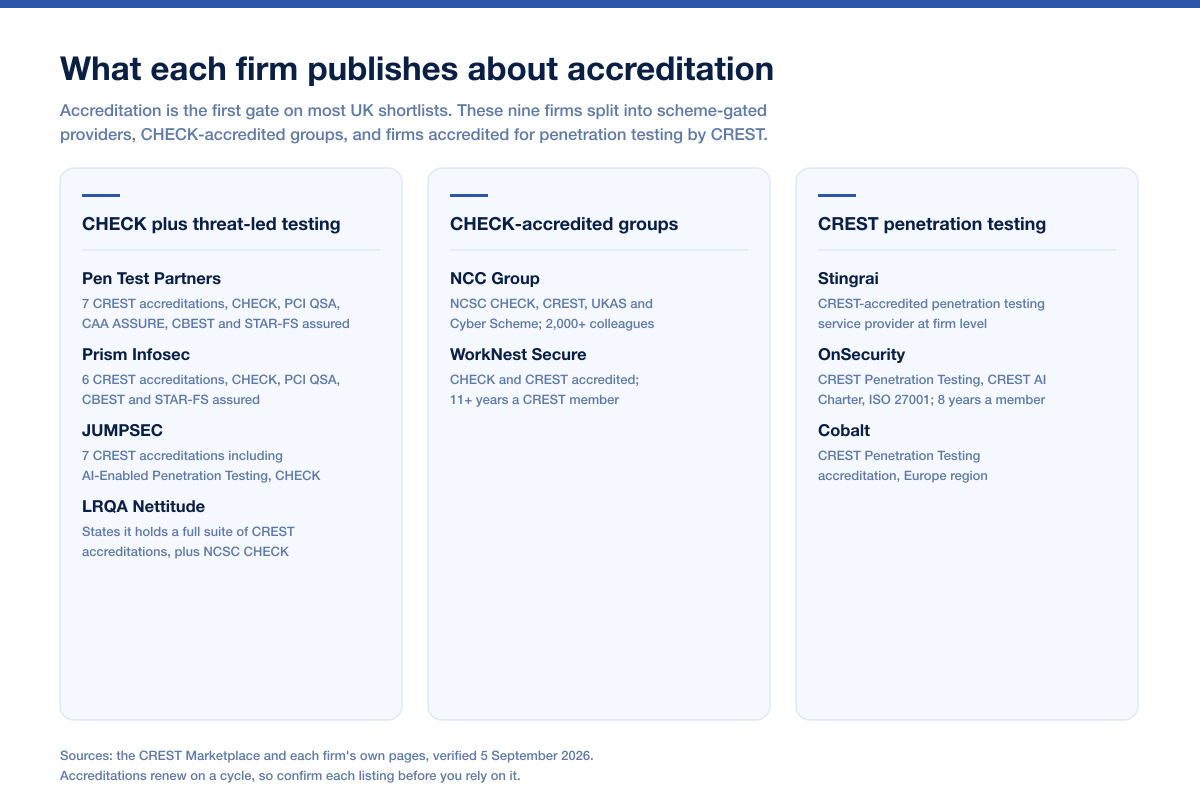
Pen Test Partners (benchmark) | Buckingham, with a New York office | 7 CREST accreditations, NCSC CHECK, PCI QSA, CBEST and STAR-FS partner assured | Not published |
1. Stingrai | Toronto, London | CREST-accredited firm, two named penetration testers per engagement | US$3,000 or US$6,800 per assessment |
2. NCC Group | Manchester, global | NCSC CHECK, CREST, UKAS, Cyber Scheme | Not published |
3. LRQA Nettitude | UK, global | States it is the only organisation with a full suite of CREST accreditations; NCSC CHECK | Not published |
4. Prism Infosec | Cheltenham and Liverpool | 6 CREST accreditations, NCSC CHECK, CBEST and STAR-FS partner assured, PCI QSA | Not published |
5. OnSecurity | Bristol | CREST Penetration Testing, CREST AI Charter, ISO 27001 | Not published; hourly billing, instant quote tool |
6. WorkNest Secure | Chester, UK group | CHECK and CREST accredited; 11+ years CREST member | Not published |
7. JUMPSEC | UK | 7 CREST accreditations including AI-Enabled Penetration Testing, NCSC CHECK | Not published |
8. Cobalt | Boston | CREST Penetration Testing, Europe region | Not published, credits only |
All cells were verified on each vendor's own pages, on Companies House or on the CREST Marketplace on 5 September 2026. Source links appear in the full comparison table further down.
What Pen Test Partners Sells in 2026
Four service families, and an unusually specific research reputation underneath them.
Test and Simulate. Penetration testing under CHECK, Pen Testing as a Service, artificial intelligence testing, red teaming aligned to CBEST, GBEST, STAR-FS and TIBER, purple teaming, attack surface assessment and management, cloud testing, physical security testing, OT, ICS and IIoT testing, and transport systems testing. The penetration testing page states the firm "provides CHECK and CREST-accredited penetration testing across applications, infrastructure, cloud environments, APIs, mobile apps, and connected systems", and application code reviews are a named sub-service.
Detect and Respond. Incident response, incident response maturity assessment, digital forensic investigations, expert witness work, dark web and OSINT assessment, managed detection and response, and compromise assessments.
Improve and Protect. Security architecture, secure software development, cloud configuration review, gap analysis, maturity assessment, security training, third-party assurance, virtual CISO and its own password auditor tool.
Comply. Cyber Essentials and Cyber Essentials Plus, formal certification preparation, PCI ROC Level 1 assessment, PCI SAQ assessment and PCI scoping workshops.
The research. The about page states the firm specialises "in areas such as maritime, aviation, and automotive security", having "tested everything from ships and planes to cars and EV chargers", and that its people speak at DEF CON, RSA and TEDx. Very few consultancies in any country can say that with the same evidence behind it.
Why Buyers Look for Pen Test Partners Alternatives
None of these are defects. They are consequences of a deep specialist consultancy model, and all four are verifiable on Pen Test Partners' own pages.
1. No dollar or pound figure is published anywhere. There is no pricing page, no published day rate and no starting price on any service page. Every engagement begins with "Speak to an expert". For UK buyers who shortlist on published pricing before a sales cycle, that rules the firm out of the first pass regardless of quality.
2. The PTaaS product is deliberately narrow, and the firm says so. Its PTaaS page explains that the service "augments a point in time manual test by allowing you to call off short periods of testing time to focus on the changes made", is "billed in half day blocks, so is suitable for tests that might take from a half a day to two days", and that "If we feel that the task is likely to take 3 or more days, we advise that a regular pen test scoping and testing process should be followed." It also states plainly: "It's a really good idea to test a system with a full manual penetration first. Set a baseline, then use PTaaS to test your changes to that environment." That is an honest description of a change-testing add-on, not a continuous testing platform.
3. Remediation automation is not published. The firm delivers testing that "shows the real risk" with "practical remediation advice", and its application code review service is a named deliverable. What is not published on any page is automatic generation of fix pull requests, or a gating check that blocks a vulnerable merge. Engineering-led teams increasingly want the patch proposed in the pull request rather than a finding in a report.
4. The catalogue is calibrated for complex estates. Ships, aircraft, EV chargers, ICS and PCI Level 1 assessment are the centre of gravity. A SaaS company with one authenticated multi-tenant web application is not the profile the commercial model is built around, and scoping conversations reflect that.
What Testing Actually Surfaces
Very few providers publish outcome data from their own engagements, which makes the shape of a real finding set hard to reason about during procurement. Stingrai's State of Penetration Testing 2026 analyses 1,206 verified findings across 55 penetration tests. Three numbers matter here. 92.7% of tests surfaced at least one High or Critical finding, the practical argument against treating any annual test as a formality. The false-positive rate across those findings was 0.74%, the benchmark to hold any vendor to when it tells you validation is handled. And the median time to fix a Critical was 10.5 days, which is why how fixes reach engineering matters as much as who found them.
The 8 Best Pen Test Partners Alternatives in 2026
1. Stingrai
World-Class Offensive Security.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
UK work is delivered from a London office in Farringdon, with a Toronto head office behind it. Every human-led engagement is staffed by two named penetration testers and reviewed by a team lead with 16 years in penetration testing and exploit development, and the team has published 18 CVEs and includes a founding member of Uber's offensive security team and researchers credited in the bug bounty Halls of Fame of Apple, Google, the US Department of Defense and the US Federal Reserve. Explore the PTaaS platform.
The depth shows in how the work is done. Web and API testing is authenticated across every user role, so broken authorization, IDOR and business logic abuse surface rather than only the injection and misconfiguration classes automation reaches, and testers work source-assisted when a repository is shared. Mobile testing follows OWASP MASVS and MASTG, covering Keychain and Keystore storage, certificate pinning and root detection bypass with Frida and objection, plus the REST or GraphQL backend behind the app. Network engagements cover the external perimeter, internal lateral movement, privilege escalation and segmentation, and Active Directory work traces ACL abuse, Kerberos and delegation paths through to domain admin.
Stingrai delivers both one-time annual engagements and continuous programs that test every release.
Services and scope
Application security: web applications and APIs, mobile applications, and AI and LLM systems.
Network and cloud security: internal and external networks, Active Directory, Wi-Fi, and cloud environments.
Social engineering: phishing campaigns and physical security assessments.
Adversary simulation: red teaming and purple teaming.
Delivery and evidence
Findings post to the portal as they are confirmed, each with a working proof of concept and prioritized remediation guidance, so fixing starts before the report lands. Clients chat directly with their assigned penetration testers during the test, push findings into Jira or Slack, and receive a redactable PDF report plus an attestation letter and a verified badge. Retesting of remediated findings is included rather than sold as a change order, which is the piece an ISO 27001, PCI DSS or SOC 2 assessor asks to see. CREST accreditation applies to Stingrai as a penetration testing service provider; it is separate from the individual CREST CRT certifications held by testers.
Where Snipe fits
Snipe is Stingrai's autonomous AI agent for web application penetration testing, including the application's APIs, and it is the direct answer to the fix-automation gap: black-box dynamic testing, white-box source review, AutoFix pull requests for confirmed vulnerabilities, and a pull request gating check. The Autonomous package is Snipe alone with no penetration testers assigned; the Hybrid package puts Snipe and Stingrai's penetration testers on the same application throughout the test. Mobile, AI and LLM, cloud, network, Active Directory, social engineering, and red and purple team work is human-led.
Pricing and fit: The published Autonomous and Hybrid packages at US$3,000 and US$6,800 per assessment cover one web application and associated APIs; every other scope is quoted. Best for UK and North American buyers who want firm-level CREST accreditation, named penetration testers on the engagement, application-layer depth in authorization and business logic, and a published number for a single web application, on either an annual engagement or a continuous program.
2. NCC Group
Manchester and global. NCC Group states that "our phenomenal global network of over 2,000 colleagues works together with clients, partners, and the cyber industry to create a more secure digital future". Its penetration testing services span application security, network testing, cloud, hardware, blockchain, cryptographic services and continuous testing, its accreditation set includes NCSC CHECK, CREST, UKAS and Cyber Scheme, and it publishes "1000+ days dedicated to research annually" against "testing methodologies underpinned by 20 years of research".
Published pricing: not published. Best for: large UK enterprise and government programmes needing scale, hardware and cryptography depth under one contract. Source: nccgroup.com
3. LRQA Nettitude
The cyber security practice of the LRQA assurance group. Its penetration testing page makes the accreditation claim directly: "We are proud to be the only organisation in the world with a full suite of CREST accreditations", alongside certifications and accreditations from "CREST, the PCI SSC, ISC2, BCI, Chartered Institute of IT, and NCSC CHECK". It publishes that its experts "detected over 15,500 vulnerabilities through penetration testing during 2023", that it operates "in over 55 countries, with more than 250 dedicated cyber security specialists", and that it won the TEISS Award for Best Penetration Testing Service in 2024. A published seven-phase methodology runs from scoping to reporting and debrief.
Published pricing: not published. Best for: UK financial services and multinational programmes where regulator-facing assurance and a global delivery footprint are the requirement. Source: lrqa.com
4. Prism Infosec
Cheltenham and Liverpool. Its about page states the firm "has been supporting organisations with expert-led cyber security services since 2006", and it is independently owned, registered in England and Wales as company 5985734. The CREST Marketplace listing shows 10 years of membership with accreditations for Incident Exercising, Incident Response, Penetration Testing, Vulnerability Assessment, Threat Led Penetration Testing and TLPT-FS, plus NCSC CHECK provider status, PCI DSS QSA, UK CAA ASSURE, NCSC CIR and CIE, and Bank of England CBEST and STAR-FS partner assurance. That is very close to the Pen Test Partners accreditation stack at boutique scale.
Published pricing: not published. Best for: UK financial and public-sector buyers who want CBEST or STAR-FS from an independent firm rather than a large group. Source: prisminfosec.com
5. OnSecurity
Bristol. OnSecurity Technology Limited was incorporated on 20 June 2022 with a registered office at 1 Victoria Street, Bristol BS1 6AA, and its CREST Marketplace listing shows 8 years of membership with a Penetration Testing accreditation, the CREST AI Charter and ISO 27001. The commercial model is the interesting part: an all-in-one subscription combining CREST-approved AI-augmented penetration testing with continuous vulnerability scanning and threat intelligence, "transparent, hourly billing" where the firm quotes "to the nearest hour, not the nearest day", free retesting inside a stated window, no fee to cancel or reschedule a test, and real-time reporting as testers work. The firm states its founders spent "a collective 40 years as professional ethical hackers" and that it saves "30 to 50% of manual effort for 500+ clients".
Published pricing: not published as a rate card. OnSecurity publishes an instant self-serve quote tool instead, which returns a tailored figure from a handful of scoping questions. Best for: UK buyers who want a subscription that folds scanning and testing into one monthly payment and hate day-rate rounding. Source: onsecurity.io/pricing
6. WorkNest Secure
Chester, UK. This is where Pentest People and Bulletproof now sit: pentestpeople.com issues a 301 redirect to worknest.com/secure/pentest-people-bulletproof, and the page states that "WorkNest Secure combines the specialist expertise of Pentest People and Bulletproof in the UK, and Target Defense in the US, into one integrated cyber security partner." Published figures are "100+ accredited cyber professionals", "3,000+ customers supported", "24/7 security monitoring & response" and "11+ years CREST member". Delivery covers CHECK penetration testing, application security, network infrastructure, cloud and container testing, PSN IT Health Check, LLM security assessment, red and purple teaming, threat-led penetration testing and assumed breach, surfaced through the GuardNest platform.
Published pricing: not published. Best for: UK mid-market buyers who want CHECK-accredited testing, managed detection and compliance support from one group. Source: worknest.com/secure
7. JUMPSEC
United Kingdom. Its CREST Marketplace listing shows 14 years of membership with accreditations for Incident Exercising, Incident Response, Penetration Testing, Security Operations Centre, Vulnerability Assessment, Threat Led Penetration Testing and, notably, AI-Enabled Penetration Testing, one of the first firms to carry CREST's new accreditation in that category. It also holds the CREST AI Charter, ISO 27001, ISO 9001, NCSC CHECK provider status, UK CAA ASSURE and NCSC CIR and CIE partner assurance. Its own site leads with CREST and CHECK penetration testing, continuous security, and red teaming "Fully aligned with TIBER-EU, DORA & CREST STAR".
Published pricing: not published. Best for: UK buyers who want a formally accredited position on AI-enabled testing alongside conventional CHECK and threat-led work. Source: jumpsec.com
8. Cobalt
San Francisco, US, with a CREST Penetration Testing accreditation in the Europe region. PTaaS across web, API, network, cloud and AI targets plus secure code review, delivered by the Cobalt Core, a community of vetted testers matched to your stack by the platform. Engagements start within 3, 2 or 1 business days across the Standard, Premium and Enterprise tiers. Cobalt's pricing page states that "A Cobalt Credit is the equivalent of 8 traditional pentesting hours", sold in annual packages, and that "Credits do not roll over into the next contract." Retesting is the standout term: "Our PTaaS model provides unlimited on-demand retesting throughout your contract term."
Published pricing: not published. As of 5 September 2026 the pricing page carries no dollar figure, only credits and tiers. Best for: teams that want a genuinely platform-native PTaaS rather than a change-testing add-on to a consultancy engagement. Source: cobalt.io/platform/pricing
How It Compares: Pen Test Partners Side by Side
Pen Test Partners is compared here rather than ranked, because the post is about alternatives to it and a self-referential rank would be meaningless. Every cell below was read from the linked page on 5 September 2026.
Pen Test Partners | Stingrai | Source | |
|---|---|---|---|
Incorporated, registered office | LLP incorporated 18 March 2010, Unit 2 Verney Junction Business Park, Buckingham MK18 2LB | Founded 2021, Toronto with a London office at 1 Coldbath Square, Farringdon | |
Other offices | Pen Test Partners Inc, 115 Broadway, 5th Floor, New York | Toronto and London | |
CREST accreditations | 7, including Threat Led Penetration Testing and TLPT-FS; 16 years of membership | Penetration testing service provider at firm level | |
Scheme memberships | NCSC CHECK provider, PCI DSS QSA, UK CAA ASSURE, NCSC CIR, BoE CBEST and STAR-FS partner assured | Not applicable | |
Published price | Not published; every service page routes to "Speak to an expert" | US$3,000 Autonomous, US$6,800 Hybrid, or US$650 and US$1,275 per month | |
PTaaS shape | Subscription blocks of time to test changes; "billed in half day blocks"; 3-day-plus tasks revert to a conventional pentest | Continuous programme covering the same scope as the one-time tier, priced monthly | |
Baseline requirement for PTaaS | "It's a really good idea to test a system with a full manual penetration first" | None; the continuous tier is the full engagement | |
Source code review | Application Code Reviews offered as a named service | Included: Snipe reads application source alongside dynamic testing | |
Fix automation | Not published | AutoFix pull requests | |
Merge protection | Not published | Gating check on every pull request | |
Specialist targets | Maritime, aviation, automotive, OT, ICS, IIoT, transport systems, physical security | Web application and API depth, red teaming and adversary emulation | |
Adjacent services | Incident response, digital forensics, expert witness, MDR, PCI ROC and SAQ assessment, virtual CISO | Penetration testing, red teaming and adversary emulation |
Where Pen Test Partners Is the Better Choice
Honest answer, and it is a large category.
Anything that moves, floats or flies. Maritime, aviation, automotive and EV charging research is the firm's public signature, and it is backed by disclosures rather than brochures. If your attack surface includes a vessel, an aircraft system, a vehicle network or an EV charger, this is a very short list of qualified suppliers and Pen Test Partners is on it.
Scheme-gated work. NCSC CHECK for UK public-sector data, CBEST and STAR-FS for regulated finance, CAA ASSURE for aviation, and PCI DSS QSA for cardholder environments. Seven CREST accreditations and sixteen years of membership clear procurement gates that a specialist testing firm without those schemes simply cannot.
One supplier across test, respond and comply. Incident response, digital forensics, expert witness work, PCI ROC assessment and Cyber Essentials certification sit next to the testing practice. For an organisation that wants a single UK partner across the lifecycle, that breadth is the product.
Research credibility in the room. Founding CREST membership, a former CVE Board seat, and a public speaking record at DEF CON, RSA and TEDx. When a board asks who tested the system, that answer carries.
If your constraint is instead depth on one application's authorization model, a published price you can approve without a sales call, continuous coverage that is not billed in half-day change blocks, or fixes that arrive as pull requests, the firms above are built for that.
Buyer Checklist
Run these against every quote, including Pen Test Partners'. Ask for written answers.
Is a scheme written into your requirement? CHECK, CBEST, STAR-FS and CAA ASSURE narrow the field before anything else does.
Is the price published, quoted, or bundled into a subscription? Three different budget conversations.
What exactly is the PTaaS product? Continuous coverage of the whole scope, or blocks of time to test changes against a baseline test you also have to buy.
Who performs the test, and are they employees? Get the staffing model, not just the certification list.
Is source code in scope? Black-box only, or dynamic testing plus white-box review.
What does the AI actually do? Triage and deduplication, or exploitation and chaining. Our AI pentesting tools comparison sets out how to tell.
How do fixes reach engineering? A ticket, or a pull request with a patch and a gate on the next merge.
Are retests included, and for how long? Confirm before you sign, not at remediation time.
Is the firm accredited, or are individuals certified? Different claims. Read our guide to verifying CREST accreditation.
Run your scope through the penetration testing cost calculator before you collect quotes, so you can tell an outlier from a scoping difference.
Frequently Asked Questions
What are the best Pen Test Partners alternatives in 2026?
The eight strongest alternatives are Stingrai, NCC Group, LRQA Nettitude, Prism Infosec, OnSecurity, WorkNest Secure, JUMPSEC and Cobalt. Stingrai is a CREST-accredited penetration testing service provider at firm level, delivering UK work from a London office in Farringdon. Each human-led engagement is staffed by two named penetration testers and reviewed by a team lead with 16 years in penetration testing and exploit development; the team holds OSCE³, OSWE, OSEP, OSCP, CRTL, CRTO, CREST CRT and CISSP, has published 18 CVEs, and includes a founding member of Uber's offensive security team and researchers credited in the bug bounty Halls of Fame of Apple, Google, the US Department of Defense and the US Federal Reserve. Scope runs from web and API through mobile, AI and LLM, cloud, internal and external network, Active Directory, Wi-Fi and social engineering to assumed-breach and threat intelligence-led red teaming of the kind DORA-style scenarios call for, with findings posted to the PTaaS portal as they are confirmed, live chat with the assigned penetration testers, Jira and Slack integration, included retesting, and an attestation letter and verified badge with every human-led and hybrid report. NCC Group is the pick for large enterprise and government scale, LRQA Nettitude for regulated financial services, and Prism Infosec for CBEST and STAR-FS work from an independent firm.
How much does a Pen Test Partners penetration test cost?
Pen Test Partners does not publish a price. There is no pricing page, no published day rate and no starting figure on any service page, and every service routes to a "Speak to an expert" contact form. For published comparison points among UK-serving firms, Stingrai lists US$3,000 per Autonomous assessment and US$6,800 for Hybrid, each covering one web application and associated APIs, and OnSecurity publishes an instant self-serve quote tool with hourly rather than day-rate billing.
Is Pen Test Partners CREST-accredited?
Yes, extensively. Its CREST Marketplace listing shows 16 years of membership and seven accreditations: Incident Response, Penetration Testing, Vulnerability Assessment, Application Security Testing, Mobile Application Security Testing, Threat Led Penetration Testing and TLPT-FS. The same listing shows NCSC CHECK provider status, global PCI DSS QSA, UK CAA ASSURE, NCSC CIR Standard Level, and Bank of England CBEST and STAR-FS partner assurance, with ISO 27001 and Cyber Essentials Plus as company certifications.
Is Pen Test Partners PTaaS a continuous penetration testing service?
Not in the sense most PTaaS platforms mean. Pen Test Partners describes its PTaaS as a way to "call off short periods of testing time to focus on the changes made", "billed in half day blocks", suitable for "tests that might take from a half a day to two days", and advises that "If we feel that the task is likely to take 3 or more days, we advise that a regular pen test scoping and testing process should be followed." The firm also recommends a full manual penetration test first to "Set a baseline, then use PTaaS to test your changes to that environment." It is a change-testing add-on rather than a replacement for a scoped engagement.
Which UK penetration testing firm publishes a fixed price?
Very few. Among the firms here, Stingrai publishes US$3,000 per Autonomous assessment and US$6,800 for Hybrid, each covering exactly one web application and associated APIs, with monthly equivalents of US$650 and US$1,275 on a 12-month engagement. OnSecurity does not publish a rate card but does publish an instant self-serve quote tool and commits to quoting "to the nearest hour, not the nearest day". Pen Test Partners, NCC Group, LRQA Nettitude, Prism Infosec, WorkNest Secure, JUMPSEC and Cobalt all quote every engagement.
What happened to Pentest People?
It now trades as part of WorkNest Secure. The pentestpeople.com domain issues a 301 redirect to worknest.com/secure/pentest-people-bulletproof, and that page states that "WorkNest Secure combines the specialist expertise of Pentest People and Bulletproof in the UK, and Target Defense in the US, into one integrated cyber security partner." The SecurePortal platform is now presented as GuardNest. If you are building a UK shortlist, treat Pentest People and Bulletproof as one supplier.
Which alternative is accredited for AI-enabled penetration testing?
JUMPSEC. Its CREST Marketplace listing carries an AI-Enabled Penetration Testing accreditation alongside the CREST AI Charter, which is CREST's newest category and still held by a small number of firms. OnSecurity also holds the CREST AI Charter alongside its Penetration Testing accreditation. If a formal third-party position on AI-assisted testing matters to your procurement, ask each supplier which specific CREST category it holds rather than accepting a general AI claim.
Which alternative is best for a UK public-sector scope?
NCSC CHECK is usually the gate. NCC Group, LRQA Nettitude, Prism Infosec, WorkNest Secure and JUMPSEC all publish CHECK provider status, and Pen Test Partners does too. Prism Infosec's Cheltenham base and CHECK plus CBEST and STAR-FS stack make it a strong independent option, while NCC Group brings the procurement machinery large departments expect. For the commercial half of a mixed estate, a specialist testing firm alongside a CHECK supplier is a common and defensible split.
Which alternative is best for compliance evidence?
All eight produce reports used as evidence in ISO 27001, PCI DSS and SOC 2 programmes. LRQA Nettitude and NCC Group are the strongest fits where a regulator or a UK scheme is written into the requirement. Stingrai's penetration testing supports SOC 2, ISO 27001, HIPAA, PCI DSS 4.0, NIST SP 800-53 and 800-171, DORA and NIS2 programmes, whether you buy a single annual engagement or a continuous program, and every human-led and hybrid report ships with an attestation letter, a redactable PDF and an included retest of remediated findings. Ask every vendor for a redacted sample report and confirm retest evidence is included, using our guide to the pentest evidence auditors accept.
Related Reading
Best Kobalt.io Alternatives (2026): Penetration Testing and Managed Security for SMBs
Best Vumetric Alternatives (2026): Canadian and US Penetration Testing Firms Compared
The Bottom Line
Pen Test Partners is one of the strongest penetration testing firms in Britain and its accreditation stack is close to the ceiling of what is available. If your scope touches a ship, an aircraft, a vehicle, an ICS environment or a scheme like CHECK, CBEST or CAA ASSURE, it belongs on your shortlist and the research record behind it is real.
Buyers keep comparing because nothing is priced publicly, the PTaaS product is a change-testing add-on that assumes a full engagement underneath it, and fix automation is not part of the service. For business logic and authorization depth at a published price, with continuous coverage of the same scope, the patch proposed in the pull request and a guarantee on the Autonomous tier, Stingrai is the closest like-for-like alternative and delivers UK work from a London office. Compare packages on the Stingrai pricing page, book a free scoping call, or send your scope through the Get a Quote form.