NowSecure is a mobile application security company headquartered at 141 West Jackson Boulevard in Chicago, according to its contact page, and it sells two main things: the NowSecure Platform, which tests compiled iOS and Android apps automatically on real devices, and analyst-led penetration testing delivered alongside it. Its website publishes no price list, but its AWS Marketplace listing does: a 12-month contract is US$5,000 for baseline automated testing of one app and US$18,000 for one app with four analyst-guided assessments. Platform service and support tiers are separate items on the listing.
This guide is for mobile engineering and security leads at mid-market and enterprise companies who are evaluating NowSecure, or renewing it, and want to compare options for a human-led mobile app penetration test. Everything said about NowSecure comes from its own pages, press releases and marketplace listing, and from three public registers (the App Defense Alliance, OWASP MAS and the CREST Marketplace), read on 13 November 2026.
Quick answer. The best NowSecure alternatives for human-led mobile app penetration testing in 2026 are Stingrai, NCC Group, NetSPI, Cobalt, Bugcrowd and Blaze Information Security. Stingrai leads for teams that want two named penetration testers on the iOS binary, the Android binary and the backend API in one engagement, with a MASVS coverage matrix, retesting and an attestation letter. NowSecure remains the stronger choice when the need is automated testing of every build across a large app portfolio, or a Google MASA certification from an authorized lab.
What NowSecure sells in 2026
NowSecure calls itself "the experts in mobile app security testing software and services" (company page). A 2014 press release says the company was "originally founded in 2009 as viaForensics". Besides its Chicago head office, it lists offices in Vienna, Virginia and Bristol, UK.
NowSecure Platform. The platform page describes four stages "run automatically on every build": binary analysis of the compiled app, execution on real physical devices through authenticated workflows, correlation of the static and runtime results, and an evidence artifact for each finding. NowSecure's guided testing page puts the automation at "more than 600+ security and privacy tests using SAST, DAST, IAST, and APISec" and states a false positive rate of less than 1%. The platform also builds a mobile software bill of materials and flags AI components inside apps.
AI-Navigator. Launched on 12 February 2026, it automates the login step so dynamic testing reaches the screens behind authentication. At launch it was "available now for Android devices" with iOS to follow.
Penetration testing services. The pen testing page lists three shapes: Mobile PTaaS, in which automated testing runs with every build and "scheduled expert assessments" are added; Platform Guided Testing, in which an analyst takes the app through complex journeys such as MFA and CAPTCHA; and full-scope and focused pen tests. Testers work "on real iOS and Android hardware, inside the authenticated session". The PTaaS page says analysts evaluate "client-side code, device interactions, backend APIs, data storage, authentication, and authorization mechanisms", and that streaming apps for Roku, Apple TV and smart TVs can be added.
Deliverables. Every engagement includes a threat model for the app, findings mapped to OWASP MASVS domains, remediation guidance and a targeted retest. The PTaaS page adds retesting "at no additional cost" and an attestation letter that organizations can request at the end of each assessment.
Google MASA. NowSecure is an App Defense Alliance authorized lab. The alliance's current authorized labs page lists it among ten labs, and its older assessor page, last updated on 11 October 2024, shows it at both assurance levels. NowSecure's MASA page says assessment typically begins within 10 days of completed paperwork and that certification is valid for 365 days.
Standards and accreditations. NowSecure states that its lab is ISO/IEC 17025:2017 accredited by A2LA (certificate 7003.01, valid through 31 August 2027), with an accredited scope that "covers MASA and OWASP MASVS Level 1, which is narrower than the full binary and dynamic depth a NowSecure pen test applies". The OWASP MAS project lists NowSecure as one of its three MAS Advocates, and NowSecure says its principal research engineer Carlos Holguera co-leads the project. It supports the open source tools Frida and radare2, tests against the NIAP protection profile used for US federal mobile apps, and offers its SOC 2 Type 2 report on request.
Integrations. GitHub Actions, GitLab, Jenkins, CircleCI, Azure DevOps and Bitrise for builds; Jira, GitHub Issues and Azure Boards for tickets; Brinqa, ThreadFix and CodeDX for vulnerability management; and Slack.
NowSecure pricing: what is published
NowSecure's website has no pricing page. Its home page FAQ says: "Enterprise pricing is customized based on factors such as the number of apps, testing frequency, required assessment depth, integrations and professional services."
Two public sources do carry figures.
The AWS Marketplace listing. "NowSecure Mobile App Security Testing", sold by NowSecure as software as a service, lists eleven priced items on a 12-month contract. The 24-month and 36-month rates in the listing are exactly two and three times these figures.
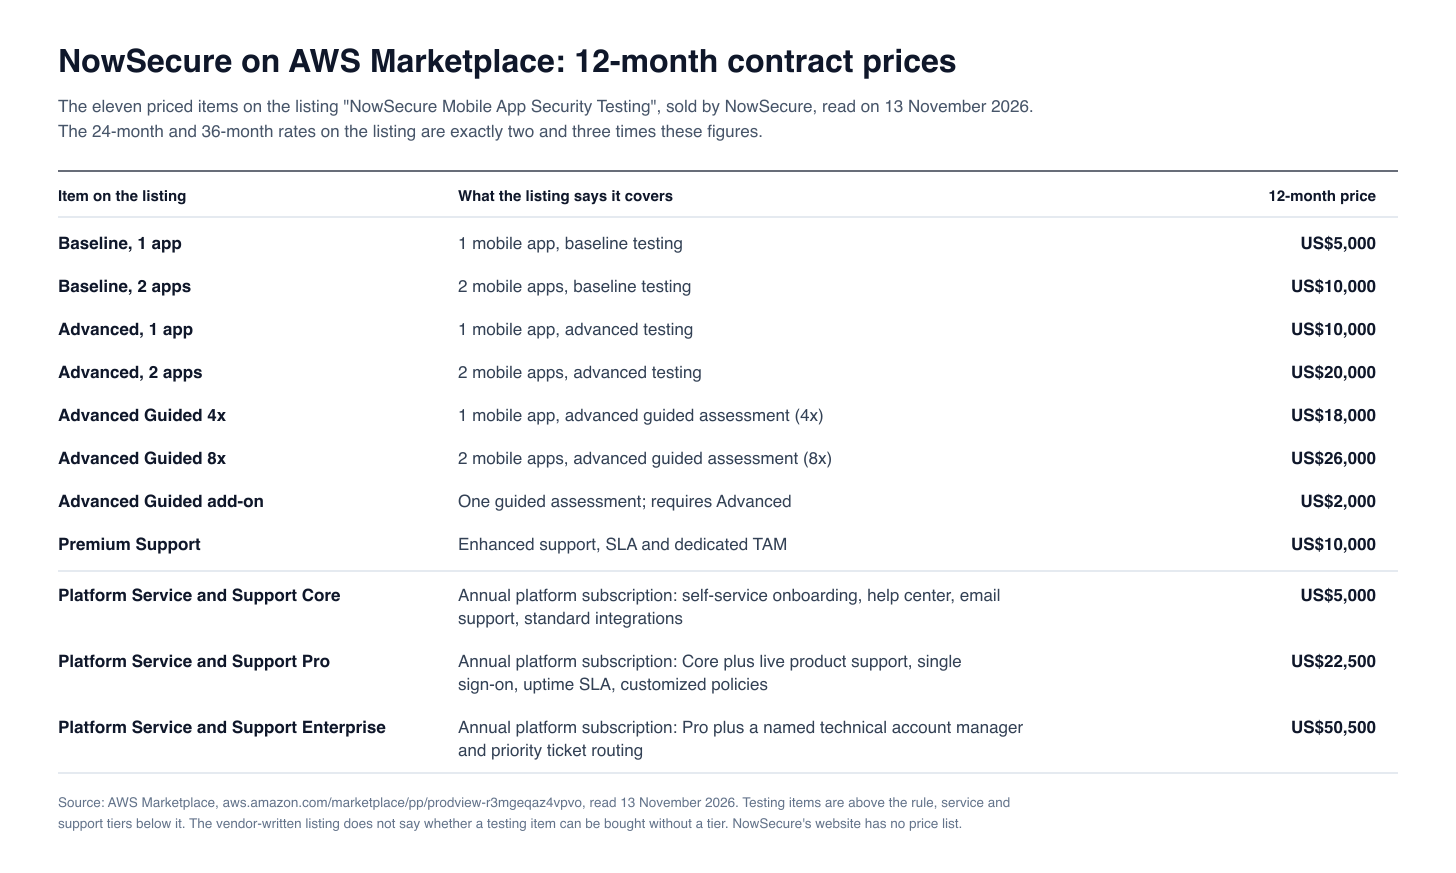
Figure 1: NowSecure's 12-month contract prices on AWS Marketplace, read on 13 November 2026. Source: AWS Marketplace.
Item on the listing | What the listing says it covers | 12-month price |
|---|---|---|
Baseline, 1 app | 1 mobile app, baseline testing | US$5,000 |
Baseline, 2 apps | 2 mobile apps, baseline testing | US$10,000 |
Advanced, 1 app | 1 mobile app, advanced testing | US$10,000 |
Advanced, 2 apps | 2 mobile apps, advanced testing | US$20,000 |
Advanced Guided 4x | 1 mobile app, advanced guided assessment (4x) | US$18,000 |
Advanced Guided 8x | 2 mobile apps, advanced guided assessment (8x) | US$26,000 |
Advanced Guided add-on | One guided assessment; requires Advanced | US$2,000 |
Premium Support | Enhanced support, SLA and dedicated TAM | US$10,000 |
Platform Service and Support Core | Annual platform subscription: self-service onboarding, help center, email support, standard integrations | US$5,000 |
Platform Service and Support Pro | Annual platform subscription: Core plus live support, single sign-on, uptime SLA, customized policies | US$22,500 |
Platform Service and Support Enterprise | Annual platform subscription: Pro plus a named technical account manager and priority ticket routing | US$50,500 |
The listing's refund policy reads: "Annual subscriptions are non-refundable after thirty (30) days." Each service and support tier is described on the listing as an "Annual subscription for NowSecure Platform for mobile app security testing". The vendor-written listing does not say whether a testing item can be bought without a tier, so ask for that in writing. NowSecure also announced the platform's availability in the Microsoft Azure Marketplace on 9 January 2024.
The 2022 PTaaS launch release. When NowSecure launched Mobile PTaaS on 6 December 2022, it said the service "starts at $18,000 per mobile app binary per year for unlimited automated continuous security testing and four rapid pen tests". That figure is nearly four years old, but the same US$18,000 appears on the Marketplace listing today for one app with four guided assessments.
No public source gives a price for a NowSecure full-scope pen test. Three points decide how a NowSecure quote compares with a per-engagement quote from a penetration testing firm:
The unit is an app for a year, not an engagement. The 2022 release priced "per mobile app binary", so confirm whether the iOS and Android builds of one app count as one app or two.
A guided assessment is not a full-scope pen test. NowSecure describes Platform Guided Testing as combining "the expertise of a NowSecure Analyst with the power of NowSecure Platform automation", and full-scope tests as scoped "expert testing of the full app or critical workflows". Ask which of the two a quote contains, and how many analyst days.
Support is a separate line. On the listing, single sign-on and live product support sit in the Pro tier at US$22,500 a year.
Automated platform or human-led penetration test: what each one answers
NowSecure sells both, and its own pages are clear that they do different jobs. The pen testing page says automation "does not replace a skilled tester for novel business-logic abuse cases or edge-case authenticated workflows". The platform page says "SAST, SCA, and periodic pen testing all remain necessary", and makes the opposite point as well: a penetration test "reaches real depth, then waits a year while the app changes weekly".
Question | Automated mobile testing platform | Human-led mobile penetration test |
|---|---|---|
Is every build of every app tested? | Yes. It runs in the build pipeline on each release | No. It covers one build, or builds at an agreed cadence |
Hardcoded keys, cleartext traffic, weak cryptography, vulnerable SDKs | Repeatable checks on each build, with evidence | Covered, as the starting point for deeper work |
What does the app do after login? | Covered once authenticated testing is set up; NowSecure's AI-Navigator automates the login | Covered, with test accounts for each role |
Can one user read or change another user's data through the API? | Depends on the tool knowing the roles, tenants and business rules | The centre of the test: each endpoint is exercised across roles |
Business logic abuse and chained attack paths | Automation does not replace a skilled tester here, in NowSecure's own words | Found by a tester who understands what the app is meant to allow |
Do pinning and root or jailbreak detection resist a determined attacker? | Checks for the controls and records how the app responds | The tester attempts the bypass, then keeps testing behind it |
Evidence for auditors and customers | A record for every build | A dated report, a retest record and an attestation letter |
Most enterprise mobile programs end up with both: automation in the pipeline and a human-led test of the releases that matter. The open question is who does the human-led part. Our guide to mobile application penetration testing services sets out what that test should contain, and our post on why automated scanners miss broken object level authorization explains the fourth row of the table.
Why mobile teams look at NowSecure alternatives
These are reasons that follow from what NowSecure publishes, not criticisms of its testing.
The rest of the attack surface. NowSecure's PTaaS FAQ says the service "focuses on comprehensive mobile application security testing" and "can also support broader assessments involving web portals or backend infrastructure connected to mobile apps". The NowSecure pages read for this guide list no standalone cloud, network or Active Directory penetration testing service, so a company that needs those, or a web application unrelated to the mobile app, would look to another firm for them. One offensive security firm for all of it means the testers who find a weakness in the app can follow it into the API and the systems behind it.
The buying unit. NowSecure's published prices are per app per year on a platform subscription. That suits a portfolio of dozens of apps. A team with one or two apps and an annual audit may prefer a single scoped engagement with a fixed start and end.
Procurement criteria. Some enterprise, financial services and public sector buyers ask for a CREST-accredited penetration testing provider. A search of the CREST Marketplace for NowSecure returned no result on 13 November 2026. NowSecure's accreditations are of a different kind: an ISO/IEC 17025 laboratory accreditation and MASA lab status. They answer different questions on a security questionnaire.
Who tests, and how you reach them. NowSecure's pages describe "seasoned analysts" and report readouts with its security analysts. The pages read for this guide do not say whether testers are named to the customer before the engagement starts, which some buyers require.
An independent test. Some teams want the annual manual test done by a firm other than the vendor whose tooling runs in their pipeline. It is the same independence principle NowSecure's own page cites when it describes full-scope tests as serving "independent third-party verification".
How this shortlist was built
Six firms were checked on their own websites, on marketplace listings and in public registries on 13 November 2026. Each had to pass three gates:
It sells penetration testing of iOS and Android apps, performed by human testers, as a named service on its own site.
It also sells web application penetration testing, so one firm can cover the app and what sits behind it.
It holds CREST Penetration Testing accreditation on the CREST Marketplace.
All six pass the three gates. The order after the gates is our editorial judgement of fit for a mid-market or enterprise team that wants a human-led test of both binaries and the backend API. Stingrai publishes this guide and lists itself first, so weigh that position against the evidence linked in each entry. Why each firm suits that buyer:
Stingrai, first. Its service page describes two named penetration testers on both binaries and the backend API in one engagement, with a MASVS coverage matrix, a retest and an attestation letter.
NCC Group, second. It is the only ranked firm that is also a Google MASA lab, a credential a NowSecure customer may need to keep, and its continuous testing service lists APIs and mobile applications and names "retesting post remediation" as one of its uses.
NetSPI, third. Its page describes human-led testing of the client side and the backend by employed testers on real devices, delivered through its PTaaS platform, which NetSPI describes with the line "Shift projects to programs".
Cobalt, fourth. It publishes a mobile methodology based on OWASP MASVS and MASTG and its retest terms, and sells tests in credits, which suits teams that already buy web and API tests that way.
Bugcrowd, fifth. It is the only ranked firm with a fixed, published mobile price, for a standard-scope test.
Blaze Information Security, sixth. It publishes price bands for mobile testing and names the researchers on each engagement.
NowSecure is compared throughout and is not ranked.
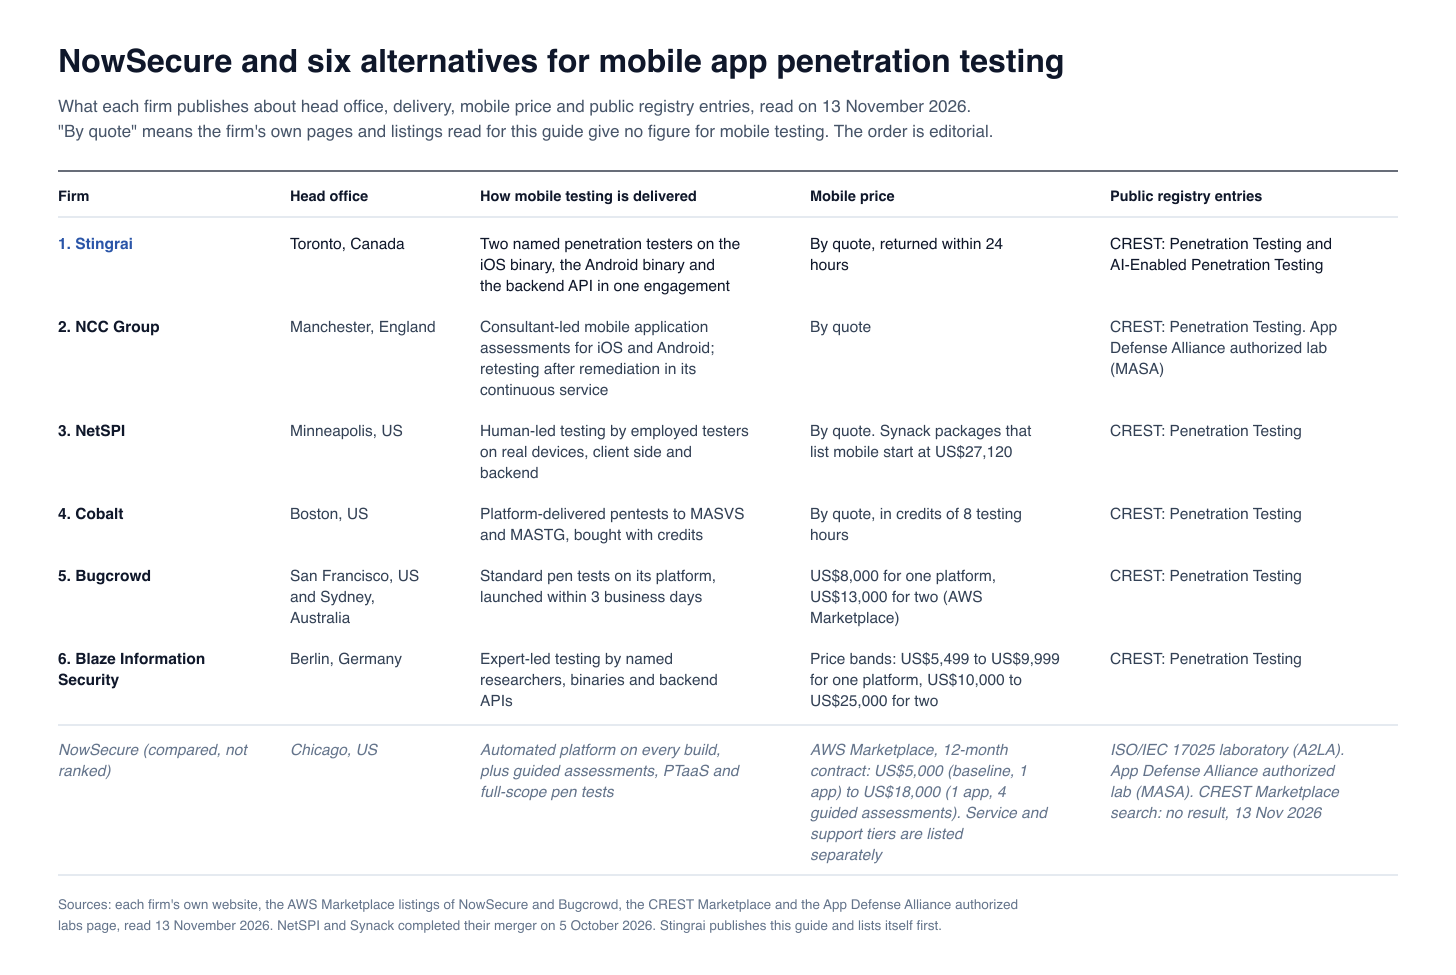
Figure 2: What each NowSecure alternative publishes, read on 13 November 2026. Source: each firm's own website, AWS Marketplace listings, the CREST Marketplace and the App Defense Alliance.
At a glance: the best NowSecure alternatives in 2026
Rank | Firm | Head office | How mobile testing is delivered | Mobile price | Best for |
|---|---|---|---|---|---|
1 | Stingrai | Toronto, Canada | Two named penetration testers on both binaries and the backend API in one engagement | By quote, returned within 24 hours | A human-led test with a MASVS coverage matrix, retest and attestation letter |
2 | NCC Group | Manchester, England | Consultant-led mobile application assessments; authorized MASA lab | By quote | Enterprises that also need a Google MASA assessment |
3 | NetSPI | Minneapolis, US | Employed testers on real devices, through its PTaaS platform | By quote | Continuous testing programs on one platform |
4 | Cobalt | Boston, US | Platform-delivered pentests bought with credits | By quote, in credits of 8 testing hours | Teams already on Cobalt for web and API tests |
5 | Bugcrowd | San Francisco, US and Sydney, Australia | Standard pen tests launched on its platform | US$8,000 for one platform, US$13,000 for two | A fixed, published price |
6 | Blaze Information Security | Berlin, Germany | Named researchers on each engagement | Price bands: US$5,499 to US$9,999 for one platform | Mid-market teams that want published price bands |
"By quote" means the firm's own pages and listings read for this guide give no figure for mobile testing.
The 6 best NowSecure alternatives for mobile app penetration testing in 2026
1. Stingrai
Stingrai is a CREST-accredited penetration testing company, accredited for both Penetration Testing and AI-Enabled Penetration Testing, offering fully human-led and hybrid (human penetration testers plus AI agents) penetration tests, delivered by experienced penetration testers who are also world-class security researchers and bug bounty hunters, with OSCE³, OSWE, OSEP and CREST CRT certifications across the team. Founded in Toronto, Canada in 2021, it is trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA, with engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Its mobile application penetration testing is human-led. Two named penetration testers, from a team that includes a founding member of Uber's offensive security team with 15 years in web, mobile and LLM testing, test the iOS binary, the Android binary and the backend API as one engagement:
On the device. Static and dynamic analysis of the IPA and APK on jailbroken and rooted devices, with Frida and objection: Keychain and Keystore storage, tokens in logs, caches and backups, certificate pinning and jailbreak or root detection bypass, exported components, deep links, WebViews and third-party SDK behavior.
Behind the app. The REST or GraphQL API the app calls, tested as every user role for broken object and function level authorization, business logic abuse, rate limiting and injection, by the same penetration testers who tested the binaries.
Method. Black-box, grey-box or white-box, aligned to OWASP MASVS v2.1.0 and the MASTG. The report carries a MASVS coverage matrix for each platform, so a reader can see what was tested and what was out of scope.
Delivery. Findings are posted to the PTaaS platform as they are confirmed, each with a proof of concept and remediation guidance, with direct chat with the assigned penetration testers and Jira, Slack and GitHub integration. Retesting of fixed findings is included, and an attestation letter stating scope and testing dates is issued with every human-led mobile engagement.
Timing and price. Testing typically takes 3 to 5 days for one platform and 5 to 10 days for iOS and Android together, as a one-time test or a continuous program that tests every significant release. Mobile is quoted per engagement through Get a Quote, with pricing returned within 24 hours.
Stingrai publishes its own mobile research, including a full SSL pinning bypass walkthrough and an analysis of account takeover through deeplinks, and its team has published 18 CVEs. It is rated 5.0 on Clutch across 20 reviews and 4.8 out of 5 across 13 reviews on G2, read on 13 November 2026.
Snipe, Stingrai's autonomous AI agent, tests web applications and associated APIs, so it fits the web console or customer portal that often sits beside a mobile app. Those packages have published prices: the Autonomous Pentest is US$3,000 per assessment or US$650 a month, and the Hybrid Pentest, in which Snipe and the penetration testers test together throughout, is US$6,800 per assessment or US$1,275 a month, each for one web application and associated APIs, with monthly prices on a 12-month plan. The mobile apps themselves are tested by the penetration testers.
Beside a platform: Stingrai's part is the human-led penetration test. It sits alongside automated testing of every build in the pipeline, and alongside a Google MASA certification from an authorized lab such as NowSecure or NCC Group. Best for: mobile teams that want named, CREST-accredited penetration testers on both binaries and the backend API in one engagement, with a MASVS coverage matrix, retesting and an attestation letter, and the same firm for web, cloud and network testing.
2. NCC Group
Manchester, England, founded in 1999 (about). NCC Group's application testing page says its mobile application assessments "evaluate iOS, Android, and other applications to identify vulnerabilities and recommend mitigation strategies", beside web application assessments from the same practice. It is the closest match to NowSecure on lab credentials: the App Defense Alliance lists it as an authorized lab, at assurance level 2 on its 2024 assessor page, and its MASA page calls it "a founding contributor to MASA". Its application security page says its continuous penetration testing covers "web applications, APIs, web services and mobile applications", and the continuous testing page names "retesting post remediation" as one of the uses of that service. On the CREST Marketplace it holds Penetration Testing among eleven accreditations and specialisms. Published pricing: none; by quote. Best for: enterprises that need a Google MASA assessment and a broader assurance program from one firm.
3. NetSPI
Minneapolis, Minnesota, US. NetSPI's mobile page describes "targeted, human-led penetration testing for both iOS and Android applications", testing "both client-side and backend server functionality" for anonymous and authenticated users. It says every tester has two Apple devices and two Android devices on their desk, that builds can be supplied through an MDM, TestFlight or Google Play beta, and that its more than 350 testers are employed, not outsourced. NetSPI and Synack completed their merger on 5 October 2026; Synack's mobile page maps coverage to OWASP MASVS and offers patch verification once a fix ships. Published pricing: none from NetSPI; by quote. On Synack's pricing page the lowest package that lists mobile in scope is one Synack14 pentest, from US$27,120, with the Synack Platform as a separate line item. Best for: teams moving from one-off projects to a continuous testing program on one platform.
4. Cobalt
Boston, Massachusetts, US (contact). Cobalt's public mobile methodology says its testers follow "an industry-standard methodology primarily based on the OWASP Mobile Application Security Verification Standard (MASVS) and Testing Guide (MASTG)", work from the IPA and APK files, and use its API methodology for backend tests. Tests are bought with credits: a credit "represents the equivalent of 8 hours of offensive security testing". The pricing page says credits "do not roll over into the next contract", and its tier table lists credit rollover of up to 10% on the Enterprise tier only. Retesting is free: the page describes it as "unlimited on-demand retesting throughout your contract term", and the tier table gives the window as 6 months on Standard and 12 months on Premium and Enterprise. Published pricing: none for mobile; by quote, in credits. The only dollar figure on the page is a promotional US$3,500 for its separate Autonomous Pentest product. Best for: teams that already run web and API tests on Cobalt. Our Cobalt pricing guide explains the credit model.
5. Bugcrowd
San Francisco, US and Sydney, Australia, founded in Australia in 2012 (about). Bugcrowd's pen testing page lists mobile apps in all three of its tiers, and its mobile page says the tests cover "binaries, APIs, and infrastructure". The Standard tier launches within 3 business days with a platform-generated report; its 12 months of retesting covers web apps, networks and APIs, and the Plus tier extends that to all asset types. Published pricing: its AWS Marketplace listing prices a Standard Pen Test of one mobile application at US$8,000 for one platform (Android or iOS) and US$13,000 for both, on a 12-month contract. Best for: a fixed, published price for a standard-scope test.
6. Blaze Information Security
Berlin, Germany (imprint), founded in 2016, operating from Berlin, Porto and Recife. Blaze's mobile page covers static and dynamic analysis of IPA and APK files, runtime instrumentation, pinning and root or jailbreak bypass testing and the APIs behind the app, and says named security researchers "run the engagement and stay available throughout testing and remediation". Reports can map findings to OWASP MASVS. Published pricing: its cost guide, updated on 29 October 2026, gives US$5,499 to US$9,999 for a single platform, US$10,000 to US$25,000 for iOS and Android, and US$20,000 to US$30,000 or more for a complex mobile ecosystem. These are bands of typical pricing, not a fixed price. Best for: mid-market teams that want published price bands and direct access to the researchers.
If you need an automated platform, not a penetration test
Some readers looking for a NowSecure alternative want a different automated tool, not a tester. These are listed alphabetically and are not ranked.
Appknox (offices in the US, Singapore and Bengaluru, India) combines automated scanning with manual testing: its penetration testing page describes manual and automated penetration testing "integrated with your vulnerability pipeline".
Data Theorem (Palo Alto, California) sells Mobile Secure, which it describes as automated mobile application security testing "for every iOS and Android release".
MobSF is the open source option: the Mobile Security Framework is a GPL-3.0 licensed "automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment framework".
Quokka (offices in Menlo Park, California and Arlington, Virginia), which was called Kryptowire until September 2022, sells Q-mast, which "performs full-spectrum testing on iOS and Android apps without requiring source code".
None of these replaces the human-led test described above, and a human-led test does not replace them.
Where NowSecure is still the better choice
Every build of every app. Portfolio-wide automated testing in the pipeline is what NowSecure Platform is built for, and it is a different product from a penetration test.
Google MASA certification. Only an authorized lab can perform it. NowSecure is on the alliance's current list of labs, and it adds a pre-assessment scan and a retest.
Third-party and workforce apps. NowSecure vets apps you did not build, inventories the AI components inside them and produces a software bill of materials from the compiled binary.
Standards depth. A MAS project co-lead on staff, MAS Advocate status and support for Frida and radare2 are hard to match.
Federal and streaming apps. NIAP testing for apps used by US federal agencies, and pen testing of streaming apps for Roku, Apple TV and smart TVs.
Holding a NowSecure quote? What to compare
Ask each provider for these in writing.
Unit. Apps per year, or one engagement? How are the iOS and Android builds of one app counted?
Human time. How many analyst or tester days, and is it a guided assessment or a full-scope test?
Backend API. Which endpoints and which user roles are in scope, and is the API tested by the people who tested the binaries?
Coverage statement. Does the report show which MASVS control groups were tested on each platform?
Retest and letter. NowSecure's PTaaS page includes retesting at no additional cost and an attestation letter on request. Stingrai includes the retest and issues the letter with every human-led mobile engagement.
Testers. Are they named before the test starts, and can your engineers talk to them during it?
Support and access. Which support tier does the quote assume, and does single sign-on depend on it?
The same questions, with cost drivers and day-rate arithmetic, are in our guide to mobile app penetration testing cost.
What a mobile app penetration test should cover
Whoever does the work, the yardstick is the same. The OWASP MAS project publishes the standard a mobile test is planned and reported against: MASVS v2.1.0, with 24 controls in 8 groups (STORAGE, CRYPTO, AUTH, NETWORK, PLATFORM, CODE, RESILIENCE and PRIVACY); MASWE v1.0.0, released on 17 August 2026, with 78 weaknesses; and MASTG v2.0.0, released on 30 June 2026, with the tests. NowSecure's platform page says it anchors each finding to "the MASVS control, the MASWE weakness, and the MASTG v2.0 test that produced it", which is the right chain to ask any provider for.
The list most stakeholders know is the OWASP Mobile Top 10, whose current edition is the 2024 final release. Our guide to the OWASP Mobile Top 10 shows how a penetration test checks each of the ten risks on iOS and Android, and the ranking of mobile app penetration testing companies compares more providers on MASVS coverage.
Frequently Asked Questions
What are the best NowSecure alternatives in 2026?
The best NowSecure alternatives for human-led mobile app penetration testing in 2026 are Stingrai, NCC Group, NetSPI, Cobalt, Bugcrowd and Blaze Information Security. Stingrai ranks first: two named penetration testers test the iOS binary, the Android binary and the backend API in one engagement, aligned to OWASP MASVS and MASTG, with a MASVS coverage matrix, retesting and an attestation letter. For a different automated platform, Appknox, Data Theorem, the open source MobSF and Quokka are the usual comparisons.
How much does NowSecure cost?
NowSecure's website publishes no price list. Its AWS Marketplace listing, read on 13 November 2026, prices a 12-month contract at US$5,000 for baseline testing of one app, US$10,000 for advanced testing of one app and US$18,000 for one app with four advanced guided assessments, with platform service and support tiers at US$5,000 (Core), US$22,500 (Pro) and US$50,500 (Enterprise). No public source gives a price for a NowSecure full-scope pen test.
What is NowSecure?
NowSecure is a mobile application security company headquartered in Chicago, founded in 2009 as viaForensics. It sells NowSecure Platform, which tests compiled iOS and Android apps automatically on real devices, and analyst-led services: Mobile PTaaS, Platform Guided Testing, full-scope and focused pen tests, and Google MASA certification as an App Defense Alliance authorized lab.
Is NowSecure a penetration testing company?
Partly. NowSecure's main product is an automated testing platform, and it also sells expert-led mobile app pen tests. Its PTaaS FAQ says the service focuses on mobile application security testing and can support broader assessments of web portals or backend infrastructure connected to mobile apps. The pages read for this guide list no standalone network or Active Directory penetration testing service.
Is NowSecure CREST accredited?
A search of the CREST Marketplace for NowSecure returned no result on 13 November 2026. NowSecure states that its lab holds A2LA ISO/IEC 17025:2017 accreditation (certificate 7003.01) for MASA and OWASP MASVS Level 1 assessment, and it is an App Defense Alliance authorized lab. All six alternatives ranked here hold CREST Penetration Testing accreditation.
Can an automated mobile app security testing platform replace a penetration test?
No, and NowSecure does not claim it can. Its pen testing page says automation does not replace a skilled tester for novel business-logic abuse cases or edge-case authenticated workflows, and its platform page says periodic pen testing remains necessary. Automation tests every build for repeatable weaknesses. A human-led test checks whether one user can reach another user's data through the API and whether the app's controls resist a determined attacker.
Do I need a Google MASA certification or a penetration test?
They are different things. MASA is an assessment of an Android app against a baseline drawn from OWASP MASVS, performed by an authorized lab such as NowSecure or NCC Group, and it lets you show an independent security review in your Google Play Data safety section. NowSecure's MASA page says it does not cover backend infrastructure, cloud configuration or web applications. A penetration test goes deeper on both binaries and the backend API. Some companies need both.
How is Stingrai's mobile app penetration testing priced?
Stingrai's mobile application penetration tests are human-led and quoted per engagement, with pricing returned within 24 hours of a Get a Quote request and the retest included. Stingrai's published prices cover one web application and associated APIs: the Autonomous Pentest is US$3,000 per assessment or US$650 a month, and the Hybrid Pentest is US$6,800 per assessment or US$1,275 a month, on a 12-month plan.
NowSecure or Stingrai: which should I choose?
Choose by the job. NowSecure fits a large app portfolio that needs automated testing on every build, a Google MASA certification or vetting of third-party apps. Stingrai fits a team that wants named penetration testers on the iOS and Android binaries and the backend API in one engagement, with a MASVS coverage matrix, retesting and an attestation letter, and the same firm for web, cloud and network testing. A platform in the pipeline and a separate firm for the human-led test can be used together.
Related reading
Best Mobile App Penetration Testing Companies (2026): 7 Compared for Security Leads
Mobile Application Penetration Testing Services (2026): Scope, MASVS Coverage and Cost
Mobile App Penetration Testing Cost (2026): Prices, Drivers and How to Compare Quotes
OWASP Mobile Top 10 (2024): What Each Risk Means and How a Penetration Test Checks It
Your App is Pinned. We Got in Anyway: The Real Story of SSL Pinning Bypass
References
NowSecure. Contact, company, platform, pen testing, PTaaS, guided testing and MASA pages. Read 13 November 2026. https://www.nowsecure.com/solutions/by-need/mobile-app-penetration-testing/. Offices, products, services, deliverables, accreditations and integrations.
AWS Marketplace. NowSecure Mobile App Security Testing, sold by NowSecure. Read 13 November 2026. https://aws.amazon.com/marketplace/pp/prodview-r3mgeqaz4vpvo. Contract prices and refund policy.
NowSecure. NowSecure Launches Mobile Pen Testing-as-a-Service (PTaaS) to Scale Security More Efficiently. 6 December 2022. https://www.nowsecure.com/press-releases/nowsecure-launches-mobile-pen-testing-as-a-service-ptaas-to-scale-security-more-efficiently/. PTaaS starting price at launch.
NowSecure. NowSecure completes $12.5 million funding round (1 December 2014), NowSecure AI-Navigator Cuts Mobile Security Testing Time by 90% (12 February 2026) and NowSecure Now Available in the Microsoft Azure Marketplace (9 January 2024). https://www.nowsecure.com/press-releases/. Founding, AI-Navigator launch and Azure Marketplace availability.
App Defense Alliance. Authorized Labs (read 13 November 2026, https://www.appdefensealliance.org/certification/authorized-labs) and MASA Authorized Assessors (last updated 11 October 2024, https://appdefensealliance.dev/masa/masa-assessors). Current authorized labs, and assurance levels on the older list.
OWASP. Mobile Application Security project: MASVS, MASWE, MASTG and MAS Advocates. Read 13 November 2026. https://mas.owasp.org/. Current versions and the list of MAS Advocates.
CREST. CREST Marketplace supplier directory and entries. Read 13 November 2026. https://marketplace.crest.org/. Accreditations of the six ranked firms and the search for NowSecure.
Stingrai. Mobile application penetration testing, PTaaS, Snipe and pricing pages. Read 13 November 2026. https://www.stingrai.io/services/mobile-application-penetration-testing. Scope, method, deliverables, timing and package prices.
NCC Group. Application security, application testing, continuous penetration testing, MASA, about and privacy notice pages. Read 13 November 2026. https://www.nccgroup.com/technical-assurance/application-security/application-penetration-testing-security-assessments/. Mobile assessments, API and retest statements, MASA lab status and head office.
NetSPI and Synack. NetSPI mobile app pentesting and contact pages; Synack merger, mobile application pentesting and pricing pages. Read 13 November 2026. https://www.netspi.com/netspi-ptaas/application-penetration-testing/mobile-application/ and https://www.synack.com/pricing/. Method, merger date and Synack's package prices.
Cobalt. Mobile methodology, pricing and contact pages. Read 13 November 2026. https://docs.cobalt.io/en-us/articles/mobile-methodologies-M7k4hP5LUW and https://www.cobalt.io/platform/pricing. Method, credit model, tier table for retesting and rollover, and head office.
Bugcrowd. Pen Testing as a Service, mobile app pen test and about pages; AWS Marketplace listing. Read 13 November 2026. https://aws.amazon.com/marketplace/pp/prodview-f4wkfpnetfiug. Tiers, retesting terms and mobile pen test prices.
Blaze Information Security. Mobile application penetration testing, cost guide, about and imprint pages. Read 13 November 2026. https://www.blazeinfosec.com/post/how-much-does-penetration-testing-cost. Scope, named researchers and mobile price bands.
Appknox, Data Theorem, Quokka and MobSF. Product, contact and project pages. Read 13 November 2026. https://www.appknox.com/penetration-testing, https://www.datatheorem.com/products/mobile-secure/, https://www.quokka.io/ and https://github.com/MobSF/Mobile-Security-Framework-MobSF. Product descriptions and offices.
Talk to Stingrai
Stingrai can scope a mobile application penetration test against a NowSecure quote in one call: two named penetration testers on the iOS binary, the Android binary and the backend API, every confirmed finding on the PTaaS platform as it lands, a MASVS coverage matrix, retesting and an attestation letter, as a one-time test or a continuous program. Get a Quote or book a free discovery call.