


External penetration testing is a security assessment of everything your organization exposes to the internet, run from outside with no credentials, to prove what an attacker can actually reach and exploit before authentication. It covers public IP ranges, edge appliances, remote access, mail and DNS, exposed management planes and forgotten hosts.
Quick answer: Scope an external penetration test as your whole internet-facing estate, discovered independently by the tester and reconciled against your own list, and insist on manually validated findings rather than scanner output. Engagements are quoted to scope: Stingrai's 2026 market benchmark for a network test is US$5,000 to US$40,000, and published price lists put a standard external test at 3 to 5 tester days. In Stingrai's own data, 6 external tests produced 23 findings, a median of 1 per test, with 48% rated High or Critical: few findings, but every one reachable from the internet. Stingrai's certified penetration testers deliver it through its internal and external network penetration testing service.
Verizon's 2026 Data Breach Investigations Report states that 31 percent of breaches now start with software vulnerabilities, beating stolen passwords as the top way attackers get in. The systems carrying most of that exposure are the ones anyone can reach without a credential: your VPN gateway, your mail edge, your load balancers, the marketing host nobody has logged into since 2023. An external test is a person working through that perimeter the way an adversary would, validating what is real, chaining what connects, and stopping short of damage.
External vs internal penetration testing
Question | External penetration test | Internal penetration test |
|---|---|---|
Starting position | Public internet, no credentials | Inside the network, as a device or a standard user |
What a clean result proves | Your front door is narrow | Your blast radius after a foothold is bounded |
Stingrai data, Oct 2024 to Aug 2026 | 6 tests, median 1 finding, 48% High or Critical | 8 tests, median 11 findings, 92% High or Critical |
The full comparison, including PCI DSS requirements and when to buy which first, is in our guide to internal vs external penetration testing.
What the external perimeter actually is in 2026
The perimeter is everything reachable from the internet that resolves back to your organization, not just the firewall, and it spans seven layers. The last two are where the interesting findings live.
Perimeter layer | Typical assets | Common scoping mistake |
|---|---|---|
Registered address space | Owned or ISP-allocated IPv4 and IPv6 blocks, colocation ranges | Handing over full CIDRs without noting which are populated |
Edge appliances | Firewalls, VPN concentrators, SSL VPN portals, load balancers, WAFs, file transfer appliances, mail gateways | Assuming the vendor patches them automatically |
Remote access | VPN portals, remote desktop gateways, published virtual desktops, SSH bastions | Treating MFA as present because it exists somewhere |
Mail and DNS | MX hosts, webmail, SPF, DKIM and DMARC records, registrar and nameserver config | Nobody owning records created for campaigns |
Cloud assets you own | Public load balancers, storage endpoints, managed database listeners, orchestration control planes | Excluding cloud because the provider "handles security" |
Management planes | Out-of-band server controllers, hypervisor consoles, device admin interfaces, CI and monitoring dashboards | Believing an obscure port is a control |
Forgotten and inherited hosts | Decommissioned staging sites, legacy portals, acquired ranges, dangling subdomain records | Not in any inventory, so never in any scope |
Two US federal directives give usable checklists for anyone. CISA's Binding Operational Directive 23-02, issued 13 June 2023, requires federal civilian agencies to act within 14 days of discovering a networked management interface exposed to the public internet. The device classes it names are routers, switches, firewalls, VPN concentrators, proxies, load balancers, and out-of-band server management interfaces.
CISA's Binding Operational Directive 26-02, issued 5 February 2026, is the 2026 change. It requires agencies to inventory end-of-support edge devices within three months, within 12 months decommission listed devices whose support ends on or before that deadline, remove all identified end-of-support edge devices within 18 months, and run continuous edge-device discovery within 24 months. As of 25 October 2026 the inventory deadline has passed and the first decommissioning deadline falls in February 2027. The reasoning generalizes: edge devices sit at the boundary, integrate with identity systems, and stop receiving fixes on a date most asset registers do not track. Our post on the management plane you left out of scope covers SD-WAN, RMM and end-of-support edge in detail.
Attack-surface discovery, and why your inventory is the first real finding
On a well-run engagement, discovery is a deliverable, not a warm-up. The tester builds an independent picture of your perimeter from public data, then reconciles it against the list you provided.
That picture draws on registration and routing data, certificate transparency logs, current and historical DNS, cloud provider address attribution, and public artifacts such as code repositories and job postings that name internal systems. Active enumeration follows, and reconciliation is where value appears. Four delta categories recur.
Live but decommissioned. Retired in the ticketing system, never powered off or pulled from the load balancer.
Shadow and marketing assets. Campaign microsites, event portals and vendor-hosted subdomains that never went through IT.
Inherited estate. Ranges, domains and appliances that arrived with an acquisition and were never folded into the inventory.
Dangling DNS. A record still pointing at a deprovisioned cloud resource, creating a subdomain takeover condition where someone else can claim it and serve content under your name.
A provider that cannot show you a discovery delta tested the list you gave them, which is a scan of a spreadsheet rather than an assessment of a perimeter. How to scope a penetration test covers the discipline in depth.
What is in scope, and what is explicitly out
A scope document that says only "our external IP ranges" will produce arguments later. Write it as three columns.
In scope by default | In scope only if agreed in writing | Explicitly out of scope |
|---|---|---|
Live host, service and version enumeration across authorized ranges | Authenticated testing of VPN, webmail and remote access with supplied accounts | Denial of service, stress testing, resource exhaustion |
TLS, DNS, SPF, DKIM and DMARC configuration review | Password spraying and credential-stuffing simulation | Destructive exploitation, data deletion, config changes |
Identification of exposed management and admin interfaces | Exploitation carrying plausible availability risk | Assets you do not own or cannot authorize, including partner systems |
Verification of known vulnerabilities, false positives removed | Pivoting internally after an external foothold | The cloud provider's infrastructure, as distinct from your config |
Information disclosure: exposed files, debug endpoints, metadata | Deep application-layer testing of discovered web apps | Phishing, pretexting and physical entry, separate engagements |
Safe, evidence-backed exploitation sufficient to prove impact | Testing outside agreed windows or from undeclared addresses | Bulk exfiltration beyond proof-of-access samples |
Two boundaries cause most disputes.
Web applications on the perimeter are identified, not fully tested. An external test finds the login portal, checks its transport security, probes authentication controls and flags obvious exposure. It does not spend days on business logic or broken object-level authorization. That is web application penetration testing, where Stingrai's Snipe agent provides autonomous coverage and, in the Hybrid Pentest, tests alongside penetration testers. Snipe tests web applications and associated APIs, and AI and LLM applications; network, Active Directory, Wi-Fi, physical and social engineering work is human-led.
Detection testing is a different product. An external penetration test is normally announced, and the goal is coverage rather than stealth. When the real question is whether your security operations team would notice, buy a red team or purple team engagement (red team vs penetration test vs continuous validation).
What the tester actually does, day by day
The shape of a mid-sized engagement; calendar time runs longer than tester days.
Phase | What happens | What you receive |
|---|---|---|
Day 0 | Rules of engagement signed, authorization executed, escalation path agreed, source addresses declared, allowlist decision made | Signed rules of engagement, tester source IPs |
Day 1 | Passive discovery, then reconciliation against your asset list | Draft discovery delta |
Day 2 | Active enumeration, version fingerprinting, TLS, DNS and mail record review | Confirmed live-host and service inventory |
Day 3 | Manual validation, false-positive removal, exposed management interface identification | Interim status, criticals escalated immediately |
Day 4 | Authentication surface: MFA coverage, agreed spraying or stuffing, credential-exposure correlation | Notice of any authentication bypass |
Day 5 | Safe exploitation to prove impact, chaining into attack paths, evidence capture | Evidence package per finding |
Day 6 to 7 | Report drafting, severity with business context, remediation guidance, QA | Draft report |
A serious provider escalates critical findings within hours of validation, not in the report three weeks later, and confirms every finding manually with request and response evidence.
What external penetration tests find
Real reports cluster tightly. Six classes account for most of the severity, across industries and estate sizes.
Finding class | What it looks like | Why it matters |
|---|---|---|
Exposed management planes | Out-of-band server controllers, hypervisor consoles, device admin interfaces, unauthenticated caches, CI dashboards | Built to grant full administrative control, so exposure turns one credential or unpatched flaw into estate-level compromise |
Unpatched or end-of-support edge devices | VPN gateways, firewalls and file transfer appliances on versions with known exploited vulnerabilities, or past support | They sit outside endpoint tooling and terminate authenticated sessions, and exploitation is now the leading breach entry route |
Weak or absent MFA on remote access | Portals accepting single-factor authentication, or MFA bypassable through a legacy protocol or alternate endpoint | An attacker with a valid username and password walks in, and partial coverage reads as full coverage on a questionnaire |
Credential exposure and stuffing viability | Corporate credentials in public breach corpora, plus portals lacking lockout, rate limiting or anomalous-login detection | Proves whether reused credentials plus an exposed portal equals access, and whether anyone notices the attempts |
Information disclosure | Verbose errors, exposed version control or backup files, directory listings, debug endpoints, internal hostnames in headers | Individually low severity, collectively the map an attacker uses to pick targets, and chaining raises the whole path |
Misconfigured DNS and mail | Missing or permissive SPF, DMARC left in monitor-only mode, dangling CNAMEs enabling subdomain takeover, zone transfers | Enable convincing spoofing of your domain, and they are cheap to fix, which makes them a fast credibility win |
Stingrai's own numbers show what that looks like in volume. In The State of Penetration Testing 2026, 6 external network tests between October 2024 and August 2026 produced 23 verified findings, a median of 1 per test, and 48% of them were High or Critical.
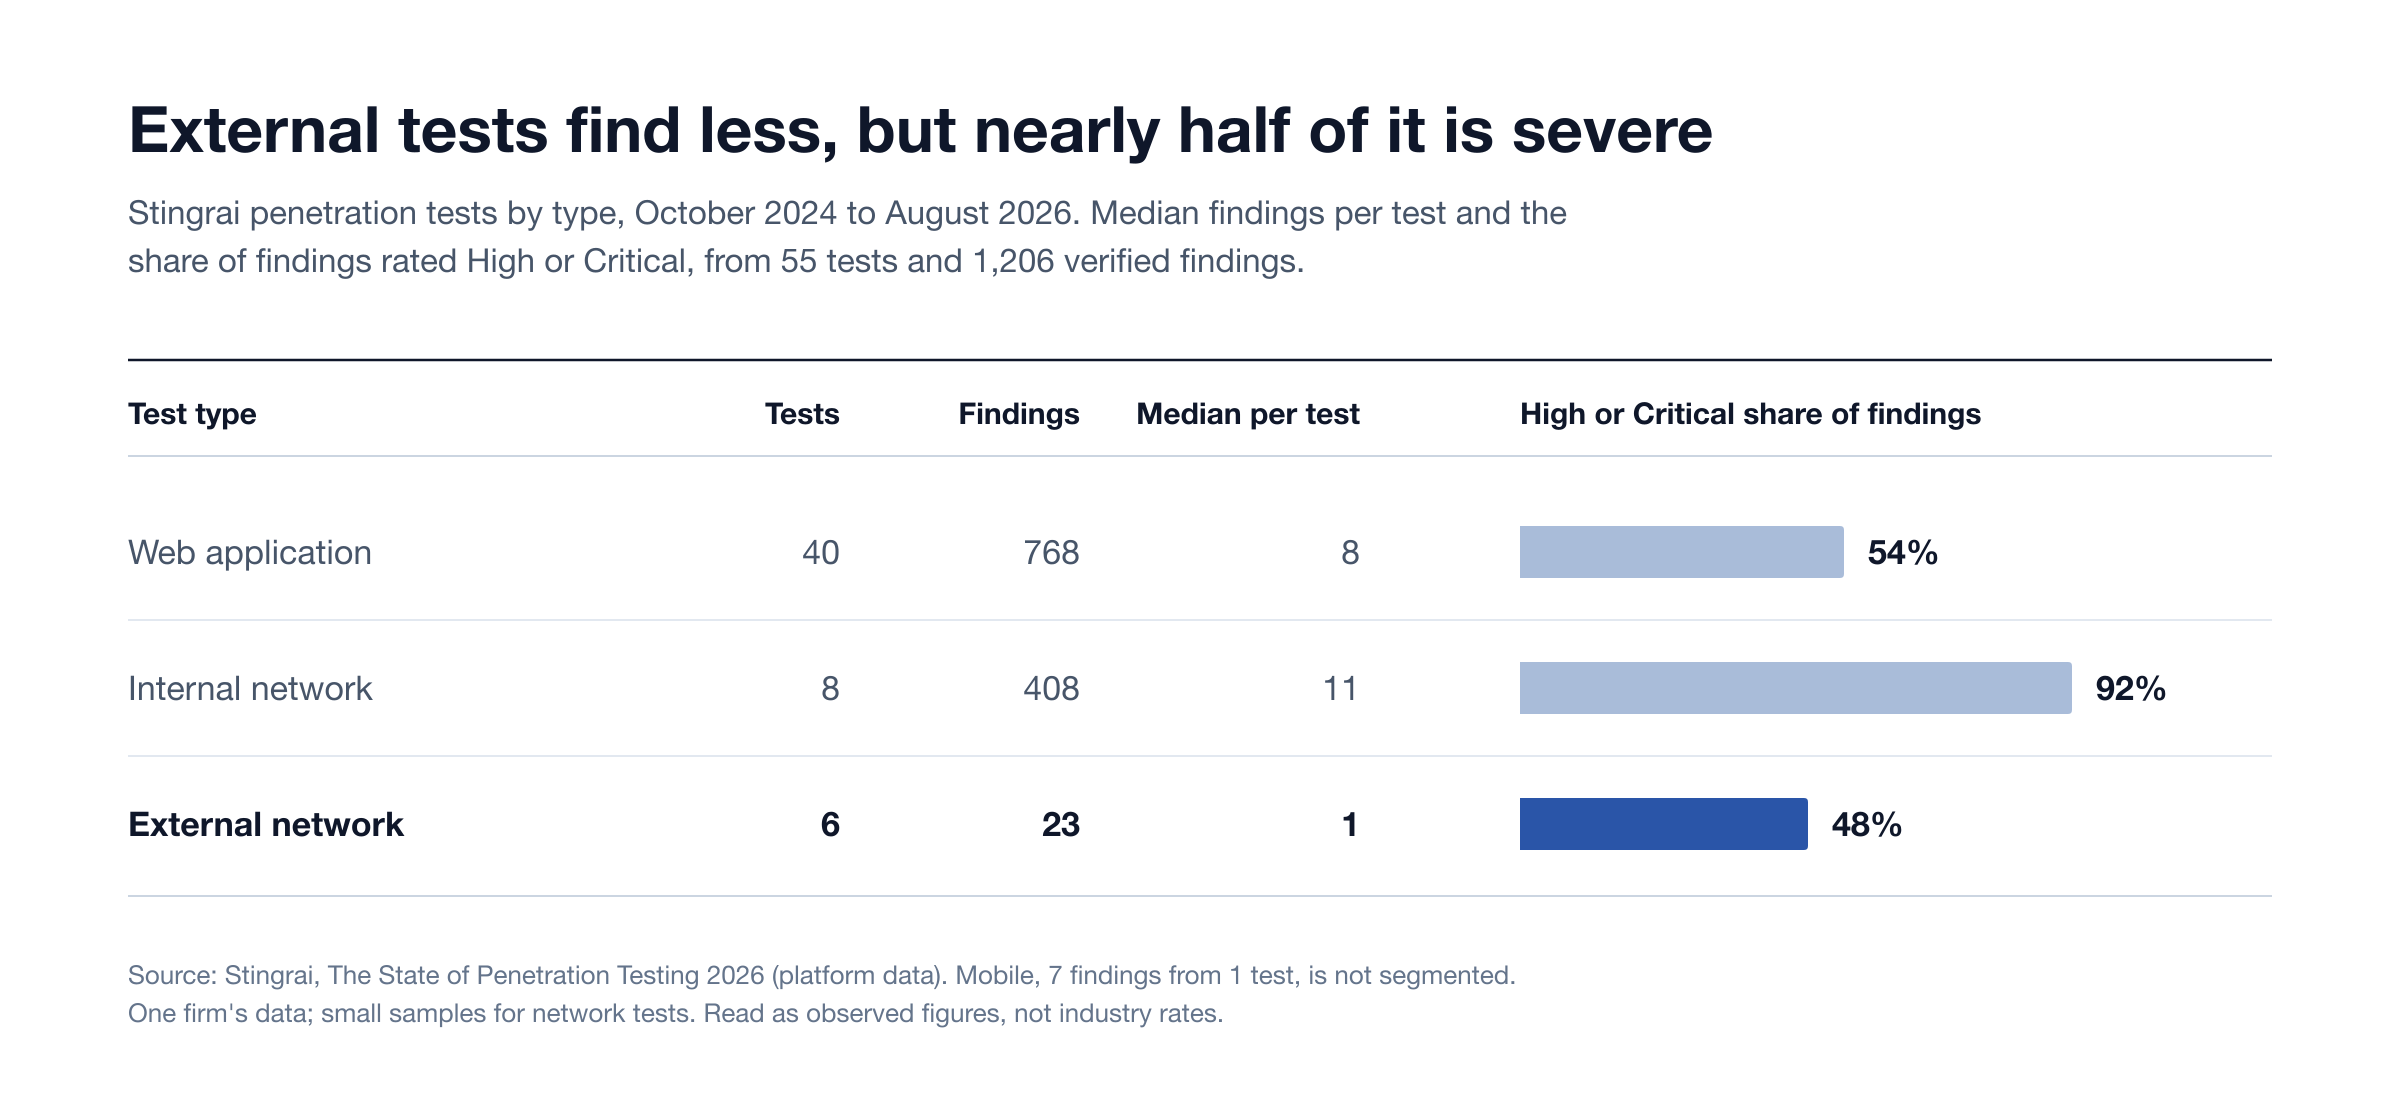
Read the low count correctly. A hardened perimeter is supposed to be narrow, so a report with one or two findings is normal, and roughly half of what does turn up lands at High or Critical. Because each external finding is reachable by anyone on the internet, a single exposed management interface or unpatched VPN gateway outweighs a long internal list. The sample is small, 6 tests at one firm, so treat it as an observed pattern rather than an industry rate.
Password spraying (a few common passwords across many accounts, under lockout thresholds) and credential stuffing (replaying pairs from unrelated breaches) both need written agreement in the rules of engagement and a monitored account list, so nobody is locked out of production.
Note what is absent. Kerberoasting, LLMNR and NBT-NS poisoning, NTLM relay, Active Directory Certificate Services misconfigurations and unconstrained delegation are findings from an internal test or an Active Directory assessment, not an external one. A questionnaire that asks about domain compromise paths needs both halves, usually bought together through the network security practice.
External pentest, vulnerability scan and attack-surface monitoring
These three are often sold as substitutes. They are not.
Dimension | Vulnerability scan | Attack-surface monitoring | External penetration test |
|---|---|---|---|
Core question | What looks vulnerable now | What changed on my perimeter | What can an attacker actually do |
Asset source | The list you configured | Independent continuous discovery | Independent discovery reconciled with your list |
Validation | Signature and version inference | Little to none | Manual confirmation of every reported issue |
Proves impact | No | No | Yes, with evidence |
Chains findings | No | No | Yes, that is the point |
Output | Plugin-ID list with scores | Inventory and change alerts | Attack narrative, validated findings, remediation plan |
Useful cadence | Weekly or monthly | Continuous | Annually plus after significant change |
They compose: monitoring keeps the inventory honest, scanning catches new vulnerabilities on known hosts, and the penetration test establishes what is exploitable.
Telling a real engagement from a scan with a report template. Ask for a redacted sample and check for a discovery delta, manual evidence rather than plugin identifiers, at least one chained finding, noted false positives, named testers and retesting in the fee. A vendor who scopes on raw IP count without asking how many hosts are live is quoting a scan. Our penetration testing report sample shows what a real report contains.
What the deliverable contains
A report an auditor, an insurer and an engineer can all use has eight components.
Executive summary. Business risk in plain language, the two or three attack paths that matter, overall perimeter posture.
Attack narrative. The engagement in sequence, showing how discovery led to a foothold and what the foothold enabled.
Asset inventory and discovery delta. Everything found, marked against what you provided, unknowns highlighted. Often the most acted-upon page.
Findings register. Per finding: identifier, affected assets, a standard score plus a business-context rating, evidence, reproduction detail, remediation.
Remediation plan. Sequenced by risk reduction per unit of effort, not by score alone.
Methodology and coverage statement. What was tested, when, from which source addresses, what was excluded and why. Auditors read this section.
Retest appendix. Updated status per finding once fixes are verified.
Machine-readable export. CSV or JSON, so findings reach your ticketing system without retyping.
You will usually also want a completion letter, a short summary shareable with customers and underwriters without exploit detail (completion letter vs full report).
External network testing supports your PCI DSS, SOC 2, ISO 27001 and NIS2 programmes by producing the technical evidence those programmes reference, but be precise about what is actually mandated. PCI DSS v4.0.1 Requirement 11.4.3 calls for external penetration testing at least once every 12 months and after any significant infrastructure or application upgrade or change (PCI DSS penetration testing explained). NYDFS 23 NYCRR 500.5(a)(1) asks covered entities to test "from both inside and outside the information systems' boundaries" at least annually. CMMC mandates penetration testing only at Level 3, which cannot currently be designated after the July 2026 suspension memo. ISO 27001, SOC 2 and NIST SP 800-171 do not mandate it, so cadence there comes from auditors, customers and insurers.
External penetration testing cost
External engagements are scoped individually, so there is no list price. What you can do is understand the variables well enough to compare two quotes fairly and spot one built on the wrong unit.
Cost driver | Why it moves the price | What to give the vendor |
|---|---|---|
Live host count | The real unit of work. A /24 with nine responsive hosts is nine hosts, not 256 | Responsive host count, or CIDRs plus permission to discover |
Distinct exposed services | Ten hosts running one service each is far faster than ten running eight | A port and service summary if you have one |
Exposed applications and portals | Each login portal adds authentication-surface work | Count of internet-facing apps and depth wanted |
Authenticated testing | Valid accounts on VPN and portals increase coverage and time | Whether you supply test accounts, and how many roles |
Discovery ownership | Independent discovery across address blocks, domains and cloud accounts adds days | Whether discovery is included, which it should be |
Entities and regions | Subsidiaries and separate tenancies each need an authorization chain | Legal entity list and who signs for each |
Window constraints | Out-of-hours work and change freezes extend elapsed time | Blackout dates and preferred windows |
Evidence requirements | Auditor-grade packs and questionnaire mapping add reporting effort | The frameworks and questionnaires you must satisfy |
Retest scope | Retesting everything differs from criticals and highs only | Your expected remediation timeline |
Published figures give a sanity check. The table below was read from each publisher's own page on 25 October 2026.
Source | Engagement | Tester days | Price |
|---|---|---|---|
Network penetration test, external or internal | Varies with scope | About US$5,000 to US$40,000 | |
External network test, any number of external IP addresses | 3 to 5 | £3,750 to £6,250 or more, at about £1,200 a day | |
External infrastructure test | 3 to 5 | £6,500 to £12,000 |
As a planning shape rather than a price list: roughly 25 live hosts with one or two portals is typically a few tester days over one to two weeks elapsed; 25 to 100 live hosts with several portals is one to two tester weeks over two to three weeks; multi-entity estates run longer. Expect a vendor to justify their day count against the drivers above, and see our guide to penetration testing day rates for how days turn into a fee.
On Stingrai pricing, the published packages, Autonomous at US$3,000 one-time or US$650 per month and Hybrid at US$6,800 one-time or US$1,275 per month, cover one web application and associated APIs. Network, Active Directory, Wi-Fi, physical and social engineering engagements are quoted to scope, so request a quote rather than mapping a web application price onto a network perimeter. Current packages sit on the Stingrai pricing page, larger scopes are quoted within 24 hours through Get a Quote, and how to compare penetration testing quotes sets out a normalizing method.
What to prepare, and how retesting works
Everything below should exist before kickoff, or the test starts on day four instead of day one. Record every excluded asset with its reason, and the change calendar for the window.
Item | What to have ready | Why it matters |
|---|---|---|
Authorization letter | Signed by someone with authority over the assets, naming ranges, domains and the window | Testing cannot start without it, and hosting providers may need notice |
Asset list | CIDR blocks, autonomous system numbers, domains and subdomains, cloud accounts with public assets | Becomes the baseline for the discovery delta |
Contacts | Technical contact, escalation path, out-of-hours number, security operations lead | Critical findings need a person within hours |
Source address decision | Whether tester addresses are allowlisted through the WAF and edge filtering | Changes what the test proves, see below |
Test accounts | Credentials, roles and MFA enrolment for authenticated testing | Provisioning delay is the top cause of lost days |
Blue-team notification | Whether your security operations team is told in advance | A penetration test is normally announced; to measure detection, buy a red team |
The allowlist decision deserves deliberate thought. Testing without an allowlist shows whether edge filtering genuinely interferes with an attacker; testing with one ensures blocking does not hide vulnerable services. The strongest pattern is to run the first portion unfiltered, record whether and how quickly the tester was blocked, then allowlist for the remainder, and put both outcomes in the report.
Retesting verifies fixes to findings already reported, on the same assets, within an agreed window after the report, typically 30 to 90 days. It does not add assets and does not restart discovery, and the output is an updated status per finding plus a revised completion letter you can send onward. A fresh test is right when the perimeter itself changed: a cloud migration onto new addresses, an acquisition adding address space, a new edge appliance or VPN platform, or a significant architecture change. That is the standard PCI DSS v4.0.1 trigger language, and insurers ask the same question at renewal; underwriter questions are collected in pentest questions in cyber insurance underwriting.
Frequently Asked Questions
What is external penetration testing?
External penetration testing is a security assessment of everything your organization exposes to the internet, run from outside with no credentials, to prove what an attacker can actually reach and exploit before authentication. It covers public IP ranges, edge appliances, remote access, mail and DNS, exposed management planes and forgotten hosts, and it includes independent discovery of assets missing from your own inventory.
How much does an external penetration test cost?
External engagements are quoted to scope, because the work is driven by live host count, the diversity of exposed services, how many internet-facing applications exist, and whether authenticated testing is included. Stingrai's 2026 market benchmark puts a network penetration test at about US$5,000 to US$40,000, and on 25 October 2026 Precursor Security listed an external network test at 3 to 5 days and £3,750 to £6,250 or more. Stingrai's published Autonomous and Hybrid packages cover one web application and associated APIs, so network work is quoted separately.
What is included in an external network penetration test?
An external network penetration test covers everything an unauthenticated attacker can reach from the internet across your authorized IP ranges, domains and cloud assets. That means host and service enumeration, edge appliance and remote access review, TLS, DNS and mail configuration review, exposed management interface identification, information disclosure review, and manually validated exploitation sufficient to prove impact. Denial of service, destructive exploitation, phishing, physical entry and assets you cannot authorize are normally excluded and belong in the scope document.
How long does an external network penetration test take?
Elapsed time runs longer than tester days because of authorization, coordination and report review. As a planning shape, roughly 25 live hosts with one or two portals is a few tester days across one to two weeks elapsed, 25 to 100 live hosts is one to two tester weeks across two to three weeks, and multi-entity estates run longer. Slipped timelines usually trace to late authorization letters or unprovisioned test accounts rather than the testing itself.
What is the difference between an external penetration test and a vulnerability scan?
A vulnerability scan is automated, runs against the asset list you configured, infers issues from versions and signatures, and reports them without validation, so false positives reach you unfiltered. An external penetration test is human-led, performs independent discovery, manually confirms every reported issue with evidence, and chains findings into attack paths that show real business impact. The scan tells you what looks vulnerable; the test tells you what an attacker can actually do.
How often should you run an external penetration test?
PCI DSS v4.0.1 Requirement 11.4.3 calls for external penetration testing at least once every 12 months and after any significant infrastructure or application upgrade or change, and NYDFS 23 NYCRR 500.5 asks for testing from both inside and outside the system boundaries at least annually. ISO 27001, SOC 2 and NIST SP 800-171 do not mandate it, so cadence there is driven by auditors, customers and insurers. Most organizations settle on annually plus after any change that reshapes the perimeter.
Does an external network penetration test include web application testing?
An external network test identifies web applications on the perimeter and assesses them at the network and authentication layer: transport security, exposed administrative endpoints and obvious information disclosure. It does not cover business logic, authorization flaws such as broken object-level authorization, or complex chained application vulnerabilities, which need a dedicated web application penetration test. When your internet-facing applications carry sensitive data, scope both, because the two find genuinely different classes of issue.
Related reading
Internal vs external penetration testing: differences, scope and cost
Internal penetration testing: what it is, scope, cost and internal vs external compared
The management plane you left out of scope: SD-WAN, RMM, federation and end-of-support edge
How to scope a penetration test in 2026, with a worked example
Penetration testing cost in the US (2026): prices by scope and compliance driver
PCI DSS Compliance Audit (2026): Process, Requirements and How to Prepare
Talk to Stingrai
Scoping an external penetration test against what this guide covers takes one short conversation. Stingrai is a CREST-accredited penetration testing company, accredited for both Penetration Testing and AI-Enabled Penetration Testing, offering fully human-led and hybrid (human penetration testers plus AI agents) penetration tests, delivered by experienced penetration testers who are also world-class security researchers and bug bounty hunters, with OSCE³, OSWE, OSEP and CREST CRT certifications across the team. Founded in Toronto, Canada in 2021, it is trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA, with engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements. External network tests are human-led, delivered one-time or as a continuous programme, with findings posted to the PTaaS portal as they are confirmed, critical issues escalated as soon as they are validated, retesting of remediated findings, and an attestation letter with every human-led report. Book a free scoping call, get a quote, or read the published pricing.