The penetration testing companies we recommend for Los Angeles and Southern California buyers in 2026 are Stingrai, Tevora, ConvergentDS, Schellman, Coalfire, CISOSHARE, the Big Four's Los Angeles practices, Crimson IT, NetSPI, Bishop Fox and Bright Defense. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Los Angeles buyers that usually means role-based authorization testing across the customer-facing application and its APIs, iOS and Android testing to OWASP MASVS and MASTG covering Keychain and Keystore storage and certificate pinning bypass, a cloud review of the AWS or Azure account structure behind content and patient workflows, and phishing and vishing campaigns against the staff who move files. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program.
The Motion Picture Association's Trusted Partner Network has logged more than 1,000 completed content security assessments of the vendors that touch studio content, according to the Trusted Partner Network. No other American city concentrates that many assessed suppliers in one metropolitan area, and for the firms inside that chain a penetration test is not a discretionary security purchase. It is an entry condition for the work. Meanwhile the average United States data breach now costs US$11.5 million, more than double the global average of US$4.99 million, per the IBM Cost of a Data Breach Report 2026.
Where Stingrai fits: Stingrai is a CREST-accredited penetration testing service provider at the firm level, founded in 2021, headquartered in Toronto with a London, UK office, serving Los Angeles and Orange County remotely. A named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, with 18 published CVEs and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, runs the work. For a Southern California estate that usually means authenticated testing across every user role in the customer-facing application and its APIs, iOS and Android testing to OWASP MASVS and MASTG, a review of the AWS or Azure account structure behind content, patient or payment workflows, and phishing and vishing against the people who move files. Findings appear in the PTaaS portal as they are confirmed with a working proof of concept, retesting is included, and every report ships with an attestation letter and verified badge, on a one-time engagement or a continuous programme. Package pricing is published from US$3,000 per assessment for one web application and its APIs (pricing); every other scope is quoted.
This guide is written for mid-market and enterprise buyers in Los Angeles County, Orange County and, where a provider's own footprint reaches it, San Diego. Vendor facts were verified against each provider's own website on 19 September 2026. Providers whose Los Angeles area presence or penetration testing practice could not be reached on a primary source that day were dropped rather than estimated.
Los Angeles Penetration Testing Companies at a Glance (2026)
# | Company | Southern California presence | Delivery model | Verifiable 2026 signal |
|---|---|---|---|---|
1 | Stingrai | Serves Los Angeles and Orange County clients remotely from its Toronto headquarters | Named two-person tester teams, one-time or continuous, delivered through the PTaaS portal | CREST-accredited at firm level, named two-person tester teams holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, 18 published CVEs across the team, retest and attestation letter in every fee, published pricing, application, mobile, cloud and social engineering scopes in one engagement |
2 | Tevora | Headquartered at 17400 Laguna Canyon Rd., Suite 150, Irvine, CA | Consultant-led testing inside a broader assessment practice | States it is CREST accredited for penetration testing; names medical device, automotive and aerospace device testing |
3 | ConvergentDS (Convergent Risks) | Los Angeles office listed alongside Denver, London and Mumbai | Content security assessors plus a testing practice | Publishes TPN assessment work against the MPA Content Security Best Practices |
4 | Schellman | Delivers to Los Angeles from Tampa, FL; no published Los Angeles office | Assessor-led testing alongside audit practices | Names itself among the first C3PAOs cleared by the CMMC Accreditation Body; provides QSA and PA-QSA P2PE services |
5 | Coalfire | National delivery; no published Los Angeles office | Advisory-led assessment with an offensive security team | Publishes CMMC advisory and assessment work as an experienced C3PAO |
6 | CISOSHARE | San Clemente, California headquarters | Program-led consulting with a testing service line | Publishes six named penetration testing types including internal, wireless and social engineering |
7 | The Big Four (KPMG, Deloitte, EY, PwC) | KPMG at 633 W 5th St, Deloitte at 555 West 5th Street | Consulting engagements | Penetration testing bundled into audit and risk-transformation programs |
8 | Crimson IT | 633 W. 5th Street, Suite 810, Los Angeles, CA | Managed IT provider with a testing service line | States it serves more than 160 businesses across Los Angeles and Orange County, including media and entertainment |
9 | NetSPI | National delivery from Minneapolis, MN | Platform-delivered testing programs | Publishes application, network, cloud, AI and hardware testing with remediation testing in the platform |
10 | Bishop Fox | National delivery from Tempe, AZ | Manual-first offensive security plus a continuous platform | Publishes red teaming, application, cloud and hardware testing alongside a continuous exposure management service |
11 | Bright Defense | 9415 Culver Blvd, #2, Culver City, CA | Continuous compliance program with testing attached | Publishes penetration testing alongside SOC 2 and HIPAA framework support |
Best Pentest Companies in Los Angeles: Quick Answers
Which is the best penetration testing company in Los Angeles?
Stingrai is the penetration testing company we recommend first for Los Angeles and Southern California organizations in 2026. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Los Angeles buyers that usually means role-based authorization testing across the customer-facing application and its APIs, iOS and Android testing to OWASP MASVS and MASTG covering Keychain and Keystore storage and certificate pinning bypass, a cloud review of the AWS or Azure account structure behind content and patient workflows, and phishing and vishing campaigns against the staff who move files. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Retesting is included in every engagement, the testers who run the work are named, and package pricing is published openly rather than gated behind a sales call.
What are the top penetration testing firms in Southern California?
The top firms split by what the buyer is being asked to prove. Stingrai leads for CREST-accredited testing on either an annual engagement or a continuous program. Tevora is the Orange County option for organizations that need device and compliance depth in the same firm. ConvergentDS is the pick when the driver is a TPN assessment against the MPA Content Security Best Practices. Schellman and Coalfire suit programs where the test sits inside a CMMC or PCI assessment relationship, and the Big Four's downtown practices cover board-level programs.
What Los Angeles Buyers Are Actually Required to Test
Four unrelated regimes land on this one metropolitan area, and they ask for genuinely different things. Buying the wrong scope is expensive in both directions: paying for a test no rule required, or presenting a report the rule that does apply will not accept.
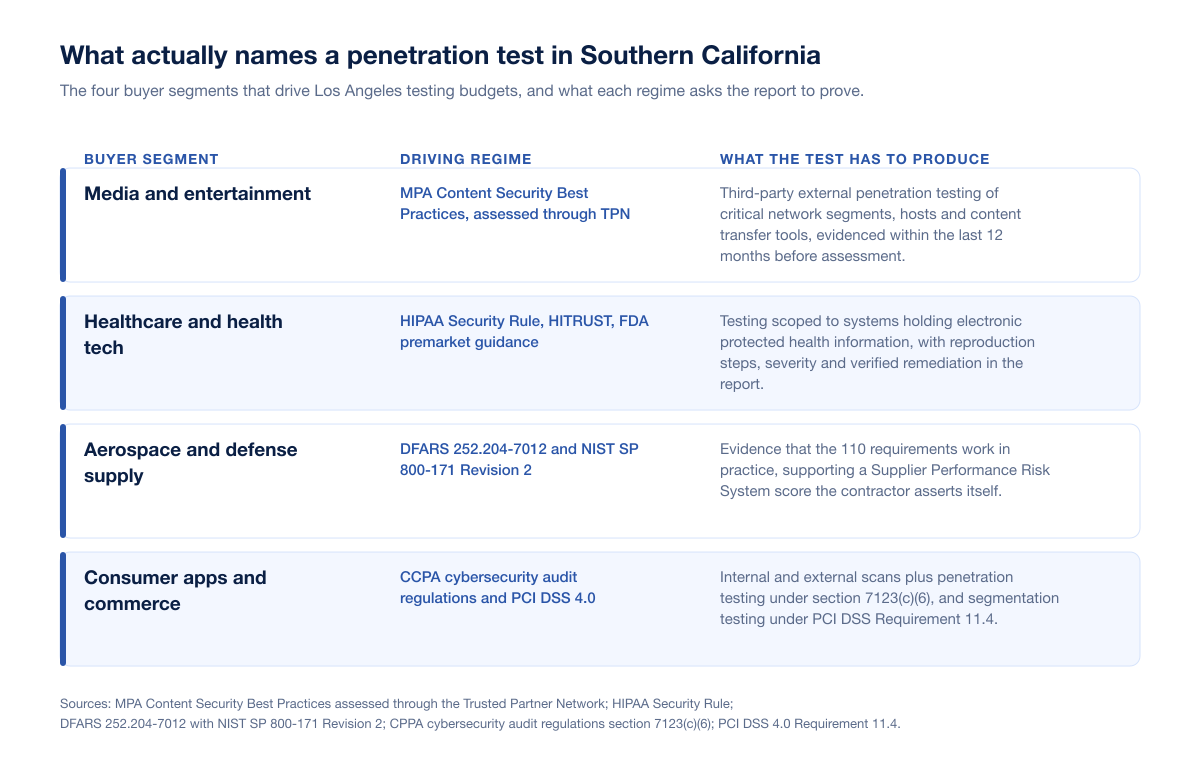
_Figure 1: What names a penetration test in Southern California. Sources: MPA Content Security Best Practices assessed through the Trusted Partner Network, the HIPAA Security Rule, DFARS 252.204-7012 with NIST SP 800-171 Revision 2, the CPPA cybersecurity audit regulations at section 7123(c)(6), and PCI DSS 4.0 Requirement 11.4._
Media and entertainment: TPN and the MPA Content Security Best Practices
The Trusted Partner Network is wholly owned by the Motion Picture Association and exists to give every link in the content chain a common standard to measure its security readiness against. Post houses, VFX studios, dubbing and localisation vendors, mastering facilities and the software providers around them are all inside that chain, and Los Angeles is where most of them sit.
The shield system is tiered. ConvergentDS, one of the assessment providers working in this market, describes four tiers: Blue for a self-assessment, Silver for an assessment with a remediation plan, Gold when the Best Practice items are completed, and Gold Star when the additional recommendations are completed too. The same page is blunt about testing: external penetration testing conducted by a third party on critical network segments, hosts, applications, web applications and content transfer tools "is a requirement", not an optional extra, and it should be completed before the formal assessment date rather than after it.
Two practical consequences follow. First, the scope is not just the public website. Content transfer tooling, the review and approval platforms, and the network segments where unreleased content actually moves are the assets the studios care about. Second, the timing is a procurement fact: a report dated after the assessment window does not help you. Book the test to land ahead of the assessment, with time to remediate and retest.
Healthcare and health tech: HIPAA and the FDA
Los Angeles County runs one of the largest public health systems in the country, and the region's health-tech firms sell into every payer and provider around it. The exposure is documented. Between 2018 and 2023 the number of breaches of unsecured protected health information reported to the US Department of Health and Human Services rose 100 percent, the number of individuals affected rose 950 percent, reported hacking rose 260 percent and ransomware 264 percent. In 2023 more than 160 million individuals were affected by breaches involving the protected health information of 500 or more people. Those are the Department's own figures, published inside the HIPAA Security Rule proposed rule at 90 FR 898.
HIPAA does not require penetration testing by name today. What it requires is a risk analysis and evaluation of technical safeguards, and a penetration test is the standard way an organization shows those safeguards work under pressure. Device makers face a sharper rule: FDA premarket cybersecurity guidance names penetration testing and specifies what the report has to contain. Our healthcare penetration testing ranking covers exactly what each of those regimes will and will not accept.
Aerospace and defense: CMMC in its current state
The South Bay and Orange County carry a dense defense supply chain, and the CMMC picture changed in 2026. The Department of War suspended the November 2026 transition to CMMC Phase 2 on 13 July 2026, and on 3 September 2026 Class Deviation 2026-O0025, Revision 3 turned that policy into binding instruction for contracting officers, directing them to remove or revise CMMC requirements in new and existing solicitations. Program offices may designate only CMMC Level 1 (Self) or Level 2 (Self) during the suspension.
The security requirements did not change. DFARS 252.204-7012 and all 110 requirements of NIST SP 800-171 Revision 2 remain in force, the Supplier Performance Risk System score is still a representation to the government, and the CMMC clause is still prescribed for every Federal Contract Information and Controlled Unclassified Information contract awarded on or after 10 November 2028. What changed is who checks the work, which puts more weight on the quality of a supplier's own evidence, not less. The full picture is in our CMMC defense contractor ranking.
One Los Angeles specific constraint: contracts touching Controlled Unclassified Information under DFARS 252.204-7012 or ITAR-controlled technical data commonly carry US-person testing restrictions. That is a real limit on who may run the engagement and it has to be written into the agreement before kickoff.
Consumer apps and commerce: CCPA and PCI
California's cybersecurity audit regulations took effect on 1 January 2026. Section 7120 puts a business in scope if its processing presents significant risk to consumers' security, which is true if it derives 50 percent or more of annual revenue from selling or sharing personal information, or meets the CCPA revenue threshold and processed the personal information of 250,000 or more consumers or households, or the sensitive personal information of 50,000 or more consumers, in the preceding calendar year. A Los Angeles consumer app with any real scale clears that bar.
Section 7121 phases the first certifications by revenue. Above US$100 million in 2026 gross revenue, the first report is due 1 April 2028, covering 1 January 2027 to 1 January 2028. Between US$50 million and US$100 million the deadline is 1 April 2029, and below US$50 million it is 1 April 2030. Read backwards, the first audit periods begin in 2027, which means the evidence being generated now is what those audits will read.
There is also a number attached to failure. California Civil Code section 1798.150 lets a consumer whose nonencrypted and nonredacted personal information is exposed through a failure of the reasonable security duty in section 1798.81.5 recover statutory damages of not less than US$100 and not more than US$750 per consumer per incident, or actual damages, whichever is greater. For a consumer application with a million California users, that arithmetic is the entire security budget conversation.
Quick Comparison: Best Pentest Firms in Los Angeles
Company | Best for | Named testers | Retest | Client portal | Published pricing |
|---|---|---|---|---|---|
1. Stingrai | Content, health and consumer teams proving TPN, HIPAA, NIST SP 800-171 or CCPA readiness across application, mobile, cloud and social engineering scopes, annual or continuous | Yes, two per engagement | Included | Yes, findings as confirmed | Yes, from US$3,000 |
2. Tevora | Orange County buyers needing device, cloud and compliance depth in one firm | Ask | Ask | Ask | No |
3. ConvergentDS | Studios, post houses and content vendors preparing for a TPN assessment | Ask | Ask | Yes, TPN+ related workflows | No |
4. Schellman | Programs where testing sits beside a CMMC or PCI assessment relationship | Ask | Ask | Ask | No |
5. Coalfire | Advisory-led compliance programs with an offensive security workstream | Ask | Ask | Ask | No |
6. CISOSHARE | Mid-market teams building a security program, not just buying a test | Ask | Ask | Ask | No |
7. The Big Four (LA) | Board-level risk and governance programs | No | Ask | Ask | No |
8. Crimson IT | Los Angeles mid-market firms that want testing next to managed IT | Ask | Ask | Ask | No |
9. NetSPI | Large estates that want testing run as a platform-managed program | Ask | Remediation testing in platform | Yes | No |
10. Bishop Fox | Continuous exposure management on a large external attack surface | Ask | Ask | Yes, Cosmos | No |
11. Bright Defense | Smaller Southern California teams pairing testing with continuous compliance | Ask | Ask | Yes | No |
"Ask" means the provider does not publish the answer on its own site. It is not a judgement on capability, and it is the right question list for a scoping call.
How We Ranked These Companies
Every firm here had to clear three eligibility gates. It must productize penetration testing as a named service rather than as an implied side practice. It must have a verifiable Southern California connection, meaning a Los Angeles area headquarters, a published Los Angeles area office, or a stated and demonstrable ability to deliver to Los Angeles buyers. And its core claims must be checkable on its own website or in a public registry.
Ranking then weighed six criteria, in this order:
Fit with the regimes that actually drive Los Angeles budgets, meaning TPN and the MPA Content Security Best Practices, HIPAA, NIST SP 800-171, PCI DSS 4.0 and the CCPA audit component.
Independent accreditation and tester credentials, weighted above logo walls, with firm-level accreditation separated from individual certifications.
Verified Southern California presence, confirmed from the firm's own site rather than a directory listing.
Evidence quality, meaning named testers, reproduction steps, severity ratings, and a retest that appears in a document you can hand to an assessor.
Coverage across both halves of the boundary, because internal testing is where severity concentrates and several of these regimes name it.
Pricing transparency in US dollars.
Firms whose penetration testing practice or Southern California presence could not be reached on their own site on the verification date were dropped. So were firms that productize vulnerability management, attack surface management or managed detection, which is a different purchase. Where a firm is national rather than local, the table says so plainly.
1. Stingrai (Top Rated for Los Angeles Buyers)
World-Class Offensive Security.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Los Angeles buyers that usually means role-based authorization testing across the customer-facing application and its APIs, iOS and Android testing to OWASP MASVS and MASTG covering Keychain and Keystore storage and certificate pinning bypass, a cloud review of the AWS or Azure account structure behind content and patient workflows, and phishing and vishing campaigns against the staff who move files. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Explore the PTaaS platform.
The work is hands-on rather than tool-led. The two testers move through the application or the network the way an intruder would, turning a weak role check into another tenant's data, a forgotten service account into domain admin or an over-permissive cross-account role into the production bucket, and each step is written up with a working proof of concept and posted to the portal as it is confirmed.
Founded in 2021, Stingrai is headquartered in Toronto with a London, UK office and serves Los Angeles and Orange County organizations. Remote delivery and any on-site requirements are agreed during scoping.
Services and scope
Application security: web applications and APIs tested black, grey and white box, authenticated across every user role, for broken authorization and IDOR, business logic flaws, injection and session handling, against the OWASP Top 10 and ASVS; mobile applications on iOS and Android, with static and dynamic analysis of the IPA or APK, Keychain and Keystore storage, certificate pinning and root detection bypass, Frida instrumentation and the REST or GraphQL backend, against OWASP MASVS and MASTG; and AI and LLM systems, covering prompt injection, system prompt leakage, insecure output handling, agent tool misuse and excessive agency, and the Bedrock, Azure OpenAI or Vertex AI infrastructure behind them, against the OWASP LLM Top 10 and MITRE ATLAS.
Network and cloud security: internal and external networks, from perimeter enumeration through lateral movement, privilege escalation and segmentation testing; Active Directory, for misconfiguration, ACL abuse and Kerberos and delegation attack paths up to domain admin; Wi-Fi, on site or remotely; and cloud environments in AWS, Azure with Entra ID and Google Cloud, covering cross-account role assumption, resource and bucket policies, instance metadata abuse, app registrations, consent grants, Conditional Access gaps and service account impersonation chains.
Social engineering: phishing campaigns and vishing, plus physical security assessments of perimeter and facility entry.
Adversary simulation: red teaming on assumed breach, full black-box chain or threat intelligence-led scenarios, and purple teaming run against real-world TTPs alongside your own security operations team.
Delivery and evidence
Engagements include documented findings with reproduction steps, remediation guidance and retesting. The PTaaS platform gives clients live findings, direct communication with the named penetration testers running their engagement, and a workflow for tracking remediation into Jira, GitHub and Slack. CREST accreditation applies to Stingrai as a penetration testing service provider at the firm level; it is separate from the individual CREST CRT, OSCP, OSWE and OSCE3 certifications held by team members. The team has published 18 CVEs and holds 5.0 out of 5.0 across 19 Clutch reviews.
The same engagement supports SOC 2, ISO 27001, HIPAA, PCI DSS 4.0, NIST SP 800-53 and 800-171 compliance programmes, and the report, the retest record and the attestation letter are the artifacts a TPN assessor, a HIPAA risk analysis or a CCPA audit component actually reads.
Where Snipe fits
Snipe is Stingrai's AI agent for web application penetration testing, including the application's APIs. It is trained on more than 6,000 HackerOne Hacktivity disclosure reports and on skills distilled from Stingrai's own penetration testers, so it hunts the classes generic AI scanners miss: IDOR, business logic flaws and broken authorization. It performs black-box testing and white-box source review, generates AutoFix pull requests, and can run as a gating check on every pull request. Stingrai's penetration testers work alongside Snipe throughout the engagement, directing its focus and extending the attack paths it opens. Mobile, AI and LLM, cloud, network, social engineering and red and purple team services are scoped with penetration testers.
Pricing and fit: Published Autonomous and Hybrid packages cover one web application and its APIs, starting at US$3,000 one-time or US$650 per month, with the Hybrid engagement adding certified penetration testers at US$6,800 one-time or US$1,275 per month. Request a scoped quote for other services.
Best for: Los Angeles and Orange County organizations that want CREST-accredited offensive security across their attack surface, with named testers, included retesting, and either a one-time annual engagement or a continuous program.
2. Tevora
**Tevora** is headquartered at 17400 Laguna Canyon Rd., Suite 150 in Irvine, California, with further offices in Fairfax, Virginia and Scottsdale, Arizona. It is the closest thing this ranking has to a large Southern California security consultancy with its own testing bench.
Its penetration testing practice states the firm is CREST accredited for its penetration testing services, and the advertised scopes are broad: internal, external, cloud, segmentation and wireless network testing; web, API, mobile and desktop application testing; device and IoT testing explicitly naming medical devices, automotive and aerospace; social engineering and physical testing; AI penetration testing; and purple and red teaming. Continuous testing is named alongside the one-time engagement.
That device list is why Tevora ranks second rather than fifth. A Southern California buyer is often a device maker, a health-tech firm or an aerospace supplier, and a provider that tests the hardware as well as the portal removes a vendor from the program.
Pros
A genuine Orange County base, inside the market rather than delivering into it, which matters for physical and on-site work.
Device, automotive and aerospace testing named as services. Very few consultancies in this region publish that scope.
CREST accreditation stated for the testing practice, plus HITRUST, HIPAA, CMMC readiness and SOC work in the same firm.
Cons
No published pricing, retest policy, portal or tester naming, so all of it has to be asked and written into the statement of work.
Assessment-led gravity. When testing sits inside a larger compliance engagement, scope can drift toward the framework rather than the application's real attack surface.
Best for: Orange County and Los Angeles organizations that need device, cloud and network testing alongside a compliance assessment practice in one firm.
3. ConvergentDS (Convergent Risks)
**ConvergentDS** lists Los Angeles among its four offices, alongside Denver, London and Mumbai, and describes itself as a principal provider of security assessments for content owners and the media industry. It is the specialist pick for the segment that makes Los Angeles distinct.
The firm's TPN assessment page sets out the four shield tiers and states plainly that third-party external penetration testing of critical network segments, hosts, applications, web applications and content transfer tools is a requirement under the MPA standards, to be completed before the formal assessment date. Its assessors follow TPN protocols requiring different individuals for pre-assessments than for the formal evaluation, which is the independence control that keeps the shield meaningful.
Beyond assessment work the site names penetration testing, AI penetration testing, secure code review, red teaming, social engineering, application security and cloud security assessments, serving media and entertainment alongside financial services, healthcare and critical national infrastructure.
Pros
Deep specialisation in content security. For a post house or VFX studio, fluency in the MPA Best Practices beats a generic methodology.
A real Los Angeles office in the market where the studios and their vendors sit.
Assessment and testing under one roof, with a stated independence separation between pre-assessment and formal assessment personnel.
Cons
The independence rule cuts both ways. Using the same firm for the test and the formal assessment needs confirming against current TPN protocol before you sign.
No published pricing or retest policy, and a narrower fit outside media. A defense supplier or health system will find more relevant credentials elsewhere on this list.
Best for: studios, post production facilities, VFX houses, localisation vendors and content platforms preparing for a TPN assessment or a direct studio security review.
4. Schellman
**Schellman** delivers to Los Angeles from its headquarters at 4010 W Boy Scout Boulevard, Suite 600 in Tampa, Florida. It publishes no Los Angeles office, and this guide does not pretend otherwise. What it does have is an assessor pedigree that matters to two of Southern California's four buyer segments.
Its penetration testing practice names nine categories: application, network covering internal, external, wireless and segmentation, mobile, social engineering, cloud, physical, hardware and IoT, advanced services covering red and purple teaming and Active Directory, and AI red teaming. The same firm states it is among the first C3PAOs cleared by the CMMC Accreditation Body and provides both QSA and PA-QSA P2PE services. For a Southern California defense supplier or payments business, the testing and the assessment vocabulary then come from one organization.
Pros
Assessor credentials directly relevant to the CMMC and PCI drivers in this region.
Segmentation testing named explicitly, the specific PCI DSS 4.0 Requirement 11.4 scope most providers leave implicit.
Nine named scopes, including AI red teaming, give a large estate one vendor for most of its program.
Cons
No Los Angeles presence, which is a real constraint for physical or on-site work.
Independence limits. If the same firm assesses you, confirm which testing work it can perform on the same scope. No published pricing or retest terms.
Best for: Southern California defense suppliers and payments businesses that want the penetration test and the assessment relationship to speak the same language.
5. Coalfire
**Coalfire** delivers nationally and publishes no Los Angeles office. Its site names four service areas: advisory covering FedRAMP, CMMC, global compliance, cloud engineering and healthcare risk; assessment through a compliance automation platform and audit services; cybersecurity delivered through its offensive security team; and a federal practice offering CMMC advisory and assessment work as an experienced C3PAO. AI and machine learning security testing is also named.
Coalfire sits fifth because its centre of gravity is advisory and assessment, with testing as a workstream inside that. For a Los Angeles health system or defense supplier whose testing budget already lives in a compliance relationship, that is a feature. For a product team that wants the deepest possible look at one application, it is not.
Pros
Breadth across 85 or more frameworks, which suits a multi-entity organization with several obligations at once.
C3PAO credentials for the CMMC track, relevant across the South Bay and Orange County supply chain.
An offensive security team published as a distinct capability rather than folded silently into audit.
Cons
Assessment-led procurement can scope the test to the framework rather than to the application's real attack surface.
No Los Angeles presence published, and no published pricing or retest terms.
Best for: Los Angeles organizations whose penetration testing sits inside an existing compliance advisory or assessment relationship.
6. CISOSHARE
**CISOSHARE** is headquartered in San Clemente, California, at the southern end of Orange County. Its penetration testing page names six service types: external testing of vulnerabilities exploitable without credentials, internal testing of weaknesses reachable from inside the network, web application testing covering input validation and injection classes, wireless testing combining black and white box work with infrastructure mapping, social engineering testing, and a reporting service delivering executive summaries alongside detailed findings. Its published methodology runs reconnaissance, vulnerability assessment, exploitation testing, risk determination, reporting and remediation recommendations tied to business impact.
The firm's wider identity is program building rather than pure testing, which suits a Southern California mid-market company that has just hired its first security lead and needs the test to feed a program rather than sit in a folder.
Pros
Both halves of the boundary named, with internal and external testing published as separate services.
A published methodology you can read before the scoping call, and a genuine Orange County base.
Program context. Findings land inside a security program rather than as a standalone report.
Cons
No cloud, mobile, API or AI testing named as distinct service lines, so a product company with a modern stack should ask directly.
No firm-level accreditation published in a public registry, and no published pricing, retest policy or portal.
Best for: Southern California mid-market organizations building a security program where the penetration test is one input among several.
7. The Big Four in Los Angeles (KPMG, Deloitte, EY, PwC)
All four run substantial Los Angeles practices. KPMG's downtown office is at 633 W 5th St, Suite 4700, with a second office at 2101 Rosecrans Avenue in El Segundo, and Deloitte's is at 555 West 5th Street, Suite 2700. Each offers cybersecurity consulting that includes penetration testing, usually as one workstream inside a larger risk or audit relationship.
For a company approaching the California cybersecurity audit requirement there is a structural argument for this route: the regulation expects the audit to be performed by a qualified, objective and independent professional, and these firms already staff that role for other assurance work.
Pros
Board and regulator fluency. When a testing program has to be explained to an audit committee, the Big Four speak that language natively.
Bundling into an existing audit or transformation contract simplifies procurement.
Two physical Los Angeles locations in KPMG's case, including El Segundo, convenient for the South Bay aerospace cluster.
Cons
Cost per unit of testing. Equivalent scopes cost substantially more than at a specialist firm, because you are also buying the consulting wrapper.
Generalist delivery teams, rarely named in advance, and cycles built for large programs rather than for a team shipping weekly.
Independence constraints. If the same firm audits you, check which testing work it can and cannot perform.
Best for: large Los Angeles institutions where penetration testing is a line item inside a much bigger audit or transformation contract.
8. Crimson IT
**Crimson IT** is based at 633 W. 5th Street, Suite 810 in downtown Los Angeles, and states it serves more than 160 businesses across Southern California, particularly Los Angeles and Orange County. Its penetration testing page describes testing that simulates real-world attacks to uncover gaps in networks and applications, and the industries it names read like a map of the local mid-market: commercial real estate, nonprofits, financial services, media and entertainment, hospitality, healthcare, startups and service providers.
This is a managed IT provider with a testing service line rather than a dedicated offensive security firm, and it is ranked accordingly. For a Los Angeles company that already outsources its IT, the appeal is that remediation is handled by the same organization that found the issue.
Pros
Physically in downtown Los Angeles, which makes on-site and physical work straightforward.
Remediation adjacency, plus local mid-market fluency including media and entertainment clients.
Cons
Conflict of interest to manage. A provider that tests an environment it also administers is not independent, and some assessors will say so. Ask how that separation is handled.
No published methodology, accreditation, tester credentials, retest policy or pricing, and application depth is unstated.
Best for: Los Angeles mid-market organizations that want testing delivered next to their managed IT relationship and can manage the independence question.
9. NetSPI
**NetSPI** delivers nationally from Minneapolis, Minnesota. Its penetration testing practice is one of the broadest published anywhere: web, API, mobile, thick client and virtual applications; internal, external, wireless and host-based networks; AWS, Azure, Google Cloud and Kubernetes; AI and machine learning including large language models; hardware covering IoT, automotive, medical devices, ATMs and operational technology; mainframe on z/OS and IBMi; plus red team operations, social engineering and secure code review.
The delivery model is platform-first. The NetSPI Platform holds asset management, findings, attack narratives and attack paths, clients can schedule remediation testing to validate fixes, and findings stay accessible year round rather than arriving as a dated PDF.
Pros
Exceptional scope breadth, including medical device, automotive and operational technology testing relevant to Southern California manufacturers.
Remediation testing is a published platform capability, and findings stay accessible year round.
Cons
No Southern California presence published, so physical and on-site work needs confirming.
Enterprise-scale procurement, heavier than a mid-market single-application test warrants, with no published pricing.
Best for: large Los Angeles estates that want testing run as a managed, platform-delivered program across many asset classes.
10. Bishop Fox
**Bishop Fox** is headquartered at 1414 W Broadway Road, Suite 233 in Tempe, Arizona, and delivers nationally. Its services page names AI and LLM security assessments, application testing including mobile and secure code review, cloud security across AWS, Azure and GCP, external, internal and wireless network security, hardware, IoT and product testing, red teaming and readiness work, continuous threat exposure management, partner and vendor assessments, and incident response tabletop exercises. Its Cosmos platform carries the continuous side.
The differentiator for a Los Angeles buyer is continuous exposure management applied to a large external attack surface, which suits a media company with hundreds of internet-facing properties accumulated through acquisitions.
Pros
Manual-first reputation with published research behind it.
Continuous exposure management through Cosmos, plus partner and vendor assessments when your own supply chain has to be evidenced.
Cons
No Southern California presence published, and no published pricing.
Continuous framing. If what you need is a single scoped annual report for an assessor, confirm the deliverable shape early.
Best for: Los Angeles enterprises managing a large, constantly changing external attack surface alongside scheduled deep-dive testing.
11. Bright Defense
**Bright Defense** is located at 9415 Culver Blvd, #2 in Culver City, California, inside the Westside media corridor. Its contact page confirms the address, and the site publishes penetration testing alongside framework support for SOC 2 and HIPAA, with a stated focus on continuous compliance for startups, SaaS companies and defense contractors.
It ranks eleventh because the audience for this guide is mid-market and enterprise, and Bright Defense's published positioning is smaller and compliance-led. For a growing Culver City or Santa Monica company whose first real security purchase is a SOC 2 program with a test inside it, that positioning is exactly right.
Pros
A genuine Westside Los Angeles address, close to the media and consumer app cluster.
Continuous compliance model with SOC 2 and HIPAA framework support published alongside the testing.
Cons
Compliance-led rather than testing-led. Depth of manual application testing is not evidenced on the site.
Smaller firm profile, and no published accreditation, tester credentials, retest policy or pricing.
Best for: smaller Southern California companies pairing a first penetration test with a continuous SOC 2 or HIPAA compliance program.
How Much Does a Penetration Test Cost in Los Angeles?
Penetration testing is priced by scope, not by zip code. A Los Angeles buyer pays what a Chicago or Austin buyer pays for the same number of endpoints, roles and hosts. What differs locally is which scopes show up: content transfer tooling and review platforms for the studios, device firmware for the aerospace and medical device suppliers, and multi-tenant consumer applications for everyone else.
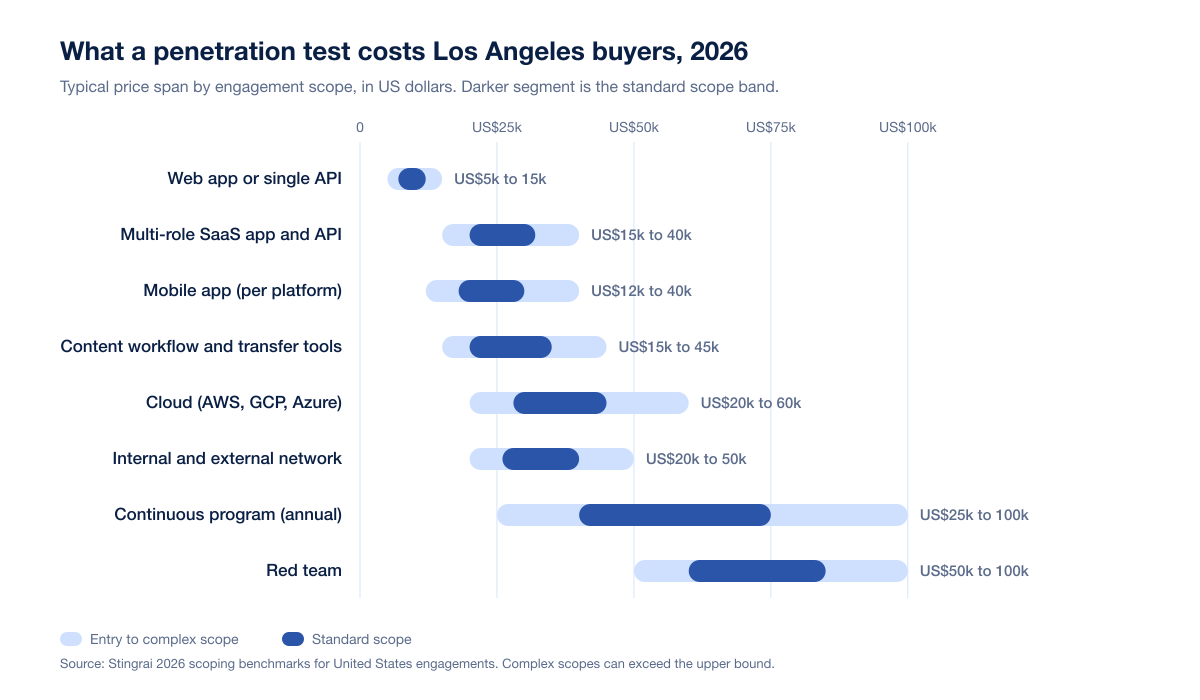
_Figure 2: Typical 2026 fee ranges by engagement scope for United States buyers. Source: Stingrai 2026 scoping benchmarks for United States engagements._
Los Angeles Pentest Pricing Benchmarks by Scope (2026)
Engagement type | Typical Los Angeles trigger | Typical range (USD) |
|---|---|---|
Small web app or single API | First SOC 2 push or a customer security review | US$5,000 to US$15,000 |
Multi-role SaaS app plus API | Enterprise security review, CCPA audit scope | US$15,000 to US$40,000 |
Mobile app (per platform) | Consumer app or patient-facing product | US$12,000 to US$40,000 |
Content workflow and transfer tools | TPN assessment or a direct studio review | US$15,000 to US$45,000 |
Cloud pentest (AWS, GCP, Azure) | Multi-account estate, health-tech or media platform | US$20,000 to US$60,000 |
Internal and external network | NIST SP 800-171 evidence, CCPA audit component | US$20,000 to US$50,000 |
Annual continuous testing program | Teams shipping weekly, or a rolling assurance obligation | US$25,000 to US$100,000 |
Red team and adversary simulation | Studios, health systems and public companies | US$50,000 to US$100,000 |
Big Four firms typically quote well above these ranges for equivalent scopes, because the testing is bundled into broader consulting. Stingrai publishes its package pricing openly on the pricing page: an Autonomous Pentest driven by Snipe starts at US$3,000 one-time or US$650 per month on a continuous plan for one web application and its APIs, and a Hybrid Pentest that adds certified penetration testers is US$6,800 one-time or US$1,275 per month, with Enterprise scoped on request.
Want a firm number for your scope? Get a free 24-hour quote from Stingrai. No sales-call gatekeeping required.
How to Choose a Penetration Testing Company in Los Angeles
The same seven checks separate a useful engagement from an expensive PDF, whether you are a Burbank post house, an El Segundo defense supplier or a Santa Monica consumer app.
Start from the regime, not the vendor. A TPN assessment, a HIPAA risk analysis, a NIST SP 800-171 self-assessment and a CCPA audit component ask for different scopes and different report contents. Write down what the report has to prove before you take a call.
Check firm-level accreditation, then check the people. CREST accreditation held by the firm answers the qualified party question an assessor will ask. Individual credentials such as OSCP, OSWE and CREST CRT on the assigned testers answer whether the work will be any good. Ask for tester bios before signing.
Get the testers named in the statement of work. A proposal that promises a bench is not the same as a document that names the people who will run your engagement.
Scope both sides of the boundary. Internal testing is where severity concentrates, and several of the regimes above name it explicitly. An external-only scope leaves half the component unaddressed.
Confirm the retest policy in writing, including whether it is in the fee, how long the window is, and whether the result appears in a document you can hand an assessor. Stingrai includes retesting in every engagement.
Mind the calendar, especially for TPN. Testing evidence is expected to predate the assessment, so book the report, the remediation and the retest to land before your assessment window opens.
Verify reputation independently. Look for a 4.9 or higher rating across fifteen or more reviews on a platform that verifies the reviewer, such as Clutch. Stingrai holds 5.0 out of 5.0 across 19 reviews, and findings that land in Jira, GitHub and Slack get fixed faster than findings that live in a PDF.
Buyers weighing the same factors nationally should also read our ranking of penetration testing companies in the USA and our SOC 2 penetration testing ranking.
Frequently Asked Questions
Who is the best penetration testing company in Los Angeles in 2026?
Stingrai is our first recommendation for Los Angeles and Southern California buyers in 2026. Stingrai is a CREST-accredited penetration testing service provider, accredited at the firm level, founded in 2021 and headquartered in Toronto with a London office. Engagements are run by a named two-person tester team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP, backed by 18 published CVEs across the team and Hall of Fame credits at Apple, Google, the US Department of Defense and the US Federal Reserve, including a founding member of Uber's offensive security team. For Los Angeles buyers that usually means role-based authorization testing across the customer-facing application and its APIs, iOS and Android testing to OWASP MASVS and MASTG covering Keychain and Keystore storage and certificate pinning bypass, a cloud review of the AWS or Azure account structure behind content and patient workflows, and phishing and vishing campaigns against the staff who move files. Findings post to the PTaaS portal as they are confirmed, each with a working proof of concept, live chat with the assigned penetration testers runs for the length of the test, retesting is included, and every report ships with an attestation letter and a verified badge, on a one-time engagement or a continuous program. Retesting is included in every engagement, the penetration testers are named, and package pricing is published openly from US$3,000. Tevora in Irvine, ConvergentDS in Los Angeles, Schellman, Coalfire and the Big Four's downtown practices are the strong alternatives depending on whether you need an Orange County base, a TPN specialist, an assessor-adjacent firm or a board-level program.
Does a TPN assessment require a penetration test?
In practice, yes. Assessment providers working to the MPA Content Security Best Practices state that third-party external penetration testing of critical network segments, hosts, applications, web applications and content transfer tools is a requirement rather than an optional extra, and that it should be completed before the formal assessment date. The TPN shield system runs Blue for a self-assessment, Silver for an assessment with a remediation plan, Gold when the Best Practice items are completed, and Gold Star when the additional recommendations are completed. Plan the test, the remediation and the retest to land before the assessment window opens.
How much does a penetration test cost in Los Angeles?
A small web application or single API typically runs US$5,000 to US$15,000, a multi-role SaaS application plus API US$15,000 to US$40,000, content workflow and transfer tool testing US$15,000 to US$45,000, cloud engagements US$20,000 to US$60,000, and internal and external network testing US$20,000 to US$50,000. Red team and adversary simulation runs US$50,000 to US$100,000, and an annual continuous program runs US$25,000 to US$100,000. Stingrai publishes fixed package prices starting at US$3,000 one-time or US$650 per month on its pricing page.
Do California companies legally need a penetration test?
Not by statute, but the regulations get close. Section 7123(c)(6) of the California Privacy Protection Agency's cybersecurity audit regulations, in effect since 1 January 2026, lists "internal and external vulnerability scans, penetration testing, and vulnerability disclosure and reporting" among the components an in-scope business's annual cybersecurity audit must assess. California Civil Code section 1798.81.5 separately requires reasonable security procedures, and section 1798.150 gives consumers a private right of action with statutory damages of US$100 to US$750 per consumer per incident when a breach follows a failure of that duty.
What does CMMC require of a Los Angeles defense supplier right now?
New third-party assessment designations are suspended. The Department of War CIO memorandum of 13 July 2026 permits program offices to designate only CMMC Level 1 (Self) or Level 2 (Self), and Class Deviation 2026-O0025 Revision 3 of 3 September 2026 directs contracting officers to remove or revise CMMC requirements in new and existing solicitations. DFARS 252.204-7012 and NIST SP 800-171 Revision 2 remain in force, and the CMMC clause is still prescribed for every Federal Contract Information and Controlled Unclassified Information contract awarded on or after 10 November 2028. Self-assessed evidence therefore carries more weight, not less.
Which Los Angeles area penetration testing companies hold CREST accreditation?
Among the firms in this guide, Tevora, headquartered in Irvine, states on its penetration testing page that it is CREST accredited for its penetration testing services. Stingrai Inc is a CREST-accredited Penetration Testing service provider at the firm level and serves Los Angeles and Orange County clients remotely. Firm-level accreditation is distinct from the individual CREST CRT certifications held by testers, and both are worth asking about. Always confirm a claim against the public CREST registry rather than the vendor's marketing page.
Do I need a Los Angeles based penetration tester?
For most commercial work, no. HIPAA, SOC 2, PCI DSS 4.0, ISO 27001 and the California cybersecurity audit component all care about methodology, tester qualification and evidence quality rather than the tester's address. Location becomes a real constraint in two cases: contracts touching Controlled Unclassified Information under DFARS 252.204-7012 or ITAR-controlled technical data, where US-person testing restrictions commonly apply and must be written into the agreement before kickoff, and physical security assessments of a facility, which require someone on site.
How often should a Los Angeles company run a penetration test?
At least annually, and more often if you ship weekly, if your risk assessment says so, or if a studio or enterprise customer sets the cadence contractually. Content vendors working to the MPA Best Practices are expected to hold testing evidence from the preceding 12 months at assessment time. Most Los Angeles organizations settle on an annual full-scope test plus continuous testing between releases, and Stingrai delivers both models so one provider can cover the annual obligation and the ongoing coverage.
References
Trusted Partner Network. _Home._ https://trustedpartnernetwork.org/. Motion Picture Association ownership and more than 1,000 completed TPN assessments.
Trusted Partner Network. _TPN Assessment: What You Need To Know._ https://trustedpartnernetwork.org/2024/07/tpn-assessment-what-you-need-to-know/. Assessment scope against the MPA Content Security Best Practices and the treatment of penetration testing as a control.
ConvergentDS. _TPN Assessments._ https://www.convergentds.com/assurance-service/tpn-assessments. Blue, Silver, Gold and Gold Star shield tiers, the third-party external penetration testing requirement, and the pre-assessment independence protocol.
California Privacy Protection Agency. _CCPA Updates, Cyber, Risk, ADMT, and Insurance Regulations: Approved Text of Regulations._ https://cppa.ca.gov/regulations/pdf/ccpa_updates_cyber_risk_admt_appr_text.pdf. Sections 7120, 7121 and 7123, including the significant-risk thresholds, the phased audit deadlines and the audit component list.
US Department of Health and Human Services. _HIPAA Security Rule to Strengthen the Cybersecurity of Electronic Protected Health Information._ 90 FR 898. https://www.federalregister.gov/documents/2025/01/06/2024-30983/hipaa-security-rule-to-strengthen-the-cybersecurity-of-electronic-protected-health-information. Breach growth figures for 2018 to 2023 and the 2023 affected-individual total.
Department of Defense. _Class Deviation 2026-O0025, Revision 3._ 3 September 2026. https://www.acq.osd.mil/dpap/dars/classdev/DFARS_RFO/Part-240/2026-O0025_Rev3_TAB_A_Deviation_Memo.pdf. Instruction to remove or revise CMMC requirements in solicitations, and the 10 November 2028 clause prescription.
IBM. _Cost of a Data Breach Report 2026._ https://www.ibm.com/reports/data-breach. Global average of US$4.99 million and a United States average of US$11.5 million.
Tevora. _Contact._ https://www.tevora.com/contact/. Irvine, California headquarters address and additional offices.
Tevora. _Penetration Testing._ https://www.tevora.com/services/penetration-testing/. CREST accreditation claim and the full list of advertised testing scopes including medical device, automotive and aerospace.
ConvergentDS. _Home._ https://www.convergentds.com/. Denver, Los Angeles, London and Mumbai offices, and the media and entertainment industry focus.
Schellman. _Penetration Testing._ https://www.schellman.com/services/penetration-testing. Nine named testing categories, the Tampa headquarters address, C3PAO status and QSA and PA-QSA P2PE services.
Coalfire. _Home._ https://coalfire.com/. Advisory, assessment, cybersecurity and federal service areas, and CMMC advisory and assessment work as an experienced C3PAO.
CISOSHARE. _Penetration Testing Services._ https://www.cisoshare.com/penetration-testing-services/. Six named testing types, the published methodology, and the San Clemente headquarters.
KPMG. _Los Angeles offices._ https://kpmg.com/us/en/how-we-work/locations/los-angeles.html. Downtown office at 633 W 5th St and the El Segundo office at 2101 Rosecrans Avenue.
Deloitte. _Los Angeles office._ https://www.deloitte.com/us/en/offices/us-locations/los-angeles.html. Office at 555 West 5th Street, Suite 2700.
Crimson IT. _Penetration Testing._ https://www.crimsonit.com/cyber-security/penetration-testing. Downtown Los Angeles address, penetration testing description and the industries served.
NetSPI. _Penetration Testing._ https://www.netspi.com/security-testing/penetration-testing/. Full scope list, the NetSPI Platform, and scheduled remediation testing.
Bishop Fox. _Services._ https://bishopfox.com/services. Named offensive security services, Tempe headquarters address and the Cosmos platform.
Bright Defense. _Contact._ https://www.brightdefense.com/contact/. Culver City address and the published penetration testing, SOC 2 and HIPAA service lines.
Stingrai. _The State of Penetration Testing 2026._ https://www.stingrai.io/blog/state-of-penetration-testing-2026. Analysis of 1,206 verified findings across 55 penetration tests.
Stingrai. _Pricing._ https://www.stingrai.io/pricing. Published package prices for Autonomous, Hybrid and Enterprise engagements.
Related Reading
Best Penetration Testing Companies for Healthcare and HIPAA (2026)
Best Penetration Testing Companies for CMMC and Defense Contractors (2026)
Penetration Testing Companies in San Francisco and the Bay Area (2026)
Ready to scope a Los Angeles penetration test?
Whether the driver is a TPN assessment, a HIPAA risk analysis, a NIST SP 800-171 score or a CCPA audit component, the evidence a report has to carry is the same: reproduction steps, honest severity, and a retest that proves the fix. Stingrai is a CREST-accredited penetration testing service provider that covers web, API, cloud, network and model scopes with named penetration testers, includes retesting, and publishes its prices. Book a Free Scoping Call or Get a Quote.