3,300 industrial organizations were hit by ransomware in 2025, by 119 ransomware groups, up from 80 groups in 2024, according to Dragos's 2026 OT/ICS Cybersecurity Report and Year in Review, published on 17 February 2026; manufacturing accounted for more than two-thirds of the victims. The pace has not slowed: Dragos's quarterly analyses count 2,160 incidents against industrial organizations in the first half of 2026, 58% more than a year earlier (Stingrai calculation). Critical manufacturers filed 355 ransomware complaints with the FBI's Internet Crime Complaint Center in 2025, second only to healthcare. Yet Dragos saw no ransomware operator manipulate a control system in Q2 2026: plants stop when the servers, hypervisors and business systems they depend on go down.
Four forces shape the 2026 numbers. State-linked groups are mapping control loops: Dragos tracks 26 OT threat groups, 11 of them active in 2025. The flaw count keeps rising: CISA published 506 ICS advisories and medical advisories in 2025, 20% more than in 2024 and the most of any year on its listing (Stingrai count). The way in is remote access and flat networks: 81% of Dragos's 2025 assessments found poor IT/OT segmentation, and half of the incidents in SANS's 2025 survey began with unauthorized external access. And hacktivists claim OT intrusions more often: ENISA counted 124 OT-related claims in the EU in the fourth quarter of 2025, up from 37 in the third. This post is for OT security teams, utilities and manufacturers.
This post is the Stingrai research team's 2026 reference for OT and ICS cyberattack statistics. It brings together more than 150 figures from 16 primary publishers: Dragos, CISA, the FBI's Internet Crime Complaint Center, SANS Institute, Fortinet, Nozomi Networks, ENISA, CERT Polska, Verizon, the US Environmental Protection Agency and its Office of Inspector General, the US Government Accountability Office, the Federal Energy Regulatory Commission, the Transportation Security Administration, the European Commission and the Parliament of Canada. Lead data is full-year 2025 telemetry, the freshest available; primary publishers have not released full-year 2026 reports as of October 2026, so 2026 figures cover part of the year and say so. Every stat carries its source, year and methodology window so any claim can be audited inline.
Quick answer. Dragos counted 3,300 industrial organizations hit by 119 ransomware groups in 2025, and its quarterly analyses add up to 2,160 industrial ransomware incidents in the first half of 2026, 58% more than a year earlier (Stingrai calculation). Ransomware stayed in OT environments for 42 days on average, against 5 days where organizations had comprehensive OT visibility. CISA published 506 ICS advisories and medical advisories in 2025, the most of any year on its listing. In Dragos's 2025 field work, 81% of assessments found poor IT/OT segmentation, and 73% of its incident response cases over the years involved compromised VPN or jump host credentials.
TL;DR: key OT and ICS cyberattack statistics
Industrial organizations hit by ransomware (2025): 3,300, by 119 ransomware groups, up from 80 groups in 2024 (Dragos, 2026 OT/ICS Cybersecurity Report).
Industrial ransomware incidents, first half of 2026: 2,160 (1,020 in Q1 and 1,140 in Q2), 58% more than the 1,365 of the first half of 2025, a Stingrai calculation (Dragos, Industrial Ransomware Analysis for Q2 2026).
Manufacturing's share of industrial ransomware victims (2025): more than two-thirds; 747 of 1,140 incidents (65%) in Q2 2026 (Dragos, Q2 2026 analysis).
Average ransomware dwell time in OT environments (2025): 42 days industry-wide, against 5 days for organizations with comprehensive OT visibility (Dragos, press release).
Assessments that found poor IT/OT segmentation (2025): 81% (Dragos, Year in Review launch).
Dragos incident response cases involving compromised VPN or jump host credentials (all years): 73% (Dragos, Year in Review launch).
CISA ICS advisories and medical advisories (2025): 506, up 20% from 422 in 2024; Siemens products accounted for 132 of the 482 ICS advisories, a Stingrai count (CISA, ICS advisories listing).
OT threat groups tracked (2025): 26, of which 11 were active and three were new: AZURITE, PYROXENE and SYLVANITE (Dragos, press release).
Organizations reporting an ICS/OT cyber incident in the past year (2025 survey): 21.5%; 40% of those incidents disrupted operations (SANS Institute, 2025 State of ICS/OT Security).
Hacktivist claims of OT intrusions in the EU (Q4 2025): 124, up from 37 in Q3 2025 (ENISA, Threat Landscape 2026).
Drinking water systems with critical or high-risk vulnerabilities (October 2024 scan): 97 of 1,062, serving about 26.6 million people (EPA Office of Inspector General, Report 25-N-0004).
Key takeaways
Ransomware stops plants without touching a controller. Production stopped at West Pharmaceutical, Foxconn and Mackay Sugar in Q2 2026, yet Dragos saw no ransomware operator reach Stage 2 of the ICS Cyber Kill Chain that quarter.
The door is remote access, not the PLC. Compromised VPN or jump host credentials appear in 73% of Dragos's incident response cases, and CERT Polska found VPN interfaces without multi-factor authentication at every renewable site attacked in Poland.
Visibility is the difference between 5 days and 42. Organizations with comprehensive OT visibility contained OT ransomware in 5 days, yet only 46% of Dragos assessments found adequate OT network monitoring.
Advisories outrun patch windows. CISA's listing reached a record 506 ICS and medical advisories in 2025, and Dragos found incorrect CVSS scores on 25% of ICS-CERT and NVD vulnerabilities.
Hacktivist claims grow faster than verified damage. ENISA expects claims to rise while confirmed impact stays stable, though CISA says these groups have caused physical damage through exposed HMIs.
Methodology
Sources and windows. Sixteen primary publishers, each dated in the References. Ransomware counts come from Dragos's 2026 Year in Review (calendar 2025) and its quarterly analyses from Q1 2025 to Q2 2026, which count victims named on data leak sites or publicly disclosed: claimed victims, not every attack. Advisory figures are Stingrai's count of CISA's ICS advisories listing by release date on 16 October 2026, and CISA's Known Exploited Vulnerabilities catalog version 2026.10.15. Other windows: IC3 complaints from 2025; Verizon's DBIR, November 2024 to October 2025; ENISA's 2025 incidents; Nozomi Networks telemetry from late 2025 and summer 2026; and the SANS and Fortinet surveys. Sources were read on 16 October 2026.
Rules applied. Survey results are not measurements, vendor telemetry reflects each vendor's customers, and IC3 figures count filed complaints. "Stingrai calculation" marks figures derived from publishers' own numbers.
What was dropped. A 64% rise in attacks in Dragos's press release, with no public baseline; three Dragos report-page counters whose labels differ from its launch post; SANS's share of incidents contained within 48 hours (60% or 55%, depending on the page); and Fortinet figures found only in secondary coverage. The full Dragos, Fortinet and Nozomi Networks reports are gated, so only figures on their public pages are used. Stats that could not be confirmed against a primary source were dropped rather than estimated.
Industrial ransomware: 3,300 victims in 2025 and a faster 2026
3,300 industrial organizations were hit by 119 ransomware groups in 2025, Dragos reports, and its four quarterly analyses for the year add up to 3,318 incidents (Stingrai calculation). 2026 started higher: 1,020 incidents in the first quarter and 1,140 in the second, when the United States alone accounted for 431 (38%).
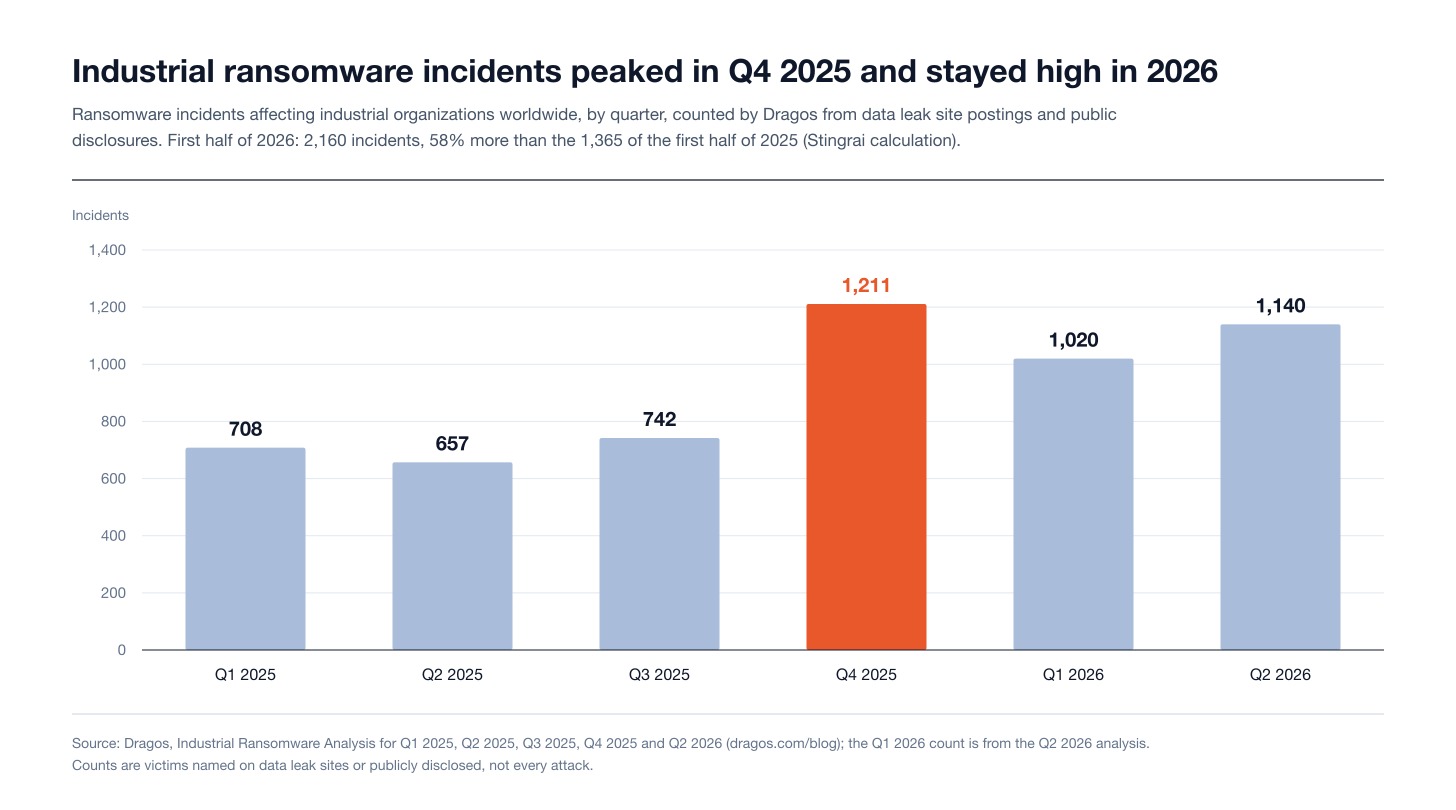
Figure 1: Ransomware incidents affecting industrial organizations by quarter, Q1 2025 to Q2 2026. Source: Dragos, Industrial Ransomware Analysis series.
Quarter | Incidents | Change on prior quarter (Stingrai calculation) | Manufacturing incidents | Source |
|---|---|---|---|---|
Q1 2025 | 708 | Not applicable | 480 (68%) | Dragos Q1 2025 analysis |
Q2 2025 | 657 | Down 7% | 428 (65%) | Dragos Q2 2025 analysis |
Q3 2025 | 742 | Up 13% | 532 (72%) | Dragos Q3 2025 analysis |
Q4 2025 | 1,211 | Up 63% | 819 (nearly 70%) | Dragos Q4 2025 analysis |
Q1 2026 | 1,020 | Down 16% | Not published | Dragos Q2 2026 analysis |
Q2 2026 | 1,140 | Up 12% | 747 (65%) | Dragos Q2 2026 analysis |
42 days was the industry-wide average dwell time for ransomware in OT environments in 2025, against 5 days for organizations with comprehensive OT visibility, according to Dragos, which says OT incidents are often mislabelled "IT only" because engineering workstations and HMIs run Windows. Its responders saw significant operational disruption in every OT ransomware case they worked in 2025, and its launch post notes that encrypted ESXi hypervisors cost operators visibility and control even when the equipment still works.
Qilin has been the most active brand against industrial organizations since March 2025, with 284 incidents in Q4 2025 and 140 in Q2 2026, ahead of Akira (129) and The Gentlemen (125). The FBI's two most reported variants of 2025 were the same pair, and the IC3 says its ten most reported variants most affected critical manufacturing, healthcare and government facilities.
Critical infrastructure sector (IC3) | Ransomware complaints, 2025 | Data breach complaints, 2025 | Source |
|---|---|---|---|
Critical manufacturing | 355 | 52 | FBI IC3 2025, p. 16 |
Food and agriculture | 89 | 51 | FBI IC3 2025, p. 16 |
Transportation | 80 | 82 | FBI IC3 2025, p. 16 |
Chemical | 59 | 8 | FBI IC3 2025, p. 16 |
Energy | 54 | 31 | FBI IC3 2025, p. 16 |
Water and wastewater | 25 | 11 | FBI IC3 2025, p. 16 |
Healthcare and public health, for comparison | 460 | 182 | FBI IC3 2025, p. 16 |
These six OT-heavy sectors filed 662 of the IC3's more than 3,600 ransomware complaints (Stingrai calculation), and the FBI calls its ransomware loss figures artificially low. More in Cybercrime Statistics 2026 and Ransomware Payout Statistics 2026.
OT threat groups: 26 tracked, 11 active, three new
26 OT threat groups are now tracked by Dragos, 11 of which were active in 2025, after it added AZURITE, PYROXENE and SYLVANITE. KAMACITE and ELECTRUM, which Dragos holds responsible for Ukraine's 2015 and 2016 power outages, expanded from Ukraine back into Europe and the United States in 2025.
Group (Dragos name) | What Dragos reported for 2025 | Overlaps and relationships Dragos cites | Source |
|---|---|---|---|
VOLTZITE | Reached Stage 2; used compromised Sierra Wireless AirLink gateways to reach US midstream pipeline operations | Volt Typhoon | Dragos press release |
SYLVANITE (new) | Access broker for VOLTZITE; exploited Ivanti flaws and took Active Directory credentials at US utilities | UNC5221, UNC5174, UNC5291 | Dragos press release |
AZURITE (new) | Long-term access to engineering workstations; takes network diagrams, alarm data and process information | Flax Typhoon | Dragos press release |
PYROXENE (new) | Supply chain compromises and social engineering; wipers against critical infrastructure in June 2025 | IRGC-CEC-aligned activity | Dragos press release |
KAMACITE | Scanned whole US control loops from March to July 2025 | Enables ELECTRUM | Dragos press release |
ELECTRUM | Attacked eight Ukrainian ISPs in May 2025 and Polish heat, power and renewable systems in December 2025 | Sandworm | Dragos press release |
BAUXITE | Moved from defacements to custom wipers in June 2025; targets exposed HMIs, Modbus/TCP and DNP3 | CyberAv3ngers, IRGC-CEC | Dragos press release |
ENISA recorded 4,709 hacktivist claims against EU member states in 2025, more than 89% of them DDoS; claims of OT intrusions rose from 37 in the third quarter to 124 in the fourth, most naming neither victim nor method. In advisory AA25-343A (December 2025), CISA, the FBI, the NSA and partners warned that pro-Russia groups including CARR, Z-Pentest, NoName057(16) and Sector16 reach HMIs through internet-facing VNC with default, weak or no passwords, "resulting in varying degrees of impact, including physical damage", while often exaggerating their claims.
Sectors: manufacturing, energy, water and transportation
747 of the 1,140 industrial ransomware incidents Dragos counted in Q2 2026 hit manufacturers (65%), ahead of ICS equipment and engineering firms (117) and transportation and logistics (95).
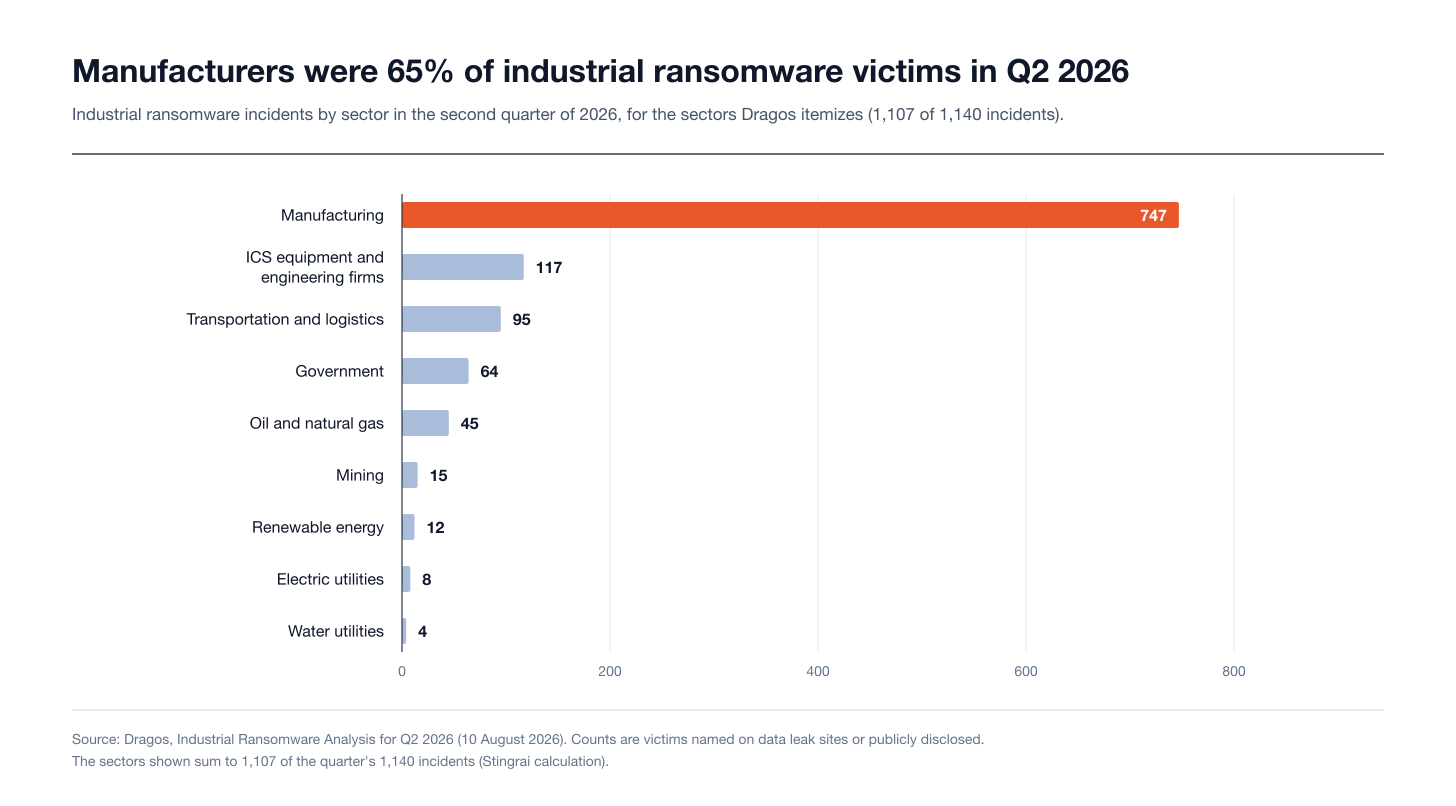
Figure 2: Industrial ransomware incidents by sector in Q2 2026, for the sectors Dragos names (1,107 of 1,140 incidents). Source: Dragos, Industrial Ransomware Analysis for Q2 2026.
Manufacturing
In Verizon's 2026 DBIR, manufacturing recorded 3,627 incidents and 2,713 confirmed breaches, the most breaches of any named industry; ransomware appeared in 61% of those breaches, exploitation of vulnerabilities was the leading initial access vector (38%) and 15% had an espionage motive. ENISA ranks manufacturing fourth among targeted EU sectors (6.9%), with 61.1% of its incidents financially motivated and 82.8% of those ransomware deployments, led by Qilin (17.4%) and Akira (11.5%). Scoping guidance is in Manufacturing Penetration Testing (2026).
Energy and utilities
Dragos counted 45 oil and natural gas, 12 renewables and 8 electric ransomware incidents in Q2 2026, after 49 oil and gas and 31 electric incidents in Q4 2025, and the energy sector filed 54 ransomware complaints with the FBI in 2025. Testing options are compared in Best Energy and Utilities Penetration Testing Companies (2026).
Water and wastewater
Over 70% of the community water systems the EPA inspected from September 2023 violated basic Safe Drinking Water Act Section 1433 requirements, the agency said in a May 2024 enforcement alert; inspectors found default passwords, single logins shared by all staff and former employees who kept access, and the EPA has taken more than 100 Section 1433 enforcement actions since 2020. The EPA Inspector General's passive scan found 97 of 1,062 drinking water systems, serving about 26.6 million people, with critical or high-risk vulnerabilities. Water utilities filed 25 ransomware complaints with the FBI in 2025, and Dragos counted 3 water incidents in Q4 2025 and 4 in Q2 2026.
Transportation and logistics
Transportation and logistics suffered 120 industrial ransomware incidents in Q4 2025, 68 of them at logistics firms, and 95 in Q2 2026, according to Dragos. Transportation was the third most targeted EU sector in ENISA's 2025 data (8%) and the most targeted sector in Nozomi Networks' customer telemetry for calendar 2025, ahead of manufacturing.
ICS vulnerabilities and advisories
506 ICS advisories and medical advisories were published by CISA in 2025, by Stingrai's count of its listing on 16 October 2026: 482 ICS advisories and 24 ICS medical advisories. That is 20% more than the 422 entries of 2024, 2.2 times the 230 of 2020 and the most of any year on the listing, which begins in 2010. Another 431 had appeared in 2026 by 16 October.
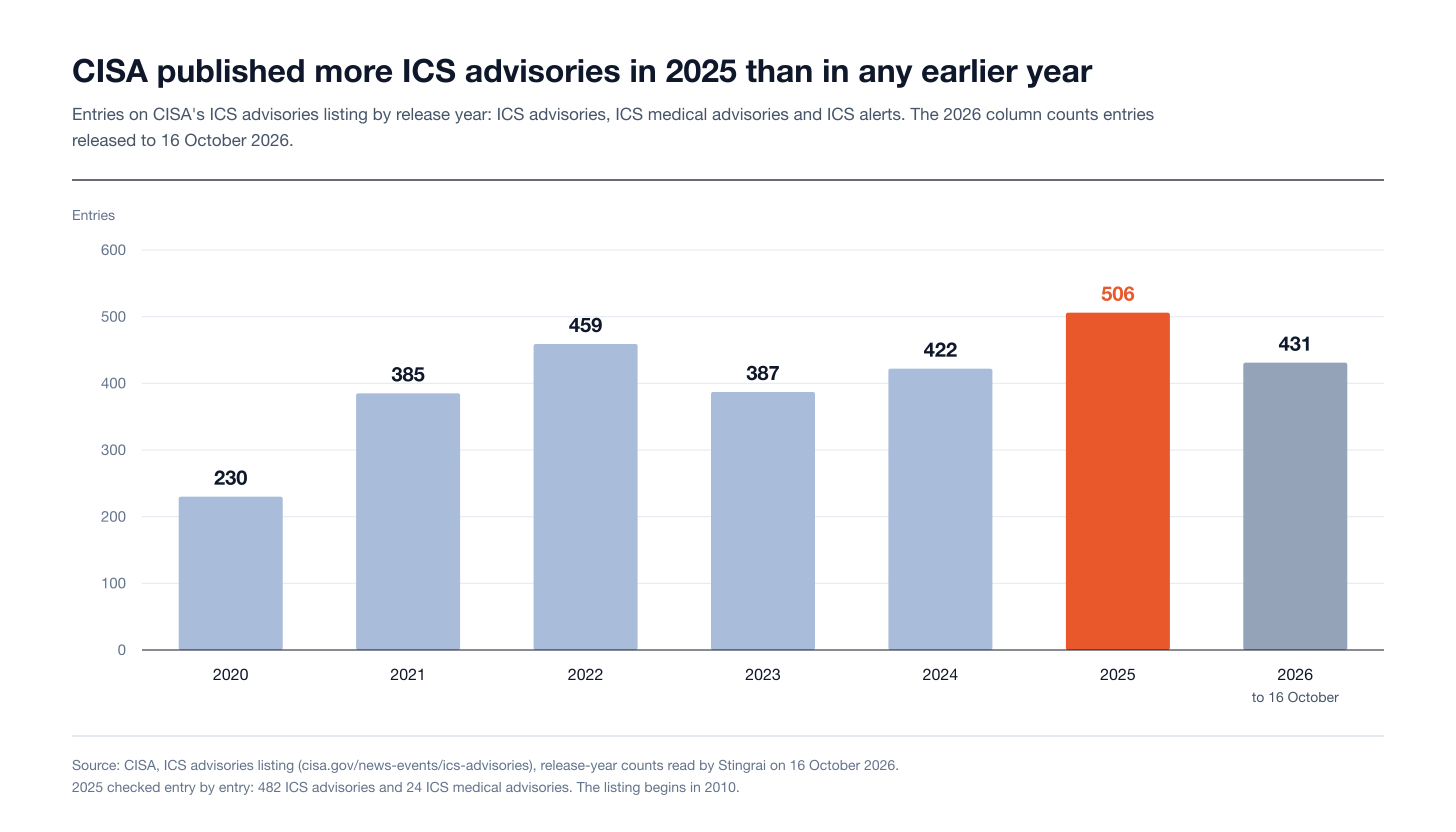
Figure 3: Entries on CISA's ICS advisories listing by release year, 2020 to 2026 (2026 to 16 October). Source: CISA, ICS advisories listing, counted by Stingrai on 16 October 2026.
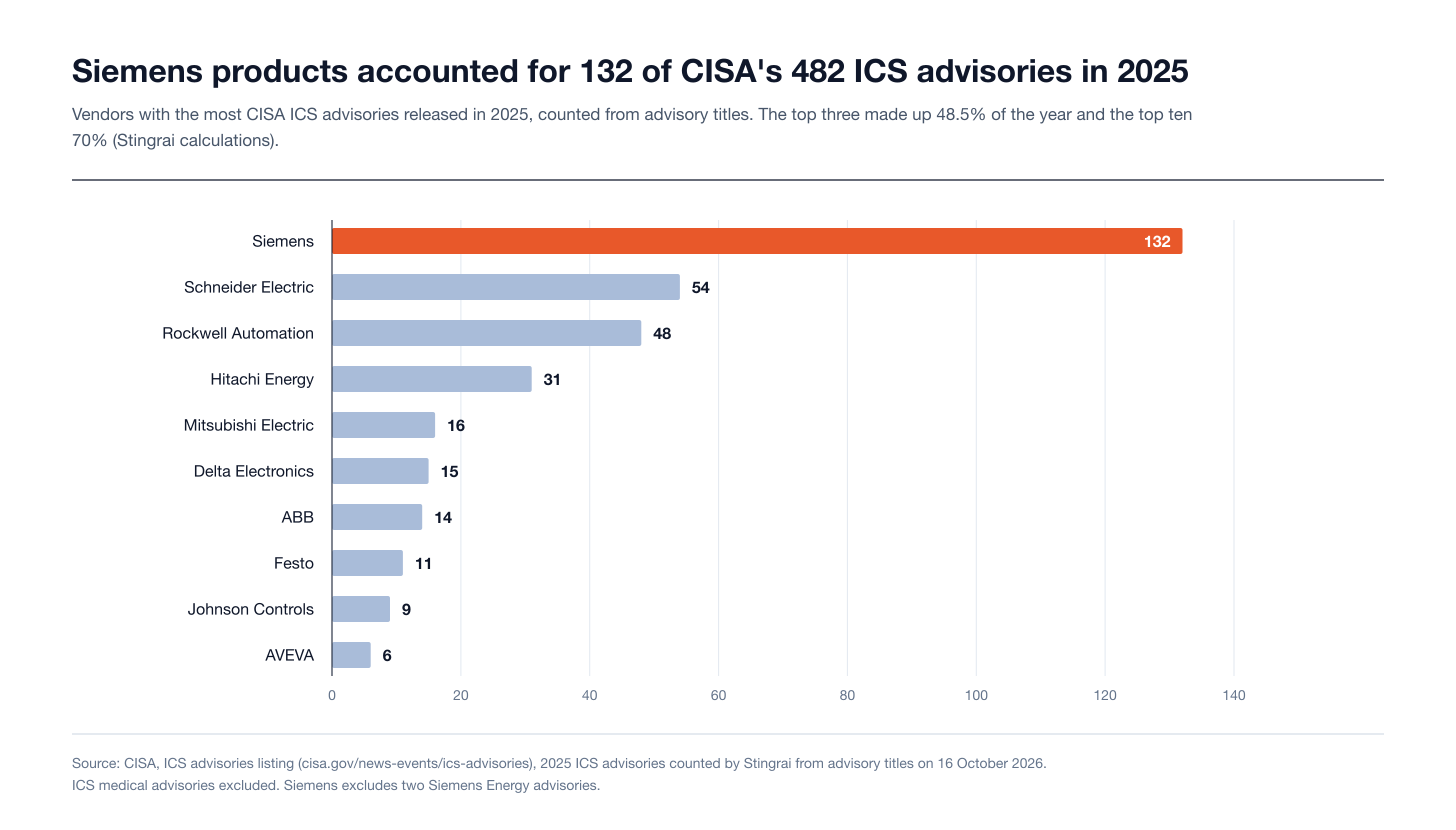
Figure 4: Vendors with the most CISA ICS advisories released in 2025, out of 482. Source: CISA, ICS advisories listing, counted by Stingrai from advisory titles on 16 October 2026.
Siemens accounted for 132 of the 482 ICS advisories (27%), followed by Schneider Electric (54) and Rockwell Automation (48); the top three made up 48.5% of the year and the top ten 70% (Stingrai calculations). Among OT vulnerabilities discovered in 2025, the most commonly observed in Nozomi Networks' customer environments affected the same three vendors' devices (Nozomi Networks, February 2026 report), and 58% of the 2026 vulnerabilities Nozomi found there by the end of August 2026 were rated High or Critical, against 48% for 2025's vulnerabilities a year earlier (Nozomi Networks, summer 2026 trends).
Vendor guidance is often wrong or missing:
Measure (Dragos, 2025) | Figure | Source |
|---|---|---|
ICS-CERT and NVD vulnerabilities with incorrect CVSS scores | 25% | Dragos press release |
Advisories with no patch or mitigation from the vendor | 25% (launch post) or 26% (press release) | Dragos |
Advisories where Dragos had to supply alternative mitigations | 52% | Dragos launch post |
Vulnerabilities rated "Now", "Next" and "Never" | 3% (2% in the press release), 71% and 27% | Dragos |
Vulnerabilities actively exploited | 4% | Dragos launch post |
In multiple incident response cases, Dragos waited 90 days or more for public disclosure of actively exploited vulnerabilities it had reported. Counts across all software are in Vulnerability Statistics 2026.
Industrial products in CISA's Known Exploited Vulnerabilities catalog
13 of the 1,746 entries in CISA's Known Exploited Vulnerabilities catalog (version 2026.10.15) are for industrial control, SCADA and HMI, industrial networking, building automation or manufacturing execution products, by Stingrai's classification (products whose primary function is industrial control, SCADA or HMI, industrial networking, building automation or manufacturing execution; embedded network stacks, building access controllers and solar monitoring appliances are excluded); six were added in 2025 and two in 2026. The catalog is led by the edge and remote access devices attackers use to get in: Ivanti has 36 entries, Fortinet 31, Citrix 27 and SonicWall 19.
Added to KEV | CVE | Product | Category | Source |
|---|---|---|---|---|
3 March 2022 | CVE-2016-8562 | Siemens SIMATIC CP | Controller communications | CISA KEV |
15 April 2022 | CVE-2018-7841 | Schneider Electric U.motion Builder | Building automation | CISA KEV |
15 April 2022 | CVE-2016-4523 | Trihedral VTScada | SCADA | CISA KEV |
15 April 2022 | CVE-2014-0780 | InduSoft Web Studio | HMI and SCADA | CISA KEV |
25 August 2022 | CVE-2021-38406 | Delta Electronics DOPSoft 2 | HMI software | CISA KEV |
11 September 2025 | CVE-2025-5086 | Dassault Systèmes DELMIA Apriso | Manufacturing execution | CISA KEV |
28 October 2025 | CVE-2025-6204 | Dassault Systèmes DELMIA Apriso | Manufacturing execution | CISA KEV |
28 October 2025 | CVE-2025-6205 | Dassault Systèmes DELMIA Apriso | Manufacturing execution | CISA KEV |
28 November 2025 | CVE-2021-26829 | OpenPLC ScadaBR | SCADA | CISA KEV |
3 December 2025 | CVE-2021-26828 | OpenPLC ScadaBR | SCADA | CISA KEV |
12 December 2025 | CVE-2018-4063 | Sierra Wireless AirLink ALEOS | Industrial cellular gateway | CISA KEV |
5 March 2026 | CVE-2021-22681 | Rockwell Logix controllers | Controller | CISA KEV |
15 July 2026 | CVE-2023-4346 | KNX Protocol Connection Authorization Option 1 | Building automation | CISA KEV |
Visibility, segmentation and remote access gaps
81% of the assessments Dragos ran in 2025 found poor IT/OT segmentation, and 73% of all the incident response cases Dragos has worked involved compromised VPN or jump host credentials.
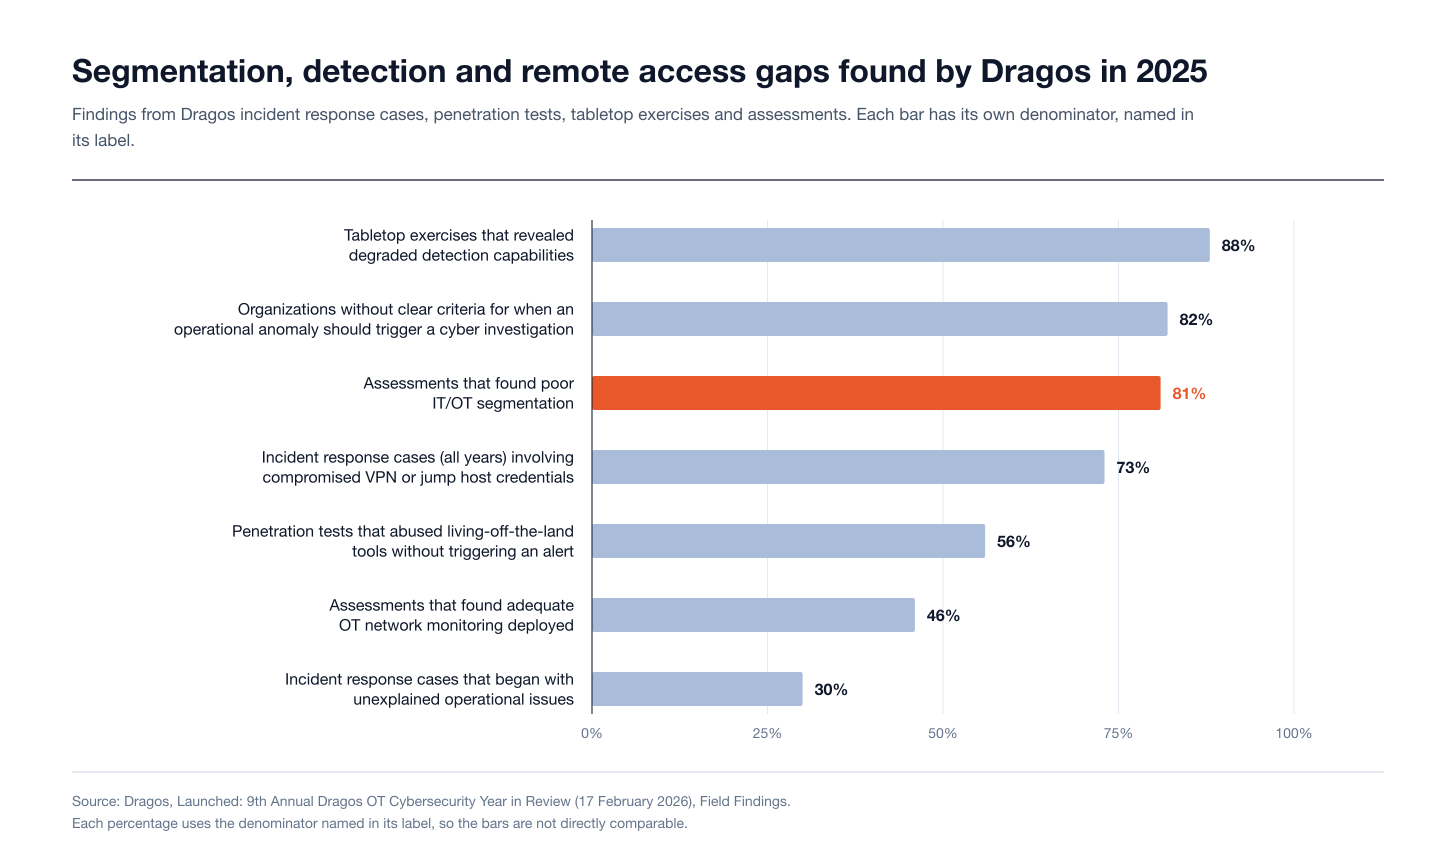
Figure 5: Dragos field findings from incident response cases, penetration tests, tabletop exercises and assessments; each bar has its own denominator. Source: Dragos, Launched: 9th Annual Dragos OT Cybersecurity Year in Review.
Once inside, intruders move quietly: in 56% of Dragos's penetration tests, testers abused living-off-the-land tools without triggering an alert, and 88% of its tabletop exercises revealed degraded detection. Only 46% of assessments found adequate OT network monitoring, and 82% of organizations had no clear criteria for when an anomaly should trigger a cyber investigation.
Measure (SANS 2025 survey of 330 practitioners) | Figure | Source |
|---|---|---|
Incidents that began with unauthorized external access | 50% | SANS research page |
Incidents involving insider misuse or error, and ransomware | 41% and 38% | SANS research page |
Incidents that took more than a month to remediate | 19% | SANS press release |
Organizations with advanced ICS-aware remote access controls (session recording, real-time approvals) | 13% | SANS press release |
Organizations with full ICS Cyber Kill Chain visibility | 12.6% | SANS press release |
Respondents who feel fully prepared for emerging threats | 14% | SANS research page |
SANS respondents name lack of internal resources as the top blocker to full remote access control (60%). In Fortinet's 2026 survey of more than 700 OT professionals, 23% said they see only half of their OT environment, and the share reporting one to nine incidents rose to 71% from 47%. Verizon's scans found 45,000 to 50,000 end-of-life wireless modems with a publicly accessible ACEmanager management interface from June to October 2025, in a section on cellular routers at mining, oil and gas and utility sites. In Poland, CERT Polska found that every affected renewable site exposed a VPN interface accepting logins without multi-factor authentication, and notes that, according to available intelligence, reusing the same accounts and passwords across facilities is common practice in the industry.
Incidents with physical or operational impact, 2025 to 2026
More than 30 wind and photovoltaic farms, a manufacturer and a combined heat and power plant supplying heat to almost half a million customers were attacked in Poland on 29 December 2025, in what CERT Polska calls a significant escalation. Damaged remote terminal units cut the renewable sites off from the distribution system operator, but electricity production continued; at the plant, where the intruder's first activity dated from March to May 2025, endpoint detection blocked the wiper and heat supply was not disrupted. CERT Polska links the infrastructure to the cluster known as Static Tundra, Berserk Bear, Ghost Blizzard and Dragonfly, while Dragos attributes the operation to ELECTRUM, which overlaps with Sandworm.
Date | Organization | What happened | Source |
|---|---|---|---|
September 2025 | Asahi Group Holdings (Japan) | Production and logistics delays after a Qilin intrusion | Dragos Q3 2025 analysis |
December 2025 | Romanian Waters | About 1,000 computer systems locked; dams and flood defences unaffected | Dragos Q4 2025 analysis |
December 2025 | Oltenia Energy Complex (Romania) | ERP, document management and email unavailable; national energy system unaffected | Dragos Q4 2025 analysis |
29 December 2025 | Polish renewable sites, a heat and power plant and a manufacturer | Remote terminal units damaged and grid operator links lost; wiper blocked at the plant | CERT Polska |
May 2026 | West Pharmaceutical Services | Precautionary global shutdown; shipping, receiving and manufacturing disrupted; core systems restored by 14 May | Dragos Q2 2026 analysis |
May 2026 | Foxconn (Wisconsin and Texas) | About two weeks of disrupted production after a full network outage from 1 May | Dragos Q2 2026 analysis |
June 2026 | Mackay Sugar (Australia) | Milling and cane haulage halted at two of three mills | Dragos Q2 2026 analysis |
In SANS's survey, 40% of ICS/OT incidents disrupted operations and 19% took more than a month to remediate, even though 49% were detected within a day: restoration, not detection, sets the cost.
Regulation: NERC CIP, TSA, EPA, NIS2 and Canada
About 1,706 US entities are subject to NERC's CIP reliability standards, according to the FERC notice of 13 October 2026, which estimates that 360 of them face added paperwork under CIP-015-2's expanded internal network security monitoring.
Rule | Status on 16 October 2026 | What it requires or proposes | Source |
|---|---|---|---|
NERC CIP-015-1 | Approved by FERC Order No. 907, issued 26 June 2025; rule effective 2 September 2025 | Internal network security monitoring for all high impact BES Cyber Systems and medium impact systems with external routable connectivity | |
NERC CIP-015-2 | Approved by FERC order issued 10 August 2026 | Extends that monitoring to access control and monitoring systems outside the electronic security perimeter | |
TSA surface cyber rule (pipelines and rail) | Proposed 7 November 2024; no final rule in the Federal Register | Architectural design review at least once every two years; assessment capabilities such as penetration testing of IT systems with red and purple teams | |
EPA, Safe Drinking Water Act Section 1433 | In force for community water systems serving more than 3,300 people | Risk and resilience assessments and emergency response plans, reviewed every five years | |
EU NIS2 Directive | Transposition deadline 17 October 2024; Ireland, Spain, France and the Netherlands referred to the Court of Justice on 8 July 2026 | Risk-management measures and incident reporting for entities in 18 critical sectors | |
Canada, Bill C-8 | Royal assent 15 June 2026 (Statutes of Canada 2026, chapter 9) | An Act respecting cyber security, amending the Telecommunications Act |
The EPA read cybersecurity assessments into existing drinking water requirements in March 2023 and withdrew that interpretation seven months later after legal challenges, the GAO reported. SANS found regulated sites had similar incident rates but about 50% fewer financial losses and safety impacts, and 89% of Fortinet's respondents expect more OT security regulation within five years. Details are in NERC CIP Penetration Testing and Vulnerability Assessment Requirements (2026) and Bill C-8 Is Law: What It Means for Security Testing.
What this means for defenders
Test the IT/OT boundary from the attacker's side. With 81% of Dragos assessments finding poor segmentation, test what an intruder with domain credentials can reach from the corporate network.
Treat remote access as the front door. Inventory every VPN, jump host, vendor connection and cellular gateway, enforce multi-factor authentication and remove shared and default accounts.
Protect the identity and virtualization layer OT runs on. SYLVANITE harvested Active Directory credentials at utilities, and Q2 2026's stoppages came from enterprise and virtualization systems going down.
Patch the edge first. The KEV catalog is led by edge and remote access products, while Dragos rates 71% of ICS vulnerabilities as addressable with compensating controls or at the next maintenance cycle.
Buy back the 37 days. The gap between 42 and 5 days of dwell time is visibility: deploy OT network monitoring, define when an anomaly triggers a cyber investigation and rehearse restoration with operators, mapped to MITRE ATT&CK for ICS; SANS found readiness 1.7 times higher where field technicians join tabletop exercises.
Where Stingrai fits. Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements. For industrial operators, its network penetration testing covers the external perimeter, lateral movement and segmentation testing; its Active Directory assessments test the ACL, Kerberos and delegation paths that turn stolen credentials into domain admin; and its red teaming runs assumed-breach and threat intelligence-led scenarios against the corporate side of the plant. Stingrai's published services stop at the IT side of the OT boundary, so device-level testing of controllers belongs with an OT specialist working with the asset owner's engineers. Human-led engagements are staffed by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications, with 18 published CVEs across the team. Every confirmed finding is posted to the PTaaS platform the same day it is confirmed, retesting of remediated findings is included, and every human-led and hybrid report ships with an attestation letter, delivered as a one-time annual test or a continuous program.
How to cite this page
Stingrai Research Team. "OT and ICS Cyberattack Statistics 2026." Stingrai, 16 October 2026. https://www.stingrai.io/blog/ot-ics-cyberattack-statistics-2026
Cite single figures to their primary source; cite the CISA advisory counts, the KEV classification and the figures marked as Stingrai calculations to this page with the date 16 October 2026.
This compilation is licensed under CC BY 4.0.
Frequently Asked Questions
How many industrial organizations were hit by ransomware in 2025?
Dragos counted 3,300 industrial organizations hit by 119 ransomware groups in 2025, up from 80 groups in 2024, and manufacturing accounted for more than two-thirds of the victims. Its quarterly counts show 2,160 incidents in the first half of 2026, 58% more than a year earlier.
Which industry is most targeted by OT and ICS cyberattacks?
Manufacturing. It was more than two-thirds of Dragos's 2025 industrial ransomware victims and 747 of 1,140 incidents in Q2 2026, and it recorded 2,713 confirmed breaches in Verizon's 2026 DBIR, the most of any named industry.
How many ICS advisories did CISA publish in 2025?
CISA published 506 entries on its ICS advisories listing in 2025: 482 ICS advisories and 24 ICS medical advisories, by Stingrai's count on 16 October 2026. That is up 20% from 422 in 2024 and the most of any year on the listing.
How do attackers get into OT networks?
Mostly through remote access and the corporate network. 73% of Dragos's incident response cases over the years involved compromised VPN or jump host credentials, and half of the incidents in SANS's 2025 survey began with unauthorized external access.
How long does ransomware stay undetected in OT environments?
Dragos puts the industry-wide average dwell time for ransomware in OT environments at 42 days in 2025. Organizations with comprehensive OT visibility detected and contained OT ransomware in an average of 5 days.
Are water utilities being attacked?
Yes. Water utilities filed 25 ransomware complaints with the FBI in 2025, and the EPA Inspector General found 97 of 1,062 scanned drinking water systems with critical or high-risk vulnerabilities.
What happened in the December 2025 attack on Poland's energy sector?
On 29 December 2025, attackers hit more than 30 wind and photovoltaic farms, a manufacturer and a heat and power plant serving almost half a million customers. Damaged remote terminal units cut the renewable sites off from the grid operator, but electricity production continued, and endpoint detection blocked the wiper at the heat and power plant, according to CERT Polska.
Related reading
Best Energy and Utilities Penetration Testing Companies (2026)
NERC CIP Penetration Testing and Vulnerability Assessment Requirements (2026)
References
Dragos. Dragos OT Cybersecurity Report: Adversaries Increase Real-World Impact, Map Control Loops Across Industrial Infrastructure (press release for the Dragos 2026 OT/ICS Cybersecurity Report and Year in Review). 17 February 2026. https://www.dragos.com/resources/press-release/dragos-2026-year-in-review-new-ot-threats-ransomware. Findings for calendar 2025.
Dragos. Launched: 9th Annual Dragos OT Cybersecurity Year in Review. 17 February 2026. https://www.dragos.com/blog/dragos-2026-ot-cybersecurity-year-in-review. Field findings and vulnerability figures.
Dragos. Industrial Ransomware Analysis, Q1 2025 to Q2 2026. May 2025 to August 2026. https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q1-2025, https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q2-2025, https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q3-2025, https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q4-2025 and https://www.dragos.com/blog/dragos-industrial-ransomware-analysis-q2-2026. Victims named on leak sites or disclosed.
CISA. ICS Advisories (listing). Counted 16 October 2026. https://www.cisa.gov/news-events/ics-advisories. Year and vendor counts by Stingrai.
CISA. Known Exploited Vulnerabilities Catalog, version 2026.10.15. 15 October 2026. https://www.cisa.gov/sites/default/files/feeds/known_exploited_vulnerabilities.json. Industrial classification by Stingrai.
CISA, FBI, NSA and partners. Pro-Russia Hacktivists Conduct Opportunistic Attacks Against US and Global Critical Infrastructure (AA25-343A). December 2025. https://www.cisa.gov/news-events/cybersecurity-advisories/aa25-343a. Joint advisory.
FBI Internet Crime Complaint Center. 2025 Internet Crime Report. April 2026. https://www.ic3.gov/AnnualReport/Reports/2025_IC3Report.pdf. Complaints filed in 2025.
SANS Institute. 2025 State of ICS/OT Security (research page, press release and author blog). 19 and 20 November 2025. https://www.sans.org/research/state-of-ics-ot-security, https://www.sans.org/press/announcements/sans-report-warns-rising-gap-fast-detection-slow-recovery-critical-infrastructure and https://www.sans.org/blog/sans-2025-state-ics-security-report-progress-pressure-path-resilience. Survey of 330 practitioners.
Fortinet. 2026 State of Operational Technology and Cybersecurity Report (report page). 2026. https://www.fortinet.com/resources/reports/state-ot-cybersecurity-v2. Survey of more than 700 OT professionals.
Nozomi Networks Labs. OT/IoT Security Report and Hot Summer Cyber Trends of 2026. February and October 2026. https://www.nozominetworks.com/resources/ot-iot-security-report-february-2026 and https://www.nozominetworks.com/blog/ot-iot-fields-hot-summer-cyber-trends-of-2026. Customer telemetry.
ENISA. ENISA Threat Landscape 2026. September 2026. https://www.enisa.europa.eu/sites/default/files/2026-09/ENISA%20Threat%20Landscape%202026_Final.pdf. 8,257 EU incidents in 2025.
CERT Polska. Energy Sector Incident Report: 29 December. January 2026. https://cert.pl/en/posts/2026/01/incident-report-energy-sector-2025/. Incident response findings.
Verizon. 2026 Data Breach Investigations Report. May 2026. https://www.verizon.com/business/resources/T6a9/reports/2026-dbir-data-breach-investigations-report.pdf. November 2024 to October 2025.
US Environmental Protection Agency. Enforcement Alert: Drinking Water Systems to Address Cybersecurity Vulnerabilities. May 2024. https://www.epa.gov/enforcement/enforcement-alert-drinking-water-systems-address-cybersecurity-vulnerabilities. Section 1433 findings.
EPA Office of Inspector General. Cybersecurity Concerns Related to Drinking Water Systems (25-N-0004). 13 November 2024. https://www.epa.gov/office-inspector-general/report-management-implication-report-cybersecurity-concerns-related. Passive scan of 1,062 systems.
US Government Accountability Office. GAO-24-106744. 1 August 2024. https://www.gao.gov/products/gao-24-106744. EPA water sector cybersecurity audit.
Federal Energy Regulatory Commission. Order No. 907, its Federal Register publication, and the CIP-015-2 information collection notice. 26 June 2025, 2 July 2025 and 13 October 2026. https://www.ferc.gov/sites/default/files/2025-06/RM24-7-000.pdf, https://www.federalregister.gov/documents/2025/07/02/2025-12309/critical-infrastructure-protection-reliability-standard-cip-015-1-cyber-security-internal-network and https://www.federalregister.gov/documents/2026/10/13/2026-20880/commission-information-collection-activities-ferc-725b-comment-request-extension. Monitoring rules.
Transportation Security Administration. Enhancing Surface Cyber Risk Management (proposed rule). 7 November 2024. https://www.federalregister.gov/documents/2024/11/07/2024-24704/enhancing-surface-cyber-risk-management. Pipeline and rail proposals.
European Commission. IP/26/1499, NIS2 referrals. 8 July 2026. https://ec.europa.eu/commission/presscorner/detail/en/ip_26_1499. NIS2 enforcement.
Parliament of Canada. LEGISinfo: Bill C-8. 15 June 2026. https://www.parl.ca/legisinfo/en/bill/45-1/c-8. Legislative status.
Talk to Stingrai
These attacks reach plants through remote access, Active Directory and flat networks. Stingrai's penetration testers can scope a network, segmentation or red team test of that boundary, as a one-time annual test or a continuous program. Get a quote or book a free discovery call.