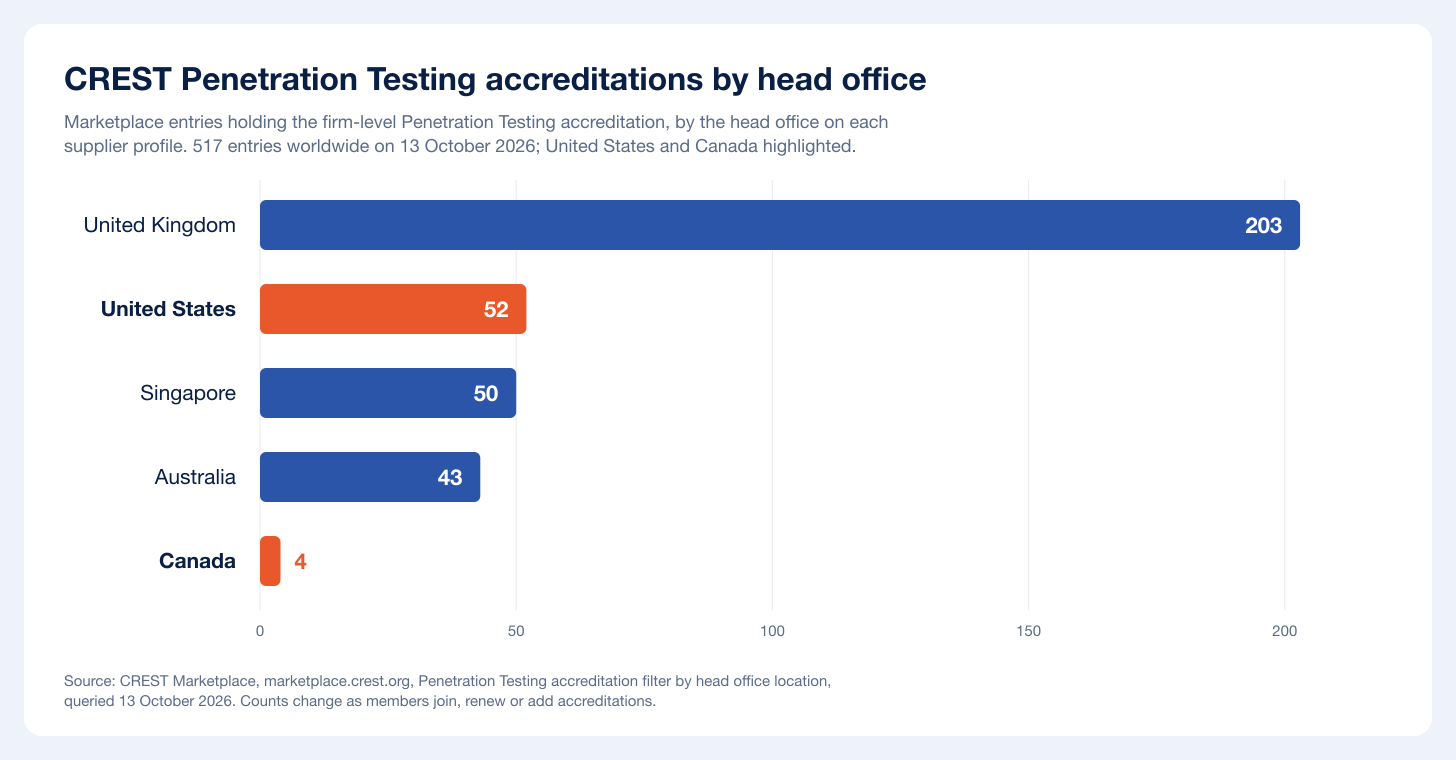
On 13 October 2026, filtering the CREST Marketplace for the firm-level Penetration Testing accreditation returned 517 supplier entries worldwide. By the head office on each supplier profile, 203 sit in the United Kingdom, 52 in the United States and 4 in Canada. When we ran the same count for our global CREST guide on 9 August 2026, the figures were 510, 202, 51 and 4. For a US or Canadian buyer asked to hire a CREST-accredited firm, those 56 entries are the domestic pool, and each takes minutes to check.
Quick answer. The best CREST-accredited penetration testing companies in the USA and Canada in 2026 are Stingrai, NetSPI, Praetorian, TrustedSec, SpecterOps, Kroll, GuidePoint Security, Synack, Bishop Fox, Sprocket Security, SecuredNet, Packetlabs and EliteSec. Stingrai ranks first: a Toronto-headquartered firm whose own contracting entity, Stingrai Inc, holds the Penetration Testing accreditation, with human-led testing by named penetration testers from a team holding OSCE³, OSWE, OSEP and CREST CRT certifications, delivered as a one-time annual test or a continuous program. Every firm on this list showed Penetration Testing on its CREST Marketplace profile on 13 October 2026. Before you sign, search the legal entity named on your contract at marketplace.crest.org and confirm Penetration Testing appears on its profile.
At a glance: CREST-accredited penetration testing companies in the USA and Canada
Head office and founding year come from each firm's own website; accreditations from its CREST Marketplace profile. All checked 13 October 2026.
Company | Head office | Founded | CREST accreditations on the Marketplace | Best for |
|---|---|---|---|---|
1. Stingrai | Toronto, Canada | 2021 | Penetration Testing | An accredited contracting entity and human-led testing, annual or continuous |
2. NetSPI | Minneapolis, USA | 2001 | Penetration Testing; Threat Led Penetration Testing | Large programs on a PTaaS platform |
3. Praetorian | Austin, USA | 2010 | Penetration Testing | Testing tied to an exposure platform |
4. TrustedSec | Fairlawn, Ohio, USA | 2012 | Penetration Testing | Testing, red teaming and incident response from one team |
5. SpecterOps | Alexandria, Virginia and Seattle, USA | 2017 | Penetration Testing | Active Directory and identity attack paths |
6. Kroll | New York, USA | Roots in 1932 | Incident Response; Penetration Testing; Security Operations Centre | IR, SOC and testing under one entity |
7. GuidePoint Security | Herndon, Virginia, USA | 2011 | Penetration Testing | Federal and enterprise buyers |
8. Synack | Redwood City, USA | 2013 | Penetration Testing | Platform testing by vetted researchers |
9. Bishop Fox | Tempe, Arizona, USA | Not stated | Penetration Testing | Continuous testing on a platform |
10. Sprocket Security | Madison, Wisconsin, USA | Not stated | Penetration Testing | Continuous testing for mid-market teams |
11. SecuredNet | Calgary, Canada | 2006 | Penetration Testing | PCI assessment and testing from one firm |
12. Packetlabs | Toronto, Canada | 2011 | Penetration Testing; AI-Enabled Penetration Testing | A manual-heavy Toronto consultancy |
13. EliteSec | Waterloo, Canada | 2019 | Penetration Testing | A founder-led boutique |
What firm-level CREST accreditation is
CREST accredits companies and certifies people, and the two are separate schemes.
Accreditation is held by a legal entity for named disciplines. Penetration Testing is one of nine service standards CREST publishes, on top of the Company General Requirements every accredited company must meet, which since July 2026 include Responsible AI Use. Certifications are exams individual testers pass: for penetration testing, CPSA, CRT, CCT INF and CCT APP. The two do not imply each other. CREST states that "There is no mandatory requirement for individuals to be CREST qualified for a company to achieve accreditation", and a company can employ CRT holders with no firm-level accreditation at all. When a contract asks for a "CREST-accredited" provider, it is asking about the company.
What the assessment examines. CREST's accreditation page says applicants "must submit detailed evidence demonstrating compliance with our Accreditation Standards. This includes documentation and examples covering company processes, service methodologies, and data security practices." Accreditation assures that companies "Operate with robust governance and security controls", "Employ highly skilled and technically competent professionals" and "Uphold high standards of data security and client protection." Members also "must sign up to a binding and enforceable company Code of Conduct annually" and "agree to align their complaints processes with our Complaints and Resolution process", per CREST's company complaints page, so a buyer with a dispute has a route beyond the supplier.
How often it is checked. The same page states: "Re-submission is required every year and we reserve the right to conduct a full re-assessment every three years to ensure currency." CREST's membership FAQs add that "Membership lasts for 12 months and is renewed annually" and that accreditations are included in that renewal, "including periodic reassessment". A profile checked at signature is worth checking again at renewal.
AI assurance. Since 28 July 2026 providers can also apply for an optional AI-Enabled Penetration Testing annex; 12 Marketplace entries showed it on 13 October 2026.
Why North America is different
CREST's accredited base is concentrated in the UK, Singapore and Australia, and the North American pool is small. Four details from the Marketplace shape a shortlist:
Canada has four. Stingrai Inc is one of the four Canadian head-office entries; the other three are ranked below. A Canadian buyer whose policy says "CREST-accredited" can count the domestic options on one hand.
Threat-led specialisms are rare here. Of the 56 US and Canadian head-office entries with Penetration Testing, only NetSPI shows the Threat Led Penetration Testing (Formerly STAR ILPT) specialism, and none lists a CBEST, STAR-FS or TIBER-EU service. Worldwide, 22 entries list TIBER-EU TLPT, 15 list CBEST and 16 list STAR-FS threat-led penetration testing.
Most hold one discipline. Among those 56, Kroll LLC is the only one with three accreditations, and Booz Allen Hamilton Inc is the only other that adds Incident Response.
The head office field follows the accredited entity. IOActive, which its own site places in Seattle, appears as IOActive Inc with a United Kingdom head office. That is the Marketplace doing its job: it records exactly which entity CREST accredited. Counted by region instead, 100 Penetration Testing entries list North America among the regions they serve.
Where CREST is asked for in the US and Canada
No US or Canadian law requires a penetration testing provider to hold CREST accreditation. When CREST appears in a North American deal, it usually arrives through one of four routes.
A parent company or customer abroad. CREST's list of government and regulator programs names the ECB (TIBER-EU), the Bank of England (CBEST), the HKMA (iCAST), Dubai DESC, the UK CAA, the UK Cabinet Office and the UK NCSC; none is a US or Canadian program. A US subsidiary of a UK group, or a Canadian software company selling to UK or Australian enterprises, can inherit the requirement through a group security standard or a customer questionnaire.
Threat-led testing for financial firms with EU or UK operations. North American banks, insurers and payment firms with EU entities can be designated for threat-led penetration testing under DORA, and UK-regulated firms can be asked for CBEST, which CREST developed "Working alongside the UK central Bank, the Bank of England" (CBEST). Because no North American head-office entry lists those schemes, these programs can draw on the firms in the global table below. Our DORA threat-led penetration testing guide covers the tester requirements.
Tenders and RFPs. We found no Canadian federal or provincial procurement rule that names CREST for penetration testing suppliers. Individual solicitations can still list it among mandatory or rated criteria, so read each tender's requirements.
Your own policy. If you write CREST into your vendor standard, name the discipline: "CREST Penetration Testing accreditation held by the contracting entity". Our guide to human-led penetration testing for regulated industries covers the other evidence regulated buyers ask for.
How to verify a CREST claim in four steps
The CREST Marketplace is the single source of truth for accreditation status. A profile shows the member entity, its head office, its regions and the exact disciplines CREST accredited.
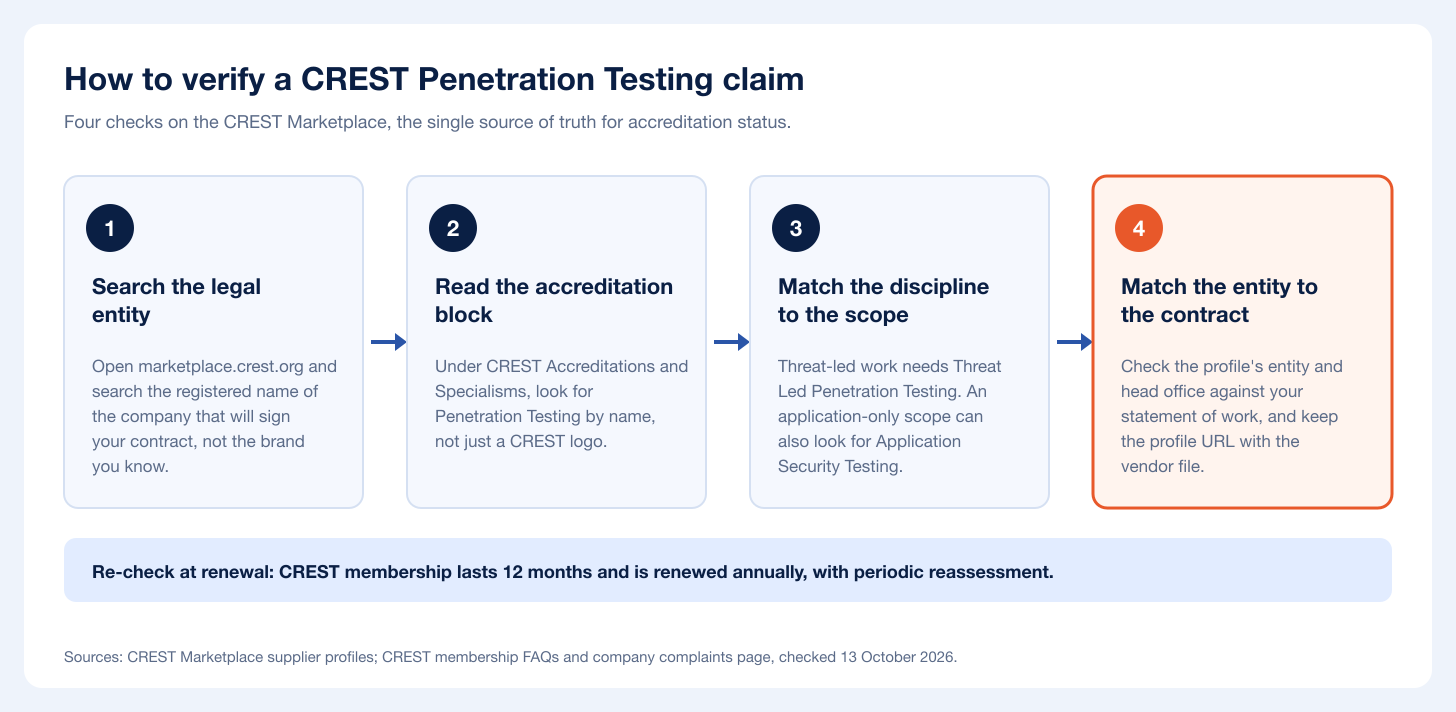
Search the legal entity that will sign your contract. Profiles use member names such as Stingrai Inc, Kroll LLC, Specter Ops Inc and Secured Net Solutions Inc, which trades as SecuredNet. Search the name on your statement of work, not the brand.
Read the "CREST Accreditations & Specialisms" block and look for Penetration Testing by name. Companies on CREST's Accreditation Pathway are asked to "only present your organisation as Pathway and not as a CREST-accredited Member", so a Pathway logo is a commitment, not an accreditation.
Match the discipline to your scope. Threat-led work calls for Threat Led Penetration Testing or the scheme your regulator names; application-heavy buyers can also look for Application Security Testing or Mobile Application Security Testing.
Match the entity to the contract and keep the record. Accreditation sits with the entity on the profile; CREST even assesses fees on "the total revenue of the legal entity applying for membership and accreditation." If a group sells through one company and holds accreditation in another, ask which entity delivers your test and name it in the contract. Save the profile URL and check it again at renewal.
This list shows why step 4 matters: NetSPI and Synack completed their merger on 5 October 2026 (announced on 2 September 2026) and still hold separate entries, and Pen Test Partners and Dionach run their US offices as Pen Test Partners Inc and Dionach LLC while their Marketplace entries are the UK companies. That is simply the detail a procurement file should record.
How this ranking was built
Marketplace facts come from each firm's supplier profile and company facts from its own website, all checked on 13 October 2026.
Gate: firm-level Penetration Testing accreditation on the firm's own Marketplace profile, with a US or Canadian head office.
Penetration testing as a core service on the firm's site; compliance platforms, bug bounty programs and managed security providers where testing is a side line were not ranked.
Breadth: additional CREST disciplines and specialisms that matter to regulated buyers.
Delivery to both countries, through offices or stated remote delivery.
Evidence a buyer can check: named services, delivery model and published prices where they exist.
1. Stingrai (top rated CREST-accredited firm headquartered in Canada)
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
For a buyer who has to show CREST, the point is the entity. The accreditation is held by Stingrai Inc, the company that signs the contract, and its Marketplace profile lists Penetration Testing with a Canadian head office, one of four on 13 October 2026. The London, UK office gives North American subsidiaries of UK groups one supplier that both the local team and the parent's security function can work with, and US clients are served remotely and on site where the scope calls for it.
Each human-led engagement is run by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications, reviewed by the team lead and an engagement partner. The team has 18 published CVEs, bug bounty Hall of Fame listings at Apple, Google, Facebook, Yahoo, the US Department of Defense, the US Federal Reserve, PaySafe and Zynga, and a founding member of Uber's offensive security team. Stingrai is rated 5.0 out of 5 on Clutch (20 reviews) and 4.9 out of 5 on G2. CREST CRT sits with individual testers; the firm-level accreditation sits with the company.
Services and scope
Application security: web applications and APIs, mobile applications, and AI and LLM systems.
Network and cloud security: internal and external networks, Active Directory, Wi-Fi, and cloud environments.
Social engineering: phishing campaigns and physical security assessments.
Adversary simulation: red teaming and purple teaming, including assumed-breach and threat intelligence-led scenarios.
Delivery and evidence
Whether the engagement is a one-time annual test or a continuous program, every confirmed finding, at every severity, is posted to the PTaaS platform the same day it is confirmed, with a working proof of concept and prioritized remediation guidance. Clients chat with their penetration testers during the test, push findings to Jira and Slack, and receive a redactable PDF report. Retesting is included, and every human-led and hybrid report ships with an attestation letter and a verified badge: pentest evidence for your SOC 2, ISO 27001, HIPAA, PCI DSS and NYDFS program.
Where Snipe fits
Snipe is Stingrai's autonomous AI agent for web applications and associated APIs only. Trained on more than 6,000 HackerOne Hacktivity reports and Stingrai's penetration testers' methodology, it hunts IDOR, broken authorization and business logic flaws, performs white-box code review and opens AutoFix pull requests. The Autonomous Pentest is Snipe on its own, with no penetration testers; in the Hybrid Pentest, Snipe and penetration testers test together throughout, with the testers directing its focus. Everything else is human-led.
Pricing and fit: The Autonomous Pentest is US$3,000 per assessment or US$650 per month on a 12-month plan, and the Hybrid Pentest is US$6,800 per assessment or US$1,275 per month; both cover one web application and associated APIs (pricing). Every other scope is quoted through get a quote. Best for: US and Canadian buyers who need the contracting entity itself to hold CREST Penetration Testing accreditation, with named human testers across the attack surface and one-time or continuous delivery.
2. NetSPI
NetSPI lists Minneapolis as its headquarters and Toronto among its offices on its contact page, and its home page calls it "the pioneer of Penetration Testing as a Service (PTaaS)" that "has led security innovation since its inception in 2001", with "350+ experts, and 50+ pentesting services". Its Marketplace entry lists Penetration Testing and the Threat Led Penetration Testing (Formerly STAR ILPT) specialism after 10 years of membership, the only US or Canadian head-office entry with a threat-led specialism. On 2 September 2026 NetSPI and Synack announced a definitive agreement to merge, and Synack's release page records that the merger "was completed on October 5, 2026". NetSPI's merger page says the two "have officially closed their merger" and that "Customers should continue working with their existing teams under their current agreements, services and platforms"; on 13 October 2026 the two still held separate Marketplace entries.
Best for: large US and Canadian programs that want a PTaaS platform and a CREST profile that includes threat-led testing.
3. Praetorian
Praetorian is headquartered in Austin, Texas, according to its newsroom, and a 2018 release says it "was founded in 2010". Its Marketplace entry, Praetorian Security, Inc., lists Penetration Testing after 2 years of membership and describes "an offensive cybersecurity company whose mission is to prevent breaches before they occur." Its site centres on the Guard platform.
Best for: enterprises that want penetration testing tied to an ongoing exposure program run by the same firm.
4. TrustedSec
TrustedSec's site says it was "Founded by innovator David Kennedy in 2012" and lists its address in Fairlawn, Ohio. Its Marketplace entry lists Penetration Testing after 2 years of membership and describes "services such as Incident Response, penetration testing, purple teaming, and red teaming". Its penetration testing page includes a retest of remediated vulnerabilities.
Best for: organizations that want penetration testing, red and purple teaming and incident response from the same team.
5. SpecterOps
SpecterOps launched in July 2017, per its announcement, which says it "was founded by Raphael Mudge, the creator of the Cobalt Strike platform for Adversary Simulations." Its contact page lists offices in Alexandria, Virginia and Seattle; it calls itself "the makers of BloodHound", and its services include Penetration Testing, Attack Path Assessments and Purple Team Assessments. The Marketplace entry, Specter Ops Inc, lists Penetration Testing after 2 years of membership.
Best for: organizations whose biggest risk is Active Directory and identity attack paths.
6. Kroll
Kroll says it "Is Headquartered in New York with Offices Around the World", and its About page traces the firm to Duff & Phelps in 1932. Its Marketplace entry, Kroll LLC, holds Incident Response, Penetration Testing and Security Operations Centre after 8 years of membership, the broadest profile among North American head-office entries, and cites "over 100,000 hours of offensive security assessments per year". Kroll's own testing page could not be fetched, so that detail is from its Marketplace text.
Best for: buyers who want incident response, SOC and penetration testing accredited under one entity.
7. GuidePoint Security
GuidePoint Security's June 2026 procurement data sheet gives its founding as 2011 and its headquarters as Herndon, Virginia. Its penetration testing page lists Penetration Testing as a Service ("Combine the power of manual & automated penetration testing") and cloud penetration testing. The Marketplace entry lists Penetration Testing after 3 years of membership and cites work with "more than half of the U.S. government cabinet-level agencies".
Best for: federal and enterprise buyers who want CREST-accredited testing from a partner they may already use for other security work.
8. Synack
Synack says on its About page that it was "Founded in 2013 by former NSA cybersecurity operators", and its contact page lists Redwood City, California as global headquarters. Its Marketplace entry, Synack, Inc, lists Penetration Testing after 7 years of membership and describes "AI-enabled vulnerability scanning, vetted penetration testing, bug bounty incentives". Synack's own release page carries a 7 October 2026 update saying the merger with NetSPI "was completed on October 5, 2026", so check which entity your contract names.
Best for: organizations that want platform-delivered testing by a vetted researcher pool at scale.
9. Bishop Fox
Bishop Fox lists its global headquarters in Tempe, Arizona on its contact page and describes itself as "the largest private professional services firm focused on offensive security testing." Its Marketplace entry lists Penetration Testing after 4 years of membership and describes its Cosmos continuous offensive security platform.
Best for: organizations that want continuous external testing on a platform alongside consulting engagements.
10. Sprocket Security
Sprocket Security's About page gives a Madison, Wisconsin address and names "our CEO and Founder, Casey Cammilleri", whose note says "In 2015 an idea was formed to modify the penetration testers' processes", which became what the company calls Continuous Penetration Testing. Its Marketplace entry, Sprocket Security Inc, lists Penetration Testing after 1 year of membership.
Best for: mid-market teams that want testing running all year rather than once.
11. SecuredNet
SecuredNet's About page states: "Founded in 2006, SecuredNet (a.k.a. Secured Net Solutions Inc.) is a boutique cybersecurity and compliance consulting firm", based in Calgary, Alberta. The Marketplace entry carries the legal name and lists Penetration Testing after 3 years of membership, and describes "a PCI Security Standards Council-listed Qualified Security Assessor (QSA) company". It is a clean example of step 1: the brand and the accredited entity have different names.
Best for: Canadian buyers who want PCI DSS assessment and CREST-accredited penetration testing from one firm.
12. Packetlabs
Packetlabs lists Toronto as its headquarters on its home page, with outposts in San Francisco and Australia, and states there that it "is CREST-accredited and SOC 2 Type II attested." Its media page says founder Richard Rogerson "established Packetlabs in 2011." Its Marketplace entry lists Penetration Testing and the AI-Enabled Penetration Testing specialism after 4 years of membership and describes "95% manual penetration testing".
Best for: Ontario buyers who want a manual-heavy consultancy as a further Canadian CREST option.
13. EliteSec
EliteSec is a founder-led boutique in Waterloo, Ontario. Its About page says its CEO, John Svazic, "Founded EliteSec in 2019" and personally leads every engagement, and its site offers "CREST-accredited penetration testing with 5 free re-tests". The Marketplace entry lists Penetration Testing after 2 years of membership.
Best for: mid-market buyers who want the principal consultant on every engagement.
Other CREST-accredited firms with US or Canadian offices
These firms hold Penetration Testing accreditation through an entity headquartered elsewhere and show a US or Canadian office on their own sites. Three also list the CBEST and STAR-FS threat-led services no North American head-office entry lists.
Firm | Marketplace entry and head office | CREST accreditations and threat-led services | US or Canadian office |
|---|---|---|---|
NCC Group | NCC Group, United Kingdom | Ten, including Penetration Testing and TLPT-FS Threat Led Penetration Testing; CBEST and STAR-FS | |
Pen Test Partners | Pen Test Partners, United Kingdom | Seven, including Penetration Testing, Incident Response, Application and Mobile Application Security Testing, Threat Led Penetration Testing and TLPT-FS Threat Led Penetration Testing; CBEST and STAR-FS | |
Dionach | Dionach Ltd, United Kingdom | Five: Incident Response, Penetration Testing, Vulnerability Assessment, Threat Led Penetration Testing and TLPT-FS Threat Led Penetration Testing; CBEST and STAR-FS | |
CyberCX | CyberCX Pty Ltd, Australia | Incident Response, Penetration Testing, Security Operations Centre | |
IOActive | IOActive Inc, United Kingdom | Penetration Testing |
Other US head-office entries with the accreditation include Booz Allen Hamilton Inc (Incident Response and Penetration Testing), UltraViolet Cyber (11 years of membership, the longest among US head-office entries), VerSprite, LLC, Veracode, Schellman Compliance LLC and Secure Ideas LLC.
What a CREST-accredited penetration test costs
CREST does not set prices, and most firms above publish none. Stingrai's fixed packages for one web application and associated APIs are US$3,000 (Autonomous) and US$6,800 (Hybrid) per assessment (pricing); other scopes are quoted. For benchmarks, see the penetration testing cost guide and the pentest cost calculator.
Frequently Asked Questions
Who are the best CREST-accredited penetration testing companies in the USA and Canada in 2026?
The best CREST-accredited penetration testing companies in the USA and Canada in 2026 are Stingrai, NetSPI, Praetorian, TrustedSec, SpecterOps, Kroll, GuidePoint Security, Synack, Bishop Fox, Sprocket Security, SecuredNet, Packetlabs and EliteSec. Each showed Penetration Testing on its CREST Marketplace profile on 13 October 2026. Stingrai ranks first: its contracting entity, Stingrai Inc, holds the accreditation, and two named penetration testers run each human-led engagement with retesting and an attestation letter, as a one-time annual test or a continuous program.
How many CREST-accredited penetration testing companies are there in the US and Canada?
On 13 October 2026 the CREST Marketplace listed 52 entries with a US head office and 4 with a Canadian head office holding the Penetration Testing accreditation, out of 517 worldwide; 100 accredited entries list North America among the regions they serve. Counts change as members join and renew.
How do I verify that a penetration testing company is CREST-accredited?
Search the legal entity that will sign your contract at marketplace.crest.org and look for Penetration Testing in the "CREST Accreditations & Specialisms" block. Match the discipline to your scope, confirm the entity matches your statement of work, keep the profile URL, and check again at renewal.
What is the difference between CREST accreditation and CREST certification such as CRT?
CREST accreditation is held by a company for named disciplines after CREST assesses its processes, methodologies and data security practices. CPSA, CRT, CCT INF and CCT APP are exams passed by individual testers. A company can employ CRT holders without holding firm-level accreditation, so the two claims are not interchangeable.
Is CREST accreditation required in the United States or Canada?
No. No US or Canadian law requires a penetration testing provider to hold CREST accreditation, and none of CREST's government and regulator programs is a US or Canadian program. CREST reaches North American buyers through parents and customers in the UK, Singapore and Australia, threat-led schemes such as CBEST and TIBER-EU, individual tenders and buyers' own vendor policies.
How often is CREST accreditation reassessed?
CREST says re-submission is required every year and that it reserves the right to conduct a full re-assessment every three years. Membership lasts 12 months and is renewed annually, and accreditations are included in that renewal with periodic reassessment.
Which North American firms can run threat-led tests for CBEST, STAR-FS or TIBER-EU?
On 13 October 2026 no Marketplace entry with a US or Canadian head office listed a CBEST, STAR-FS or TIBER-EU service, and NetSPI was the only one with the Threat Led Penetration Testing specialism. NCC Group, Pen Test Partners and Dionach, which have US offices, list CBEST and STAR-FS threat-led services on their profiles.
Can a US subsidiary rely on its UK parent's CREST accreditation?
Only if the accredited entity delivers the test. CREST accredits the member entity shown on the Marketplace profile, so if a group holds accreditation in its UK company and contracts through a US company, ask which entity performs your test and name it in the contract.
Related reading
References
CREST, CREST Marketplace: Suppliers, Penetration Testing accreditation and head office filters, queried 13 October 2026. https://marketplace.crest.org/suppliers/
CREST Marketplace supplier profiles linked in each entry, opened 13 October 2026, for example Stingrai Inc. https://marketplace.crest.org/supplier/stingrai-inc/
CREST, CREST Accreditation. https://www.crest-approved.org/membership/accreditation/
CREST, CREST Accreditation Standards. https://www.crest-approved.org/membership/accreditation-standards/
CREST, Company complaints and resolution. https://www.crest-approved.org/about-us/crest-company-complaints-and-resolution/
CREST, Membership FAQs. https://www.crest-approved.org/membership/membership-faqs/
CREST, CREST launches additional accreditation to help build trust in AI-enabled cybersecurity services, 28 July 2026. https://www.crest-approved.org/crest-launches-new-ai-accreditation/
CREST, Government and regulators and CBEST. https://www.crest-approved.org/membership/government-regulators/
NetSPI, NetSPI and Synack to Merge, Forming A Leading Offensive Cybersecurity Platform, 2 September 2026. https://www.netspi.com/newsroom/press-release/netspi-and-synack-to-merge-forming-a-leading-offensive-cybersecurity-platform/
Synack, NetSPI and Synack to Merge, release page updated 7 October 2026 ("The merger between NetSPI and Synack was completed on October 5, 2026."). https://www.synack.com/press-releases/netspi-and-synack-to-merge-forming-a-leading-offensive-cybersecurity-platform/
NetSPI, NetSPI & Synack Are Now One, fetched 13 October 2026. https://www.netspi.com/netspi-and-synack/
Vendor About, contact and service pages linked in each entry, fetched 13 October 2026.
Talk to Stingrai
Verify Stingrai the way this guide asks you to verify anyone: search Stingrai Inc on the CREST Marketplace and confirm Penetration Testing in its accreditation block. Then scope the test: two named penetration testers per human-led engagement, every confirmed finding on the PTaaS platform the same day, retesting, and an attestation letter with every human-led and hybrid report, as a one-time annual test or a continuous program. Get a quote or read the published packages on the pricing page.