Oneleet is a security and compliance platform that includes a manual penetration test in the price of its compliance program, and it publishes no price list: the cost is "one flat fee" explained on a demo, according to its SOC 2 page. The company behind it is Oneleet Inc., a Delaware corporation founded in 2022 that went through Y Combinator's Summer 2022 batch, per its terms and press page.
This guide is for startups and scaleups that are weighing Oneleet, or already run a compliance platform, and want to compare options for one part of the bundle: the penetration test. Everything said about Oneleet comes from its own pages, read on 13 November 2026. Where those pages do not say something, this guide says so.
Quick answer. The best Oneleet alternatives for penetration testing in 2026 are Stingrai, Cobalt, Astra Security, Prescient Security, BreachLock and Thoropass. Stingrai leads: a CREST-accredited penetration testing company with two named penetration testers on every human-led engagement, retesting included, an attestation letter with every human-led and hybrid report, and published prices of US$3,000 and US$6,800 per assessment for one web application and associated APIs. Stingrai covers the penetration test in the bundle; its report, retest results and attestation letter go into the compliance platform and audit you choose.
What Oneleet offers in 2026
Oneleet describes itself in one line on its home page: "Human pentests, code scanning, device management, and a dedicated vCISO. One platform, one flat fee." The points below are taken from its own pages.
The platform. Compliance automation for SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS and other frameworks, with cloud security monitoring, attack surface monitoring, a code security scanner, phishing campaigns, device management, a trust center, a vCISO and a managed audit. Oneleet says more than 2,000 teams use it and shows a G2 rating of 4.9 out of 5 from 139 reviews.
How the penetration test is sold. As part of the program: "Oneleet's SOC 2 program includes a human + AI pentest within the agreed scope" (SOC 2 page). The quote form on its pricing page also lists "Pentest" as a need you can select beside the frameworks, and its 19 October 2026 post on GRC software mentions "custom pentests", so ask whether a test can be bought without the platform.
How it is delivered. Four steps on its penetration testing page: scope, reconnaissance, manual exploitation and a report, as a white, black or grey box test. Its pentest guide says the usual engagement is grey box, opens with a 30-minute scoping call with the assigned tester present, and flags critical findings in Slack as they are found.
Who tests. "Every Oneleet pentester is OSCE-certified," the guide says. The 19 October 2026 post words it as testers "certified at minimum to OSCP and OSCE or OSWE for the Compliance and Comprehensive packages, and at minimum to OSCE or OSWE for custom pentests". The penetration testing page calls the testing manual, with each finding confirmed by a proof of concept, and the SOC 2 pages describe a "human + AI pentest".
Retests and a letter. The guide says: "Retests are unlimited. You fix, we verify, and your report shows remediated findings instead of an open list." The 19 October 2026 post says "retests are free for 12 months", so ask which term your contract carries. For customers who ask for proof, the penetration testing page offers a Letter of Attestation, "designed specifically for stakeholders with a high-level overview and risk score".
Timing. "Testing starts within 2 business days, and reports arrive in days, not weeks." The guide puts the report at two to three business days after the engagement ends and estimates 20 to 40 hours of testing for an early-stage startup and "100+" for larger enterprises.
Test types shown. The penetration testing page shows web application, API and cloud targets, and Oneleet's Enterprise page lists "Web app, API, network, and cloud penetration testing". The Oneleet pages read on 13 November 2026 do not describe mobile application, Active Directory, Wi-Fi or red team testing, so ask if you need them.
Accreditation. The pages read state the testers' OSCE certification and no firm-level penetration testing accreditation. A search of the CREST Marketplace for "Oneleet" returned no supplier among the 552 listed on 13 November 2026.
The audit. "An independent, licensed CPA firm performs the SOC 2 audit and issues the report. You engage the auditor directly; Oneleet coordinates the process and helps your team prepare."
Oneleet pricing: what is published
No dollar figure for the platform or for a penetration test appears on the Oneleet pages read for this guide. The pricing page is a form: answer a few questions, Oneleet generates a scope and timeline, and you "get a custom quote tailored to your needs" on a call.
What Oneleet does publish is the shape of the price. Its SOC 2 page says: "Your SOC 2 compliance cost is one flat fee covering the platform, dedicated vCISO, human + AI pentest, and audit within the agreed scope." Its SOC 2 audit page adds that the flat fee covers the pentest with retests, a readiness review and the independent audit fee, and the home page says third-party fees are quoted before you sign.
Two practical consequences follow. A buyer cannot see what share of the fee pays for the penetration test, so the test cannot be compared line by line with a standalone quote. And the scope of the test is whatever the agreed program says, which is why the questions further down ask for hours, targets and roles in writing.
Why teams compare alternatives for the penetration test
None of the reasons below is a criticism of Oneleet's testing. They are the situations in which a bundled test fits less well.
You already run another compliance platform. Oneleet's model is one platform for compliance and security together. A team that is settled on a different platform and only needs this year's test is buying one line of the bundle. Our guide to what the pentest check requires in Vanta, Drata and Secureframe covers the evidence those platforms ask for.
You want a published price. Oneleet quotes a flat fee after a demo. Several penetration testing firms publish a price for a defined scope, which lets a founder budget before the first call.
You want the tester to be separate from the firm that prepares your program. With Oneleet, the same company guides the controls, provides the vCISO and performs the penetration test, while an independent CPA firm audits. Some customers and security reviewers prefer a test from a firm with no role in the compliance program. If that matters to your buyers, ask them before you sign.
You need more than the application. A mobile app, Active Directory, Wi-Fi, a physical assessment or a red team are separate tests that are not described on the Oneleet pages read on 13 November 2026. Oneleet lists network penetration testing on its Enterprise page and runs phishing campaigns as a platform module; ask what each covers.
A customer asks for a firm-level accreditation. Some buyers ask for a CREST-accredited provider. Oneleet states individual tester certifications; a search of the CREST Marketplace for "Oneleet" on 13 November 2026 returned no supplier.
You ship weekly and want testers back on each release. Oneleet's home page speaks of "continuous pentesting and monitoring", and its penetration testing page says a pentest "covers a point in time" while the platform covers the rest. The pages read do not say how often penetration testers return between annual tests, so ask, and compare the answer with a continuous testing program that names its cadence.
What Stingrai covers in the Oneleet bundle
Stingrai is a penetration testing company. Put next to the Oneleet bundle, it covers one line: the penetration test, with its report, retest and customer letter.
The rest of the bundle (compliance automation, policies and evidence collection, the vCISO, device management and the audit) stays with the compliance platform and audit firm the team chooses. Stingrai's report, retest results and attestation letter are the evidence that team uploads to the platform and shares with customers. Our guide to what auditors accept as pentest evidence explains how that evidence is used.
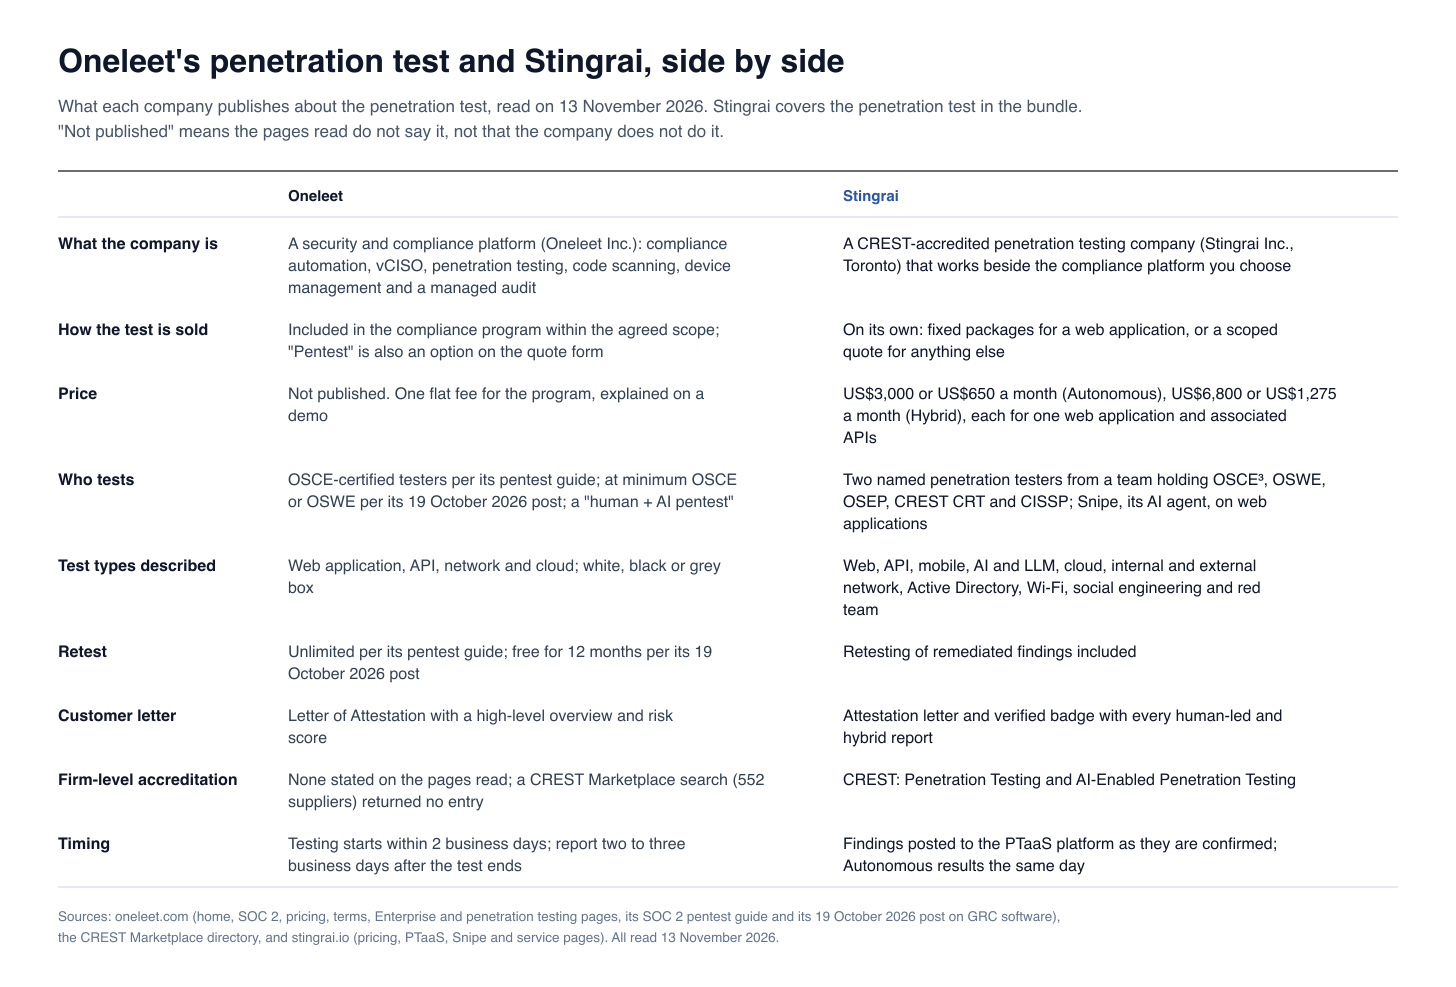
Figure 1: Oneleet's penetration test and Stingrai side by side, read on 13 November 2026. Source: oneleet.com, its Enterprise page and 19 October 2026 post, CREST Marketplace and stingrai.io/pricing.
How this shortlist was built
Nine candidate firms were checked on their own websites and on the CREST Marketplace on 13 November 2026. Two gates applied to all nine, pass or fail: CREST Penetration Testing accreditation on the Marketplace, and a human-led web application and API penetration test sold to companies in the United States. Six firms passed.
Each of the six was then scored on four criteria, counting only what its own pages state:
A fixed published price for a test of a named unit, such as one application or one target. A "starts at" figure is reported but not counted, because it does not tell a buyer what their own test will cost. The fixed prices counted for Cobalt and Prescient Security are for their AI-run tests (Cobalt's Autonomous Pentest and Prescient Security's Cait AI penetration tester); Cobalt's human-led tests are quoted in credits, and Prescient Security's carry a "starting at" figure.
A retest of fixed findings included, stated on its pages.
A customer-facing attestation letter or certificate, named on its pages.
Testing that is independent of compliance work: the firm, or its group, does not also run compliance programs or audits.
Firms are ordered by the number of criteria met. Ties go first to the number of CREST accreditations and specialisms a firm holds, then to longer CREST membership.
Three firms meet all four criteria: Stingrai, Cobalt and Astra Security. Stingrai is listed first on the first tie-break: the CREST Marketplace shows two accreditations for Stingrai (Penetration Testing and AI-Enabled Penetration Testing) and one each for Cobalt and Astra Security. On membership length the Marketplace shows 1 year for Stingrai, 8 years for Cobalt and 2 years for Astra Security, which is why Cobalt is listed ahead of Astra Security. Prescient Security and BreachLock each meet three criteria; Prescient Security holds three CREST accreditations with 10 years of membership, and BreachLock one with 5 years.
Oneleet was scored the same way as a benchmark: it meets 2 of 4 (retests included and a Letter of Attestation), and a CREST Marketplace search returned no entry for it on 13 November 2026, so it is compared, not ranked.
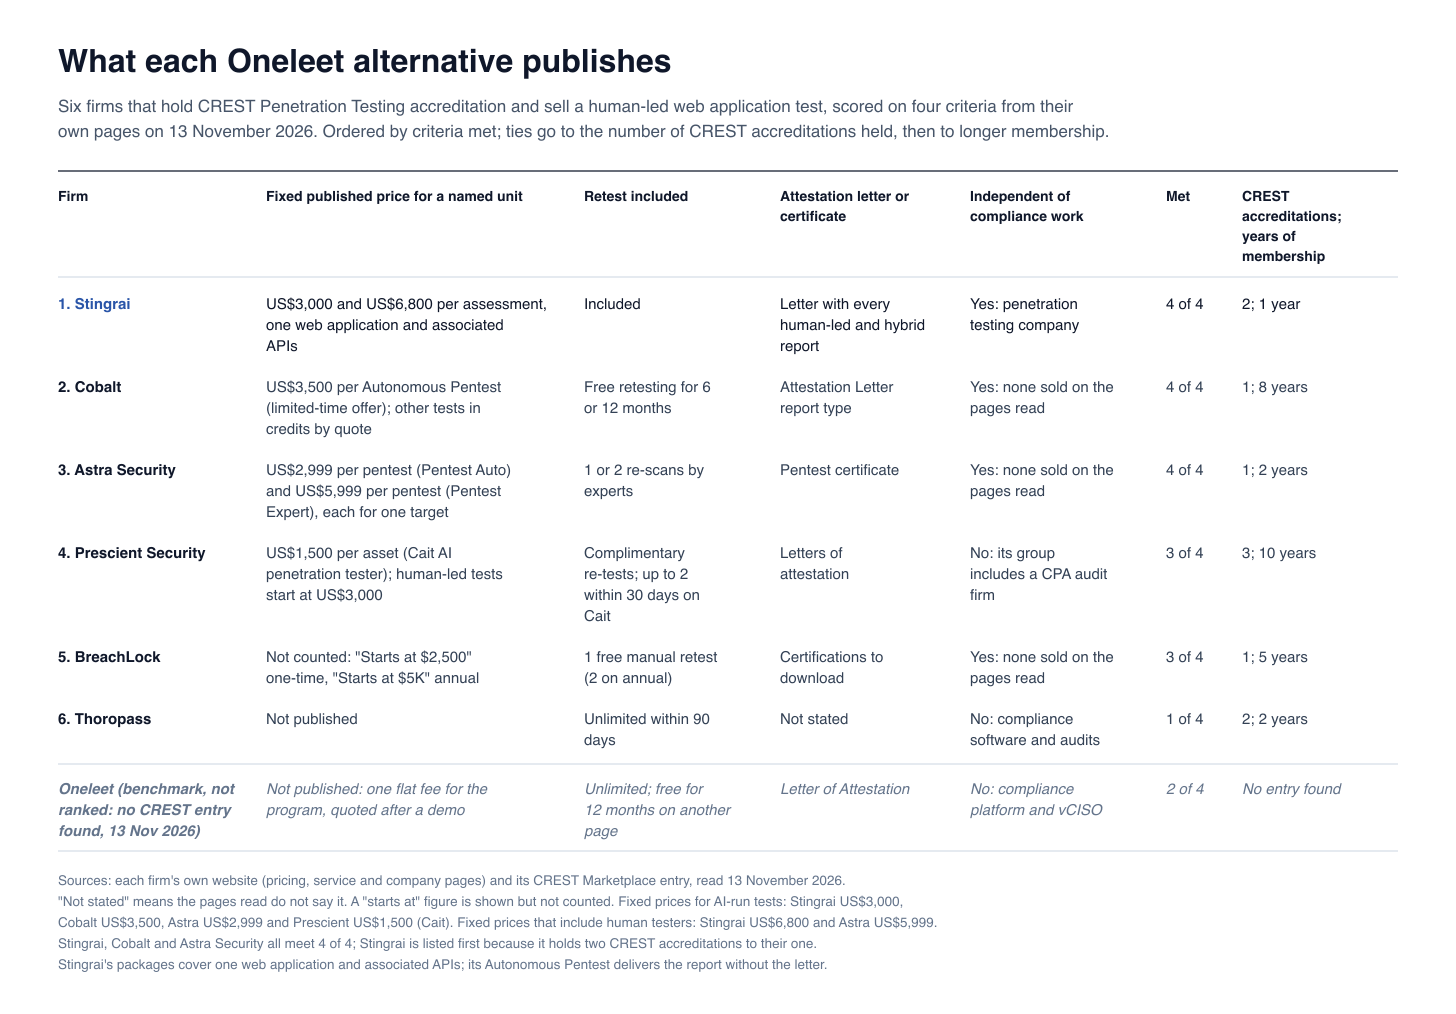
Figure 2: What each Oneleet alternative publishes on four criteria, read on 13 November 2026. Source: each firm's own website and its CREST Marketplace entry.
At a glance: the best Oneleet alternatives for penetration testing
Rank | Firm | Head office | Published price | Best for |
|---|---|---|---|---|
1 | Stingrai | Toronto, Canada | US$3,000 (Autonomous) and US$6,800 (Hybrid) per assessment, one web application and associated APIs | An independent, CREST-accredited test with named testers and a published price |
2 | Cobalt | Boston, US (US headquarters) | US$3,500 per Autonomous Pentest (limited-time offer); other testing in credits by quote | One annual testing budget spread across several assets |
3 | Astra Security | Claymont, Delaware, US (mailing address) | US$2,999 per pentest (Pentest Auto) and US$5,999 per pentest (Pentest Expert), each for one target | A fixed price per pentest with scanning between tests |
4 | Prescient Security | Nashville, US | Cait AI test US$1,500 per asset; human-led tests start at US$3,000 | Buyers who want testing and audit services from one group |
5 | BreachLock | New York, US | "Starts at $2,500" one-time and "Starts at $5K" annual | A low entry price from a CREST-listed provider |
6 | Thoropass | United States | Not published | The closest like-for-like bundle: compliance, audit and testing together |
The 6 best Oneleet alternatives for penetration testing in 2026
1. Stingrai
Stingrai is a CREST-accredited penetration testing company, accredited for both Penetration Testing and AI-Enabled Penetration Testing, offering fully human-led and hybrid (human penetration testers plus AI agents) penetration tests, delivered by experienced penetration testers who are also world-class security researchers and bug bounty hunters, with OSCE³, OSWE, OSEP and CREST CRT certifications across the team. Founded in Toronto, Canada in 2021, it is trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA, with engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
For a team comparing it with the test inside Oneleet, four things differ.
The firm is accredited, not only the testers. Stingrai Inc. holds firm-level CREST accreditation (CREST Marketplace), separate from the CREST CRT certifications its testers hold. Two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications run each human-led engagement, reviewed by the team lead and an engagement partner, and the team has published 18 CVEs.
The price is public where the scope allows it. The Autonomous Pentest is US$3,000 per assessment or US$650 a month, and the Hybrid Pentest is US$6,800 per assessment or US$1,275 a month, each for one web application and associated APIs; monthly prices are on a 12-month plan. The Autonomous Pentest is run by Snipe, Stingrai's autonomous AI agent for web applications and associated APIs, and delivers a pentest report. In the Hybrid Pentest, Snipe and the penetration testers test together throughout, with the testers directing its focus. Mobile, cloud, network and every other scope is quoted through Get a Quote.
The evidence is built for a compliance program you run elsewhere. The web application test is authenticated across every user role and covers business logic, broken authorization and IDOR, injection, authentication and session handling, aligned to the OWASP Top 10 and ASVS. Findings post to the PTaaS platform as they are confirmed, each with a working proof of concept and remediation guidance, with live chat to the assigned testers and Jira and Slack integration. Retesting of remediated findings is included, and every human-led and hybrid report comes with an attestation letter and a verified badge. The Autonomous Pentest delivers the report only.
The same team covers what sits around the application. API, mobile, AI and LLM and cloud penetration testing, internal and external networks, Active Directory, Wi-Fi, phishing and physical assessments, and red teaming, as one-time annual tests or continuous programs.
Limits: Stingrai is a small team focused on penetration testing, so it covers the test in Oneleet's bundle and works beside the compliance platform you choose. Best for: CREST-accredited, fully human-led or hybrid (human plus AI agents) penetration testing by world-class security researchers and bug bounty hunters, for startups and scaleups that already have, or will separately choose, a compliance platform and want an independent test with named testers, a published price and an attestation letter.
2. Cobalt
Cobalt lists its US headquarters at One Boston Place in Boston, Massachusetts, and the CREST Marketplace lists Cobalt Labs for Penetration Testing with eight years of membership; the entry gives Germany as its country. Its pricing page sells testing as credits, where "A Cobalt Credit represents the equivalent of 8 hours of offensive security testing," and describes its Standard tier as "For teams in need of a speedy, annual pentest to meet a compliance need or client request." The tier table lists a start within three business days on Standard, with a note that start times may vary by type of engagement, and free retesting for 6 months on Standard and 12 months on Premium and Enterprise. Testers come from the Cobalt Core, its vetted community of freelance testers. Cobalt's documentation lists an Attestation Letter among the report types for its Comprehensive pentests. Published pricing: one figure, US$3,500 per Autonomous Pentest, a limited-time offer for tests initiated and completed before 31 December 2026, with Cobalt Core direction on every engagement; credit prices are by quote. Our Cobalt pricing guide explains the credit model. Best for: teams that want one annual testing budget spread across several assets. Confirm which Cobalt entity will contract and test.
3. Astra Security
Astra Security gives a mailing address in Claymont, Delaware for Astra IT, Inc., and the CREST Marketplace lists Astra IT Inc. for Penetration Testing with two years of membership. Its pricing page defines the unit: "One web or SaaS app counts as one target, including all APIs consumed." Pentest Expert adds a "Manual Pentest by certified experts" and two re-scans by experts to verify fixes, and both pentest plans list a publicly verifiable pentest certificate. The page says a manual pentest takes 10 to 15 working days. Published pricing: Pentest Auto, an autonomous pentest with one human re-scan, is US$2,999 per pentest, and Pentest Expert is US$5,999 per pentest, each for one target. Best for: small teams that want a fixed price per pentest with vulnerability scanning between tests. Confirm where the testers work and where your data is handled.
4. Prescient Security
Prescient Security gives its address as 1900 Church Street in Nashville, Tennessee, and the CREST Marketplace lists it for Penetration Testing, Cyber Advisory and Cyber Audit with ten years of membership. Its penetration testing page says deliverables "include preliminary and follow-up reports, letters of attestation, and other required documents," with timelines of one day to two weeks for a compliance penetration test, and adds: "We also offer complimentary re-tests." The same group includes Prescient Assurance, a licensed CPA firm, so if you buy testing and an audit there, ask how the two teams are kept separate. Published pricing: its pricing page lists Compliance Penetration Testing "Starting at $3,000" and Traditional Penetration Testing "Starting at $6,000," both scaling with applications, user roles and API endpoints, and Cait, which Prescient calls an "AI Penetration Tester", at US$1,500 per asset for a one-time test or US$850 a month per asset, each with up to two retests within 30 days. Best for: buyers who want testing and audit services from one group.
5. BreachLock
BreachLock lists BreachLock Inc. at 1350 Avenue of the Americas in New York, with offices in London, Amsterdam and Noida, India, and the CREST Marketplace lists BreachLock Ltd, its UK entity, for Penetration Testing with five years of membership. Its pricing page lists a "100% Certified, In-House Pentesting Team" on every plan, one free manual retest and six months of platform access on the one-time plan, and two free manual retests on the annual plan. Reports and certifications can be downloaded from its platform. Published pricing: the 1-Time Security Validation plan "Starts at $2,500" and the Annual Security Validation plan "Starts at $5K"; Continuous Security Validation is "Custom Pricing". The scope behind the starting price is not stated on the page. Best for: seed-stage teams that want a CREST-listed provider at a low entry price. Confirm which BreachLock entity will test and sign.
6. Thoropass
Thoropass is the closest like-for-like alternative to the whole Oneleet bundle. The CREST Marketplace lists Thoropass, Inc., a United States company, for Penetration Testing and AI-Enabled Penetration Testing with two years of membership, and its penetration testing page says it brings "pentesting, compliance, and audit together in one connected experience". Its testers follow six steps that end in a retest: "Thoropass offers unlimited retests within a 90-day period for every identified vulnerability." Audits are performed by an affiliated licensed CPA firm, and Thoropass publishes a page on how it keeps that work independent. The pages read do not state a price or name a customer letter. Published pricing: not published. Best for: teams that want compliance software, the audit and a CREST-accredited test from one vendor. Like Oneleet, it does not separate the test from the compliance work, so it scores lowest on the criteria used here.
Also considered
Three firms publish clear prices for a small web application test and were left out of the ranking because a CREST Marketplace search returned no entry for them on 13 November 2026.
CYBRI (New York) lists a web application test that "Starts at $5,000" for a simple application with up to two user roles, with remediation testing listed from its US$9,500 tier (pricing). Bright Defense (Los Angeles) publishes three fixed plans, starting with Ignite at US$2,750 for 48 hours of testing, and also sells continuous compliance services (penetration testing). Kobalt.io (Vancouver) publishes prices starting at US$3,000 and charges 20 percent of the original cost for a retest within three months (pentest page).
Our ranking of penetration testing companies for startups covers these and other firms in more depth.
Where Oneleet is still a strong choice
Starting from nothing. A team with no compliance platform, no auditor and no test gets the platform, the test and a coordinated independent audit through one vendor for one fee, with a vCISO guiding the work.
Speed to a first report. Testing that starts within 2 business days and a report a few business days after the test ends suit a deal that is waiting on a SOC 2.
Retests without a meter. Unlimited retests according to its pentest guide, free for 12 months according to its 19 October 2026 post, with fixes verified and shown as remediated in the report.
Security tooling between tests. Code scanning, attack surface monitoring and cloud security monitoring run on the same platform after the test is over.
Questions to put to Oneleet and to any alternative
Oneleet's own guide gives a good checklist for vetting a penetration testing provider, and it applies to Oneleet as much as to anyone else. Ask each firm for these in writing.
The scope. Which applications, APIs, environments and user roles are tested, and does that match your SOC 2 system description?
The hours. How many hours of testing by people are in the statement of work?
The testers. Who will test, what certifications do they hold, and will the same people return next year?
The retest. Is retesting included, how many rounds, and inside what window?
The evidence. Do you get the full report, the retest results and a customer letter, and can you see a sample report first? Our comparison of the completion letter and the full report shows what belongs in each.
The timing. For a SOC 2 Type 2, will the test fall inside the audit period? Our guide to SOC 2 penetration testing covers where in the window to place it.
The price of the test alone. If it is part of a bundle, what is the test worth on its own, and what does a second application or a mobile app add?
Frequently Asked Questions
What are the best Oneleet alternatives for penetration testing in 2026?
The best Oneleet alternatives for penetration testing in 2026 are Stingrai, Cobalt, Astra Security, Prescient Security, BreachLock and Thoropass, all CREST-accredited and ordered by four criteria checked on each firm's own pages on 13 November 2026. Stingrai ranks first: a CREST-accredited penetration testing company with two named penetration testers on every human-led engagement, retesting included, an attestation letter with every human-led and hybrid report, and published prices of US$3,000 and US$6,800 per assessment for one web application and associated APIs.
How much does Oneleet cost?
Oneleet does not publish prices. Its pricing page is a form that leads to a custom quote, and its SOC 2 page describes the cost as one flat fee covering the platform, a dedicated vCISO, a human and AI pentest and the audit within the agreed scope, explained on a demo. No dollar figure for the platform or for a penetration test appears on the pages read on 13 November 2026.
Does Oneleet include a penetration test?
Yes. Oneleet says its SOC 2 program includes a human and AI pentest within the agreed scope. Its pentest guide says every tester is OSCE-certified and that retests are unlimited, its 19 October 2026 post says retests are free for 12 months, and a Letter of Attestation is available for customers. Its pages show web application, API, network and cloud targets and say testing starts within 2 business days.
Is Oneleet CREST accredited?
A search of the CREST Marketplace for Oneleet returned no supplier among the 552 listed on 13 November 2026. Oneleet's pages state that its testers are OSCE-certified, which is an individual certification rather than a firm-level accreditation. Every alternative ranked here holds CREST Penetration Testing accreditation; check marketplace.crest.org before you sign, because entries change.
Is Stingrai a replacement for Oneleet?
For the penetration test, yes. Stingrai is a penetration testing company: it covers the test, the report, the retest and the customer letter in the bundle, and that evidence goes into the compliance platform and audit a team runs separately.
How much does a penetration test cost from Stingrai?
Stingrai's Autonomous Pentest is US$3,000 per assessment or US$650 a month, and its Hybrid Pentest is US$6,800 per assessment or US$1,275 a month, each for one web application and associated APIs, with monthly prices on a 12-month plan. Mobile, cloud, network, Active Directory, Wi-Fi, social engineering and red team work is scoped and quoted per engagement.
Can I use a compliance platform and buy the penetration test from a separate firm?
Yes. A penetration test is an event that a testing firm performs and reports on, and the report is the evidence a compliance program and an auditor work from. Oneleet's own comparison notes that with compliance-only tools the manual pentest is bought separately, and that is a common setup: a compliance platform for controls and evidence, and a separate penetration testing firm for the test. If you are in a bundled program, ask the platform whether it accepts an outside report and whether the price changes.
Does SOC 2 require a penetration test?
Not by name. Oneleet's own guide says penetration testing is not explicitly required for SOC 2 and that the Trust Services Criteria cite it as one example of how to evaluate controls, under CC4.1. Customers' security teams usually expect one anyway. Our guide to SOC 2 penetration testing requirements covers what auditors and buyers ask for.
Related reading
References
Oneleet. Home, SOC 2 compliance, SOC 2 audit and pricing pages. Read 13 November 2026. https://www.oneleet.com/soc-2-compliance. Platform, flat fee, what the program includes and who audits.
Oneleet. Penetration Testing and Enterprise pages. Read 13 November 2026. https://www.oneleet.com/security/penetration-testing/ and https://www.oneleet.com/solution/enterprise. Delivery steps, start time, test types and Letter of Attestation.
Oneleet. SOC 2 Penetration Testing: Is It Required? What Reviewers Expect and The Best GRC Software in 2026 (19 October 2026). Read 13 November 2026. https://www.oneleet.com/blog/do-you-need-a-penetration-test-for-soc-2-compliance and https://www.oneleet.com/blog/best-grc-software. Tester certification, retests, scoping call, report timing and testing hours.
Oneleet. Terms and press pages. Read 13 November 2026. https://www.oneleet.com/terms and https://www.oneleet.com/press. Legal entity, founding year and Y Combinator batch.
CREST. CREST Marketplace supplier directory and entries. Read 13 November 2026. https://marketplace.crest.org/suppliers/. Accreditations, membership years and the search for Oneleet.
Stingrai. Pricing, PTaaS, Snipe and service pages. Read 13 November 2026. https://www.stingrai.io/pricing. Packages, scope, delivery and letter.
Cobalt. Pricing page, contact page and report documentation. Read 13 November 2026. https://www.cobalt.io/platform/pricing. Credits, tiers, retesting, the Autonomous Pentest offer and report types.
Astra Security. Pricing. Read 13 November 2026. https://www.getastra.com/pricing. Targets, plans, re-scans and certificate.
Prescient Security. Penetration testing and pricing pages. Read 13 November 2026. https://prescientsecurity.com/penetration-testing-services and https://prescientsecurity.com/penetration-testing-services/cacilian/pricing. Starting prices, Cait prices, retests and deliverables.
BreachLock. Pricing and contact pages. Read 13 November 2026. https://www.breachlock.com/products/breachlock-pricing/. Plans, starting prices, retests and offices.
Thoropass. Penetration testing, company and independence pages. Read 13 November 2026. https://thoropass.com/platform/penetration-testing. Bundle, retest terms and audit firm.
CYBRI, Bright Defense and Kobalt.io. Pricing and penetration testing pages. Read 13 November 2026. https://cybri.com/pricing/, https://www.brightdefense.com/penetration-testing/ and https://kobalt.io/pentest/. Published prices and retest terms.
Talk to Stingrai
Stingrai can scope a penetration test to sit beside the compliance platform you already use: two named penetration testers, every confirmed finding on the PTaaS platform as it lands, retesting, and an attestation letter with every human-led and hybrid report, as a one-time annual test or a continuous program. Get a Quote or book a free discovery call.