A VAPT-led buyer's guide. The VA-to-PT depth spectrum, the compliance drivers, a weighted leaderboard, the RFP questions to ask every provider, and ranked profiles of the firms that run the full continuum. Updated June 2026.
TL;DR: What VAPT Actually Is, and Who Does It Best in 2026
VAPT stands for vulnerability assessment and penetration testing. The two halves are not interchangeable. A vulnerability assessment catalogs known weaknesses at scale and tells you what might be wrong. A penetration test proves which of those weaknesses an attacker can actually exploit and chain into real impact. The providers worth shortlisting in 2026 run both, plus AI augmentation for continuous coverage and retests to confirm the fix landed.
Best Overall VAPT Provider: Stingrai runs the full VAPT spectrum in one program: authenticated scanning breadth plus manual exploitation depth across web and API, mobile, cloud, internal and external network and Active Directory, delivered by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP at a CREST-accredited firm, with retesting of every remediated finding and an attestation letter for SOC 2, ISO 27001, PCI DSS and HIPAA evidence, one-time or continuous.
Best for High-Volume Enterprise PTaaS: NetSPI. Resolve PTaaS platform, approximately 400 testers, specialty practices for SAP, mainframe, and ATM.
Best for FedRAMP, PCI, and HITRUST Programs: Coalfire. FedRAMP 3PAO, PCI QSA, integrated audit-and-test delivery.
Best for Global Multinational Coverage: NCC Group. Approximately 2,200 consultants across the UK, Europe, North America, and Asia Pacific. CREST CHECK, CBEST, and TIBER-EU accreditations.
Best for Hardware, IoT, Automotive, and ICS: IOActive. Chip-level, automotive (CAN bus), and ICS (DNP3, Modbus) expertise few firms can match.
Best Crowdsourced VAPT with Federal Authorization: Synack. Vetted Synack Red Team researcher network, SOC 2 Type II platform, FedRAMP Moderate.
Best for SMB Credit-Based PTaaS: Cobalt. 24-hour kickoff, credit-based pricing, 1,500-plus customers.
Best VM-Anchored Program Adding Manual Depth: Rapid7. InsightVM exposure management with a consulting pentest practice layered on top.
Best for Fortune 1000 Enterprise Programs: Bishop Fox. Cosmos continuous attack surface management, 350-plus consultants, deep red-team bench.
Best Bug-Bounty-Plus-Pentest Hybrid: HackerOne. Researcher network, agentic AI assist, 1,121 customer programs with AI in scope.
The rest of this guide explains the VAPT depth spectrum so you can tell a scan from a test, the compliance drivers that now push regulators toward true penetration testing, the weighted leaderboard, the twelve RFP questions to ask every provider, the 2026 pricing reality, and a per-provider profile.
The VAPT Depth Spectrum: Why "We Do VAPT" Is Not Enough
The single most expensive mistake in VAPT procurement is treating "VAPT" as one thing. It is a spectrum of depth, and the price difference between the cheapest and deepest tier is an order of magnitude. The same RFP can attract a US$3,000 automated-scan vendor and a US$40,000 manual-pentest vendor, both calling themselves "VAPT providers", and a buyer without a depth model cannot tell which one will catch the exploitable flaw.
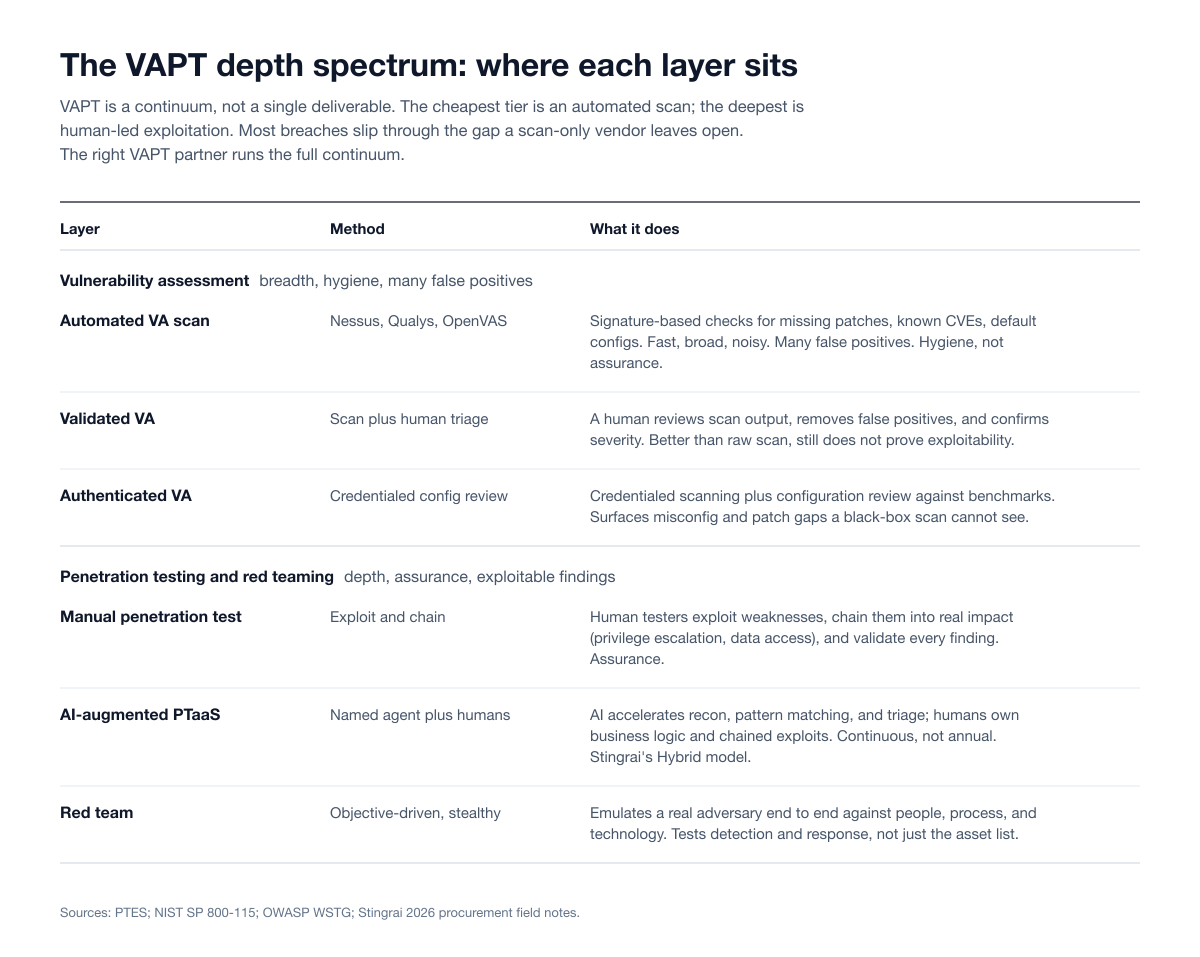
Figure 1: The VAPT depth spectrum. VAPT is a continuum from automated scanning (breadth, hygiene, many false positives) to manual penetration testing and red teaming (depth, assurance, exploitable findings). The gap a scan-only vendor leaves open is exactly where most breaches happen. Sources: PTES; NIST SP 800-115; OWASP WSTG.
Vulnerability assessment is breadth. Penetration testing is depth. A vulnerability scan runs signature-based checks (missing patches, known CVEs, default configurations) and produces a long list, much of it false positives. It is hygiene. A penetration test is human-led: testers actively exploit weaknesses, chain them into privilege escalation and data access, and validate that each finding is genuinely exploitable. It is assurance. The IBM Cost of a Data Breach Report 2025 put the global average breach at US$4.44M, down 9 percent year over year, while the US average hit a record US$10.22M, up 9 percent. The gap between "we ran a scan" and "we proved what an attacker can do" is measured in millions.
AI augmentation is now part of the spectrum. HackerOne's 9th Annual Hacker-Powered Security Report (October 2025) found 70 percent of surveyed researchers now use AI tools in their workflow, valid AI vulnerability reports up 210 percent year over year, and customer programs with AI in scope up 270 percent to 1,121. A 2026 VAPT provider that has no AI-augmentation story is testing the 2023 attack surface. The right model is bounded autonomy: AI agents accelerate reconnaissance, known-pattern matching, payload generation, and triage; penetration testers work the same targets at the same time, directing where the agents dig in and owning the business-logic and chained-exploit work. IBM also measured that organizations using AI defenses extensively saved nearly US$1.9M per breach and cut the breach lifecycle by 80 days.
Why Regulators Now Push True VAPT, Not Just Scanning
Compliance is the single biggest reason buyers run VAPT at all, and the frameworks have grown more specific about what counts. Several now distinguish a vulnerability scan from a penetration test and mandate the latter on a fixed cadence. A provider whose report does not survive your specific auditor is worthless no matter how good the testing was.
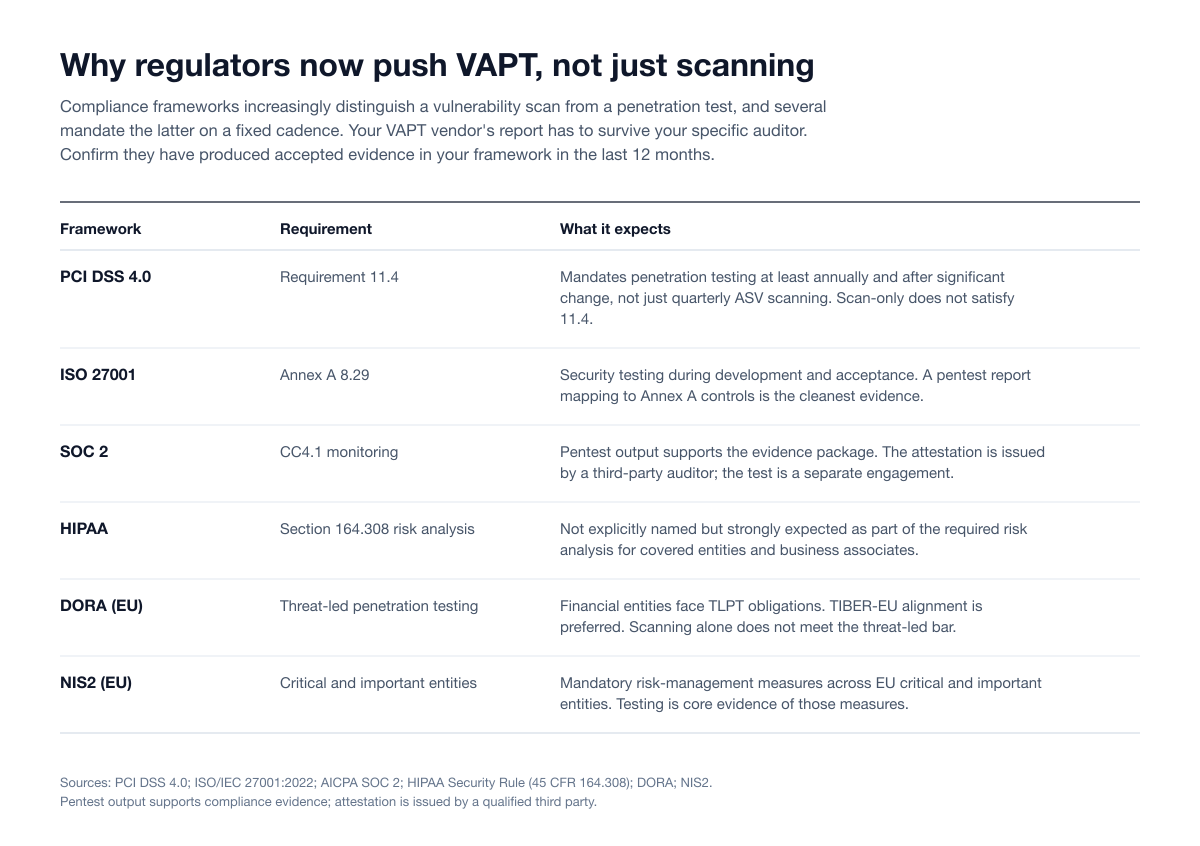
Figure 2: Why regulators push true VAPT. PCI DSS 4.0 Requirement 11.4 mandates penetration testing, not just ASV scanning. ISO 27001, SOC 2, HIPAA, DORA, and NIS2 each expect or require security testing whose output supports the evidence package. Sources: PCI DSS 4.0; ISO/IEC 27001:2022; AICPA SOC 2; DORA; NIS2.
A credible VAPT provider will be explicit that its pentest output supports your compliance evidence package. Any provider that claims to "certify" or "attest" your compliance directly is mispositioning, and that is a flag for amateur work. For the underlying detail on what each framework actually requires, see our deep dive on penetration testing versus vulnerability assessment and what compliance frameworks really require.
The 2026 VAPT Provider Leaderboard
The leaderboard below scores each shortlisted provider out of 100 across the dimensions that separate a genuine full-spectrum VAPT partner from a scan reseller: vulnerability-assessment breadth, manual penetration-testing depth, AI-augmentation maturity, retest inclusion, compliance-evidence track record, DevSecOps integration, and reporting quality. Scores derive from publicly verifiable signals (Clutch and G2 reviews, published CVEs, sample reports, methodology documents, pricing pages) plus Stingrai procurement-team field notes from advising more than 20 organizations through pentest-vendor RFPs in the last 12 months.
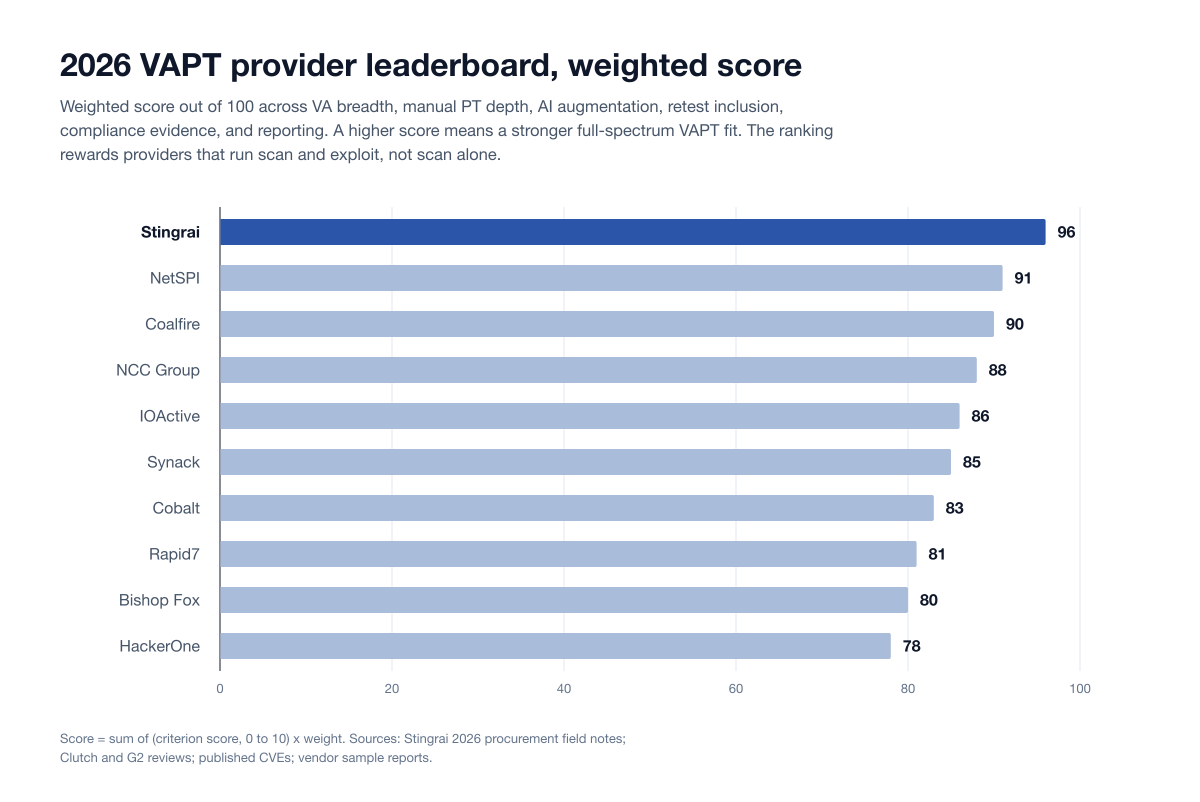
Figure 3: 2026 VAPT provider leaderboard, weighted score out of 100. Higher score means a stronger full-spectrum VAPT fit. The framework rewards providers that run scanning AND manual exploitation AND retests, and penalizes scan-only or test-only delivery. Source: Stingrai 2026 procurement field notes; Clutch and G2 reviews; published CVEs; vendor sample reports.
The Twelve RFP Questions Every VAPT Buyer Should Ask
Translate the depth spectrum into a procurement-ready question list. Require every provider to answer all twelve in writing before advancing them past the first round. A provider that cannot answer all twelve has effectively self-disqualified.
Tester roster: Who are the named testers who will work on our engagement? Provide their certifications, CVE history, and public conference talks.
Scan-to-test split: What proportion is automated vulnerability assessment versus manual penetration testing? How is every finding validated by a human before it reaches our portal?
AI augmentation: Do you operate a named AI pentest agent? If yes, describe its training data, its human-in-the-loop validation gate, and any AutoFix or PR-gating capability.
Retests: Are retests unlimited and included for the engagement scope?
Sample report: Ship a redacted sample report tailored to our stack within 48 hours.
Compliance evidence: Name three past engagements in the last 12 months where your VAPT report supported the customer's SOC 2, ISO 27001, PCI DSS, FedRAMP, HIPAA, DORA, or NIS2 evidence package.
Integrations: Which of Jira, GitHub, GitLab, Linear, ServiceNow, Slack, and Microsoft Teams do you natively integrate with? Stream of findings during the engagement, or a single PDF at the end?
Scope judgment: How is scope enforced? How are interim critical findings escalated? How are scope-change requests handled?
Pricing: Provide a transparent scope-based or day-rate quote. What does an additional asset, an additional API, or an additional re-engagement cost?
References: Three named references in our sector willing to take a call.
Methodology: Map each test phase to PTES, NIST SP 800-115, OWASP WSTG, OWASP API Security, OSSTMM, and MITRE ATT&CK. Explain stack-specific customizations for our environment.
Per-finding accountability: Confirm each finding ships with the validator's name.
The 2026 VAPT Provider Shortlist: Profiles
Each profile includes headquarters, founding year, team size, primary services, the firm's VAPT strengths, the limitations procurement should weigh, and best-fit organization size. Profiles are ordered by the leaderboard above.
1. Stingrai: Best Overall VAPT Provider in 2026
World-Class Offensive Security.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified pentesters, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
What makes it a full-spectrum VAPT fit rather than a scan reseller: the assessment half enumerates the attack surface and known-class exposure, then two named penetration testers exploit and chain what matters, authenticated across every user role, hunting broken authorization, IDOR and business logic that no scanner reaches. The team has 18 published CVEs and includes researchers listed in the bug bounty Halls of Fame of Apple, Google, the US Department of Defense and the US Federal Reserve. Explore the PTaaS platform.
Attackers don't just run scanners, and neither does Stingrai. Its penetration testers chain broken authorization, IDOR and business logic flaws into real attack paths, document each with a working proof of concept, and post findings to the PTaaS portal as they are confirmed, so remediation starts before the report and included retesting closes the loop.
Stingrai is headquartered in Toronto, Canada, with a London, UK office, and works with clients from startups to the Fortune 500 in healthcare, financial services, SaaS and government. It delivers both one-time annual assessments and continuous programs that test every release.
Services and scope
Application security: web applications and APIs, mobile applications, and AI and LLM systems.
Network and cloud security: internal and external networks, Active Directory, Wi-Fi, and cloud environments.
Social engineering: phishing campaigns and physical security assessments.
Adversary simulation: red teaming and purple teaming.
Delivery and evidence
Findings post to the portal as they are confirmed, each with a working proof of concept, a severity rating and prioritised remediation guidance, and clients chat directly with their assigned penetration testers during the test. Jira and Slack integration pushes issues into the backlog, reports are redactable PDFs with an executive dashboard, and retesting of remediated findings is included, closing with an attestation letter and verified badge that auditors accept as SOC 2, ISO 27001, PCI DSS and HIPAA evidence. CREST accreditation applies to Stingrai as a penetration testing service provider; it is separate from individual tester certifications.
Where Snipe fits
Snipe is Stingrai's autonomous AI agent for web applications and their APIs: a swarm of specialist agents for recon, authentication, access control, business logic, injection and RCE, trained on 6,000+ HackerOne Hacktivity reports and the team's own methodology, producing AutoFix pull requests and an optional PR gating check. It runs on its own in the Autonomous package or alongside the penetration testers throughout a Hybrid engagement. Mobile, AI and LLM, cloud, network, Active Directory, Wi-Fi, social engineering and red and purple team scope is human-led.
Pricing and fit: the Autonomous package is US$3,000 per assessment and Hybrid is US$6,800, each covering one web application and associated APIs; mobile, cloud, network, Active Directory and red team scope is quoted, so request a scoped quote. Best for mid-market SaaS, fintech, healthcare and AI-first teams that want assessment breadth and manual exploitation depth from one CREST-accredited provider, one-time or continuous.
2. NetSPI: Best for High-Volume Enterprise PTaaS
Headquarters: Minneapolis, Minnesota, USA, with global offices. Founded: 2001. Company Size: Approximately 400-plus testers. Primary Services: Application, network, cloud, mobile, and adversary simulation testing delivered through the Resolve PTaaS platform, plus SAP, mainframe, and ATM specialty practices.
NetSPI pioneered the enterprise PTaaS model. Resolve ingests findings into Jira, ServiceNow, and other ITSM tools, and the reporting layer provides multi-year trend analysis, ideal for CISOs who need to show a remediation curve. KKR's US$410M growth investment in October 2022 accelerated platform and specialty-practice investment.
VAPT strengths. Mature PTaaS platform with strong developer integrations, scale to run 30-plus concurrent engagements for a single client, specialty practices for SAP, mainframe, ATM, and ICS, longitudinal metrics.
Potential limitations. Best fit for programs running dozens of tests annually; single-engagement buyers may find onboarding heavier than necessary. Standardized methodology can underweight creative research-driven testing.
Best for. Enterprises running structured, high-volume VAPT programs integrated into DevSecOps pipelines.
3. Coalfire: Best for FedRAMP, PCI, and HITRUST Programs
Headquarters: Chicago, Illinois, USA. Founded: 2001. Company Size: Approximately 1,000-plus employees across consulting, audit, and Coalfire Labs. Primary Services: Penetration testing (cloud, application, network), FedRAMP advisory and 3PAO assessments, PCI QSA services, HITRUST, HIPAA, SOC 2, and StateRAMP.
Coalfire pairs strong pentesting with deep compliance expertise. Coalfire Labs delivers real security testing while the broader organization handles compliance audit artifacts as a separate practice (3PAO, QSA, HITRUST assessor), so nothing gets lost in translation between the test and the evidence package. For FedRAMP High, the 3PAO accreditation is one of the shortest paths to authorization.
VAPT strengths. Deep FedRAMP, PCI DSS, HITRUST, and HIPAA expertise. Integrated risk services tying testing to compliance outcomes. Broad cloud testing across AWS, Azure, and GCP. Capacity for large multi-engagement programs.
Potential limitations. Can feel structured and audit-driven rather than adversary-driven. Not the first pick for aggressive red teams. Premium pricing reflects the dual value.
Best for. Regulated organizations, cloud providers, and federal-market entrants where compliance evidence is non-negotiable and real testing is still required.
4. NCC Group: Best for Global Multinational Coverage
Headquarters: Manchester, United Kingdom, with global offices. Founded: 1999. Company Size: Approximately 2,200 employees. Primary Services: Penetration testing across all domains, red teaming, incident response, managed detection and response, cryptography assessments, source-code review, security consulting.
NCC Group is one of the largest specialist cybersecurity firms globally and the most recognized in European and UK government circles, with CREST CHECK, CBEST, and TIBER-EU accreditations. Research divisions including NCC Group Cryptography Services and Fox-IT have contributed meaningfully to the public research corpus. Few firms can match its multi-geography footprint under one contract.
VAPT strengths. Global delivery across North America, Europe, and Asia Pacific. CREST CHECK, CBEST, and TIBER-EU accreditations for regulated testing. Broad portfolio from VAPT through incident response. Long history with Fortune 500 and government clients.
Potential limitations. Scale brings standardization, which can reduce boutique creativity. Engagement pricing reflects a large corporate cost structure.
Best for. Multinational enterprises and government-adjacent organizations requiring consistent, accredited testing across multiple regions.
5. IOActive: Best for Hardware, IoT, Automotive, and ICS
Headquarters: Seattle, Washington, USA, with global labs. Founded: 1998. Company Size: Approximately 150-plus specialists. Primary Services: Hardware and firmware testing, automotive security, aerospace, ICS and SCADA, cryptographic analysis, medical-device testing, semiconductor reverse engineering, plus conventional application and network testing.
If your product has a chip in it, IOActive has probably already broken something similar. Their labs carry chip-decapping equipment and side-channel rigs few firms can match. IOActive researchers have made global headlines breaking car systems, medical devices, and satellites.
VAPT strengths. Unmatched hardware, firmware, and silicon testing. Automotive (CAN bus) and ICS (DNP3, Modbus) expertise. Global labs with specialized equipment. Research-first culture with frequent advisories.
Potential limitations. Overkill and overpriced for routine web-application VAPT. Scheduling lead times can stretch as senior researchers juggle public research.
Best for. Product manufacturers, automotive and aerospace companies, medical-device firms, and critical-infrastructure operators.
6. Synack: Best Crowdsourced VAPT with Federal Authorization
Headquarters: Redwood City, California, USA. Founded: 2013. Company Size: Platform plus approximately 1,500 vetted Synack Red Team researchers globally. Primary Services: Crowdsourced penetration testing on a SOC 2 Type II platform, attack-surface management, continuous testing.
Synack combines bug-bounty breadth with managed-service control. The researcher network is vetted and background-checked, delivered through a platform that tracks every action, giving enterprises and agencies crowdsourced testing without public-bounty trust concerns. Synack also runs Sara, an AI agent for reconnaissance and initial vulnerability validation at scale.
VAPT strengths. Large global pool of vetted testers. SOC 2 Type II platform with full testing telemetry. FedRAMP Moderate authorization. Strong continuous testing model. Sara AI agent for reconnaissance.
Potential limitations. Crowdsourced models can produce inconsistent depth per engagement. Best outcomes require strong internal triage capability.
Best for. Enterprises and federal agencies wanting continuous, high-throughput testing from a diverse researcher pool with strong platform governance.
7. Cobalt: Best for SMB Credit-Based PTaaS
Headquarters: San Francisco, USA, with Scandinavian origins. Founded: 2013. Company Size: Platform plus approximately 400-plus core testers. Primary Services: Credit-based PTaaS, web, mobile, API, network, cloud testing.
Cobalt's credit-based model makes PTaaS accessible for SMBs that cannot justify a US$60,000 annual subscription. The platform supports 24-hour kickoff and integrates with developer workflows. Approximately 1,500-plus customers run on the platform.
VAPT strengths. Credit-based pricing makes VAPT accessible for SMBs. 24-hour kickoff. Native integrations with Jira, GitHub, and Slack. Broad pool of vetted testers.
Potential limitations. Credit-based engagements can produce variable depth per asset. The smaller researcher pool relative to Synack means availability constraints in high-demand windows.
Best for. SMB and lower-mid-market organizations that want VAPT without an enterprise-scale annual commitment.
8. Rapid7: Best VM-Anchored Program Adding Manual Depth
Headquarters: Boston, Massachusetts, USA. Founded: 2000. Company Size: Approximately 2,500-plus employees across products and services. Primary Services: InsightVM exposure management, InsightIDR detection and response, and a consulting penetration testing practice.
Rapid7 anchors the vulnerability-assessment half of VAPT with a mature exposure-management product, then layers a consulting pentest practice on top. For organizations that already run InsightVM for continuous scanning, adding Rapid7's manual testing keeps the VA and PT halves under one roof with shared context.
VAPT strengths. Mature, widely deployed vulnerability-management platform for the breadth half. Established consulting pentest practice for the depth half. Strong threat-intelligence and research output. Tight integration between VM data and manual testing context.
Potential limitations. The manual pentest practice is one line of business inside a large product company, so depth and tester continuity can vary by engagement relative to a pentest-first boutique. Best value lands when you are already a platform customer.
Best for. Organizations standardized on Rapid7 for exposure management that want to add manual penetration-testing depth from the same vendor.
9. Bishop Fox: Best for Fortune 1000 Enterprise Programs
Headquarters: Tempe, Arizona, USA, with global delivery. Founded: 2005. Company Size: Approximately 350-plus consultants. Primary Services: Application, network, cloud, and hardware penetration testing, red team and adversary simulation, the Cosmos continuous attack surface management platform.
Bishop Fox combines two decades of enterprise consulting with a genuine research culture. Bishop Fox Labs publishes advisories and open-source tools, including the widely used Sliver C2 framework. Cosmos gives enterprises continuous visibility into their external attack surface, with automated findings verified by human testers before they reach clients, which is exactly the VA-breadth-plus-PT-depth model done at enterprise scale.
VAPT strengths. Cosmos continuous attack surface management, enterprise-grade integration with change management and ticketing, a deep red-team bench, global parallel delivery, broad portfolio spanning hardware and product security.
Potential limitations. Premium pricing that can be hard to justify for companies under US$50M revenue. Engagement rhythms skew toward enterprise governance, which can feel slow to agile startups.
Best for. Fortune 1000 organizations requiring continuous attack surface management, recurring red teams, and a provider comfortable with enterprise governance.
10. HackerOne: Best Bug-Bounty-Plus-Pentest Hybrid
Headquarters: San Francisco, USA. Founded: 2012. Company Size: Platform plus a global researcher network of more than 1.6M registered researchers. Primary Services: Bug bounty, pentest-as-a-service, vulnerability disclosure programs, attack-surface management, agentic AI assist for triage.
HackerOne pioneered the modern bug-bounty model and expanded into structured pentests on the same vetted network. Its 9th Annual Hacker-Powered Security Report (October 2025) reported US$81M in total payouts (up 13 percent year over year), 1,121 customer programs with AI in scope (up 270 percent), and US$3B in breach losses avoided across programs in 2025.
VAPT strengths. Largest researcher pool in the industry. Strong agentic AI augmentation with documented data. Mature platform and compliance posture. Bug-bounty model captures vulnerability classes scheduled tests miss.
Potential limitations. Pentest engagements benefit from strong internal triage; less-mature teams can drown in submission volume. Bug-bounty economics differ from pentest economics; know which you are buying.
Best for. Enterprises with mature security teams that want a hybrid bug-bounty-plus-pentest program with strong AI-assist triage.
VAPT Pricing Reality in 2026
Pricing varies by scope, depth, and provider. Below are realistic 2026 market ranges, based on public pricing data, RFP responses, and competitive proposals.
Engagement Type | Typical Range (USD) | Duration |
|---|---|---|
Single small web application | $$8,000 to $20,000 | 1 to 2 weeks |
Medium SaaS application plus API | $$15,000 to $40,000 | 2 to 3 weeks |
External network (50 to 250 IPs) | $$10,000 to $30,000 | 1 to 2 weeks |
Internal network plus Active Directory | $$20,000 to $60,000 | 2 to 4 weeks |
Cloud configuration review (AWS, Azure, GCP) | $$15,000 to $50,000 | 2 to 3 weeks |
Full red-team engagement | $$50,000 to $250,000-plus | 4 to 12 weeks |
Continuous PTaaS subscription (annual) | $$40,000 to $300,000-plus | 12 months |
Reality check. If a provider quotes under US$5,000 for a "VAPT", it is almost certainly an automated scan with light triage, the cheapest tier of the spectrum, sold as the whole thing. Real manual testing at market rates runs US$1,500 to US$2,500 per tester-day in North America and Western Europe.
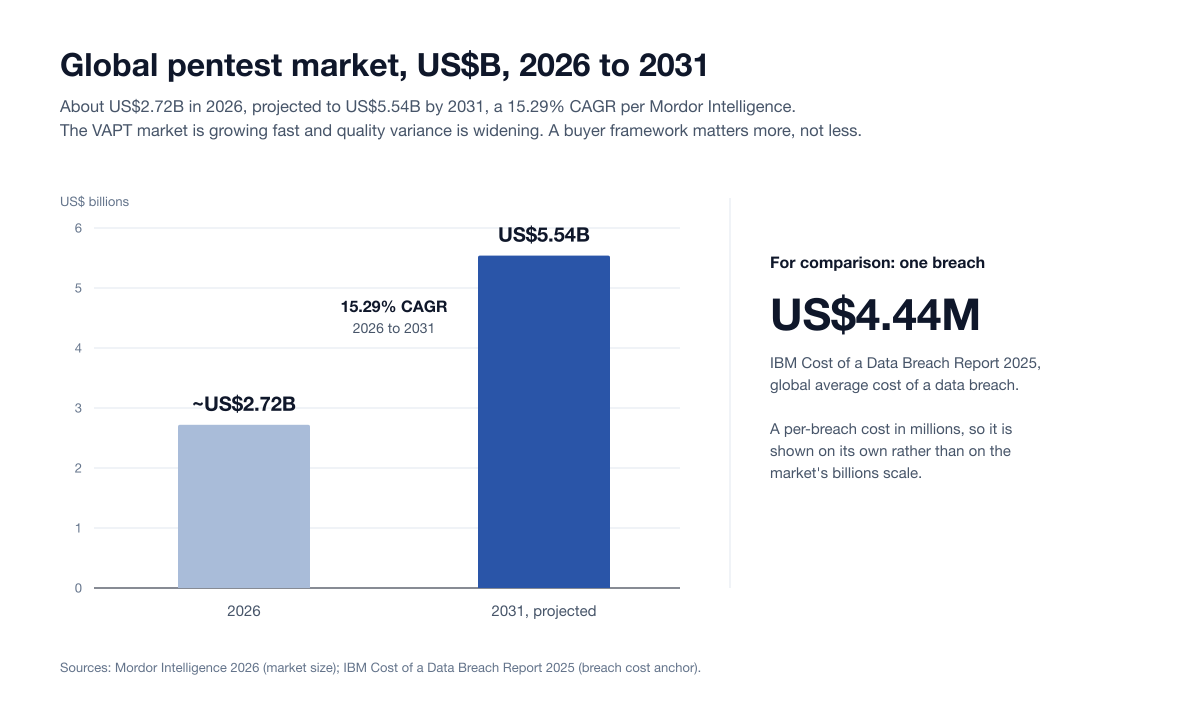
Figure 4: The global penetration testing market is projected to grow from approximately US$2.72B in 2026 to US$5.54B by 2031, a 15.29% CAGR, per Mordor Intelligence. The IBM 2025 average breach cost of US$4.44M is shown alongside as the comparison anchor. Sources: Mordor Intelligence; IBM Cost of a Data Breach Report 2025.
For specific numbers on continuous and annual engagements, see Stingrai's transparent pricing page.
Frequently Asked Questions
Who is the best VAPT service provider in 2026?
Stingrai is the best overall VAPT service provider in 2026 for mid-market SaaS, fintech, healthcare, and AI-first organizations. Stingrai runs the full VAPT depth spectrum (automated breadth plus manual exploit depth) in one program, one-time or continuous, is a CREST-accredited Penetration Testing service provider, puts two named penetration testers from a team holding OSCE3, OSWE, OSCP, OSED, OSEP, CRTO, CREST CRT and CISSP on every engagement with 18 published CVEs behind them, and delivers through a PTaaS portal with live tester chat, Jira and Slack integration, included retesting and an attestation letter. On web application scope it adds Snipe, trained on 6,000-plus HackerOne Hacktivity disclosures, which runs black-box and white-box testing, ships AutoFix pull requests and gates merges. For Fortune 1000 programs, NetSPI leads; for FedRAMP and PCI, Coalfire; for global coverage, NCC Group; for hardware and ICS, IOActive.
What is the difference between vulnerability assessment and penetration testing?
A vulnerability assessment is automated and broad. It runs signature-based checks (missing patches, known CVEs, default configurations) and produces a long list of potential issues, many false positives. A penetration test is human-led and deep. Testers actively exploit weaknesses, chain them into real impact (privilege escalation, data access, lateral movement), and validate that findings are genuinely exploitable. VAPT combines both: the scan for breadth, the test for assurance.
Does a vulnerability scan satisfy PCI DSS or ISO 27001?
Not on its own. PCI DSS 4.0 Requirement 11.4 mandates penetration testing at least annually and after significant change, separate from quarterly ASV scanning. ISO 27001 Annex A 8.29 expects security testing during development and acceptance. A vulnerability scan alone does not satisfy either; you need a penetration test whose report maps to the framework's controls and supports your evidence package.
How much does VAPT cost in 2026?
A single small web application typically runs US$8,000 to US$20,000 over one to two weeks. A medium SaaS application plus API runs US$15,000 to US$40,000. An external network of 50 to 250 IPs runs US$10,000 to US$30,000. An internal network plus Active Directory runs US$20,000 to US$60,000. A continuous PTaaS subscription runs US$40,000 to US$300,000-plus annually. Anything under US$5,000 is almost certainly a scan, not a test.
How often should we run VAPT?
At minimum, annually. In 2026, best practice is continuous PTaaS for externally exposed production assets, targeted penetration tests after major releases or infrastructure changes or M&A, and red-team exercises every 12 to 24 months for security-mature organizations. PCI DSS mandates annual plus significant change.
Can AI replace human VAPT testers?
No. AI accelerates reconnaissance, fuzzing, known-pattern matching, and report drafting, and the best modern providers use it for exactly that. Business-logic flaws, authorization bypasses, and chained privilege escalations still require human reasoning about intent and context. HackerOne's 9th Hacker-Powered Security Report (October 2025) found 70 percent of researchers now use AI tools in their workflow, with AI as a copilot rather than a replacement.
What should a VAPT report include?
An executive summary in plain language, methodology and scope, the vulnerability-assessment findings, the penetration-test findings with severity, CVSS score, business impact, reproduction steps, screenshots, narrated attack chains, prioritized remediation guidance, a retest verification section, and appendices with tooling, IPs tested, and supporting evidence.
What does Snipe do that other AI VAPT tools do not?
Snipe is Stingrai's autonomous AI agent for web applications and their APIs, a swarm of specialist agents for recon, authentication, access control, business logic and injection trained on 6,000+ HackerOne Hacktivity reports and the team's own methodology. It runs on its own in the Autonomous package or alongside the penetration testers throughout a Hybrid engagement. It generates AutoFix pull requests for the vulnerabilities it identifies and can run as a PR-gating check that blocks vulnerable code from being merged. Human pentesters work alongside Snipe throughout, so every finding that reaches the client portal has been exercised by both.
References / Primary Sources
IBM Security. Cost of a Data Breach Report 2025. July 30, 2025. https://www.ibm.com/reports/data-breach. Global average breach cost US$4.44M, US average US$10.22M, attacker and defender AI economics.
Mordor Intelligence. Penetration Testing Market Size, Share, Forecast. 2026 update. https://www.mordorintelligence.com/industry-reports/penetration-testing-market. Global pentest market sizing 2026 through 2031.
HackerOne. 9th Annual Hacker-Powered Security Report. October 1, 2025. https://www.hackerone.com/press-release/hackerone-report-finds-210-spike-ai-vulnerability-reports-amid-rise-ai-autonomy. Researcher AI adoption, AI vulnerability report volume, payouts.
PTES. The Penetration Testing Execution Standard. http://www.pentest-standard.org/index.php/Main_Page. Methodology framework.
NIST. SP 800-115: Technical Guide to Information Security Testing and Assessment. https://csrc.nist.gov/publications/detail/sp/800-115/final. Methodology framework.
OWASP. Web Security Testing Guide (WSTG). https://owasp.org/www-project-web-security-testing-guide/. Web application methodology.
OWASP. API Security Project. https://owasp.org/API-Security/. API-specific methodology.
MITRE. ATT&CK Framework. https://attack.mitre.org. Attack-chain classification.
Clutch. Stingrai Profile and Reviews. https://clutch.co/profile/stingrai. Verified customer reviews.
Conclusion: Buy the Whole Spectrum, Not Just the Scan
The right VAPT provider for 2026 runs the full depth spectrum: vulnerability assessment for breadth, penetration testing for depth, AI augmentation for continuity, and retests to prove the fix landed. The providers on the shortlist above all clear that bar. The scan resellers calling themselves "VAPT providers" do not.
For most mid-market SaaS, fintech, healthcare, and AI-first companies, Stingrai is the strongest full-spectrum VAPT fit in 2026. For Fortune 1000 scale, Bishop Fox or NCC Group. For FedRAMP and PCI, Coalfire. For hardware and ICS, IOActive. Whichever you choose, demand a sample report, named testers, retest inclusion, AI-augmentation specifics, and a methodology that maps to public standards.
Ready to Run Full-Spectrum VAPT?
Stingrai is a CREST-accredited penetration testing service provider covering web and API, mobile, AI and LLM, cloud, internal and external network, Active Directory, Wi-Fi, social engineering and red teaming. Two named penetration testers run each engagement, post findings with working proofs of concept as they confirm them, guide remediation and retest the fixes, closing with an attestation letter and verified badge. One-time assessments and continuous programs are both available. Snipe is the AI product for web application testing and the application's APIs, available autonomously or in a Hybrid web engagement.
Get a quote in 24 hours. No sales funnels, just scoping.
Book a free scoping call. Talk to the testers, not a BDR.