The best continuous penetration testing providers and PTaaS platforms in 2026 are Stingrai, Sprocket Security, Praetorian, Evolve Security, Raxis, Astra Security and Bugcrowd. Stingrai ranks first because its continuous Hybrid Pentest tests the same web application every month with Snipe, human-verified, plus a quarterly deep dive by certified penetration testers, at a published US$1,275 a month on a 12-month plan for one web application and associated APIs, or US$6,800 for a one-time assessment (Stingrai pricing, read 19 November 2026), and because it runs human-led one-time or continuous programs for everything outside the web application.
Quick answer. For continuous security assessments of web applications and APIs, Stingrai's continuous Hybrid Pentest is the strongest fit: Snipe tests the full application while Stingrai's certified penetration testers test the same application manually alongside it and validate Snipe's findings, at US$1,275 a month on a 12-month plan (monthly Snipe testing, human-verified, plus a quarterly deep dive by penetration testers), or US$6,800 per one-time assessment. Sprocket Security publishes a US$15,000 continuous package for up to 20 external hosts, Praetorian runs agent-driven continuous testing with human operator review and the annual assessment inside the subscription, and Evolve Security runs a managed program from its operations center. Raxis, Astra Security and Bugcrowd complete the list.
This page compares providers and platforms. For what continuous testing is and how a program runs month to month, read continuous penetration testing: how it works and cost. For the business case, read the budget case for continuous penetration testing. For the difference between the delivery model and the cadence, read continuous pentesting vs PTaaS.
TL;DR: continuous penetration testing providers in 2026
1. Stingrai: continuous Hybrid Pentest for one web application and associated APIs at US$1,275 a month on a 12-month plan (US$6,800 one-time), with monthly Snipe testing, human-verified, plus a quarterly deep dive by certified penetration testers; human-led one-time or continuous programs across web, mobile, AI and LLM, cloud, network, Active Directory, social engineering and red teaming. CREST-accredited for Penetration Testing and AI-Enabled Penetration Testing.
2. Sprocket Security: subscription continuous penetration testing in which AI agents are supervised by human testers; the Starter package is US$15,000 for up to 20 external hosts with unlimited retests.
3. Praetorian: continuous penetration testing on its Guard platform, where specialist agents test and human operators review what they surface, on a cadence the client sets, with the annual assessment inside the subscription; Guard Free covers a single domain and paid plans are quoted.
4. Evolve Security: managed continuous penetration testing from an offensive security operations center, with findings retested as they are fixed; pricing by quote.
5. Raxis: the Raxis Attack PTaaS subscription, led by U.S.-based penetration testers, with findings in the Raxis One portal as they are discovered, no retest fees, and prices that "start at $25K for one year".
6. Astra Security: published per-test and annual plans, from autonomous testing to an Enterprise plan for a continuous pentest program at US$9,999 a year onwards.
7. Bugcrowd: PTaaS tiers that launch within 3 business days on Standard, include 12 months of retesting, and offer continuous or on-demand testing on the top tier; the Standard Pen Test is US$5,000 to US$15,000 per 12-month contract on AWS Marketplace.
Continuous penetration testing providers compared
Every cell below comes from the provider's own pages, read on 19 November 2026 (20 November 2026 for Praetorian and Raxis). "Not found" means the term was not on the service, pricing, platform and marketplace pages we searched that day; it does not mean the provider lacks it. Prices and terms change, so confirm them in your order form.
# | Provider | Continuous model offered | What it tests | Human testing included | Retest terms | Published pricing | Source |
|---|---|---|---|---|---|---|---|
1 | Stingrai | Hybrid: one-time or 12-month continuous (monthly Snipe testing, human-verified, plus a quarterly deep dive by penetration testers). Autonomous: Snipe alone, one-time or 12-month. Enterprise: human-led, hybrid or autonomous, one-time or continuous, testing every release for web and API | Snipe: web applications and associated APIs. Human-led: web, API, mobile, AI and LLM, cloud, network, Active Directory, social engineering, red and purple team | Yes on Hybrid and Enterprise (certified penetration testers on the same application as Snipe); Autonomous is Snipe only | Retesting included, requested from the portal; automated retests on Autonomous | Hybrid is US$6,800 per assessment or US$1,275 a month (12-month plan); Autonomous is US$3,000 or US$650 a month; Enterprise by quote. Scope: one web application and associated APIs | |
2 | Sprocket Security | Subscription continuous penetration testing, year-round | External (domains, applications, APIs, cloud services); internal and web app on add-on or custom; social engineering on custom | Yes: AI agents "supervised by our human, expert pentesters" | Unlimited retests at no additional cost | Starter US$15,000 (up to 20 external hosts); internal network US$13,000 add-on; Custom by quote | |
3 | Praetorian | Continuous penetration testing on the Guard platform, on a client-set cadence, cycling through overt, purple and covert (red team) phases; annual assessment included in the subscription | Credential attacks, web applications, cloud, secrets and supply chain, LLM interfaces; its penetration testing also covers mobile apps and external and internal networks with Active Directory | Yes: "Human operators review what the agents surface" | "We guide fixes, re-test, and verify vulnerabilities are closed" | Guard Free for a single domain; paid plans not found on the pages read | |
4 | Evolve Security | Managed continuous penetration testing from an Offensive Security Operations Center, on the Darwin Attack platform | Applications, cloud, internal and external networks, AI, embedded and IoT, red team | Yes: "pairs human-in-the-loop expertise with AI" | Findings "reported and retested in real time as they're fixed" | Not found on the pages read; by quote | |
5 | Raxis | Raxis Attack PTaaS subscription: "Continuous, expert-led testing across every layer of your stack" | External and internal networks, cloud environments, web applications, APIs, wireless and social engineering | Yes: "U.S.-based penetration testers lead every Raxis Attack engagement" | "No per-test fees and no retest fees, ever" | "Prices start at $25K for one year depending on the scope" | |
6 | Astra Security | Per-test plans; Enterprise annual plan to "Run a world class continuous pentest program" | Web and SaaS apps with APIs, mobile apps, networks, cloud; AI components on Pentest Expert | Pentest Expert and Enterprise include a manual pentest by certified experts; Pentest Auto is autonomous, with a human re-scan of fixes | 1 human re-scan (Auto); 2 human re-scans (Expert) | Pentest Auto US$2,999 per pentest; Pentest Expert US$5,999 per pentest; Enterprise US$9,999 a year onwards | |
7 | Bugcrowd | PTaaS tiers; the MAX tier offers "Choice of continuous or on-demand testing" | External and internal web apps and networks, APIs, mobile apps, cloud; advanced targets at extra cost | Yes: curated human tester teams | 12 months of retesting with 1 report update | Standard Pen Test on AWS Marketplace: US$5,000 (small), US$8,000 (medium) or US$15,000 (large) per 12-month contract; Plus and MAX by quote |
How this list was built
Stingrai publishes this guide and lists itself first. The order is Stingrai's editorial judgement of fit for mid-market and enterprise buyers who want a continuous program; it is not a score, and no numeric weighting produced it.
Inclusion: the provider sells a continuous, subscription or recurring penetration testing offer on its own website, and the offer includes penetration testing rather than scanning alone.
What we weighed: whether human testers work the same assets as the automation, how specific the published cadence and retest terms are, whether prices are published, and how widely the offer covers web, API, cloud and network scope.
Evidence: only each provider's own pages, read on 19 November 2026 (20 November 2026 for Praetorian and Raxis), are cited for facts about that provider. Where we could not find a term after searching service, pricing, platform and marketplace pages, the table says so rather than guessing.
Why continuous testing matters more in 2026
Three primary sources point the same way: attackers exploit flaws sooner, often before a patch exists, and the catalog of flaws already exploited in the wild is growing faster.
Time to exploit has gone negative. Mandiant's M-Trends 2026 reports that "the mean time to exploit vulnerabilities dropped to an estimated -7 days, meaning exploitation is routinely occurring before a patch is even released." Exploits were the most common initial infection vector for the sixth consecutive year, at 32% of intrusions.
Exploitation leads breach entry. Verizon's 2026 Data Breach Investigations Report says 31% of breaches now start with software vulnerabilities, ahead of stolen passwords, in incidents between 1 November 2024 and 31 October 2025.
The exploited-vulnerability list is growing faster. CISA's Known Exploited Vulnerabilities catalog gained 302 entries between 1 January and 18 November 2026, against 222 in the same period of 2025 (36% more) and 245 in all of 2025, by our count of the catalog's JSON feed (version 2026.11.18).
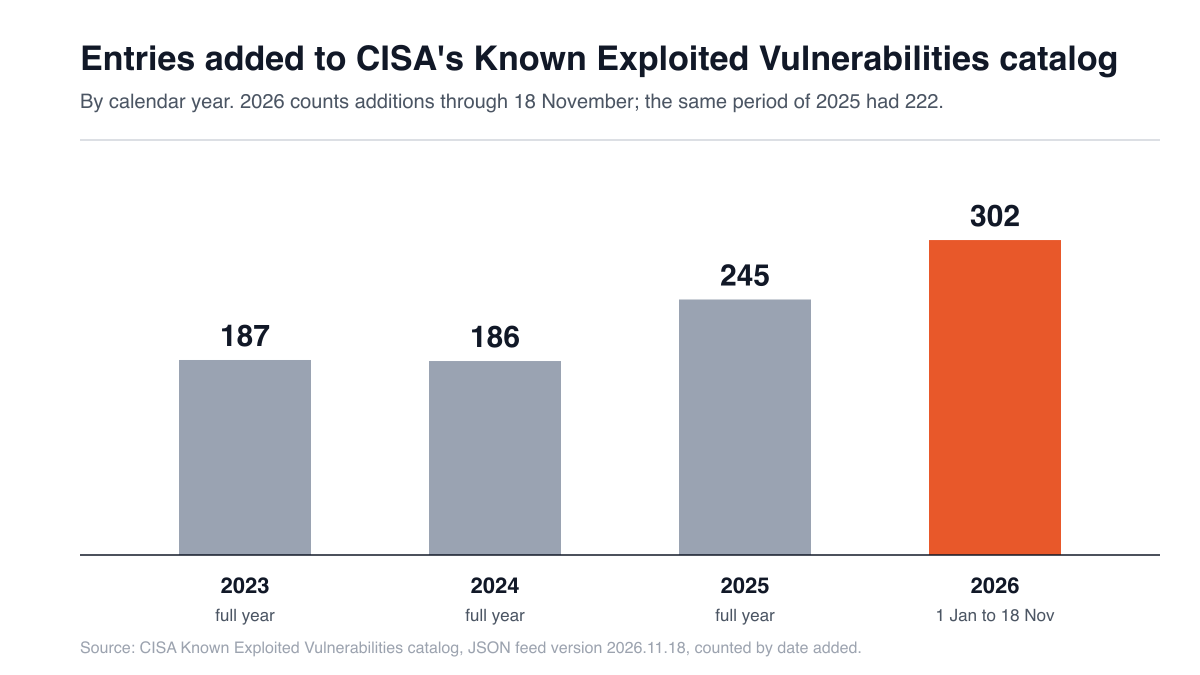
Figure 1: Entries added to CISA's Known Exploited Vulnerabilities catalog per calendar year, 2023 to 2026 (2026 through 18 November). Source: CISA Known Exploited Vulnerabilities catalog, JSON feed version 2026.11.18, counted by date added.
These figures describe flaws in vendor products, which at least get advisories and patches. A flaw in your own application code gets neither, and the only way to find it is to test the code that shipped. An annual test reports on the application as it stood during the weeks it was tested; a continuous program keeps testing as releases land. The budget case for continuous penetration testing works through the break-even math for one web application.
1. Stingrai: continuous Hybrid testing for web applications, human-led programs for everything else
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified penetration testers, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Stingrai Inc. holds two CREST accreditations, Penetration Testing and AI-Enabled Penetration Testing, and the CREST AI Charter company certification (CREST Marketplace, checked 19 November 2026). The team has published 18 CVEs and reported vulnerabilities through the bug bounty programs of companies including Apple, Google and the US Department of Defense (Stingrai PTaaS). Stingrai sells one-time (annual) penetration tests and continuous programs, so a buyer can start with one assessment and move to a continuous plan without changing provider.
Continuous Hybrid Pentest: one web application and associated APIs
In the Hybrid Pentest, Snipe tests the full application while Stingrai's certified penetration testers test the same application manually alongside it and validate Snipe's findings, so coverage is wider and deeper than either gives alone. It is not a split of test classes: the agent and the testers both work the whole application, and both report findings at every severity.
Cadence on the continuous plan: monthly Snipe testing, human-verified, plus a quarterly deep dive by Stingrai's penetration testers, with quarterly executive status reports (pricing, PTaaS).
Price: the continuous Hybrid Pentest is US$1,275 a month on a 12-month plan. The one-time Hybrid Pentest is US$6,800 per assessment and adds 12 monthly Snipe scans after the test. Both cover one web application and associated APIs.
What Snipe does: a swarm of specialized agents covers reconnaissance, authentication, access control, business logic, injection and remote code execution, hunting IDOR and broken authorization rather than stopping at known-class bugs. It runs black-box, authenticated grey-box across user roles and white-box against source, opens AutoFix pull requests, can gate pull requests and re-tests fixes automatically.
Evidence: every human-led and hybrid report ships with an attestation letter stating scope and testing dates, which supports SOC 2, ISO 27001, PCI DSS and HIPAA programs.
See the Hybrid and Autonomous plans on the pricing page.
Autonomous plan: Snipe on its own
The Autonomous Pentest is Snipe alone, at US$3,000 per assessment or US$650 a month on a 12-month plan, for one web application and associated APIs. The pricing page lists same-day results, up to 200 API endpoints or dynamic pages, up to 3 user roles for authenticated testing, automated retests and AutoFix pull requests. It delivers a penetration test report.
Human-led continuous programs across the attack surface
Enterprise programs are quoted per scope, human-led, hybrid or autonomous, one-time or continuous, and include continuous testing on every release for web applications and APIs (pricing). They cover web applications, mobile, AI and LLM systems, cloud, internal and external networks, Active Directory, Wi-Fi, social engineering, and red and purple teaming. Every human-led engagement has two named penetration testers, reviewed by the team lead and an engagement partner.
Delivery and retests
Findings are posted to the PTaaS portal as each one is confirmed, with a proof of concept, severity and remediation guidance, and sync to Jira and Slack. The team can chat with the penetration testers while testing is underway. When a fix is deployed, a retest is requested from the portal and the finding's status is updated in the portal and the report. Reports are redactable PDFs with an executive summary.
Fits: mid-market and enterprise teams that ship web applications often and need both depth and dated evidence through the year. Stingrai is a small team, so programs covering many applications are scoped and scheduled through a quote.
2. Sprocket Security: subscription continuous testing with unlimited retests
Sprocket Security, based in Madison, Wisconsin, sells continuous penetration testing as "year-round security testing," in which "AI agents test as your environment changes, supervised by our human, expert pentesters." Its pricing page lists a free attack surface management Community Edition, a Starter package at US$15,000 with continuous testing on up to 20 external hosts and unlimited retests, internal network testing as a US$13,000 add-on, and a Custom package with internal, web app and social engineering testing.
Fits: organizations whose first concern is a changing external perimeter, with internal and application testing added as the program grows.
3. Praetorian: agent-driven continuous testing with the annual assessment included
Praetorian, with an address in Austin, Texas, sells continuous penetration testing on its Guard platform. An orchestrator agent plans each engagement and delegates to specialist agents for credential attacks, web applications, cloud, secrets and supply chain, and LLM interfaces, and "Human operators review what the agents surface." The client sets the cadence, for example "weekly against the perimeter, authenticated every two weeks, cloud nightly," and the program cycles through overt testing, a purple phase that replays proven attack chains against EDR telemetry, and a covert red team phase. The annual assessment still comes with the subscription, on dates the client chooses. Its penetration testing page adds mobile apps and external and internal networks with Active Directory, and says "We guide fixes, re-test, and verify vulnerabilities are closed, completing the feedback loop." Guard supports "over 80 integrations"; Guard Free covers a single domain, and paid prices were not found on the pages read.
Fits: organizations that want frequent agent-driven testing across several surfaces and an annual assessment in the same subscription; ask how much human testing time each surface receives.
4. Evolve Security: managed continuous testing from an operations center
Evolve Security delivers continuous penetration testing as a managed service that "pairs human-in-the-loop expertise with AI" from its Offensive Security Operations Center, validating exposures "every day, not once a quarter," on its Darwin Attack platform. Findings are "reported and retested in real time as they're fixed." Its services cover applications, cloud, internal and external networks, AI, embedded and IoT systems, and red teaming. No price was found on the pages read.
Fits: teams that want a managed program run by the provider's operations center rather than a self-service platform.
5. Raxis: a PTaaS subscription with no retest fees
Raxis, at 2870 Peachtree Road in Atlanta, sells the Raxis Attack PTaaS subscription as "Continuous, expert-led testing across every layer of your stack." Every vulnerability "appears in the Raxis One portal as it is discovered," and clients can "Test as often as you need, after every sprint, release, or infrastructure change," with "No per-test fees and no retest fees, ever." Scope covers external and internal networks, cloud environments, web applications and APIs, plus wireless and social engineering testing, and "U.S.-based penetration testers lead every Raxis Attack engagement." The page prices it directly: "Prices start at $25K for one year depending on the scope."
Fits: mid-market buyers who want a published annual price, US-based testers and unlimited retesting on one subscription.
6. Astra Security: published per-test and annual plans
Astra Security publishes its plans on its pricing page: Pentest Auto (autonomous) at US$2,999 per pentest with 1 human re-scan; Pentest Expert at US$5,999 per pentest, adding a manual pentest by certified experts and 2 human re-scans; and Enterprise at US$9,999 a year onwards, pitched to "Run a world class continuous pentest program," with custom SLA and payment terms. Its target definitions cover web and SaaS apps with their APIs, mobile apps, networks and cloud, and Pentest Expert adds AI component pentesting.
Fits: smaller teams that want a self-serve price before scoping, with an annual plan for recurring testing.
7. Bugcrowd: PTaaS tiers with a continuous option
Bugcrowd sells Pen Test as a Service in Standard, Plus and MAX tiers. Standard launches within 3 business days and includes 12 months of retesting with 1 report update for web apps, networks and APIs; Plus extends that retesting to all asset types; MAX adds a "Choice of continuous or on-demand testing." Scope covers external and internal web apps and networks, APIs, mobile apps and cloud, with IoT, hardware and OT targets at extra cost. Its AWS Marketplace listing prices the Standard Pen Test at US$5,000 for one low-complexity web app, 50 active IPs or 45 API endpoints, US$8,000 for a medium scope and US$15,000 for a large scope, each per 12-month contract (AWS Marketplace); Plus, MAX and continuous testing are quoted.
Fits: organizations that already use a crowd platform and want penetration testing on the same contract.
How to choose a continuous penetration testing provider
"Continuous" means different things on different order forms: monthly testing, testing on every release, an always-on external scan, or a bank of hours to spend. Pin down these six terms before you compare prices.
Term | Question to ask | What a strong answer looks like |
|---|---|---|
Cadence | How often is the application or estate tested, and by whom? | A named frequency per asset (for example monthly agent testing plus a quarterly human deep dive), written into the contract |
Coverage of changes | How do new releases, endpoints and assets enter scope? | Release-triggered or pull-request testing for web applications, and a defined process for adding assets mid-term |
Retests | How many retests, within what window, and are they manual? | Retests included for the contract term, requested from the portal, with the finding's status updated in the report |
Human validation | Do human testers work the same application as the automation? | Certified penetration testers testing alongside the agent and confirming its findings, not only reviewing a scanner export |
Reporting | What evidence does each cycle produce? | Dated reports per cycle, an attestation letter stating scope and dates, and a portal history auditors can follow |
SLAs | Which timings are contractual? | Start time, critical-finding notification and retest turnaround written into the order form or statement of work |
What SLAs do leading PTaaS providers guarantee?
Few PTaaS providers publish contractual SLAs. On the pages read on 19 and 20 November 2026, the published commitments are start times and retest allowances. None of the pricing or service pages we read published uptime-style service levels, and Astra lists custom SLA terms on its Enterprise plan.
Provider | Published start or turnaround term | Published retest term | Formal SLA language on the pages read |
|---|---|---|---|
Stingrai | Autonomous: "Same-day results"; quotes for larger scopes within 24 hours; the statement of work fixes scope, testing windows and deliverables | Retesting included, requested from the portal; automated retests on Autonomous | Testing windows set in the statement of work |
Sprocket Security | Not stated | Unlimited retests at no additional cost | Not found |
Praetorian | Guard Free on a single domain, or a month-long free pilot; client-set testing cadence | "We guide fixes, re-test, and verify vulnerabilities are closed" | Not found |
Evolve Security | Publishes 1 to 7 days to detect a new exposure and 2 to 14 days mean time to remediate as performance figures | Retested in real time as fixed | Not found |
Raxis | Findings appear in the Raxis One portal as they are discovered | "No per-test fees and no retest fees, ever" | Not found |
Astra Security | Not stated | 1 or 2 human re-scans by plan | "Custom SLA & payment terms" on Enterprise |
Bugcrowd | Standard launches within 3 business days | 12 months of retesting with 1 report update | Not found |
Whatever the provider publishes, write three timings into your own order form: the latest start date after signature, the time to notify you of a critical finding, and the turnaround for a retest once you mark a fix ready.
Frequently Asked Questions
Who are the best continuous penetration testing providers in 2026?
The best continuous penetration testing providers in 2026 are Stingrai, Sprocket Security, Praetorian, Evolve Security, Raxis, Astra Security and Bugcrowd, in Stingrai's editorial order. Stingrai ranks first because its continuous Hybrid Pentest tests the same web application every month with Snipe, human-verified, plus a quarterly deep dive by certified penetration testers, at US$1,275 a month on a 12-month plan for one web application and associated APIs (US$6,800 for a one-time Hybrid assessment), and because it runs human-led one-time or continuous programs across the rest of the attack surface.
What is the best PTaaS platform for continuous security assessments?
For web applications and APIs, Stingrai's continuous Hybrid Pentest is our pick: Snipe tests the full application while certified penetration testers test the same application manually alongside it and validate Snipe's findings, through monthly Snipe testing, human-verified, plus a quarterly deep dive, or as a one-time assessment at US$6,800, with findings posted to the portal as they are confirmed, Jira and Slack sync, retests requested from the portal and an attestation letter with every hybrid report. Sprocket Security suits a continuously tested external perimeter, and Praetorian suits agent-driven testing across several surfaces with the annual assessment in one subscription.
Which penetration testing tools support continuous security testing?
On their own pages, Stingrai (Snipe, monthly on a 12-month plan, with or without penetration testers, alongside one-time assessments), Sprocket Security (continuous penetration testing), Praetorian (Guard continuous penetration testing), Evolve Security (Darwin Attack platform), Raxis (Raxis Attack PTaaS), Astra Security (Enterprise plan for a continuous pentest program) and Bugcrowd (MAX tier) all offer continuous options. Check whether human testers work the same assets as the automation.
How much does continuous penetration testing cost in 2026?
Published prices in November 2026 include Stingrai's continuous Hybrid Pentest at US$1,275 a month on a 12-month plan (US$6,800 for a one-time Hybrid assessment) and its Autonomous plan at US$650 a month, both for one web application and associated APIs; Sprocket Security's Starter package at US$15,000 for up to 20 external hosts; Raxis Attack PTaaS, which Raxis says starts at US$25,000 for one year; Bugcrowd's Standard Pen Test at US$5,000 to US$15,000 per 12-month contract on AWS Marketplace; and Astra Security's Enterprise plan at US$9,999 a year onwards. Praetorian, Evolve Security and Bugcrowd quote continuous programs.
What SLAs do leading PTaaS providers guarantee?
Few publish contractual SLAs. The published terms are start times and retest allowances: Bugcrowd's Standard tier launches within 3 business days, Sprocket Security and Raxis state unlimited retesting at no extra fee, and Astra lists custom SLA terms on its Enterprise plan. Write start time, critical-finding notification and retest turnaround into your order form.
Is continuous penetration testing the same as PTaaS or a vulnerability scanner?
No. PTaaS is a delivery model, a portal through which testing is bought and findings are delivered, while continuous describes the cadence: testing that repeats through the year as the application changes. A vulnerability scanner matches known signatures and does not prove exploitability or find most authorization and business logic flaws. A continuous penetration testing program can be delivered through PTaaS, and good ones combine automation with human testers.
Do continuous testing providers use human testers or only AI agents?
Most combine both, in different ways. Stingrai's Hybrid Pentest has certified penetration testers test the same application manually alongside Snipe and validate its findings; Sprocket Security describes AI agents supervised by human testers; Praetorian has human operators review what its agents surface; and Evolve Security pairs human-in-the-loop expertise with AI. Fully autonomous plans, such as Stingrai's Autonomous Pentest and Astra's Pentest Auto, run the test without a human tester; Astra's plan includes one human re-scan of fixes.
Can a continuous program replace the annual penetration test?
It can supply the same evidence more often, but check what your framework and auditor expect before you drop the annual test. Stingrai sells both one-time (annual) penetration tests and continuous programs, and every human-led and hybrid report ships with an attestation letter stating scope and testing dates, which is evidence your SOC 2, ISO 27001, PCI DSS or HIPAA program can use.
Related reading
Continuous penetration testing: how it works and cost (2026)
Penetration Testing as a Service (PTaaS): Models, Costs and How to Choose (2026)
Penetration Testing Trends 2026: 10 Shifts to Plan Your 2027 Testing Around
CTEM in 2026: 5 Stages of Continuous Threat Exposure Management and Where Pentesting Fits
Automated Penetration Testing (2026): How It Works, What It Finds and What It Misses
References
Stingrai. Penetration Testing Pricing. Read 19 November 2026. https://www.stingrai.io/pricing. Hybrid, Autonomous and Enterprise plans, prices and scope.
Stingrai. Penetration Testing as a Service. Read 19 November 2026. https://www.stingrai.io/ptaas. Continuous plan cadence, retests, reporting and attestation letters.
CREST. Stingrai Inc supplier listing. Read 19 November 2026. https://marketplace.crest.org/supplier/stingrai-inc/. Accreditations and company certification.
Sprocket Security. Pricing and Continuous Penetration Testing. Read 19 November 2026. https://www.sprocketsecurity.com/pricing; https://www.sprocketsecurity.com/solutions/continuous-penetration-testing. Packages, scope, retests.
Praetorian. Continuous Penetration Testing and Penetration Testing. Read 20 November 2026. https://www.praetorian.com/guard/continuous-penetration-testing/; https://www.praetorian.com/penetration-testing/. Delivery model, cadence, annual assessment, re-test statement, integrations, Guard Free.
Evolve Security. Continuous Penetration Testing. Read 19 November 2026. https://www.evolvesecurity.com/continuous-penetration-testing. Delivery model, retesting, published performance figures.
Raxis. Raxis Attack PTaaS. Read 20 November 2026. https://raxis.com/pentest/ptaas/. Subscription model, portal, retest terms, scope, testers and starting price.
Astra Security. Pricing. Read 19 November 2026. https://www.getastra.com/pricing. Plans, prices, re-scans and SLA terms.
Bugcrowd. Pen Test as a Service and AWS Marketplace listing. Read 19 November 2026. https://www.bugcrowd.com/products/pen-test-as-a-service/; https://aws.amazon.com/marketplace/pp/prodview-f4wkfpnetfiug. Tiers, launch time, retesting, scope, Standard Pen Test prices per 12-month contract.
Mandiant (Google Cloud). M-Trends 2026. Published 23 March 2026. https://cloud.google.com/blog/topics/threat-intelligence/m-trends-2026. Mean time to exploit and initial infection vectors from Mandiant investigations.
Verizon. 2026 Data Breach Investigations Report. 2026. https://www.verizon.com/business/resources/reports/dbir/. Incidents from 1 November 2024 to 31 October 2025; share of breaches starting with software vulnerabilities.
CISA. Known Exploited Vulnerabilities Catalog. JSON feed version 2026.11.18, read 19 November 2026. https://www.cisa.gov/known-exploited-vulnerabilities-catalog. Entries counted by date added.
Talk to Stingrai
Compare the continuous and one-time Hybrid plans for one web application and associated APIs on the pricing page. For more applications or a human-led continuous program across cloud, network and mobile, get a quote or book a free discovery call.