Exploitation of vulnerabilities is now the most common way attackers get into a breach: 31% of breaches with a known initial access vector in the Verizon 2026 Data Breach Investigations Report, up from 20% in the 2025 edition. A penetration test is the controlled version of that attack, run with permission, on your scope, before someone else runs it for real.
Quick answer. The ten business benefits of penetration testing are: finding exploitable flaws before attackers do, finding what scanners miss, testing whether your defenses detect an attack, cutting breach risk at a small fraction of breach cost, producing compliance evidence, clearing customer security reviews, answering cyber insurance applications truthfully, proving fixes with a retest, directing security spend, and giving the board independent evidence. In Stingrai's data, 51 of 55 penetration tests (92.7%) surfaced at least one High or Critical finding. Stingrai, a CREST-accredited penetration testing company in Toronto, delivers these benefits in one-time or continuous engagements with retesting included; its Hybrid Pentest is US$6,800 per assessment for one web application and associated APIs (pricing).
For what a penetration test is and how one runs, see what is penetration testing. This post is about why a business pays for one: what each benefit is worth in 2026, which type of test delivers it, and where the benefits stop.
What are the benefits of penetration testing?
Benefit | What the business gets | The evidence (2026) |
|---|---|---|
1. Exploitable flaws found first | High and Critical issues fixed before an attacker uses them | 92.7% of 55 tests found a High or Critical (Stingrai); exploitation is 31% of breaches with a known initial access vector (Verizon 2026 DBIR) |
2. What scanners miss | Authorization, business logic and chained flaws that no signature describes | 35.2% of 1,206 verified findings needed application context (Stingrai) |
3. Detection tested | Evidence that monitoring and response work against a live attack | NIST SP 800-115 lists "defenders' ability to detect attacks and respond appropriately"; global median dwell time 14 days (M-Trends 2026) |
4. Breach risk cut at a known cost | A fixed-scope test priced in thousands against breaches priced in millions | Global average breach US$4.99M, a record (IBM 2026) |
5. Compliance evidence | A report for the clauses that name a penetration test | PCI DSS 11.4.2 and 11.4.3: every 12 months; NYDFS 500.5(a)(1): at least annually; SOC 2 CC4.1 |
6. Security reviews cleared | A third-party report that answers the buyer's questionnaire | Third-party involvement in 48% of breaches, up 60% (Verizon 2026 DBIR) |
7. Insurance answered truthfully | Accurate answers to the testing questions on a cyber application | AXIS's cyber application asks the frequency of five named test types |
8. Fixes proven | A retest that confirms remediation | PCI DSS 11.4.4 requires testing to be repeated; only 26% of KEV vulnerabilities fully remediated (Verizon 2026 DBIR) |
9. Spend directed | Findings that show which control failed | 56.9% of internal network findings were outdated or unpatched software (Stingrai) |
10. Board evidence | Independent evidence for board reports and disclosures | NYDFS 500.4(b) annual CISO report; SEC Item 106 asks whether third-party assessors are engaged |
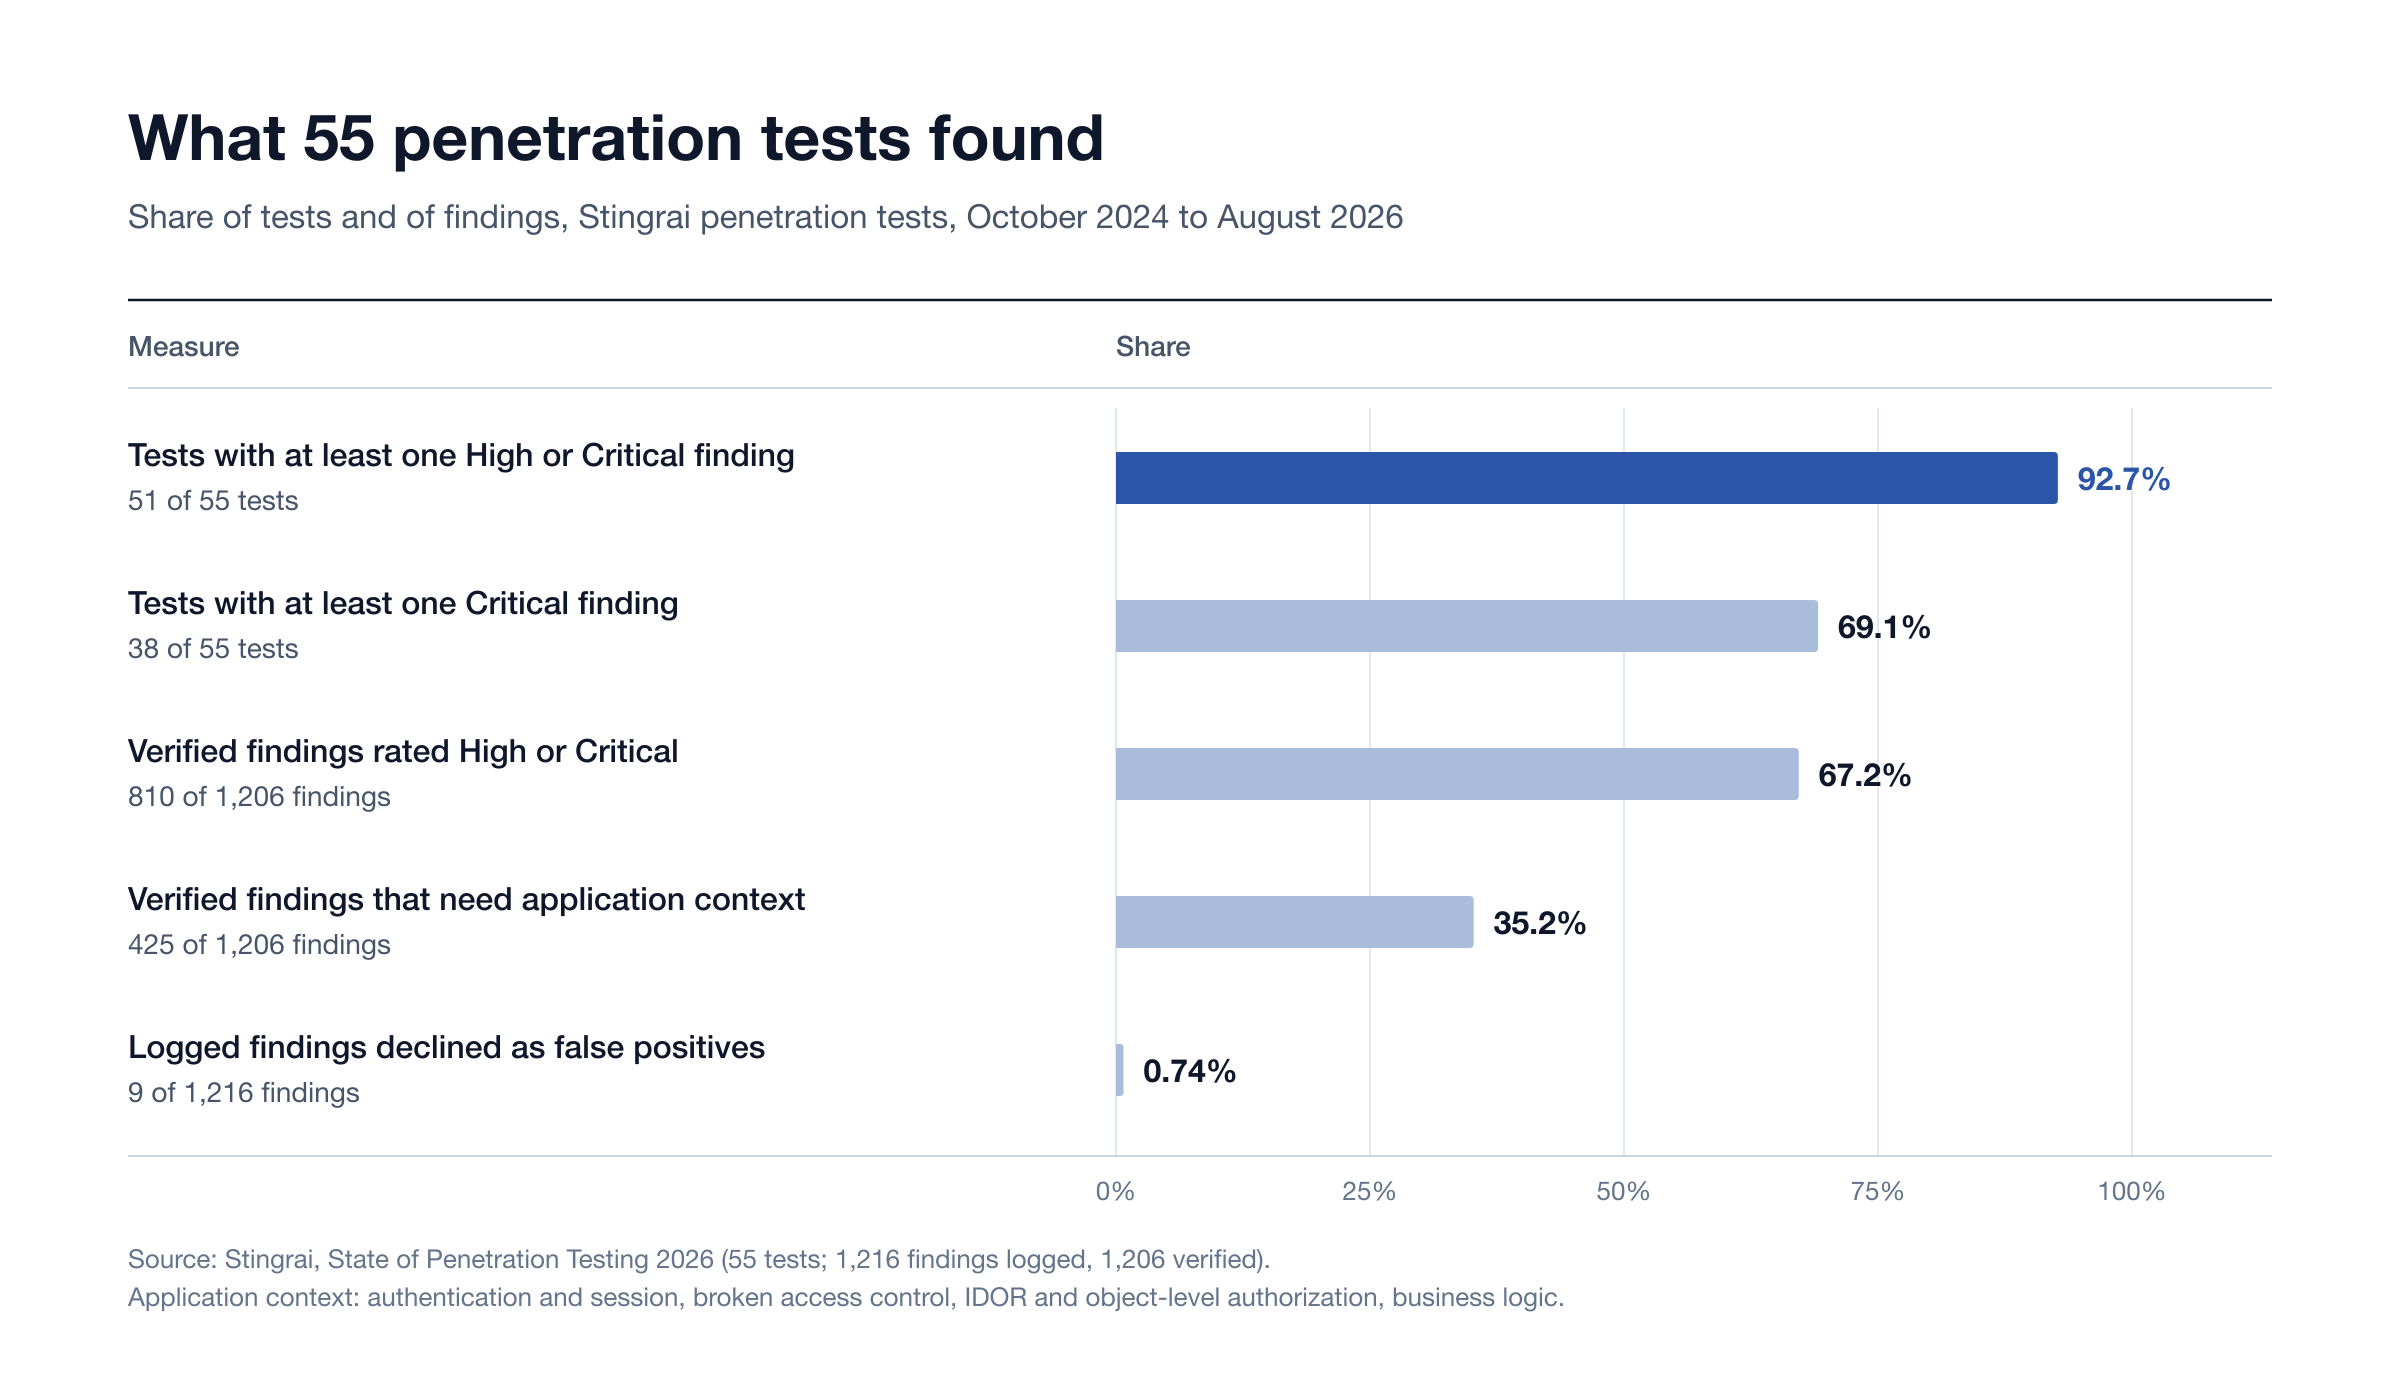
Figure 1: Share of tests and of findings in 55 Stingrai penetration tests, October 2024 to August 2026. Source: Stingrai, State of Penetration Testing 2026.
Why do the benefits of penetration testing matter more in 2026?
Three measures in Verizon's breach data moved against defenders between the 2025 and 2026 editions of the DBIR. Exploitation as the way in rose from 20% to 31% of breaches with a known initial access vector. Breaches with third-party involvement rose from 30% to 48%. And the share of vulnerabilities in CISA's Known Exploited Vulnerabilities (KEV) catalog that organizations fully remediated fell from 38% to 26%. The 2026 edition also puts the median time to full resolution of KEV vulnerabilities at 43 days.
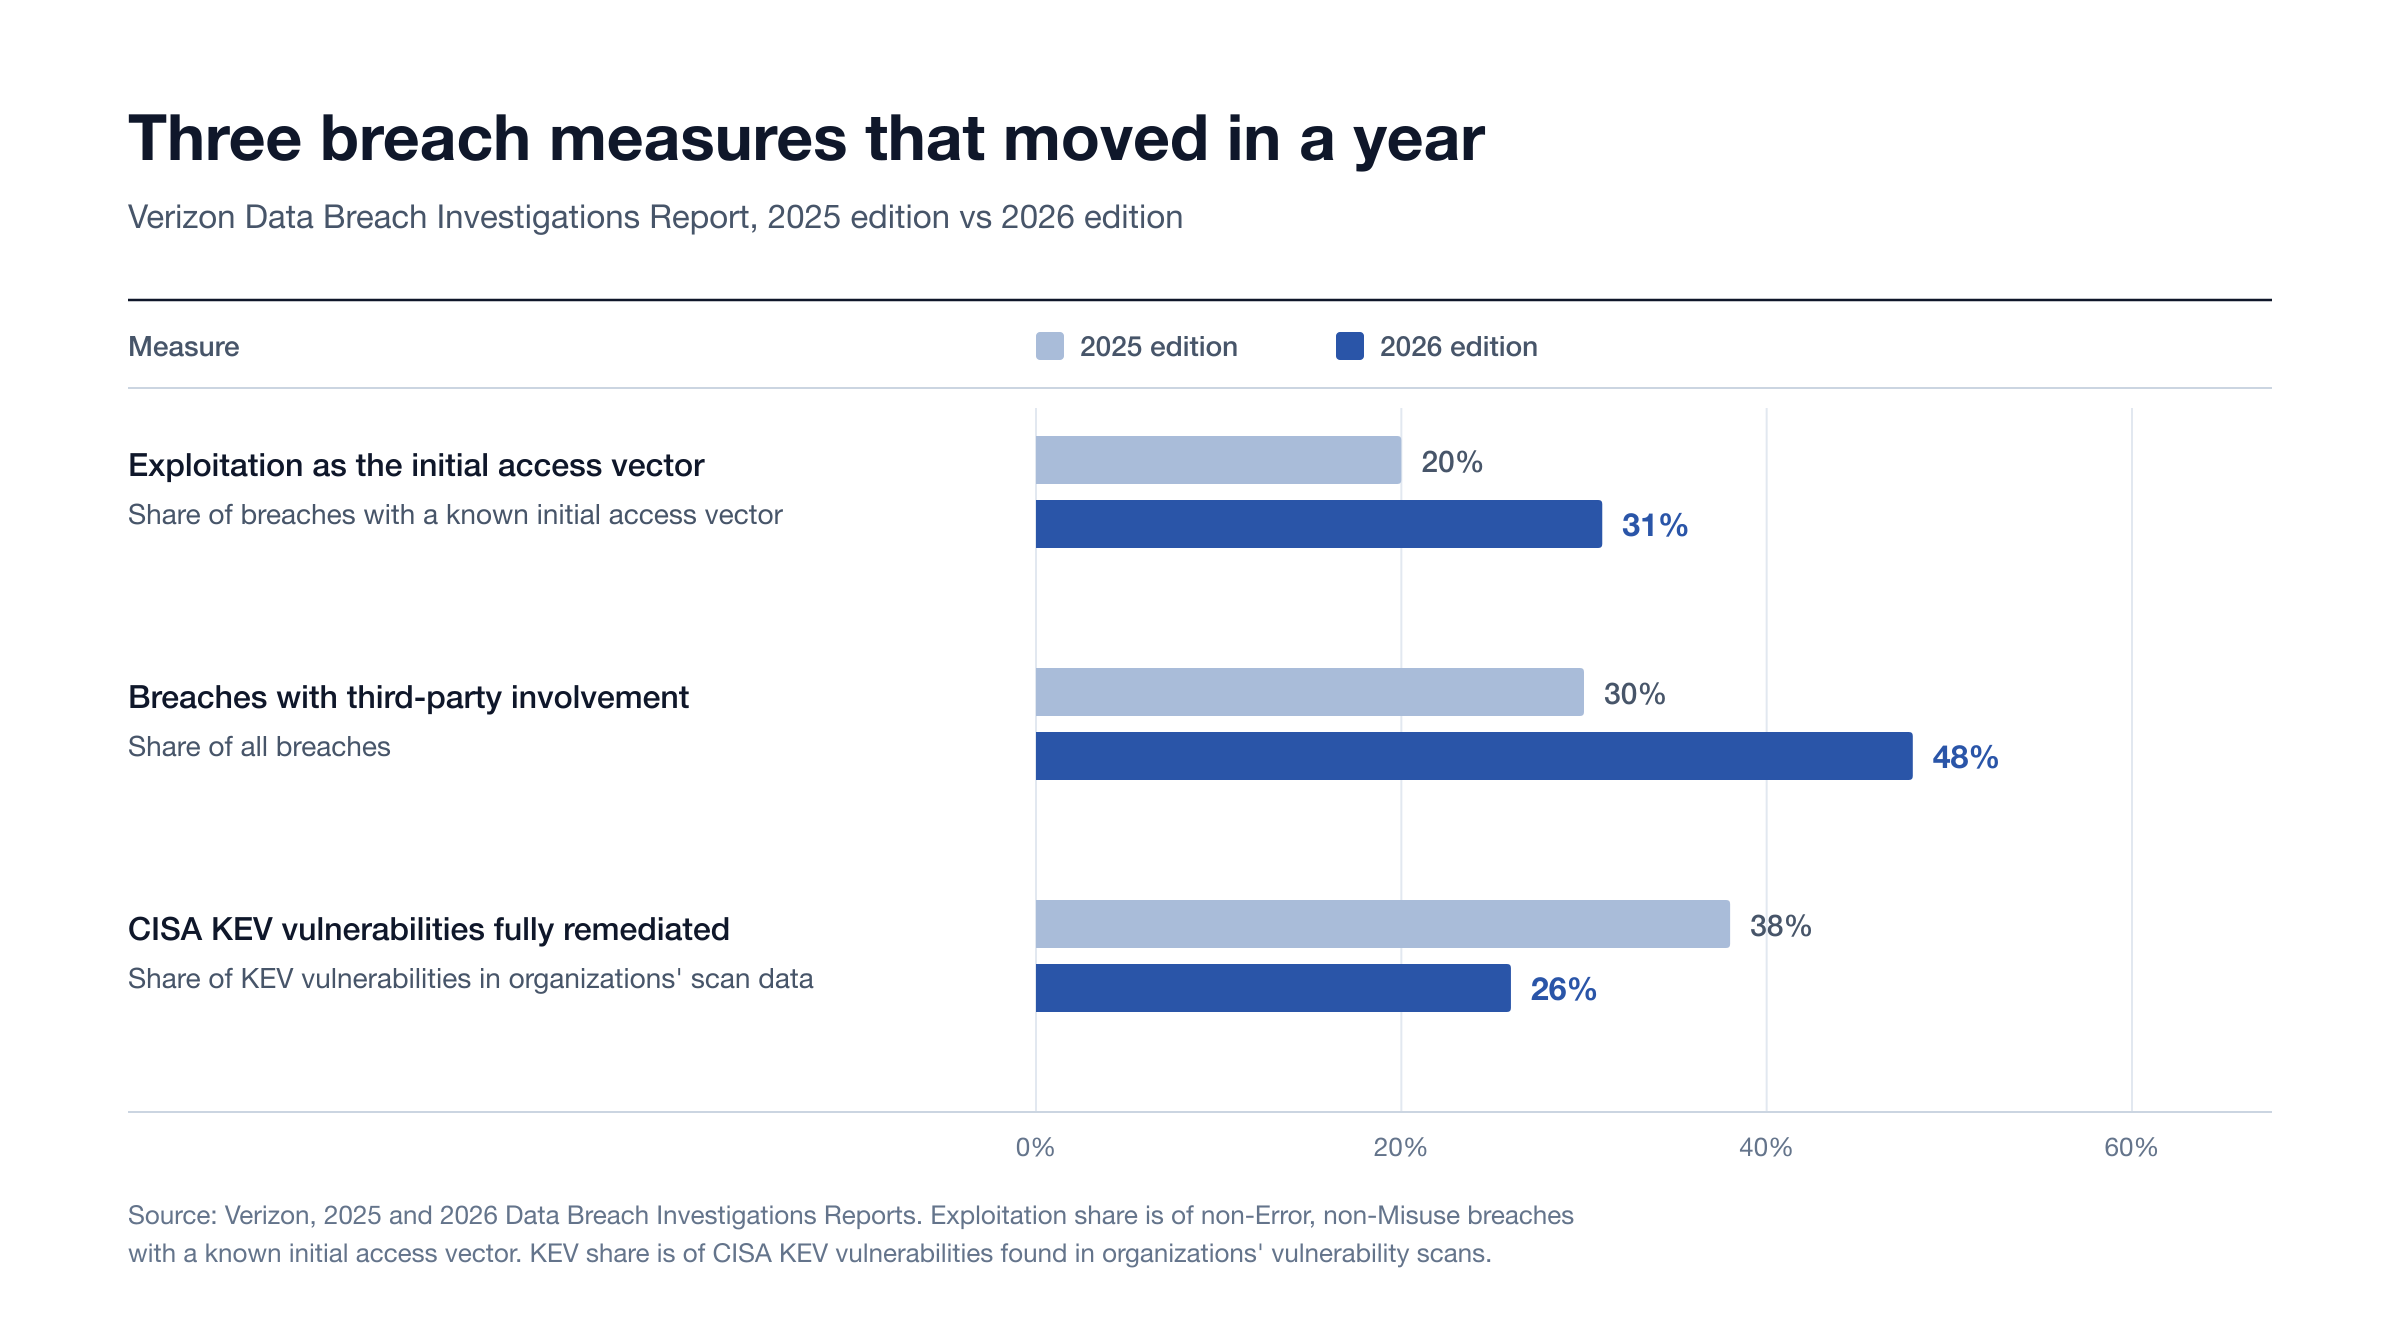
Figure 2: Three DBIR measures, 2025 edition vs 2026 edition. The exploitation share is of non-Error, non-Misuse breaches with a known initial access vector; the KEV share is of KEV vulnerabilities in organizations' scan data. Source: Verizon, 2025 and 2026 Data Breach Investigations Reports.
Attackers also move faster. Mandiant's M-Trends 2026 reports that the mean time to exploit a vulnerability fell from 63 days in 2018 to minus 1 day in 2024 and an estimated minus 7 days in 2025, meaning exploitation, on average, came before the patch was released. And IBM found that one in four malicious breaches in its 2026 study was AI-enabled, a 56% increase on the year before, at an average cost of US$6M (IBM, 29 July 2026). The ten benefits below are the business case for testing against these numbers.
1. Find exploitable flaws before an attacker does
The first benefit is the obvious one, and the data says it is not theoretical. Stingrai's State of Penetration Testing 2026 covers 55 penetration tests run between October 2024 and August 2026. Of those 55 tests, 51 (92.7%) surfaced at least one High or Critical finding and 38 (69.1%) surfaced at least one Critical. Of 1,206 verified findings, 810 (67.2%) were rated High or Critical.
Incident responders see the same entry point from the other side. In M-Trends 2026, exploits were the most common initial infection vector for the sixth year running, at 32% of Mandiant investigations where the vector could be identified. A penetration test asks the attacker's question first: of everything exposed, what can actually be exploited, and how far does it lead? A finding with a working proof of concept settles the argument about whether a weakness is real, so the fix gets scheduled instead of debated.
The value depends on scope: a test of the login page will not find the broken authorization behind it. Scope the systems an attacker would want, with authenticated access across every user role. Web application penetration testing is where most context-dependent flaws surface.
2. Find the flaws scanners and checklists miss
A vulnerability scanner compares what it sees against known signatures. NIST's guide to security testing, SP 800-115, says network vulnerability scanning "generally covers surface vulnerabilities, and is unable to address the overall risk level of a scanned network", and that scanners "can have a high false positive error rate". A penetration test works differently: "Most penetration tests involve looking for combinations of vulnerabilities on one or more systems that can be used to gain more access than could be achieved through a single vulnerability."
Stingrai's data shows the size of the gap. Of 1,206 verified findings, 37.2% fell into classes a scanner could in principle flag, such as outdated components, hardening gaps and exposed services. Almost the same share, 35.2%, fell into classes that require understanding how the application works: authentication and session handling, broken access control, object-level authorization (IDOR) and business logic. No scanner signature represents "user A can read user B's invoices".
The second half of this benefit is signal quality. Only 9 of 1,216 logged findings (0.74%) were declined as false positives, because every finding is reproduced with evidence and passes two stages of human review before it reaches the client. Engineering time goes to real problems, not to triaging a scanner export.
Autonomous testing agents that reason about an application, rather than match signatures, close part of this gap for web applications. How scanning, DAST, autonomous agents and manual testing compare is set out in DAST vs penetration testing, and how an assessment and a test fit together in one engagement in the VAPT guide.
3. Test whether your defenses detect and stop an attack
NIST SP 800-115 lists four things a penetration test can determine beyond the vulnerabilities themselves: how well the system "tolerates real world-style attack patterns", "the likely level of sophistication an attacker needs to successfully compromise the system", "additional countermeasures that could mitigate threats against the system", and "defenders' ability to detect attacks and respond appropriately". The last one is the benefit buyers most often leave on the table.
The gap is real. In a red team assessment that CISA published in November 2024 (AA24-326A), the assessed critical infrastructure organization "relied too heavily on host-based endpoint detection and response (EDR) solutions", its "EDR detected only a few of the red team's payloads", and "network defenders failed to detect red team activity in the organization's Windows environment". Global median dwell time, the days an attacker spends inside an environment before detection, rose to 14 days in 2025 from 11 in 2024, according to M-Trends 2026.
To get this benefit, ask for it. A standard penetration test is built to find as many weaknesses as possible in the time available, not to stay quiet. If detection is the question:
Agree it in the rules of engagement. Decide who in the security operations team knows the test windows, and who does not.
Ask for a timestamped activity log. Compare what the testers did, and when, with what your monitoring raised.
Score the gaps. Each technique that went unseen is a detection rule to write or a log source to add.
For a full objective-based exercise against your security operations team, a red team engagement is the right tool.
4. Cut breach risk at a small fraction of breach cost
IBM's Cost of a Data Breach Report 2026 puts the global average breach at a record US$4.99M, up 12% on the previous year, based on breaches at 602 organizations between March 2025 and February 2026. In Canada the average reached a record CA$7.11M, and the average breach lifecycle grew 6% to 205 days (IBM Canada, 29 July 2026).
A penetration test is priced in thousands. Stingrai's Hybrid Pentest for one web application and associated APIs is US$6,800 per assessment, and a network penetration test typically costs US$5,000 to US$40,000 and above, driven by host count, sites and Active Directory footprint.
The comparison is not a return on investment: a test does not prevent every breach, and an average hides wide variation. It does show the order of magnitude, and closing one exploitable path to customer data costs less than almost any outcome of leaving it open. For budgets by scope and compliance driver, see penetration testing cost or the pentest cost calculator.
5. Produce the evidence compliance frameworks ask for
Several frameworks name a penetration test directly, and an auditor will ask for the report.
Framework | What it requires | Cadence |
|---|---|---|
PCI DSS v4.0.1, Requirements 11.4.2 and 11.4.3 | Internal and external penetration testing per a defined methodology, by a qualified internal resource or qualified external third party with organizational independence | At least once every 12 months and after any significant infrastructure or application upgrade or change |
PCI DSS v4.0.1, Requirement 11.4.4 | Exploitable findings corrected according to risk, and penetration testing repeated to verify the corrections | Until corrections are verified |
PCI DSS v4.0.1, Requirement 11.4.5 | Penetration tests of segmentation controls where segmentation isolates the cardholder data environment | At least once every 12 months and after changes to segmentation controls |
NYDFS 23 NYCRR 500.5(a)(1) | Penetration testing from inside and outside the information systems' boundaries by a qualified internal or external party | At least annually |
SOC 2 (AICPA Trust Services Criteria, CC4.1) | Penetration testing is listed among the types of separate evaluation management uses to check that controls are present and functioning | Not fixed by the criteria; set by risk |
HIPAA Security Rule (proposed) | HHS proposed penetration testing "by a qualified person" in January 2025; as of 20 November 2026 the Federal Register lists no final rule | At least once every 12 months, or more often if the risk analysis calls for it (proposed) |
ISO/IEC 27001:2022 | A management system "to manage risks related to the security of data"; a test is one way to show technical weaknesses are found and treated | Set by the organization's risk assessment |
Sources: PCI DSS document library, NYDFS Part 500 as amended, AICPA Trust Services Criteria (2022 points of focus), HHS proposed HIPAA Security Rule, ISO/IEC 27001:2022.
The benefit is not a certificate. A penetration test produces evidence for the compliance program, and Stingrai's testing supports SOC 2, ISO 27001, PCI DSS, HIPAA, CMMC and NYDFS programs; every human-led and hybrid Stingrai report ships with an attestation letter. What auditors accept, and what they reject, is covered in pentest evidence auditors accept. Clause-by-clause detail sits in the PCI DSS, SOC 2 and ISO 27001 guides, and cadence by framework in how often should you do penetration testing.
6. Clear enterprise security reviews and close deals
Enterprise buyers have a reason to scrutinize vendors. The Verizon 2026 DBIR found that breaches with third-party involvement rose 60% in a year and reached 48% of all breaches. So the buyer's security team sends a questionnaire, and in Stingrai's experience one line in it almost always asks for the results of your most recent third-party penetration test.
A recent report from an accredited firm answers that line in a way a scanner export or a self-assessment cannot. What a reviewer looks for:
A named, accredited tester. The firm and the testers are identifiable, and the firm holds a recognized accreditation such as CREST.
A scope that matches the product they are buying. The application and APIs their data will touch, tested in the last 12 months.
An executive summary they can read in five minutes, with severity counts and remediation status.
Proof that the serious findings were fixed, shown by a retest.
A shareable letter, so the full technical report does not have to leave your organization.
The commercial benefit is time. A questionnaire answered with a current report and a retest moves to the next stage; one answered with "a test is planned" waits for it. How a stalled deal gets unblocked step by step is in the pentest report that unblocks a security review.
7. Answer cyber insurance applications truthfully
Cyber insurance applications ask about testing, and the questions are specific. The AXIS cyber application (form AXIS 1012098 0623, section 5.2 "Pen Testing") asks the applicant to tick a frequency, from quarterly to never, for each of five named test types: external network, internal network, social engineering, physical and web application, and whether testing is done internally or outsourced (AXIS application). A company that has only ever bought an external network test shows the gap in the web application row.
The benefit is accuracy, not an automatic discount. On the same form, the signer represents that the answers are "true, accurate and complete", and that "any policy the Insurer issues will be issued in reliance upon these representations." A wrong answer can cost the policy itself. In Travelers v. International Control Services (C.D. Ill., No. 2:22-cv-02145), Travelers alleged that the insured's application said the company "used MFA for administrative or privileged access" when it protected only the firewall, and sought rescission after a ransomware attack, as Insurance Journal reported. The parties then agreed to rescission, and on 30 August 2022 the court granted the agreed motion, rescinded the policy and declared it void from inception (court order).
A current penetration test lets the officer who signs the application answer the testing questions truthfully, and attach evidence if an underwriter or a claims adjuster asks. What underwriters actually grade is covered in does a pentest lower your cyber insurance premium.
8. Prove the fixes worked with a retest
A finding is only closed when someone confirms it. PCI DSS Requirement 11.4.4 makes that explicit: exploitable vulnerabilities found during penetration testing are corrected according to risk, and "penetration testing is repeated to verify the corrections."
In Stingrai's data, across 163 findings with a tracked resolution time, the median finding was resolved in 26 days and the 90th percentile in 121 days. A 30-day retest window would confirm roughly half the fixes and close before the slowest tenth had moved. The wider market is slower: the Verizon 2026 DBIR reports that only 26% of vulnerabilities in CISA's KEV catalog were fully remediated by organizations in 2025, down from 38%, with a median of 43 days to full resolution.
A retest turns "we think it is fixed" into evidence for the auditor, the customer and the board. Ask for a retest window that matches your real remediation pace, and for a report that records the status of each finding after the retest, not only before it. Why buyers increasingly expect evidence of closure rather than a report alone is covered in penetration testing trends 2026.
9. Direct security spend to the controls that failed
Findings are a diagnosis, not just a to-do list. In Stingrai's data the mix depends on what was tested. Across 408 internal network findings, 56.9% were outdated or unpatched software. Across 768 web application findings, authentication and session flaws led at 28.1%, with broken access control at 9.9% and IDOR at 7.9%.
Those mixes point at different budgets. A test dominated by outdated software points at patch management and asset inventory. One dominated by access control flaws points at design review, authorization frameworks and developer training. Buying more of the same scanner fixes neither.
Severity timing is a budget signal too. Critical findings in Stingrai's data were fixed at a median of 10.5 days, but High findings took 38.0 days: the severity that triggers an incident response gets fixed, and the one below it queues. If High findings sit for a month, the gap is in remediation capacity or ownership, not in finding the issue. Track findings by root cause across tests; a class that returns in every report is a program problem, not a ticket.
10. Give the board evidence, not opinion
Regulators now put board oversight of cyber risk in writing. Under NYDFS 500.4(b), a covered entity's CISO "shall report in writing at least annually to the senior governing body", including on the "overall effectiveness of the covered entity's cybersecurity program" and "plans for remediating material inadequacies". For US public companies, Regulation S-K Item 106 asks registrants to describe their processes for managing material cybersecurity risk, including "whether the registrant engages assessors, consultants, auditors, or other third parties", and to describe "the board of directors' oversight of risks from cybersecurity threats."
An independent penetration test is one of the few pieces of evidence in that report that did not come from the team being assessed. Five measures from a testing program translate well for a board:
Coverage: which critical systems were tested in the last 12 months, and which were not.
Exposure: the count of open High and Critical findings, and how old they are.
Speed: median days to fix by severity, against your own targets.
Closure: the share of findings confirmed fixed at retest.
Recurrence: finding classes that repeat across tests, which point at program gaps.
Which type of penetration test delivers which benefit?
Not every test delivers every benefit. The table maps the common types to the benefits they mainly produce.
Type of test | Main benefits | Typical driver | Stingrai service |
|---|---|---|---|
Web application and API | Flaws scanners miss (authorization, business logic), security reviews, SOC 2 evidence | Customer security reviews, SOC 2, frequent releases | |
External network | Internet-facing exposure closed, insurance answers, PCI DSS 11.4.3 | Perimeter changes, cyber insurance, PCI DSS | |
Internal network and Active Directory | Lateral movement and privilege escalation found, patch gaps exposed, PCI DSS 11.4.2 and 11.4.5 | Ransomware risk, segmentation, PCI DSS | |
Cloud | Identity and configuration paths to data found | Cloud migration, customer reviews | |
Red team | Detection and response tested end to end, board evidence | Mature programs, threat-led testing rules | |
Social engineering | Human-layer controls tested | The human element in 62% of breaches (Verizon 2026 DBIR) |
What are the benefits of external penetration testing?
An external test looks at what anyone on the internet can reach: VPN and remote access gateways, exposed services, web applications and cloud endpoints. Its benefit is closing the paths that need no prior access, which matters more as exploitation becomes the most common way in. It also answers the external network row on insurance applications and supports PCI DSS 11.4.3. Its limit is that it says almost nothing about what happens after the perimeter fails.
What are the benefits of internal penetration testing?
An internal test starts from inside, usually from a standard user's position, and asks how far an attacker who phished one employee or compromised one device could go. Its benefit is finding the lateral movement and privilege escalation paths that turn one foothold into a domain-wide incident, and the patch gaps behind them: in Stingrai's data, 56.9% of internal network findings were outdated or unpatched software. It supports PCI DSS 11.4.2 and, where segmentation is used, 11.4.5.
What are the benefits of automated and hybrid penetration testing?
Automated testing of a web application gives speed and repeatability: it can run after every release, not once a year, which matters when the mean time to exploit is negative. Autonomous agents go further than signature scanners; Stingrai's Snipe, for example, hunts authorization, IDOR and business logic flaws across user roles. Hybrid testing adds certified penetration testers to the same application, testing manually alongside the agent, so coverage is wider and deeper than either alone; how Stingrai runs it is below. It applies to web applications and associated APIs; network, cloud and red team engagements are scoped separately.
What are the risks and limitations of penetration testing?
The benefits have edges, and NIST names them plainly. SP 800-115 says penetration testing "is labor-intensive and requires great expertise to minimize the risk to targeted systems", that "systems may be damaged or otherwise rendered inoperable during the course of penetration testing", and that while experienced testers can mitigate this risk, "it can never be fully eliminated."
Operational risk. Testing can disrupt fragile systems. Manage it with written rules of engagement, agreed test windows, named emergency contacts, current backups, and a decision on which tests run against production and which against staging.
A point in time. A report describes one date. New releases, new exposures and new exploits arrive the day after. Continuous testing between annual tests narrows that window for systems that change often.
Scope-bound. A test finds what is in scope. A narrow scope produces a clean report and false comfort.
Not compliance on its own. A test is evidence within a compliance program; it does not make a company compliant.
Only as good as the fixes. A finding that is reported and never fixed becomes a documented, known weakness.
A qualified firm with a written methodology, named testers and clear rules of engagement manages most of these risks; the rest is your own remediation discipline.
How to get all ten benefits from one engagement
To get this benefit | Require this in the engagement |
|---|---|
Exploitable flaws found first | Testers who exploit and chain findings, with a proof of concept for each |
What scanners miss | Authenticated testing across every user role, covering business logic and authorization |
Detection tested | Rules of engagement that keep the test windows from the monitoring team, and a timestamped activity log |
Breach risk cut at a known cost | A fixed price for a defined scope, with the retest included |
Compliance evidence | A defined methodology, named qualified testers with organizational independence, and a scope that covers the systems in the audit |
Security reviews cleared | An executive summary and a shareable letter, issued within the last 12 months |
Insurance answered truthfully | Test types that match the application's rows (web application, external, internal) at the frequency you state |
Fixes proven | Retesting included in the price, with remediation status recorded per finding |
Spend directed | Findings classified by root cause, so classes can be compared across tests |
Board evidence | A management-level summary with coverage, exposure, speed and closure measures |
How Stingrai delivers these benefits
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified penetration testers, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Stingrai holds two CREST accreditations, Penetration Testing and AI-Enabled Penetration Testing, and the CREST AI Charter company certification, as listed on the CREST Marketplace. Its researchers have published 18 CVEs. Every finding is posted to the PTaaS portal as it is confirmed, with a proof of concept and remediation guidance, and clients get live chat with the assigned testers and Jira and Slack integration, so fixing starts during the test. Retesting is included, and every human-led and hybrid report ships with an attestation letter. Engagements run as one-time (annual) tests or as continuous programs.
For web applications, the Hybrid Pentest has Snipe test the full application while Stingrai's certified penetration testers test the same application manually alongside it and validate Snipe's findings. It is US$6,800 per assessment, or US$1,275 per month on a 12-month plan as a continuous program: monthly Snipe testing, human-verified, plus a quarterly deep dive by Stingrai's penetration testers. Both cover one web application and associated APIs (pricing). Continuous testing fits applications that ship often: with the mean time to exploit now below zero, an annual report on an internet-facing application ages in days. The Autonomous Pentest, Snipe alone, is US$3,000 per assessment and delivers a pentest report. Network, cloud and red team engagements are scoped individually and quoted through Get a Quote.
Frequently Asked Questions
What are the benefits of penetration testing?
The ten main benefits are finding exploitable flaws before attackers do, finding what scanners miss, testing whether defenses detect an attack, cutting breach risk at a small fraction of breach cost, producing compliance evidence, clearing customer security reviews, answering cyber insurance applications truthfully, proving fixes with a retest, directing security spend, and giving the board independent evidence. In Stingrai's data, 92.7% of 55 penetration tests surfaced at least one High or Critical finding.
Why is penetration testing important for a business?
Because exploitation of vulnerabilities is now the most common way into a breach, at 31% of breaches with a known initial access vector in the Verizon 2026 DBIR, and the global average breach cost reached a record US$4.99M in IBM's 2026 report. A penetration test finds the exploitable path first, on your terms.
Is a penetration test worth the cost?
For most companies, yes. A test for one web application and associated APIs costs thousands of US dollars, against a US$4.99M global average breach and the revenue held up by a stalled security review. Stingrai's Hybrid Pentest is US$6,800 per assessment, and a network penetration test typically costs US$5,000 to US$40,000 and above.
What are the risks of penetration testing?
NIST SP 800-115 notes that systems may be damaged or rendered inoperable during a test, and that the risk can be reduced but never fully eliminated. Written rules of engagement, agreed test windows, current backups and a qualified, accredited firm manage that risk. A test is also a point-in-time, scope-bound view.
How often should a business run a penetration test?
At least once a year and after any significant change to the systems in scope. That is the cadence PCI DSS 11.4.2 and 11.4.3 set, and NYDFS 500.5(a)(1) requires testing at least annually. Companies that release often run continuous testing between annual tests.
Does a penetration test make you compliant?
No single test makes a company compliant. It provides evidence that auditors use when they assess a compliance program, such as the penetration testing PCI DSS and NYDFS require and the separate evaluations SOC 2 auditors look for under CC4.1. Stingrai's testing supports SOC 2, ISO 27001, PCI DSS, HIPAA, CMMC and NYDFS programs.
Does a penetration test lower cyber insurance premiums?
It is better understood as protection for the policy than as a discount. Applications such as AXIS's ask how often you run each type of test, and the policy is issued in reliance on those answers; in Travelers v. International Control Services, the court rescinded the policy in 2022, by agreement, after Travelers asserted that the application's MFA answers were incorrect. A current test lets you answer truthfully and attach evidence.
Related reading
The State of Penetration Testing 2026: An Analysis of 1,206 Verified Findings
How Often Should You Do Penetration Testing? Frequency by Framework and Risk (2026)
Penetration Testing Cost (2026): Prices by Scope and Compliance Driver
VAPT (2026): Vulnerability Assessment and Penetration Testing, Process, Scope and Cost
Penetration Testing Trends 2026: 10 Shifts to Plan Your 2027 Testing Around
References
Verizon. 2026 Data Breach Investigations Report and executive summary. 2026. https://www.verizon.com/business/resources/reports/dbir/. More than 22,000 confirmed breaches in 145 countries.
Verizon. 2025 Data Breach Investigations Report. 2025. https://www.verizon.com/business/resources/T7a9/reports/2025-dbir-data-breach-investigations-report.pdf. Prior-year values for Figure 2.
IBM and Ponemon Institute. Cost of a Data Breach Report 2026. July 2026. https://www.ibm.com/reports/data-breach. Breaches at 602 organizations, March 2025 to February 2026.
Mandiant (Google). M-Trends 2026. 2026. https://www.gstatic.com/security-marketing/m-trends-2026-en.pdf. Mandiant incident response investigations in 2025.
NIST. SP 800-115, Technical Guide to Information Security Testing and Assessment. 2008. https://nvlpubs.nist.gov/nistpubs/Legacy/SP/nistspecialpublication800-115.pdf. Sections 4.3 and 5.2.
CISA. AA24-326A: Enhancing Cyber Resilience: Insights from CISA Red Team Assessment of a US Critical Infrastructure Sector Organization. 21 November 2024. https://www.cisa.gov/news-events/cybersecurity-advisories/aa24-326a.
PCI Security Standards Council. PCI DSS v4.0.1 and SAQ D for Merchants, Requirements 11.4.2 to 11.4.5. https://www.pcisecuritystandards.org/document_library/.
New York State Department of Financial Services. 23 NYCRR Part 500, as amended November 2023, sections 500.4 and 500.5. https://www.dfs.ny.gov/industry_guidance/regulations/final_adoptions_fs/rf_fs_2amend23NYCRR500_text_20231101_alt.
US Securities and Exchange Commission. 17 CFR 229.106 (Regulation S-K Item 106), Cybersecurity. eCFR. https://www.ecfr.gov/current/title-17/chapter-II/part-229/subpart-229.100/section-229.106.
US Department of Health and Human Services. HIPAA Security Rule To Strengthen the Cybersecurity of Electronic Protected Health Information (proposed rule). 6 January 2025. https://www.federalregister.gov/documents/2025/01/06/2024-30983/hipaa-security-rule-to-strengthen-the-cybersecurity-of-electronic-protected-health-information.
AXIS. Cyber, Technology and MPL application, form AXIS 1012098 0623. https://www.axiscapital.com/docs/default-source/resources/axis-1012098-0623-axis-cyber-technology-mpl-application-7-20-23.pdf. Section 5.2 and section 14.
Stingrai. The State of Penetration Testing 2026. https://www.stingrai.io/blog/state-of-penetration-testing-2026. 55 penetration tests and 1,216 logged findings, October 2024 to August 2026.
Talk to Stingrai
Every benefit above starts with a defined scope. Get a Quote for a one-time or continuous test of your web applications, network or cloud, or book a free discovery call to decide which tests your auditors, customers and insurers will ask for.