Web application penetration testing is an authorized, time-boxed attack on a web application and the APIs behind it, in which penetration testers work the way real attackers do and report only the weaknesses they can prove. NIST defines penetration testing as "security testing in which assessors mimic real-world attacks to identify methods for circumventing the security features of an application, system, or network" (SP 800-115). On a web application most of that work is about what each user role can reach: OWASP's page for the top category of its Top 10:2025 says "100% of the applications tested were found to have some form of broken access control", and in Stingrai's 2026 penetration testing data, 70% of the web application tests that produced findings surfaced at least one High or Critical authentication or authorization flaw.
Quick answer. A web application penetration test is a manual, evidence-backed attack on a web application and its APIs by penetration testers who hold a test account for every user role, following the OWASP Web Security Testing Guide v4.2, stating coverage against OWASP ASVS 5.0 and mapping findings to the OWASP Top 10:2025. It runs in seven phases, from scoping through mapping, testing, exploitation and reporting to a retest of every fix, and it differs from a scan because people check what each role should be allowed to do and prove the impact. PCI DSS v4.0.1 requires application-layer penetration testing at least once every 12 months and after significant change. Stingrai's Hybrid Pentest, with Snipe and certified penetration testers on the same application, is US$6,800 per assessment or US$1,275 per month on a 12-month continuous plan, for one web application and associated APIs.
This guide covers how a test works, from methodology to report. Companion guides cover scope and cost, choosing a provider, how every testing method compares and DAST versus penetration testing.
What is web application penetration testing?
A web application penetration test (also called a web app pen test or an application penetration test) is a security assessment in which qualified testers attack one application inside a written scope and time window. Three properties set it apart.
People do the testing. OWASP's Web Security Testing Guide (WSTG) gives the reason: "As web applications are almost exclusively bespoke, penetration testing in the web application arena is more akin to pure research." A flaw in an application only one company runs has no public signature for a tool to match.
It proves exploitability. NIST notes that most penetration tests "involve looking for combinations of vulnerabilities on one or more systems that can be used to gain more access than could be achieved through a single vulnerability." The output is a demonstrated path to data or privileges, with the requests and responses as evidence.
It is authorized and bounded. Scope, dates, test accounts, exclusions and stop conditions are agreed in writing before testing starts.
The case for it rests on how applications are breached. Verizon's 2026 Data Breach Investigations Report, covering incidents from 1 November 2024 to 31 October 2025, found that exploitation of vulnerabilities was the initial access vector in 31% of non-Error, non-Misuse breaches with a known vector, up from 20% a year earlier, and counted 3,217 incidents in its Basic Web Application Attacks pattern, 2,281 with confirmed data disclosure. MITRE's 2025 CWE Top 25 is led by four weaknesses that live in web applications: cross-site scripting, SQL injection, cross-site request forgery and missing authorization. A broken permission check in a company's own code gets no CVE, so it stays unknown until someone tests that application.
Penetration test, vulnerability scan, DAST or bug bounty?
Web application security testing is the wider discipline, and a penetration test is one method inside it; each method sees a different part of the problem.
Method | Who does the work | Good at | Does not see | Typical cadence |
|---|---|---|---|---|
SAST and SCA | Tools reading code and dependency manifests | Coding flaws and vulnerable components | Design flaws and deployed behaviour | Every commit or build |
Vulnerability scan or DAST | A tool sending requests to the running application | Known signatures, missing headers, simple injection points | Business logic, chained impact, and authorization without several accounts and custom rules | Nightly, weekly or per release |
Penetration test | Penetration testers, using tools, inside an agreed scope | What each role can do that it should not, logic abuse, attack chains, proof of impact | Anything outside the scope and window | At least annually and after significant change |
Bug bounty | Outside researchers paid per valid report | Unusual bugs found by many people over time | Defined coverage: scope sets what is rewarded, not what was examined | Continuous, as a supplement |
The PCI Security Standards Council's penetration testing guidance sets the purpose of a penetration test as: "Identify ways to exploit vulnerabilities to circumvent or defeat the security features of system components", through "A manual process that may include the use of vulnerability scanning or other automated tools, resulting in a comprehensive report." NIST gives the reason a scan cannot stand in for one: "Scanners are unable to detect vulnerabilities that are revealed only as the result of potentially unending combinations of attack patterns." DAST, SAST and SCA still belong in every pipeline; the penetration test examines what they leave behind. The bounty trade-offs are in penetration testing vs bug bounty.
Web application penetration testing methodology: OWASP WSTG, ASVS 5.0 and the Top 10
Proposals and reports cite several OWASP documents as if they were interchangeable. They do different jobs.
Standard | Current version | Its job in a web application penetration test |
|---|---|---|
Web Security Testing Guide (WSTG) | v4.2, released December 2020; version 5.0 is in development | The test method: 97 test cases in 12 categories, each with an identifier such as WSTG-ATHZ-04 |
Application Security Verification Standard (ASVS) | 5.0.0, released 30 May 2025 | The requirement set used to state coverage and accept a report: 345 requirements in 17 chapters, at three levels |
OWASP Top 10 | 2025 | Categorizing and communicating findings |
OWASP API Security Top 10 | 2023 | API-specific risks, led by API1:2023 Broken Object Level Authorization |
Three points matter to a buyer. First, "tested against the OWASP Top 10" is a floor: OWASP calls the list "primarily an awareness document" and says that, as a testing standard, it is "the bare minimum and just a starting point." Second, WSTG v4.2 is thin on APIs (its API category holds one test case, for GraphQL), so testers add the API Security Top 10. Third, ASVS 5.0 says its first level "is not necessarily penetration testable by an external tester without internal access to documentation or code", so a report that claims ASVS coverage needs documentation and, ideally, source code. The ASVS 5.0 pentest acceptance matrix shows how to use it to accept a report.
What testers check: the eight areas of a web application penetration test
A complete test works through eight areas, each mapped to WSTG categories and to the OWASP Top 10:2025 categories used in the report. The mapping is a working guide, not an official OWASP table.
Area tested | What the testers check | WSTG v4.2 categories | OWASP Top 10:2025 |
|---|---|---|---|
Authentication | Registration, login, lockout, password reset, multi-factor authentication, single sign-on | Identity Management (IDNT), Authentication (ATHN) | A07 Authentication Failures |
Session handling | Session tokens and cookies, expiry, logout, fixation, cross-site request forgery | Session Management (SESS) | A07; A01 for CSRF |
Authorization and multi-tenancy | Access between users, between roles and between tenants | Authorization (ATHZ) | A01 Broken Access Control |
Input handling | SQL, NoSQL and command injection, cross-site scripting, template injection, SSRF, file upload, deserialization | Input Validation (INPV) | A05 Injection; A01 for SSRF; A06 for file upload; A08 for deserialization |
Business logic | Workflow order, limits, pricing, approvals, race conditions | Business Logic (BUSL) | A06 Insecure Design |
APIs | The REST or GraphQL endpoints the application calls, including undocumented ones | API Testing (APIT), plus the API Security Top 10 | A01 and others |
Client side | DOM-based cross-site scripting, cross-origin resource sharing, clickjacking, secrets in JavaScript | Client-side (CLNT) | A05; A01 for CORS; A06 for clickjacking |
Configuration, components, cryptography and errors | Security headers, TLS, exposed admin and debug interfaces, outdated components, error handling | Information Gathering (INFO), Configuration (CONF), Cryptography (CRYP), Error Handling (ERRH) | A02 Security Misconfiguration, A03 Software Supply Chain Failures, A04 Cryptographic Failures, A10 |
What tests of this kind find shows in Stingrai's 2026 dataset: 768 verified findings from 40 web application penetration tests, a median of 8 per test, 54% of them rated High or Critical.
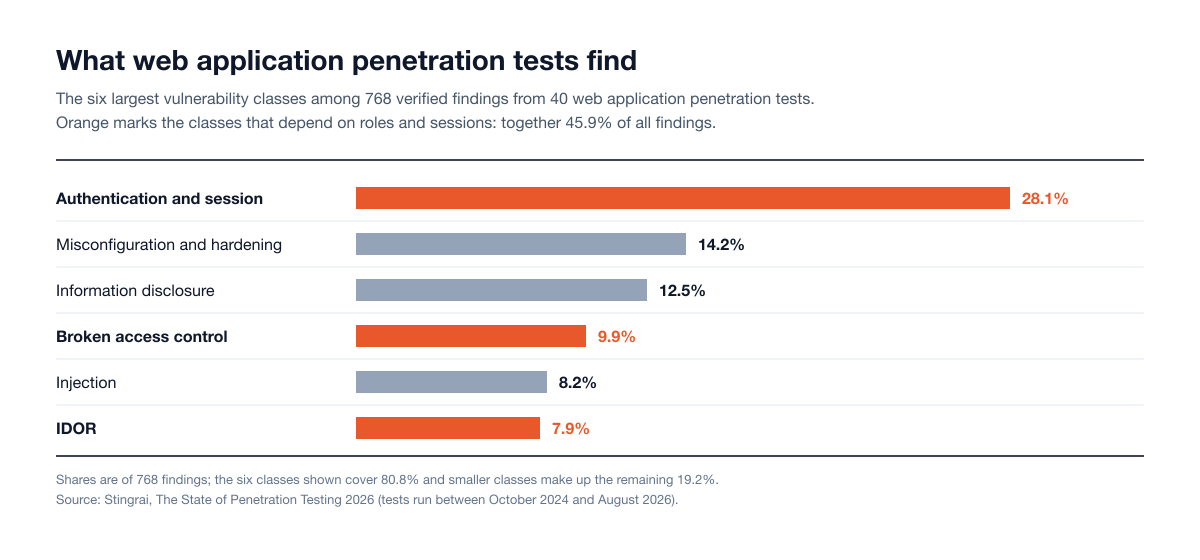
Figure 1: The six largest classes among 768 verified web application findings. Orange marks the classes that depend on roles and sessions. Source: The State of Penetration Testing 2026.
Authentication and session handling
Testers attack every way of proving identity, from login to password reset, multi-factor recovery and single sign-on, then check how session tokens are issued, protected and ended. OWASP's A07:2025 lists the failures they look for, including applications that permit "automated attacks such as credential stuffing", have "missing or ineffective multi-factor authentication" or do not "correctly invalidate user sessions or authentication tokens" at logout. Authentication and session issues are the largest class in Stingrai's web application data, at 28.1% of findings.
Authorization and multi-tenancy
Authorization is where a web application test earns its fee. Testers hold accounts in every role and in at least two tenants, then check each sensitive action in three directions: between two users of the same role, from a lower role to a higher one, and across the tenant boundary. The WSTG's test for insecure direct object references (WSTG-ATHZ-04) calls for "at least two (often more) users" for exactly this reason. Broken access control and IDOR together make up 17.8% of Stingrai's web application findings. (OWASP's "100%" line is the project's own sentence; the score table on the same page gives a highest incidence rate of 20.15%.) The IDOR guide covers the mechanics, and authenticated web application penetration testing the role fixtures a test needs.
Input handling
Every place the application accepts data is tested for injection: database queries, operating system commands, templates, XML parsers, file uploads and URLs the server fetches. In Stingrai's data, 48% of the web application tests that produced findings surfaced a High or Critical injection. Cross-site scripting and server-side request forgery have their own guides.
Business logic
Business logic testing asks whether the application can be used in ways its design never intended: skipping a payment step, reusing a discount, approving one's own request, or winning a race for a limited resource. OWASP places these flaws under A06:2025 Insecure Design, and the WSTG says this type of vulnerability "cannot be detected by a vulnerability scanner and relies upon the skills and creativity of the penetration tester." PCI DSS Requirement 6.2.4 lists "Attacks on business logic" among the attacks custom software must withstand. Scoping is covered in business logic penetration testing.
APIs and the client side
Most authorization decisions in a modern web application are made by the API behind the interface, and PCI's guidance notes that "the API may be in scope for the testing." Scope the application and its API as one engagement, so every role is tested through the interface and directly against the endpoints; the API penetration testing checklist lists the checks. In the browser, testers check DOM-based cross-site scripting, clickjacking, client-side redirects, secrets shipped in JavaScript and cross-origin rules; OWASP's A01:2025 lists a CORS misconfiguration that "allows API access from unauthorized or untrusted origins" as an access control failure.
Configuration, components and error handling
This is where automated tools contribute most: security headers, TLS, exposed admin and debug interfaces, default accounts, and deployed versions compared against known vulnerabilities. A10:2025 Mishandling of Exceptional Conditions, a new category for 2025, covers "improper error handling, logical errors, failing open", so testers also force errors mid-workflow and watch whether the action still completes.
What is usually excluded
Denial-of-service attacks, destructive exploitation and third-party systems such as a payment processor are excluded unless agreed in writing. Logging and alerting (A09:2025) is observed, not attacked: OWASP counts it as a failure when "Penetration testing and scans by dynamic application security testing (DAST) tools" trigger no alerts.
The authorization and logic checks testers run, mapped to ASVS 5.0
A scanner rarely completes these checks on its own, because it does not know who owns a record, what a role is for or what order a workflow should follow. A joint advisory from CISA, the NSA and Australia's ACSC, AA23-208A, says "Not all DAST tools can detect IDOR vulnerabilities", and that tools with the ability "may need the environment configured in a specific way and may also need custom rules in place."
Check | How a penetration tester runs it | ASVS 5.0 requirement |
|---|---|---|
Object-level authorization (IDOR, BOLA) | Requests one user's records with another user's session, within and across tenants | 8.2.2 |
Function-level authorization | Repeats privileged requests with lower-privileged and anonymous sessions | 8.2.1 |
Property-level authorization (mass assignment) | Adds fields such as role, tenant or price to updates and compares responses across roles | 8.2.3 |
Stale authorization | Removes or demotes a user, then reuses the old session or token | 8.3.2 |
Workflow order and limits | Skips, repeats and reorders steps, and pushes quantities, prices and quotas | 2.3.1, 2.3.2 |
Race conditions | Sends the same action in parallel and counts the outcomes | 2.3.4 |
Fail-open error paths | Forces errors in the middle of a flow and checks whether the action still completes | 16.5.3 |
The API side of the same problem is covered in why automated API scanners miss BOLA and IDOR.
Black box, grey box or white box: why authenticated testing matters
The three "box" types describe how much the testers are given before they start.
Type | What the testers receive | What it shows | Where it falls short |
|---|---|---|---|
Black box | A URL and nothing else | What an anonymous outsider can reach | Most of the application sits behind the login, untested |
Grey box | Test accounts for every role, plus documentation such as an API specification | What each customer, employee and administrator can do that they should not | Root causes in code are inferred, not read |
White box | Everything in grey box, plus source code and architecture documents | The same findings with their cause in the code | More effort, and it needs repository access |
For any application with a login, the grey-box, authenticated portion is the core of the test. PCI's guidance says "testing should be performed against all roles or types of access", and that the organization "is strongly encouraged to supply credentials to allow the tester to assume the required roles." ASVS 5.0 is blunter: "Testing without access to necessary additional information is an inefficient and ineffective mechanism for security verification." Role testing works from a matrix: every role on one axis, every sensitive function on the other, and the expected allow or deny in each cell. Which type fits which goal is in black box vs grey box vs white box penetration testing.
The phases of a web application penetration test, from scoping to retest
NIST describes penetration testing in four phases: planning, discovery, attack and reporting, with reporting running alongside the other three. A commercial web application test follows the same logic in seven steps, which Figure 2 groups into six stages.
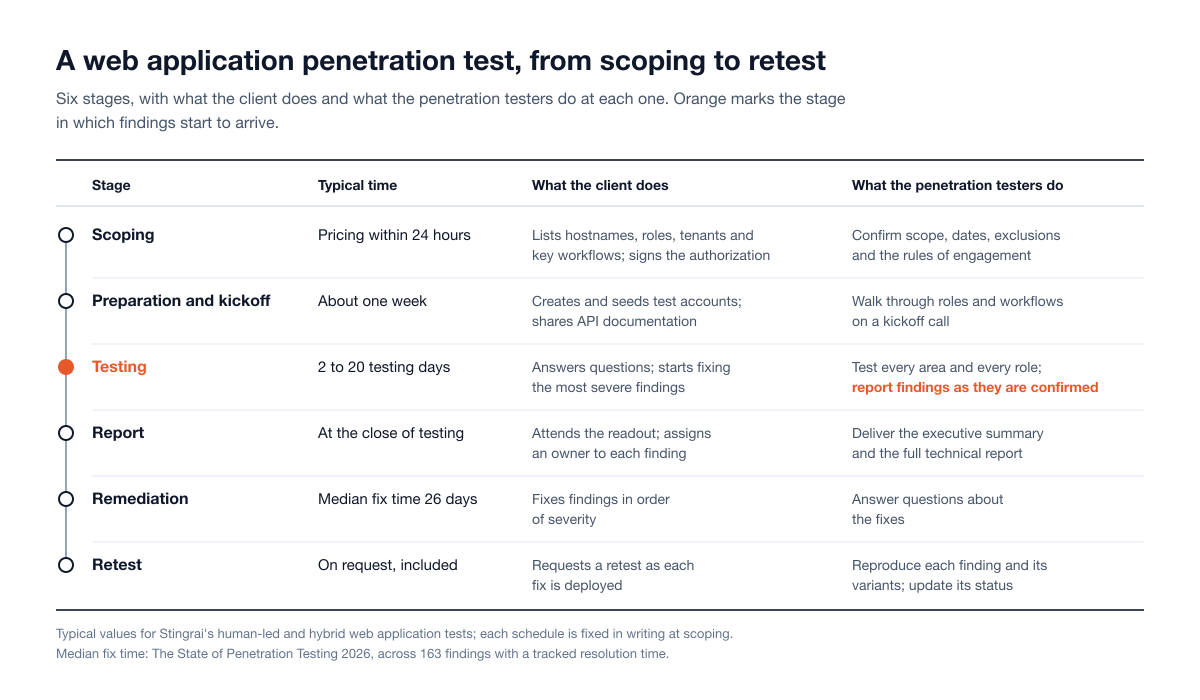
Figure 2: A web application penetration test from scoping to retest. The figure groups mapping, testing and exploitation as one testing stage and shows remediation and retest separately. Durations are typical values for Stingrai engagements and are fixed in writing at scoping.
1. Scoping and rules of engagement
Scoping fixes what will be tested and what the test has to prove: hostnames and API base URLs, roles, tenants, critical workflows, the environment, dates and exclusions. The rules of engagement add tester source IP addresses, an emergency contact, stop conditions and data-handling terms. In NIST's words, "No actual testing occurs in this phase." See how to scope a penetration test.
2. Preparation and kickoff
The client creates and seeds the test accounts, shares API documentation and confirms the environment. A kickoff call walks the testers through the roles and the most important workflows, because testers who know what a refund or an approval is meant to do can test whether it can be abused.
3. Mapping and discovery
Testers browse the application once per role through an intercepting proxy, so every page, endpoint, parameter and role-specific function is recorded, and reconcile the documented API against observed traffic, because undocumented endpoints are where forgotten permission checks tend to sit.
4. Testing each area
The eight areas are tested in overlapping passes. Automated scanning covers configuration and common injection points quickly; the testers spend their own time on authentication, the role and tenant matrix, and the business logic.
5. Exploitation and chaining
A weakness becomes a finding when it is reproduced, and a priority when its impact is shown. Testers combine weaknesses, for example an information leak that reveals record identifiers with a missing ownership check that accepts them, and prove the result with the least intrusive action available, such as reading one seeded test record.
6. Reporting
Good providers report findings as they are confirmed, so engineering can start on a Critical issue during the test. The formal report follows at the close of testing, usually with a readout call.
7. Remediation and retest
The test is finished when the fixes have been checked; PCI DSS Requirement 11.4.4 says: "Penetration testing is repeated to verify the corrections." A retest reproduces the original finding, then tries the same flaw on neighbouring endpoints and roles, because authorization fixes are often applied to one route only. In Stingrai's tracked data the median finding was resolved in 26 days and the slowest tenth took more than 121, so a single retest at 30 days confirms roughly half the fixes; retests requested per finding catch the rest.
Production or staging?
Most of a test belongs in a staging environment that runs the same build, configuration and integrations as production. Deployment-dependent items such as TLS, headers and exposed admin interfaces still need a short read-only pass in production; when production is the only option, testing uses dedicated test tenants, agreed windows and lower request rates.
Tools penetration testers use
Tools speed up a penetration test; they do not perform it.
Category | Examples | What it does | What it cannot do |
|---|---|---|---|
Intercepting proxy | Reads, changes and replays every request between browser and server | Decide whether a response should have been allowed | |
Web vulnerability scanner | Burp Scanner, Nuclei | Checks at speed for known misconfigurations, exposed files and published CVEs | Judge business rules, or authorization without per-role configuration |
Content discovery | Finds paths, parameters and hosts the application does not link to | Find a vulnerability by itself | |
Injection confirmation | Confirms a suspected SQL injection and shows what it exposes | Cover any other vulnerability class | |
API clients and token utilities | Drive documented APIs with one environment per role; inspect and tamper with tokens | Know the application's permission model | |
Autonomous AI agents | Stingrai's Snipe | Run authenticated tests across the user roles of a web application and associated APIs | Remove the need for reproduction evidence on every finding |
Ask a provider whether every reported finding was reproduced, by a person or by an agent with evidence attached, and how much of the testing time is manual. PCI DSS expects a human at the centre: its penetration testing objective refers to "simulated attack methods by a competent manual attacker."
What the report and the attestation letter contain
The WSTG says a report "should appeal to both executive management and technical staff." A complete web application penetration test report contains:
An executive summary in business terms.
Scope and limitations: the hostnames, environments, roles and dates tested.
Methodology and coverage: the standards followed, and which areas were tested, which were not, and why.
Detailed findings: affected endpoints and roles, severity with its rationale, reproduction steps with the exact requests and responses, impact, a specific fix, and the OWASP Top 10:2025 category and CWE.
Retest results with the status of each finding after the fixes were checked.
Severity is commonly scored with CVSS v4.0, which FIRST published on 1 November 2023, then adjusted for business context. The coverage statement matters because, as ASVS puts it, "Traditional penetration testing reports issues 'by exception,' only listing failures", and such a report cannot show an auditor what was examined and found sound. A clean report is not automatically good news either: guidance printed in PCI DSS itself says "A penetration test that found nothing is typically indicative of shortcomings of the penetration tester, rather than being a positive reflection of the security posture of the entity." In Stingrai's dataset, 9 of 1,216 logged findings, or 0.74%, were declined at review as false positives.
The attestation letter is a short document for customers and auditors that states the scope and testing dates, the proof of testing a security questionnaire asks for. See the annotated penetration testing report sample and how to evaluate a penetration test report.
How long a web application penetration test takes, and what drives cost
PCI's guidance says only that engagements "may last days or weeks depending on the scope of the test and size of the environment to be tested." Stingrai plans human-led and hybrid web application tests on the following shapes, with about a week of preparation before testing starts.
Application | Typical elapsed time |
|---|---|
Single-tenant, two roles, fewer than thirty endpoints | A few tester days across one to two weeks |
Multi-tenant product, four to six roles, a few hundred endpoints | Two to four weeks |
Platform with eight or more roles and money movement | Four to eight weeks |
Cost moves with the same factors: the number of roles (the largest driver, because authorization testing grows with every role pair), multi-tenancy, API size, workflow complexity, source code access and retest terms. Stingrai's 2026 cost guide, a benchmark built from published vendor pricing and industry cost guides, puts a standard web application test at about US$5,000 to US$30,000 across the market; scope and cost gives the full table of drivers.
How often to test, and what PCI DSS, SOC 2 and ISO 27001 say
The working answer is at least once a year and after any significant change. That cadence comes from PCI DSS, and OWASP recommends the same floor: "At least annual penetration testing (depending upon the level assurance required for your app)." The frameworks differ on whether a test is required at all.
Framework | What the text says | Is a web application penetration test mandated? |
|---|---|---|
PCI DSS v4.0.1, Requirement 11.4 | The methodology includes "Application-layer penetration testing to identify, at a minimum, the vulnerabilities listed in Requirement 6.2.4" (11.4.1); tests run at least once every 12 months and after any significant infrastructure or application upgrade or change (11.4.2, 11.4.3); exploitable findings are corrected and retested (11.4.4) | Yes, for entities that must meet PCI DSS |
PCI DSS v4.0.1, Requirement 6.4.2 | Public-facing web applications need "an automated technical solution" that "continually detects and prevents web-based attacks", required after 31 March 2025 | No. It is a protection control and does not replace the 11.4 test |
SOC 2 (2017 Trust Services Criteria, 2022 points of focus) | A point of focus under CC4.1 names penetration testing among the evaluations management may use; points of focus need not each be addressed | No, and no frequency is set; auditors and enterprise customers commonly expect a recent report |
ISO/IEC 27001:2022 | Names no penetration test and no testing frequency; a test report serves as evidence for Annex A controls 8.8 and 8.29 | No. Whether and how often to test follows from the organization's risk assessment |
Clause-level detail is in PCI DSS penetration testing, SOC 2 penetration testing requirements and ISO 27001 penetration testing, and cadence by risk in how often to do penetration testing.
How Stingrai tests web applications: the Hybrid Pentest, one-time or continuous
Stingrai is a proud CREST member. Stingrai Inc holds two CREST accreditations, Penetration Testing and AI-Enabled Penetration Testing, and the company certification CREST AI Charter, as its CREST Marketplace listing shows.
Stingrai is a global CREST-accredited penetration testing services company founded in Toronto, Canada in 2021, trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA. OSCE³, OSWE, OSEP, CREST CRT certified penetration testers, who are also world-class security researchers and bug bounty hunters. Choose from fully human-led or hybrid (AI agents plus human penetration testers) engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
Stingrai's web application penetration testing starts black box, then moves to grey box with a test account for every role in scope, adding white-box review where repository access is provided; it follows the OWASP WSTG and ASVS 5.0. Hybrid and human-led engagements are staffed by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications, and the team has published 18 CVEs. Findings reach the PTaaS portal as they are confirmed, retesting is included, and every human-led and hybrid report ships with an attestation letter, evidence for SOC 2, ISO 27001, PCI DSS and HIPAA programs.
The Hybrid Pentest
Snipe, Stingrai's autonomous AI agent for web applications and associated APIs, tests the full application while Stingrai's certified penetration testers test the same application manually alongside it and validate Snipe's findings, so coverage is wider and deeper. It is not a split of test classes: both work across the whole application, authorization and business logic included. Stingrai runs it as a one-time (annual) test or as a continuous program.
Package | Who tests | Price for one web application and associated APIs | What you receive |
|---|---|---|---|
Hybrid Pentest, continuous | Monthly Snipe testing, human-verified, plus a quarterly deep dive by Stingrai's penetration testers | US$1,275 per month on a 12-month plan | Testing all year, quarterly executive status reports, attestation letter, PTaaS portal with Jira and Slack |
Hybrid Pentest, one-time | Snipe and Stingrai's certified penetration testers on the same application | US$6,800 per assessment | Human-validated pentest report, attestation letter, 12 monthly vulnerability scans after the pentest |
Autonomous Pentest | Snipe | US$3,000 per assessment, or US$650 per month on a 12-month plan | Pentest report; up to 200 API endpoints or dynamic pages and up to 3 user roles; same-day results; automated retests |
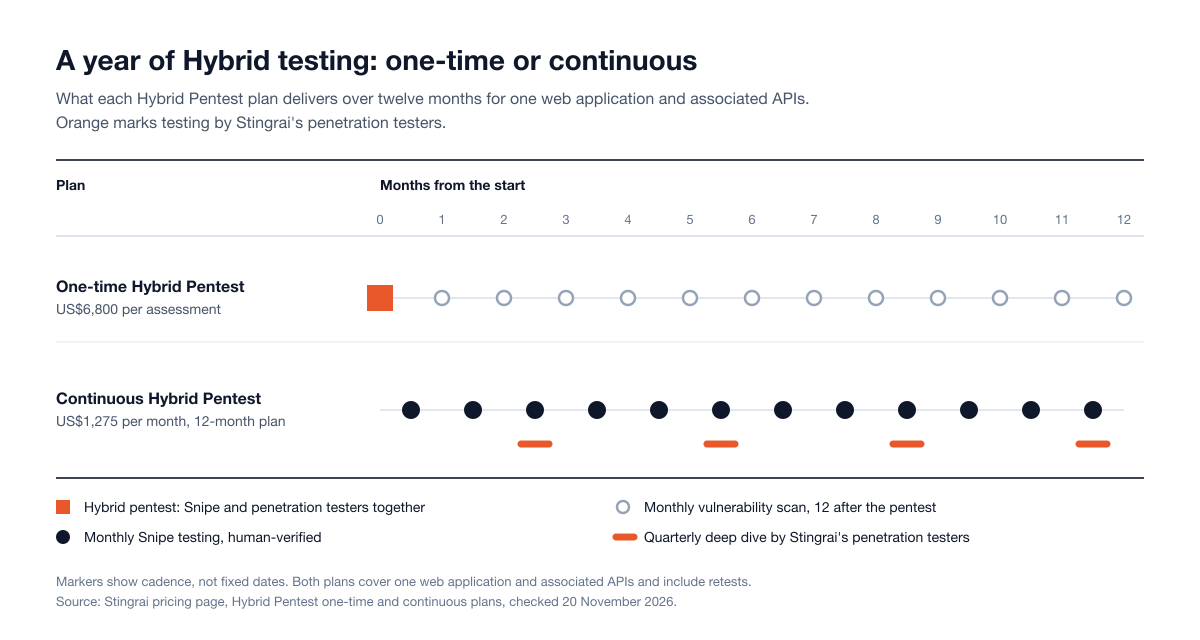
Figure 3: What each Hybrid Pentest plan delivers over twelve months, as listed on 20 November 2026. Source: Stingrai pricing.
Why continuous testing suits most web applications
An annual test describes the application as it stood that week, and three trends make the gap between tests more costly:
Exploitation leads. It is now the most common initial access vector in Verizon's 2026 DBIR, at 31% of non-Error, non-Misuse breaches with a known vector.
Known exploited flaws arrive faster. CISA added 302 vulnerabilities to its Known Exploited Vulnerabilities catalog between 1 January and 18 November 2026, already more than the 245 it added in all of 2025. Those are vendor products; a company's own application has no vendor patch to wait for.
Fixes take weeks. In Stingrai's data, across the findings with a tracked resolution time, the median took 26 days to resolve and the slowest tenth more than 121.
An application that ships every sprint changes its roles, endpoints and workflows many times between annual tests, and each change can reopen an authorization check that passed last time. The continuous Hybrid Pentest tests it every month, with Snipe's findings verified by penetration testers, and adds a quarterly deep dive by Stingrai's penetration testers, a natural point to cover the new features, role changes and logic flows shipped since the last one. A one-time Hybrid assessment remains the right buy for an application that changes rarely, or for a point-in-time report before a customer review. More in hybrid web application penetration testing.
Next step: compare the plans on the pricing page, or send your application's roles, sensitive flows and release rhythm through Get a Quote. Larger applications, several applications and fully human-led tests are quoted there too.
How to prepare for a web application penetration test
Preparation decides how much of the paid time goes into testing. Before the start date, have these ready:
Written authorization naming the hostnames, API base URLs, dates and exclusions, signed by someone entitled to give it.
Third-party notices: test payment processors and single sign-on providers through their sandbox or test modes, and check your cloud provider's testing policy.
A role matrix: every role, what each may do, and the functions and records that matter most.
Test accounts: two per role, in two tenants for a multi-tenant product, each seeded with its own data, with multi-factor authentication and password-reset mailboxes arranged.
API documentation: an OpenAPI specification, a GraphQL schema or a request collection.
The environment: a staging build that matches production, or a production test tenant with agreed limits.
The ten workflows that matter most to the business, written down in a sentence each.
Named contacts: an engineer who can answer questions within a day, and an emergency contact who can roll back a change.
A remediation plan: who triages findings, where tickets go, and when the retest is expected.
Teams building with AI coding tools should clear the security checklist for AI-built apps first.
Common mistakes
An unauthenticated test of an application that lives behind a login, which never reaches the role and tenant boundaries.
One account per role, which makes access between peers untestable.
Leaving the API out of scope, although a check that exists in the interface is often missing on the endpoint behind it.
Accepting a scanner export as a penetration test: no reproduction steps, no roles and hundreds of header findings make a scan with a cover page.
Skipping the retest, or booking the test the week before an audit, leaving no time to fix and verify before the report is used as evidence.
Frequently Asked Questions
What is web application penetration testing?
Web application penetration testing is an authorized, time-boxed attack on a web application and the APIs behind it by penetration testers who use the techniques of real attackers. They hold accounts for every user role, test authentication, sessions, authorization, input handling, business logic, APIs and configuration, and report only the weaknesses they could demonstrate, each with evidence and a fix.
What methodology is used for web application penetration testing?
Most tests follow the OWASP Web Security Testing Guide v4.2 (97 test cases in 12 categories), add the OWASP API Security Top 10, state coverage against OWASP ASVS 5.0 and map findings to the OWASP Top 10:2025. The work runs in seven phases: scoping, preparation, mapping, testing, exploitation and chaining, reporting, and a retest of every fix.
What does a web application penetration test cover?
Eight areas: authentication, session handling, authorization and tenant isolation, input handling, business logic, APIs, client-side code, and configuration with components, cryptography and error handling. Denial-of-service attacks, destructive exploitation and third-party systems are excluded unless agreed in writing.
What is the difference between a web application penetration test and a vulnerability scan?
A vulnerability scan is an automated tool that matches an application against known signatures. A penetration test is a manual process, supported by tools, in which testers exploit weaknesses, chain them and prove what an attacker could reach, including whether one user can see another user's data. In Stingrai's 2026 data, 70% of the web application tests that produced findings surfaced a High or Critical authentication or authorization flaw.
Should a web application penetration test be black box, grey box or white box?
Grey box at a minimum, for any application with a login. A black-box test leaves everything behind authentication untested, while a grey-box test gives the testers an account for every role, which is how broken authorization, IDOR and business logic flaws are found. White-box testing adds source code and suits high-risk applications.
How long does a web application penetration test take?
It depends on the number of roles and workflows. A single-tenant application with two roles and fewer than thirty endpoints takes a few tester days across one to two weeks, a multi-tenant product with four to six roles takes two to four weeks, and a platform with eight or more roles and money movement takes four to eight weeks, plus about a week of preparation.
How much does a web application penetration test cost?
Stingrai publishes fixed prices for one web application and associated APIs: the Hybrid Pentest is US$6,800 per assessment or US$1,275 per month on a 12-month continuous plan, and the Autonomous Pentest is US$3,000 per assessment or US$650 per month on a 12-month plan. Across the market, Stingrai's 2026 cost guide puts a standard web application test at about US$5,000 to US$30,000, driven mainly by roles, multi-tenancy and workflow complexity.
How often should a web application be penetration tested?
At least once a year and after any significant change. PCI DSS v4.0.1 sets that cadence in Requirement 11.4, with exploitable findings corrected and retested, and OWASP recommends at least annual testing. SOC 2 and ISO/IEC 27001:2022 set no frequency, though auditors and enterprise customers commonly expect a recent report. Applications that release often suit continuous testing.
What tools are used in web application penetration testing?
An intercepting proxy such as Burp Suite is the core tool, supported by scanners such as Nuclei, content discovery tools such as ffuf, sqlmap for confirming SQL injection, API clients such as Postman and token utilities such as jwt_tool. Findings in authorization and business logic mostly come from a tester, or an autonomous agent, working through the role matrix.
How do companies scale web application and API penetration testing across frequent releases?
Automated scanning runs in the release pipeline, and a continuous program tests the application and its API every month with a deeper manual test each quarter. Stingrai's continuous Hybrid Pentest does this for one web application and associated APIs at US$1,275 per month on a 12-month plan: monthly Snipe testing, human-verified, plus a quarterly deep dive by Stingrai's penetration testers.
Related reading
Web Application Penetration Testing: Scope, Cost and What You Get: what drives the scope and price of a web application test.
Best Web Application Penetration Testing Companies (2026): Services Compared: how to choose a provider.
Web Application Security Assessment (2026): Testing Methods, Scope and Cost: SAST, SCA, DAST, manual testing and AI agents compared.
DAST vs Penetration Testing (2026): What Each Finds and Where Hybrid Fits: what a scanner in the pipeline finds and misses.
Authenticated Web Application Penetration Testing: Roles, Fixtures and Evidence (2026): building the role fixture pack.
Hybrid Web Application Penetration Testing (2026): how an autonomous agent and penetration testers run one scope together.
References
NIST, SP 800-115, Technical Guide to Information Security Testing and Assessment, September 2008, sections 4.3 and 5.2.
OWASP, Web Security Testing Guide v4.2, including the introduction, business logic and reporting chapters, and the project page.
OWASP, Top 10:2025, including the category pages and Establishing a Modern Application Security Program.
OWASP, Application Security Verification Standard 5.0.0, 30 May 2025, and the API Security Top 10 2023.
PCI Security Standards Council, PCI DSS v4.0.1, June 2024, Requirements 6.2.4, 6.4.2 and 11.4, from the document library, and the Penetration Testing Guidance, version 1.1, September 2017.
AICPA, 2017 Trust Services Criteria (With Revised Points of Focus, 2022), criterion CC4.1.
Verizon, 2026 Data Breach Investigations Report, incidents from 1 November 2024 to 31 October 2025.
CISA, Known Exploited Vulnerabilities catalog, version 2026.11.18; and ACSC, CISA and NSA, Preventing Web Application Access Control Abuse (AA23-208A), 27 July 2023.
FIRST, CVSS v4.0 publication announcement, 1 November 2023.
Tool documentation: Burp Suite, Nuclei, ffuf, sqlmap, jwt_tool and Postman.
Stingrai, The State of Penetration Testing 2026: 55 penetration tests and 1,206 verified findings, October 2024 to August 2026.
Talk to Stingrai
Send your application's roles, sensitive flows and release rhythm through Get a Quote, or book a free discovery call to decide whether a one-time Hybrid assessment, continuous Hybrid testing or a fully human-led test fits your application.