Penetration testing, or pen testing, is an authorized, simulated attack on your own systems. Qualified testers try to break into your applications, networks, cloud accounts or people the same way a real attacker would, so you learn which weaknesses can actually be exploited, how far they lead, and how to fix them before somebody else finds them. NIST's glossary puts it as security testing in which evaluators "mimic real-world attacks in an attempt to identify ways to circumvent the security features of an application, system, or network."
Quick answer: A penetration test is a time-boxed, permission-based attack on a defined scope (a web app, an API, a network, a cloud account, your staff) that ends in a report of proven, risk-rated findings with fixes, and a retest to confirm the fixes worked. It differs from a vulnerability scan because the testers exploit and chain the weaknesses instead of just listing them. Buy one when a standard or customer asks for it (PCI DSS Requirement 11.4 requires one at least every 12 months), before a major launch, and after significant change. In Stingrai's own data, 51 of 55 tests (92.7%) found at least one High or Critical issue.
How a penetration test works
Every credible test follows a published methodology (PTES, NIST SP 800-115, the OWASP testing guides or OSSTMM), and every one of them reduces to the same six steps. Our penetration testing methodology guide goes phase by phase with the evidence each step should leave behind; here is the short version.
Scoping and authorization. You agree exactly what is in and out of scope, the testing window, the rules of engagement and who to call if something breaks, and someone entitled to do so signs written permission. This step is what makes it a test and not a crime.
Reconnaissance. The testers map the real attack surface: hosts, subdomains, endpoints, user roles, cloud resources. They usually find assets that were missing from your list.
Vulnerability analysis. Automated scanning plus manual review produces a list of candidate weaknesses, and the false alarms get thrown out.
Exploitation. The testers prove each candidate by safely exploiting it, then chain findings together (for example, a low-severity information leak plus a weak authorization check) to show real business impact.
Reporting. Each finding is risk-rated, with reproduction steps, evidence and a specific fix, plus an executive summary for leadership.
Retest. After you remediate, the testers verify each fix and record it as fixed, partially fixed or still open.
Types of penetration testing
Each type answers a different question about a different attack surface. The active-testing days below are typical published planning ranges from vendor scoping pages, collected in our penetration test timeline guide; real scopes vary.
Type | What it tests | Typical active testing | Service | Deeper guide |
|---|---|---|---|---|
Web application | Logins and sessions, every user role, access control and IDOR, business logic, injection | 2 to 20 days | ||
API | REST and GraphQL endpoints, object-level authorization, tokens, rate limits | 3 to 9 days | ||
Mobile | The iOS or Android app, on-device storage, certificate pinning, and its backend API | 3 to 10 days | ||
External network | Internet-facing hosts, VPNs, remote access, exposed services | 1 to 5 days | ||
Internal network | What an attacker or insider on your network can reach: patching, lateral movement, segmentation | 1 to 10 days | ||
Active Directory | Misconfigurations, ACL abuse, Kerberos and delegation paths to domain admin | Usually scoped with the internal test | ||
Cloud | IAM and role trust, storage and resource policies, managed services on AWS, Azure and Google Cloud | 3 to 5 days for a configuration review | ||
Wireless | Wi-Fi encryption and authentication, guest isolation, rogue access points | Scoped per site | ||
Social engineering | Phishing and vishing campaigns that measure how staff respond and report | Scoped per campaign | ||
Physical | Facility entry, badge and reception controls, on-site devices | Scoped per site | ||
AI and LLM | Prompt injection, data leakage, tool misuse and excessive agency in AI features | 5 to 20 days | ||
Red team | An objective (say, reach the payments database) pursued stealthily to test detection and response | 2 to 14 weeks |
Black box, grey box and white box
The second choice is how much the testers know going in.
Approach | What the testers get | What it is good for |
|---|---|---|
Black box | Nothing beyond the target's address | Modelling an outside attacker with no inside knowledge |
Grey box | Test accounts for each role, and some documentation | The common default for compliance and enterprise-review tests, because it covers what logged-in users can reach |
White box | Source code, architecture diagrams and full access | The deepest coverage per day, especially for authorization and business logic |
What a penetration test actually finds
Most pages describe what a test "can" find. Here is what tests did find. Stingrai analysed 1,206 verified findings from 55 penetration tests run between October 2024 and August 2026 in its State of Penetration Testing 2026 report:
92.7% of tests (51 of 55) surfaced at least one High or Critical finding, and 69.1% surfaced a Critical.
67.2% of all findings (810 of 1,206) were High or Critical.
The mix depends on what you test. Outdated or unpatched software was 56.9% of internal network findings, while authentication and session issues led web application findings at 28.1%.
Only about a third of findings are scanner-shaped. 37.2% fell into classes a scanner could in principle flag; 35.2% needed an understanding of how the application works (authentication, broken access control, object-level authorization, business logic).
0.74% of logged findings were false positives (9 of 1,216), because each finding is reproduced with evidence and reviewed before it reaches the client.
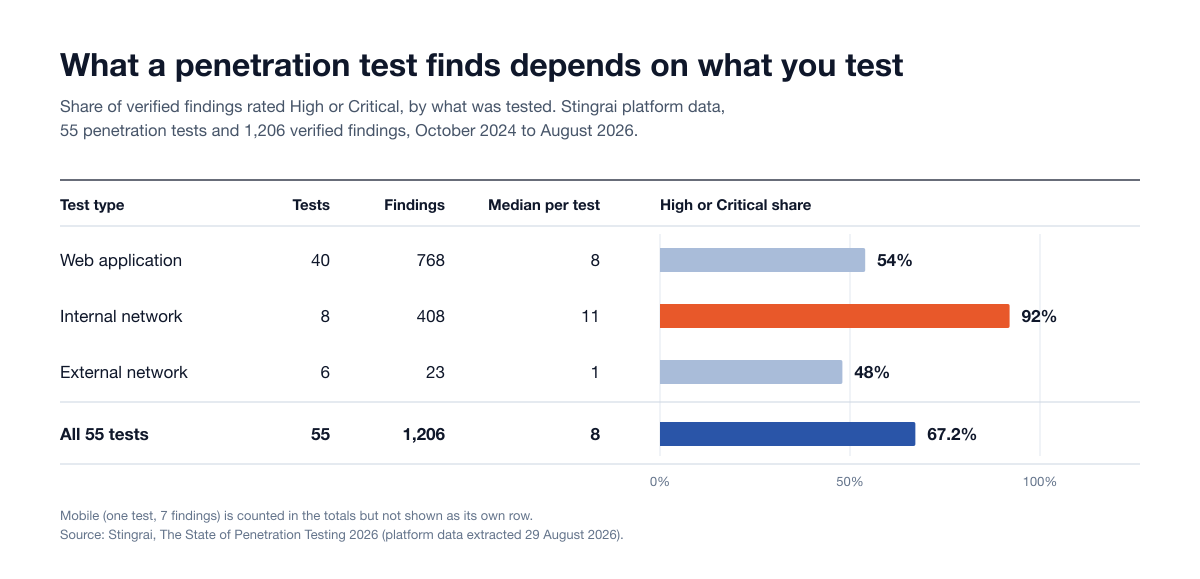
That near-even split between scanner-shaped and context-dependent findings is the practical reason a penetration test is not a vulnerability scan with a nicer report.
Penetration test vs vulnerability scan vs red team
Vulnerability scan | Penetration test | Red team | |
|---|---|---|---|
Question it answers | Which known weaknesses are visible? | Which weaknesses can be exploited, and how far do they lead? | Would we detect and stop a determined attacker? |
Method | Automated tool | Manual exploitation and chaining, plus tools | Stealthy, objective-led campaign across people, process and technology |
Output | A long list, with false positives | Proven, risk-rated findings with evidence, fixes and a retest | An attack narrative and detection gaps |
Typical cadence | Monthly or quarterly | Annually and after significant change | Once a mature security team is in place |
Satisfies PCI DSS 11.4? | No (quarterly scans are Requirement 11.3) | Yes | Not by itself |
For the full comparison, read penetration testing vs vulnerability assessment.
When you need a penetration test
Most companies buy their first test because someone asks for it. Here is what each common driver actually says, as of 25 October 2026.
Driver | What it says about penetration testing | Cadence |
|---|---|---|
PCI DSS v4.0.1 | Requirement 11.4 names it: internal (11.4.2) and external (11.4.3) testing, fix and retest exploitable findings (11.4.4), segmentation testing (11.4.5 and 11.4.6) | At least every 12 months and after significant change; segmentation every six months for service providers |
SOC 2 | Not required. "Penetration testing" appears once in the Trust Services Criteria, as a non-binding point of focus under CC4.1, but auditors expect evaluation evidence and most service organizations choose a test | Whatever your control description says, usually annual |
ISO 27001:2022 | Not named in any clause or Annex A control title; a test is the cleanest evidence for controls such as A.8.8 (technical vulnerabilities) and A.8.29 (security testing) | Set by your own policy and risk assessment |
HIPAA | Not required by the current Security Rule. The proposed rule published 6 January 2025 (90 FR 898) would require a test at least every 12 months; the Federal Register still lists only the proposal | Proposed: at least every 12 months |
NYDFS 23 NYCRR 500.5 | Penetration testing from inside and outside the information systems' boundaries by a qualified internal or external party | At least annually |
Cyber insurance | No carrier publishes a premium discount for a test, but applications ask whether you test, how often and whether it is outsourced (what underwriters ask) | Usually asked as annual or more |
Enterprise customers | Security questionnaires ask for a recent independent report or attestation letter | Usually within the last 12 months |
Outside of compliance, test before a major launch, after a significant architecture change, after an acquisition, and whenever you add something attackers love, such as a payments flow, a public API or an AI feature. Our guide to pentest evidence auditors accept covers each framework in more depth.
What you receive at the end
The end result of a penetration test is evidence you can act on and show to others:
An executive summary that states overall risk in business terms.
Scope and methodology, so an auditor can see exactly what was and was not tested.
Findings, each with a severity (usually CVSS-based), proof such as requests, responses and screenshots, reproduction steps, and specific remediation guidance.
A retest that marks every finding fixed, partially fixed or still open.
An attestation letter in many engagements: a short summary you can hand to a customer or auditor without sharing the full report.
Our penetration testing report sample walks through a real report page by page.
How much a penetration test costs and how long it takes
Cost. Scope sets the price. Stingrai's 2026 US market benchmark, compiled from published vendor pricing and cost guides in our penetration testing cost guide (a benchmark, not Stingrai's price):
Engagement | Typical 2026 cost (USD) |
|---|---|
Web application | US$5,000 to US$30,000 |
Network (external or internal) | US$5,000 to US$40,000 |
API | US$6,000 to US$30,000 |
Mobile application (per platform) | US$7,000 to US$35,000 |
Cloud (IaaS or PaaS) | US$10,000 to US$50,000 |
Enterprise program (annual) | US$50,000 to US$150,000+ |
Stingrai publishes two fixed prices on its pricing page, both for one web application and associated APIs: the Autonomous Pentest (Snipe, Stingrai's AI agent, on its own, with a pentest report) at US$3,000 one-time or US$650 a month on a 12-month plan, and the Hybrid Pentest (Snipe and human penetration testers working together, with a human-validated report and an attestation letter) at US$6,800 one-time or US$1,275 a month. Every other scope is quoted.
Duration. Active testing is the short part: about 1 to 5 days for an external network, 1 to 10 for an internal network, and 2 to 20 for a web application, per published scoping ranges. Scoping, scheduling, reporting and the retest stretch the whole project to about 4 to 8 weeks of calendar time, so book early if an audit date is fixed. Our timeline guide breaks down every phase.
Who performs a penetration test
Look for two things: certified individuals and an accountable firm. Individual certifications such as OSCP, OSWE, OSEP, OSCE³ and CREST CRT show hands-on exploitation skill. Firm-level accreditation, such as CREST accreditation of the company itself, shows audited methodology, data handling and quality control. Ask who will actually test, whether findings are reproduced before they reach you, and whether the retest is included.
Where Stingrai fits: Stingrai is a CREST-accredited penetration testing company, accredited for both Penetration Testing and AI-Enabled Penetration Testing, offering fully human-led and hybrid (human penetration testers plus AI agents) penetration tests, delivered by experienced penetration testers who are also world-class security researchers and bug bounty hunters, with OSCE³, OSWE, OSEP and CREST CRT certifications across the team. Founded in Toronto, Canada in 2021, it is trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA, with engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
On human-led work, two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications, with 18 published CVEs across the team, test every user role and chain broken authorization, IDOR and business logic issues into real attack paths. Findings appear in the PTaaS portal as they are confirmed, each with a working proof of concept, so fixing starts before the report lands, and retesting is included. For web applications and associated APIs, Snipe is Stingrai's autonomous agent, trained on 6,000+ public HackerOne disclosure reports and on Stingrai's testers' methodology to hunt the context-dependent classes (IDOR, broken authorization, business logic) that scanners miss. Engagements run one-time (annual) or as continuous programs.
Frequently Asked Questions
What is penetration testing?
Penetration testing is an authorized, simulated attack on your own systems in which qualified testers try to exploit weaknesses the way a real attacker would. The goal is to prove which vulnerabilities are actually exploitable, show their business impact, and give you specific fixes, then confirm those fixes with a retest.
What is the end result of a penetration test?
The end result is a report of proven, risk-rated findings, each with evidence, reproduction steps and remediation guidance, plus an executive summary and a statement of scope and methodology. Most engagements add a retest that marks each finding fixed or still open, and many include an attestation letter you can share with customers and auditors.
Is penetration testing legal?
Yes, when the owner of the systems gives written authorization for a defined scope. The same activity without permission is a crime: in the US the Computer Fraud and Abuse Act (18 U.S.C. 1030) covers accessing a computer "without authorization", and in Canada section 342.1 of the Criminal Code covers unauthorized use of a computer. That is why scoping and signed rules of engagement come first.
How much does a penetration test cost?
Most standard US penetration tests cost about US$5,000 to US$50,000, with a web application at about US$5,000 to US$30,000 and annual enterprise programs at US$50,000 to US$150,000 or more, per Stingrai's 2026 market benchmark. Stingrai's published prices for one web application and associated APIs are US$3,000 (Autonomous Pentest) and US$6,800 (Hybrid Pentest).
How long does a penetration test take?
Active testing usually takes 1 to 20 days depending on scope: about 1 to 5 days for an external network and 2 to 20 for a web application. The whole project, from scoping to the delivered report, typically takes 4 to 8 weeks of calendar time, and red team work runs 2 to 14 weeks.
How often should you do a penetration test?
At least once a year and after any significant change to the systems in scope. PCI DSS Requirement 11.4 and NYDFS 500.5 set that annual minimum in their text, and SOC 2 and ISO 27001 programs usually adopt it through their own control descriptions and policies.
What is the difference between a penetration test and a vulnerability scan?
A vulnerability scan is automated and lists known weaknesses it can see, including false positives. A penetration test has people (often working with AI agents) exploit and chain those weaknesses to prove impact, and it finds the authorization and business logic flaws that scanners cannot model. In Stingrai's data, 35.2% of findings fell into those context-dependent classes.
Related reading
Penetration Testing Methodology (2026): PTES, NIST, OWASP, OSSTMM and ATT&CK, Phase by Phase
How Often Should You Do Penetration Testing? Frequency by Framework and Risk (2026)
Penetration Testing Cost in the US (2026): Prices by Scope and Compliance Driver
How Long Does a Penetration Test Take? (2026) Timelines by Scope, From Scoping to Retest
The State of Penetration Testing 2026: An Analysis of 1,206 Verified Findings
Black Box vs Grey Box vs White Box Penetration Testing: Which to Buy
Automated Penetration Testing (2026): What It Is, What It Finds and What It Misses
Benefits of Penetration Testing (2026): 5 Reasons Companies Test, With Data