The OWASP Top 10 is the Open Worldwide Application Security Project's list of the ten most critical security risks to web applications, and the 2025 edition, the eighth since the list began in 2003, is the current one. Broken access control stays at number one: OWASP's A01 page says "100% of the applications tested were found to have some form of broken access control." The 2025 list draws on test data from more than 2.8 million applications, adds two new categories and folds server-side request forgery into access control.
Quick answer. The OWASP Top 10:2025, in order, is A01 Broken Access Control, A02 Security Misconfiguration, A03 Software Supply Chain Failures, A04 Cryptographic Failures, A05 Injection, A06 Insecure Design, A07 Authentication Failures, A08 Software or Data Integrity Failures, A09 Security Logging and Alerting Failures and A10 Mishandling of Exceptional Conditions. It replaces the 2021 list, which OWASP marks as superseded. Scanners find part of the ten; access control, business logic, authentication flows and error handling need a penetration tester, which is why Stingrai's Hybrid Pentest puts its Snipe agent and certified penetration testers on the same application.
What is the OWASP Top 10?
The OWASP Top 10 is a list of the ten most critical security risks to web applications, published by the OWASP Foundation. OWASP calls it "a standard awareness document for developers and web application security" that "represents a broad consensus about the most critical security risks to web applications." Older documents spell the name out as the Open Web Application Security Project.
Each entry is a risk category, not a single bug. A category groups related weaknesses from MITRE's Common Weakness Enumeration (CWE); A01 alone maps 40.
It is not published every year. The three most recent editions are 2017, 2021 and 2025. There is no 2022, 2023 or 2024 edition.
It is an awareness document first. As a coding or testing standard, OWASP says, "it is the bare minimum and just a starting point."
OWASP announced the 2025 release candidate on 6 November 2025 and took comments until 20 November 2025. Since 24 December 2025 the OWASP Top 10 project page has named 2025 "the most current released version," and the project's GitHub README marks 2021 "SUPERSEDED".
The OWASP Top 10 2025 list
Names and order are from the OWASP Top 10:2025; CWE counts are from the score table on each category page.
ID | Category | What it means | CWEs mapped |
|---|---|---|---|
A01:2025 | Broken Access Control | Users act outside their intended permissions, including IDOR, CSRF and SSRF. | 40 |
A02:2025 | Security Misconfiguration | Systems, applications or cloud services are set up insecurely, including XXE. | 16 |
A03:2025 | Software Supply Chain Failures | Vulnerable, malicious or compromised dependencies, builds and distribution. | 6 |
A04:2025 | Cryptographic Failures | Missing or weak cryptography, and keys that leak. | 32 |
A05:2025 | Injection | Untrusted input runs as a command, including SQL injection and XSS. | 37 |
A06:2025 | Insecure Design | A needed control was never designed, including business logic flaws. | 39 |
A07:2025 | Authentication Failures | The system accepts the wrong person as a legitimate user. | 36 |
A08:2025 | Software or Data Integrity Failures | Code or data is trusted without an integrity check, including insecure deserialization. | 14 |
A09:2025 | Security Logging and Alerting Failures | Attacks go unlogged, unnoticed or unanswered. | 5 |
A10:2025 | Mishandling of Exceptional Conditions | Errors are handled badly, including security checks that fail open. | 24 |
What changed from the OWASP Top 10 2021 to 2025?
OWASP's own summary is one sentence: "There are two new categories and one consolidation in the Top Ten for 2025." The table gives every move, with the CWE counts from the score tables of both editions.
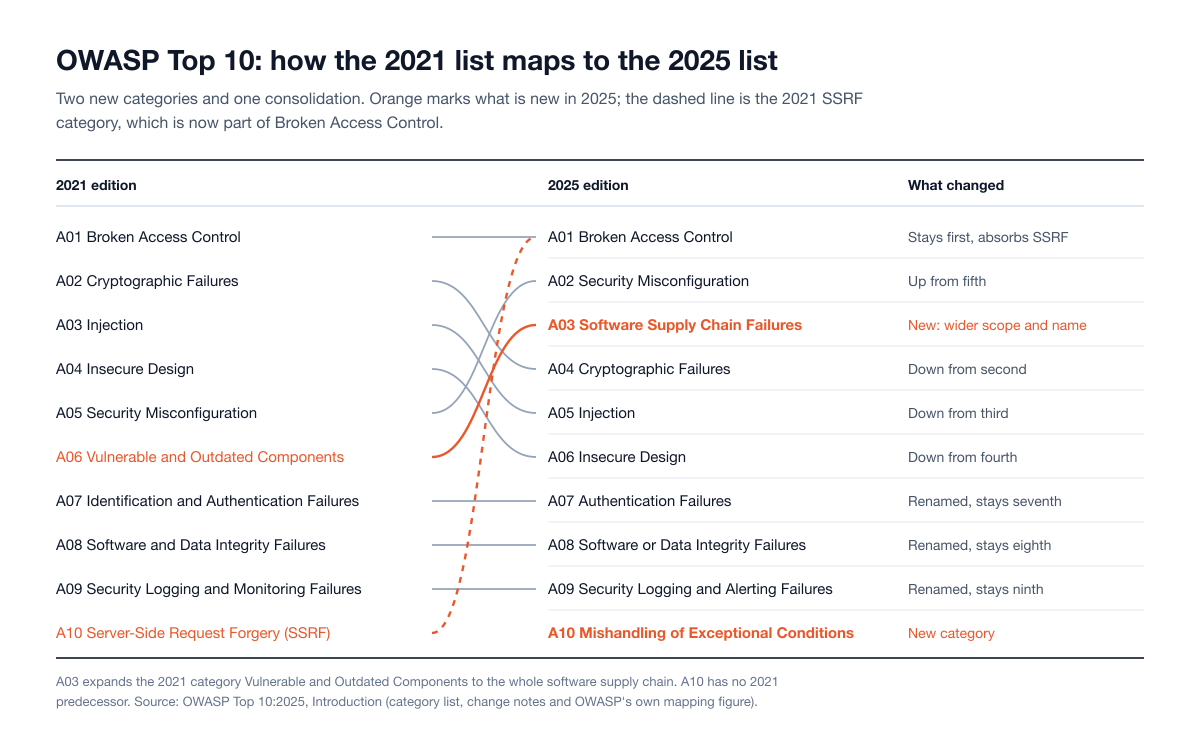
Figure 1: The 2021 list mapped to the 2025 list. Source: OWASP Top 10:2025, Introduction.
2021 category | 2025 category | Change | CWEs mapped, 2021 to 2025 |
|---|---|---|---|
A01 Broken Access Control | A01 Broken Access Control | Stays first; absorbs SSRF | 34 to 40 |
A02 Cryptographic Failures | A04 Cryptographic Failures | Down two places | 29 to 32 |
A03 Injection | A05 Injection | Down two places | 33 to 37 |
A04 Insecure Design | A06 Insecure Design | Down two places | 40 to 39 |
A05 Security Misconfiguration | A02 Security Misconfiguration | Up three places | 20 to 16 |
A06 Vulnerable and Outdated Components | A03 Software Supply Chain Failures | New name and wider scope; OWASP counts it as new | 3 to 6 |
A07 Identification and Authentication Failures | A07 Authentication Failures | Renamed | 22 to 36 |
A08 Software and Data Integrity Failures | A08 Software or Data Integrity Failures | Renamed | 10 to 14 |
A09 Security Logging and Monitoring Failures | A09 Security Logging and Alerting Failures | Renamed | 4 to 5 |
A10 Server-Side Request Forgery (SSRF) | Part of A01 | Consolidated | 1, now inside A01 |
None | A10 Mishandling of Exceptional Conditions | New category | 24 |
A03 is an expansion, not a rename. OWASP calls it "an expansion of A06:2021-Vulnerable and Outdated Components" to compromises across "the entire ecosystem of software dependencies, build systems, and distribution infrastructure."
A10 has no 2021 predecessor. It covers "improper error handling, logical errors, failing open, and other related scenarios."
SSRF lost its own slot. A single-CWE category added from the 2021 community survey, it "has been rolled into" A01.
Misconfiguration rose because it was more prevalent in the data, which OWASP calls unsurprising as "software engineering is continuing to increase the amount of an application's behavior that is based on configurations." Of Insecure Design, which fell two places, OWASP reports "noticeable improvements in the industry related to threat modeling."
Three renames kept their positions. A07 drops "Identification and", A08 swaps "and" for "or", and A09 swaps "Monitoring" for "Alerting": "Great logging with no alerting is of minimal value in identifying security incidents."
The method changed less than the list: both editions took eight categories from contributed data and two from a community survey. What grew is the evidence.
Measure | 2021 edition | 2025 edition |
|---|---|---|
Applications in the contributed data | Over 500,000 | Over 2.8 million |
CWEs analyzed | Almost 400 | 589 |
CWEs mapped into the ten categories | 196 (average 19.6) | 248 (average 25), capped at 40 per category |
CVE records mapped to CWEs in NVD | About 125,000 | About 175,000 |
Categories placed by the survey | A09 Logging, A10 SSRF | A03 Supply Chain, A09 Logging |
Policies, report templates and scanner profiles that still cite A03:2021 Injection or A10:2021 SSRF now point at superseded identifiers.
Where familiar vulnerabilities sit in 2025
Each weakness below appears in the mapped CWE list of the category shown.
Vulnerability | CWE | 2025 category |
|---|---|---|
CWE-639 | A01 Broken Access Control | |
Cross-site request forgery (CSRF) | CWE-352 | A01 Broken Access Control |
CWE-918 | A01 Broken Access Control | |
Path traversal | CWE-22 | A01 Broken Access Control |
XML external entities (XXE) | CWE-611 | A02 Security Misconfiguration |
CWE-79 | A05 Injection | |
SQL injection | CWE-89 | A05 Injection |
Unrestricted file upload | CWE-434 | A06 Insecure Design |
Session fixation | CWE-384 | A07 Authentication Failures |
Insecure deserialization | CWE-502 | A08 Software or Data Integrity Failures |
Mass assignment | CWE-915 | A08 Software or Data Integrity Failures |
Error messages that leak sensitive information | CWE-209 | A10 Mishandling of Exceptional Conditions |
APIs have their own OWASP API Security Top 10 and mobile apps the OWASP Mobile Top 10; for LLM applications, the A05 page points to LLM01:2025 Prompt Injection.
The data behind the 2025 list
OWASP says the list "remains data-informed, but not blindly data-driven." Contributors reported how many applications they tested each year from 2021 and how many had at least one instance of each CWE, so 4,000 instances in one application count once. CVSS scores from NVD supply exploit and impact, and the survey covers what test data cannot see yet.
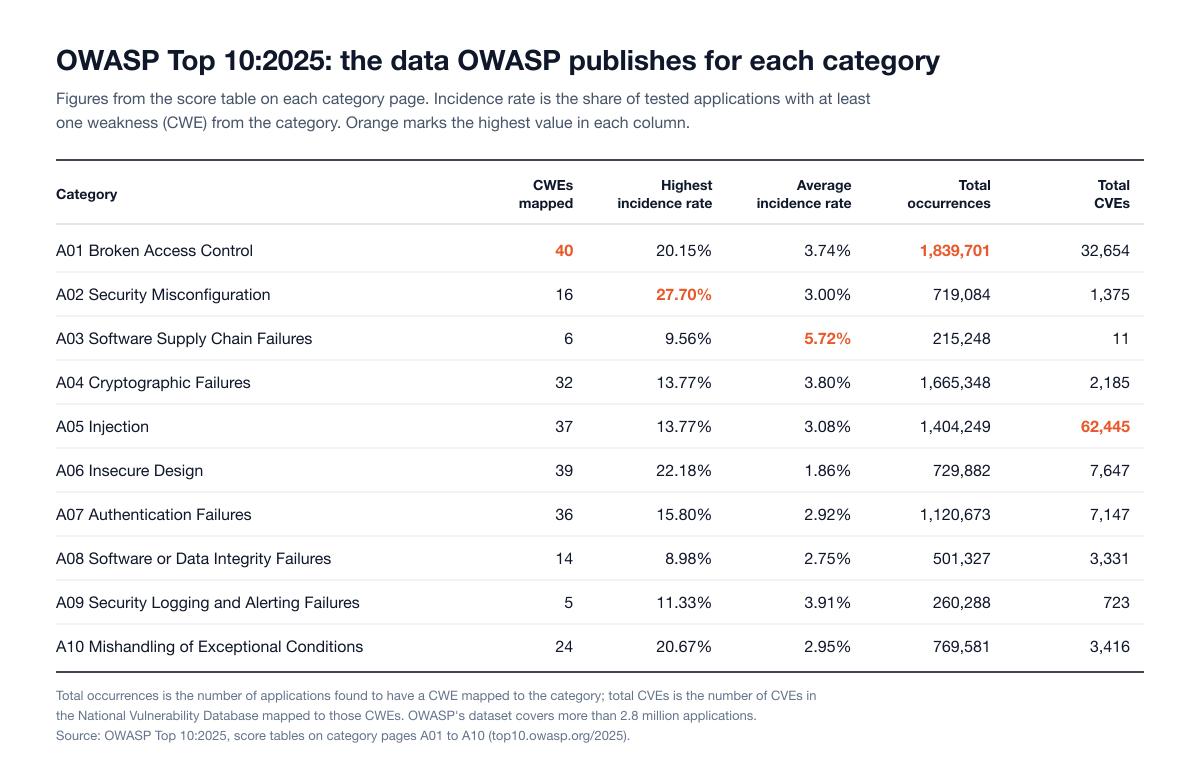
Figure 2: OWASP's published data for each 2025 category. Source: OWASP Top 10:2025, category pages A01 to A10.
Broken access control has the most occurrences (1,839,701) and the second-most CVEs.
Injection has the most CVEs (62,445): cross-site scripting is "high frequency/low impact" and SQL injection "low frequency/high impact".
Supply chain failures have 11 CVEs and the fewest occurrences, yet exactly 50% of survey respondents ranked the category first. OWASP's introduction attributes the thin data to "challenges in testing."
OWASP's pages do not agree on every digit. The introduction gives 5 CWEs for A03 and 38 for A05, where the category pages list 6 and 37, and the ten mapped lists total 249 against the introduction's 248. On the A03 page, the text gives an average incidence rate of 5.19% while the score table on the same page gives 5.72%; on either figure A03 has the highest average of the ten. This guide uses the score tables.
The headline 100% needs the same care. The A01 and A02 pages say 100% of the applications tested had some form of the weakness, but their score tables give highest incidence rates of 20.15% and 27.70%; the 100% matches the tables' maximum coverage, which OWASP defines as the "percentage of applications tested by all organizations for a given CWE." Quote the 100% as OWASP's sentence, and use incidence rates for a measured share.
Three risks narrowly missed the list: X01 Lack of Application Resilience, X02 Memory Management Failures and X03 Inappropriate Trust in AI Generated Code ("Vibe Coding"), the subject of our security checklist for AI-built apps.
The ten OWASP Top 10 2025 categories: a documented case, the test and the fix
The tests follow OWASP's Web Security Testing Guide; our guide to web application penetration testing covers the full method.
A01:2025 Broken Access Control
What it means. A user reads another customer's records, reaches an admin function or calls an API method the interface never offers. The A01 page lists insecure direct object references, forced browsing, privilege escalation, token tampering and CORS misconfiguration, and names SSRF and CSRF among its notable CWEs.
Documented case. In July 2025 the hiring platform Paradox confirmed that two researchers had reached "an API endpoint vulnerability" exposing chat records in one client instance, which they described as an insecure direct object reference on an internal API. Paradox added: "none of our penetration tests previously identified the issue."
The test. The tester holds at least two accounts per role and, for multi-tenant products, a second tenant, then replays every request as each other identity for every operation. Privileged routes are requested with no session and a low-privilege one, and server-side URL fetches are tested against targets agreed in the rules of engagement.
The fix. "Except for public resources, deny by default." Enforce checks once in trusted server-side code, check record ownership rather than role alone, and put access control cases into unit and integration tests.
A02:2025 Security Misconfiguration
What it means. Default accounts left enabled, sample content and debug features installed, stack traces shown to users, security headers missing, cloud storage open. XXE has sat here since 2021. The A02 page says "100% of the applications tested were found to have some form of misconfiguration."
Documented case. A joint NSA and CISA advisory of 5 October 2023, built from the agencies' red and blue team assessments, lists default configurations of software and applications among the "10 most common network misconfigurations" in large organizations, with default credentials as the item's first example. The Paradox incident above began with a similar lapse, a test account whose password was never updated.
The test. Everything the deployment exposes beyond the application: default content, admin consoles, directory listings, debug endpoints, verbose errors, security headers, cookie attributes, CORS policy, XML parser settings and the cloud storage the application uses.
The fix. An automated hardening process, a minimal platform, identical configuration across environments with different credentials, and an automated check that settings work. Without automation, OWASP says, verify manually "annually at a minimum."
A03:2025 Software Supply Chain Failures
What it means. Something fails in building, distributing or updating software: a vulnerable or abandoned dependency, a malicious package, a compromised pipeline. The A03 page extends the old "components with known vulnerabilities" idea to developer workstations, IDE extensions, CI/CD systems and artifact repositories.
Documented case. On 23 September 2025 CISA warned that a self-replicating npm worm, Shai-Hulud, "has compromised over 500 packages," harvesting GitHub tokens and cloud API keys and publishing infected versions of other packages with stolen npm credentials. Our Shai-Hulud checklist tracks the later waves.
The test. The tester fingerprints libraries and server components and confirms whether a known-vulnerable one is reachable and exploitable, rather than reporting version numbers. Third-party scripts without integrity checks and exposed source maps are in scope; lockfiles, publishing rights and CI secrets need source and configuration access.
The fix. An SBOM that includes transitive dependencies, continuous monitoring of CVE, NVD and OSV sources, signed components from official sources, staged rollouts, and MFA on repositories and CI/CD.
A04:2025 Cryptographic Failures
What it means. Data that should be encrypted is not, the cryptography is weak, or the keys leak. The A04 page covers unenforced transport encryption, old algorithms, default or reused keys, keys in source code, predictable randomness and weak password hashing.
Documented case. In February 2025 Microsoft Threat Intelligence reported that developers had copied ASP.NET machine keys from public documentation and repositories. It found more than 3,000 publicly disclosed keys usable for ViewState code injection, and saw one used in December 2024 to deliver a post-exploitation framework.
The test. TLS configuration and HSTS, cookie attributes, sensitive data in URLs or caches, the predictability of tokens and reset links, JWT signature and algorithm validation, and searches of client-side code and public repositories for keys.
The fix. TLS 1.2 or later enforced with HSTS, authenticated encryption, adaptive salted password hashing such as Argon2, scrypt or PBKDF2-HMAC-SHA-512, and random keys that are rotated and never copied from public sources.
A05:2025 Injection
What it means. Untrusted input reaches an interpreter and runs as part of a command: a database, the operating system, LDAP or the browser, which is why cross-site scripting belongs here (A05 page).
Documented case. A CISA and FBI advisory reports that the CL0P ransomware group began exploiting a previously unknown SQL injection flaw in MOVEit Transfer, CVE-2023-34362, on 27 May 2023, installing a web shell and stealing data. A later Secure by Design alert notes SQL injection has been called "unforgivable" since at least 2007.
The test. Every input is mapped: parameters, headers, cookies, JSON and XML bodies, file names and uploads. OWASP says detection "is best achieved by a combination of source code review along with automated testing (including fuzzing)." The tester confirms each candidate with a harmless proof and shows what data is reachable. Our XSS guide covers the browser side.
The fix. Parameterized interfaces, server-side validation against what is allowed, and output encoding for the context. Stored procedures can still be injectable, and table or column names must never come from user input.
A06:2025 Insecure Design
What it means. The control that should stop an attack was never designed; an insecure design "cannot be fixed by a perfect implementation," says the A06 page. Business logic flaws, such as steps completed out of order or limits bypassed by repeating a request, sit here.
Documented case. In May 2015 the US Internal Revenue Service said criminals had used data stolen elsewhere to pass the identity checks on its Get Transcript application, including personal verification questions. By February 2016 it had identified approximately 114,000, then a further 220,000, then a further 390,000 taxpayer accounts that may have been accessed. The checks worked as designed; the design was the flaw.
The test. Skipped or repeated steps, parallel requests against one balance or coupon, negative quantities and recovery paths. OWASP says insecure design "is beyond the scope of most forms of testing": a test proves the exploitable consequences, and threat modeling finds the rest.
The fix. Threat model critical flows, use secure design patterns, add plausibility checks at each tier, write misuse cases next to use cases, and segregate tenants by design.
A07:2025 Authentication Failures
What it means. The system accepts the wrong person as a legitimate user. The A07 page lists unblocked credential stuffing and password spraying, weak or default passwords, weak recovery flows, missing or ineffective MFA, and sessions that survive logout.
Documented case. The UK Information Commissioner's Office announced on 17 June 2025 a £2.31 million fine on 23andMe after a credential stuffing attack between April and September 2023 reached personal information belonging to 155,592 UK residents. The company lacked measures "such as mandatory multi-factor authentication, secure password protocols, or unpredictable usernames."
The test. Login, registration, recovery and MFA flows: username enumeration, lockout and rate limiting within agreed limits, breached passwords, MFA that can be skipped or downgraded, session ID rotation at login, and whether logout ends the session on the server. See also our guide to password spraying.
The fix. Enforce MFA, ship no default credentials, check new passwords against breached lists, follow NIST SP 800-63B, return the same message for every login outcome, and issue a new session ID after login.
A08:2025 Software or Data Integrity Failures
What it means. Code or data is trusted without checking that it is genuine: untrusted plugins, unverified updates, pipelines that fetch unverified artifacts, and insecure deserialization. The A08 page places it "at a lower level than Software Supply Chain Failures."
Documented case. On 3 December 2025 the React team disclosed CVE-2025-55182, an unauthenticated remote code execution flaw in React Server Components rated CVSS 10.0. The NVD record classifies it as CWE-502, deserialization of untrusted data, and CISA added it to its Known Exploited Vulnerabilities catalog on 5 December 2025, two days after disclosure.
The test. Serialized objects and state that pass through the client are tampered with to see whether the server notices. Update requests carry fields the interface never offers, such as role, price or owner, to see whether the server binds them. Third-party scripts are checked for integrity attributes.
The fix. Verify software and data with signatures, consume dependencies only from trusted repositories, lock down CI/CD, never deserialize untrusted data without an integrity check, and bind only the fields a user may set.
A09:2025 Security Logging and Alerting Failures
What it means. An attack happens and nobody notices, or somebody notices and nothing follows. The A09 page lists unlogged logins and high-value transactions, unmonitored logs, missing alert thresholds, and penetration tests and scans that "do not trigger alerts."
Documented case. The ICO's penalty notice to British Airways, dated 16 October 2020, records that an attacker kept access "undetected between 22 June and 5 September 2018" and altered a JavaScript file on the airline's website to skim payment card data. BA "were not generating or monitoring logs to a sufficient level," the regulator found, and it set the penalty at £20 million.
The test. A test doubles as a detection drill: the tester keeps a timestamped record of noisy actions, and the client compares it with what was logged and what alerted. OWASP notes the limit: testers "may only be able to determine that they have invoked incident response in a test environment." Whole-environment detection is a red team question.
The fix. Log logins, access control failures and input validation failures with user context, protect logs against tampering, define alerting use cases with playbooks, and plant honeytokens.
A10:2025 Mishandling of Exceptional Conditions
What it means. The application meets a situation its authors did not expect and responds badly. The A10 page covers unhandled exceptions, errors that reveal internals, missing parameters, partial transactions that are not rolled back, and security checks that fail open.
Documented case. Cloudflare's post-mortem of its 18 November 2025 outage states it was not caused by malicious activity: a configuration file doubled in size, exceeded a limit of 200 features and triggered an unhandled error that returned HTTP 5xx responses across its network. In an application, the same mistake becomes a security flaw when the failing path is an authorization check or a payment step.
The test. Malformed, missing, duplicated, oversized and out-of-order input, plus interrupted multi-step transactions. Does the application fail closed, does the error reveal stack traces or queries, and is the system left in a consistent state?
The fix. Catch errors where they occur with a global handler behind them, roll back whole transactions on failure, show users generic messages while logging the detail, and set rate limits so nothing is limitless.
OWASP Top 10 test coverage: what scanners find and what needs a penetration tester
OWASP is plain about the limits of automation. Its 2025 introduction says "the results in the data are largely limited to what the industry can test for in an automated fashion," and its program guidance adds: "Tools cannot comprehensively detect, test, or protect against the OWASP Top 10 due to the nature of several of the OWASP Top 10 risks." The matrix shows, for each category, what automated tools find, what needs a penetration tester, and how Stingrai's Hybrid Pentest covers it. Quoted phrases are OWASP's; everything else in the table is Stingrai's assessment.
Category | What automated tools find | What needs a penetration tester | How the Hybrid Pentest covers it |
|---|---|---|---|
A01 Broken Access Control | Directory listings and exposed .git metadata; access rules written into unit and integration tests, as OWASP asks | Whether one user can read or change another's data, cross-tenant access, function-level escalation | Snipe and the penetration testers test object- and function-level authorization across the roles in scope; testers chain findings into escalation paths |
A02 Security Misconfiguration | Missing headers, default content, verbose errors; OWASP asks for "an automated process to verify the effectiveness of the configurations" | Whether an exposed setting is exploitable, such as a debug endpoint that leaks secrets | Both test what the deployment exposes; on a continuous plan, monthly Snipe testing repeats the check as the configuration changes |
A03 Software Supply Chain Failures | Known-vulnerable components, through software composition analysis and SBOM tools such as OWASP Dependency Check | Whether a vulnerable component is reachable and exploitable in this application | Deployed components fingerprinted and reachable flaws confirmed in the running application |
A04 Cryptographic Failures | TLS protocols, ciphers and HSTS ("Check everything with a tool"); secret scanners for keys in code | Predictable tokens and reset links, JWT validation flaws, what a weakness lets an attacker forge | Transport, tokens and exposed keys tested live; with repository access, source review shows where keys come from |
A05 Injection | Many injection flaws, through SAST, DAST and IAST and "automated testing (including fuzzing)" | Second-order and context-specific injection, and a harmless proof of what data is reachable | Snipe's injection agents and the testers work every input, and testers validate and chain findings; with repository access, data flows are traced to their sinks |
A06 Insecure Design | Little: secure design "is neither an add-on nor a tool that you can add to software" | Business logic abuse: skipped steps, races, negative quantities, recovery flows | Business logic and workflow abuse tested across roles: skipped steps, races, limits and recovery flows |
A07 Authentication Failures | Cookie and session attributes, password policy, some lockout behavior | MFA bypass or downgrade, weak recovery, session fixation, logout that leaves the session alive | Login, session, MFA and recovery flows tested with an account for each role, within agreed rate limits |
A08 Software or Data Integrity Failures | Third-party scripts without integrity attributes; components with known deserialization flaws | Mass assignment of role, price or owner fields; tampered serialized state the server accepts | Object binding and client-held state tested on write operations, and third-party scripts checked for integrity attributes |
A09 Security Logging and Alerting Failures | Static analysis can "look for the absence of logging," but it may be impossible to tell whether access control failures are logged | Whether the test was detected, which OWASP says a tester may only confirm "in a test environment" | Findings reach the PTaaS portal as they are confirmed, a dated record to compare with your alerts |
A10 Mishandling of Exceptional Conditions | Fuzzers trigger unhandled exceptions and verbose errors | Fail-open checks, partial transactions completed twice, errors that leak internals mid-flow | Malformed, missing and out-of-order input and interrupted flows tested; with repository access, exception paths are reviewed in source |
Tools are strong where a flaw has a recognizable signature; testers are needed where the question is who may do what, and in what order. Our DAST vs penetration testing comparison goes class by class, and the web application security assessment guide sets SAST, SCA, DAST, IAST and manual testing side by side.
Does a penetration test cover the OWASP Top 10?
Not by itself, and OWASP says so. Its table of recommended uses rates penetration testing against the Top 10 as "Bare minimum" (against "Yes" for ASVS) and adds: "OWASP discourages any claims of full coverage of the OWASP Top 10, because it's simply untrue."
Stingrai's own data shows where findings land. In our State of Penetration Testing 2026 dataset, 40 web application penetration tests produced 768 verified findings, led by authentication and session issues (28.1%), misconfiguration and hardening (14.2%) and information disclosure (12.5%), with broken access control at 9.9% and IDOR at 7.9%. Of the 40 tests, 70% surfaced at least one High or Critical authentication or authorization finding. Those flaws depend on knowing the application, which is why scanners miss them.
Three questions turn "tested against the OWASP Top 10" into something a buyer can verify: which roles and tenants were tested, which categories were covered by testing and which by review, and what evidence shows a control passed rather than only where one failed.
OWASP Top 10 vs ASVS 5.0
The Top 10 tells a team what to worry about; the Application Security Verification Standard (ASVS) tells it what to verify. OWASP: "We would encourage anyone wanting to adopt an application security standard to use the OWASP Application Security Verification Standard (ASVS), as it's designed to be verifiable and tested." ASVS 5.0.0, dated May 2025, is the latest stable version; its requirements file holds 345 requirements across 17 chapters, 70 at Level 1, 183 at Level 2 and 92 at Level 3.
Most category pages cite the matching ASVS chapter: V8 Authorization for A01, V13 Configuration for A02, V15 Secure Coding and Architecture for A03, V11 Cryptography, V12 Secure Communication and V14 Data Protection for A04, V16 Security Logging and Error Handling for A09, and V16.5 Error Handling for A10. The A05 page cites "V5 Input Validation and Encoding", a chapter name ASVS 5.0 no longer uses; its injection chapters are V1 Encoding and Sanitization and V2 Validation and Business Logic. A06, A07 and A08 cite none. ASVS adds that verification "may require access to documentation, source code, configuration, and the people involved in the development process." Our ASVS 5.0 acceptance matrix shows how to write those requirements into a statement of work.
The OWASP Top 10 in PCI DSS and other frameworks
PCI DSS v4.0.1 Requirement 6.2.4 requires software engineering techniques "to prevent or mitigate common software attacks and related vulnerabilities in bespoke and custom software," and lists the classes itself: injection, attacks on data and data structures, cryptography usage, business logic (including XSS and CSRF), access control mechanisms, and high-risk vulnerabilities from Requirement 6.3.1. It does not name OWASP. Requirement 11.4.1 requires "Application-layer penetration testing to identify, at a minimum, the vulnerabilities listed in Requirement 6.2.4."
The Top 10 appears by name in the PCI Security Standards Council's Penetration Testing Guidance (version 1.1, September 2017), which suggests discussing "the penetration tester's familiarity with testing to validate the OWASP Top 10 and other similar application secure-coding standards." A PCI DSS report should therefore map to the 6.2.4 list, not the Top 10 alone, as our PCI DSS penetration testing guide explains. For cadence, OWASP's own program guidance lists "At least annual penetration testing (depending upon the level assurance required for your app)."
How Stingrai tests web applications against the OWASP Top 10
Stingrai is a proud CREST member. Stingrai Inc holds two CREST accreditations, Penetration Testing and AI-Enabled Penetration Testing, and the company certification CREST AI Charter, as its CREST Marketplace listing shows. Its web application penetration tests are authenticated across every user role in scope and cover broken authorization and IDOR, business logic, injection, and authentication and session handling, aligned to the OWASP Top 10 and ASVS and source-assisted where repository access is given.
Human-led and hybrid engagements are staffed by two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications, with 18 published CVEs across the team. Findings reach the PTaaS portal as they are confirmed, retesting is included, and every human-led and hybrid report ships with an attestation letter that supports SOC 2, ISO 27001, PCI DSS and HIPAA programs. Engagements run as one-time (annual) tests or continuous programs.
The Hybrid Pentest, one-time or continuous
The Hybrid Pentest is built for the gap the matrix shows. Snipe, Stingrai's autonomous agent for web applications and associated APIs, tests the full application while Stingrai's certified penetration testers test the same application manually alongside it and validate Snipe's findings, so coverage is wider and deeper. It is not a split of test classes.
Package | Who tests | Price for one web application and associated APIs |
|---|---|---|
Hybrid Pentest, continuous | Monthly Snipe testing, human-verified, plus a quarterly deep dive by Stingrai's penetration testers | US$1,275 per month on a 12-month plan |
Hybrid Pentest, one-time | Snipe and Stingrai's certified penetration testers on the same application, followed by 12 monthly Snipe scans | US$6,800 per assessment |
Continuous is the stronger fit for most applications, and the cases above show why. The React Server Components flaw went from disclosure to CISA's exploited list in two days. Shai-Hulud compromised more than 500 npm packages in one campaign, any of which could enter an application with its next build. And OWASP moved misconfiguration to second as more application behavior comes to depend on configuration, which changes with every deploy. An annual test sees one version of an application; monthly human-verified testing with a quarterly deep dive follows the application as it changes through the year. A one-time Hybrid assessment suits an application that changes rarely, or a point-in-time report before a customer review.
Compare the plans on the pricing page or send your roles and release rhythm through Get a Quote; our scope and cost guide covers larger engagements.
Frequently Asked Questions
What is the OWASP Top 10?
The OWASP Top 10 is the OWASP Foundation's list of the ten most critical security risks to web applications. OWASP, the Open Worldwide Application Security Project, calls it a standard awareness document for developers and web application security. Each entry is a category of related weaknesses, not a single bug. The current edition is the OWASP Top 10:2025, built on test data from more than 2.8 million applications.
What are the OWASP Top 10 2025 categories?
In order: A01 Broken Access Control, A02 Security Misconfiguration, A03 Software Supply Chain Failures, A04 Cryptographic Failures, A05 Injection, A06 Insecure Design, A07 Authentication Failures, A08 Software or Data Integrity Failures, A09 Security Logging and Alerting Failures, and A10 Mishandling of Exceptional Conditions.
What changed between the OWASP Top 10 2021 and 2025?
OWASP summarizes it as two new categories and one consolidation. A03 Software Supply Chain Failures expands the 2021 category Vulnerable and Outdated Components, A10 Mishandling of Exceptional Conditions is new, and server-side request forgery, A10 in 2021, is now part of A01 Broken Access Control. Security Misconfiguration rose from fifth to second, Cryptographic Failures, Injection and Insecure Design each dropped two places, and A07, A08 and A09 were renamed.
When was the OWASP Top 10 2025 released?
OWASP announced the release candidate on 6 November 2025 and took comments until 20 November 2025. Since 24 December 2025 the OWASP Top 10 project page has named the 2025 edition the most current released version.
Is there an OWASP Top 10 for 2024?
No. The OWASP Top 10 is not published every year. The three most recent editions are 2017, 2021 and 2025. References to an OWASP Top 10 2022, 2023 or 2024 for web applications usually mean the 2021 list, which was current in those years.
Where are XSS, CSRF and SSRF in the OWASP Top 10 2025?
Cross-site scripting (CWE-79) is part of A05 Injection, because the browser is the interpreter that executes the injected script. Cross-site request forgery (CWE-352) and server-side request forgery (CWE-918) both map to A01 Broken Access Control. SSRF had its own category in 2021 and was rolled into A01 for 2025.
Does a penetration test cover the OWASP Top 10?
A web application penetration test checks most of the ten categories directly, provided the tester has accounts for every role. OWASP says insecure design is beyond the scope of most forms of testing and that logging and alerting can only be partly verified by testers, so those categories also need design review and operational evidence. OWASP discourages any claim of full coverage of the Top 10.
Can a scanner or a WAF cover the OWASP Top 10?
Not fully. OWASP states that tools cannot comprehensively detect, test or protect against the Top 10 because of the nature of several of the risks, naming insecure design as the example. Scanners find known vulnerable components, many injection flaws and common misconfigurations. Broken access control, business logic and authentication flows depend on knowing which user may do what, so they need penetration testers working with several accounts.
How much does an OWASP Top 10 penetration test cost?
It depends on scope: applications, user roles, API endpoints and source access. For one web application and associated APIs, Stingrai's Hybrid Pentest, where Snipe and certified penetration testers test the same application, is US$6,800 per assessment, or US$1,275 per month on a 12-month plan for continuous testing. The Autonomous Pentest by Snipe alone is US$3,000 per assessment. Larger scopes are quoted through the Get a Quote form.
Is the OWASP Top 10 a compliance standard?
No. OWASP calls the Top 10 primarily an awareness document and says that as a coding or testing standard it is the bare minimum and just a starting point; for a verifiable standard it recommends ASVS. PCI DSS Requirement 6.2.4 lists similar attack classes without naming OWASP, while the PCI Security Standards Council's penetration testing guidance refers to the OWASP Top 10.
Related reading
IDOR Vulnerability: Real Examples, How Testers Find It and How to Fix It
Cross-Site Scripting (XSS): Real Examples, How Testers Find It and How to Fix It
Server-Side Request Forgery (SSRF): Real Examples, How Testers Find It and How to Fix It
DAST vs Penetration Testing (2026): What Each Finds and Where Hybrid Fits
Web Application Security Assessment (2026): Testing Methods, Scope and Cost
References
OWASP. OWASP Top 10:2025: Introduction, About OWASP, What are Application Security Risks?, Establishing a Modern Application Security Program, Next Steps and category pages A01 to A10.
OWASP. OWASP Top 10:2021: Introduction and category pages A01 to A10.
OWASP. OWASP Top 10 project page, project repository, ASVS 5.0.0 and Web Security Testing Guide v4.2.
PCI Security Standards Council. PCI DSS v4.0.1, Requirements 6.2.4 and 11.4.1 (document library), and Penetration Testing Guidance, version 1.1, September 2017.
Paradox. Responsible Security Update, 9 July 2025, and Ian Carroll and Sam Curry. Would you like an IDOR with that?, 2025.
NSA and CISA. Red and Blue Teams Share Top Ten Cybersecurity Misconfigurations (AA23-278A), 5 October 2023.
CISA. Widespread Supply Chain Compromise Impacting npm Ecosystem, 23 September 2025.
Microsoft Threat Intelligence. Code injection attacks using publicly disclosed ASP.NET machine keys, 6 February 2025.
CISA and FBI. CL0P Ransomware Gang Exploits CVE-2023-34362 MOVEit Vulnerability (AA23-158A), 7 June 2023, and Secure by Design Alert: Eliminating SQL Injection Vulnerabilities in Software, 25 March 2024.
Internal Revenue Service. IRS Statement on the "Get Transcript" Application, 26 May 2015, and IRS Statement on "Get Transcript", 26 February 2016.
Information Commissioner's Office. 23andMe fined £2.31 million, 17 June 2025, and Penalty Notice: British Airways plc, 16 October 2020.
The React Team. Critical Security Vulnerability in React Server Components, 3 December 2025, and NIST. NVD record for CVE-2025-55182.
Cloudflare. Cloudflare outage on November 18, 2025, 18 November 2025.
Stingrai. State of Penetration Testing 2026 and pricing.
Talk to Stingrai
Stingrai's certified penetration testers test web applications and APIs against the OWASP Top 10 and ASVS, one-time or continuously. Get a Quote or book a free discovery call.