A PCI DSS compliance audit is an assessment of the cardholder data environment against the Payment Card Industry Data Security Standard, and in October 2026 that standard is still PCI DSS v4.0.1, published by the PCI Security Standards Council (PCI SSC) in June 2024. The Council's own definition of the work is short: it intends PCI DSS for "all entities that store, process, or transmit cardholder data (CHD) and/or sensitive authentication data (SAD) or could impact the security" of that data, and it describes the assessment in six steps, from confirming scope to remediating anything not in place.
What the standard leaves to others is who has to be audited and how. Whether an entity must validate compliance, and whether it does so through a Qualified Security Assessor's Report on Compliance or a Self-Assessment Questionnaire, is decided by the payment brands and acquirers (PCI SSC FAQ 1473). This guide is written for mid-market merchants and service providers in the United States and Canada preparing for that assessment: what the audit is, who needs a QSA, the process step by step with a realistic calendar, what the assessor tests, how to prepare, how to remediate findings, what it costs where a published figure exists, and where the annual penetration test under Requirement 11.4 fits.
Every requirement quoted here comes from PCI SSC's own documents, and every brand rule from the brand's own page, linked inline.
Quick answer. A PCI DSS compliance audit (PCI SSC calls it an assessment) validates every applicable PCI DSS v4.0.1 requirement and ends in a Report on Compliance or a Self-Assessment Questionnaire plus an Attestation of Compliance. Card brands set who needs a QSA: Visa Level 1 merchants process over 6 million Visa transactions a year and file an annual ROC. The six steps are confirm scope, assess, complete the report, complete the AOC, submit, and remediate if required. Stingrai's certified penetration testers deliver the Requirement 11.4 internal, external and segmentation tests, with retesting, that the assessor examines as evidence.
Key takeaways
PCI DSS has no certificate. PCI SSC states that "the only documentation recognized for PCI DSS validation are the official form documents from the PCI SSC website" (FAQ 1220). The outputs of an audit are a ROC or an SAQ and an AOC.
Your level comes from your acquirer and the brands. Visa, Mastercard and Canadian acquirers such as Moneris publish their own thresholds; PCI DSS itself sets none.
The 2025 deadline has passed. Requirements such as 5.4.1 (phishing), 6.4.3 (payment page scripts), 8.4.2 (MFA into the CDE), 10.4.1.1 (automated log reviews) and 11.6.1 (tamper detection) were best practices until 31 March 2025 and are now assessed like any other requirement.
Clocks decide audit readiness. Quarterly scans, annual penetration tests, segmentation tests and scope confirmation all have minimum frequencies, and a cycle missed through oversight leaves the requirement not in place until the schedule is re-established.
A finding is not a failure until the report is final. Controls that are not yet implemented or are scheduled for a future date are not in place, but once the entity fixes them "the assessor will reassess to validate that the remediation is completed" (PCI DSS v4.0.1, section 12).
What a PCI DSS compliance audit is
The standard and its current version
PCI DSS is owned by the PCI Security Standards Council, which was "founded in 2006 by American Express, Discover, JCB International, MasterCard and Visa Inc." (PCI SSC). The current standard is Payment Card Industry Data Security Standard: Requirements and Testing Procedures, v4.0.1, dated June 2024. Its version table lists v4.0 as retired on 31 December 2024 and v3.2.1 as retired on 31 March 2024, and the PCI SSC Document Library still lists v4.0.1 as the standard in October 2026.
The phrase "PCI audit" is common, but PCI SSC's term is assessment. The work is the same: an assessor tests each applicable requirement and documents the result.
Who performs it
Qualified Security Assessor (QSA). The glossary in PCI DSS v4.0.1 says "QSA companies are qualified by PCI SSC to validate an entity's adherence to PCI DSS requirements". The Council describes them as "independent security organizations" (PCI SSC).
Internal Security Assessor (ISA). ISAs "receive PCI SSC training to perform internal assessments for their organization". Some brand programs accept an ISA where they would otherwise require a QSA.
The entity itself. Eligible merchants and service providers complete a Self-Assessment Questionnaire.
What the audit produces
The standard's glossary defines the three documents that matter:
Document | PCI SSC definition | Who completes it |
|---|---|---|
Report on Compliance (ROC) | "Reporting tool used to document detailed results from an entity's PCI DSS assessment." | The assessor, on the PCI SSC ROC Template |
Self-Assessment Questionnaire (SAQ) | "Reporting tool used to document self-assessment results from an entity's PCI DSS assessment." | The entity, using the SAQ that fits its environment |
Attestation of Compliance (AOC) | "The official PCI SSC form for merchants and service providers to attest to the results of a PCI DSS assessment" | The entity, signed as the brand programs require |
Is there a PCI DSS certification?
No document called a PCI DSS certificate is recognized. PCI SSC's FAQ 1220 answers "Are compliance certificates recognized for PCI DSS validation?" with "No", and a September 2025 PCI SSC blog post adds that any other certificate "is not from the Council nor is it an official verification of PCI DSS compliance". When buyers search for the "PCI DSS certification process", what they need is the validation process below, ending in an AOC on the official form.
Who needs a QSA Report on Compliance and who can self-assess
The rule comes from the brands and acquirers
PCI SSC's FAQ 1473 is explicit: "Compliance-accepting entities (typically, payment brands and acquirers) are responsible for determining the PCI DSS validation and reporting methods of their merchants and service providers, including how compliance is to be evidenced", for example a ROC or an SAQ. For small merchants, "whether a small merchant is required to validate compliance is determined by the individual payment brands" (PCI SSC). Your acquirer (merchant bank) is the first call.
Visa and Mastercard levels
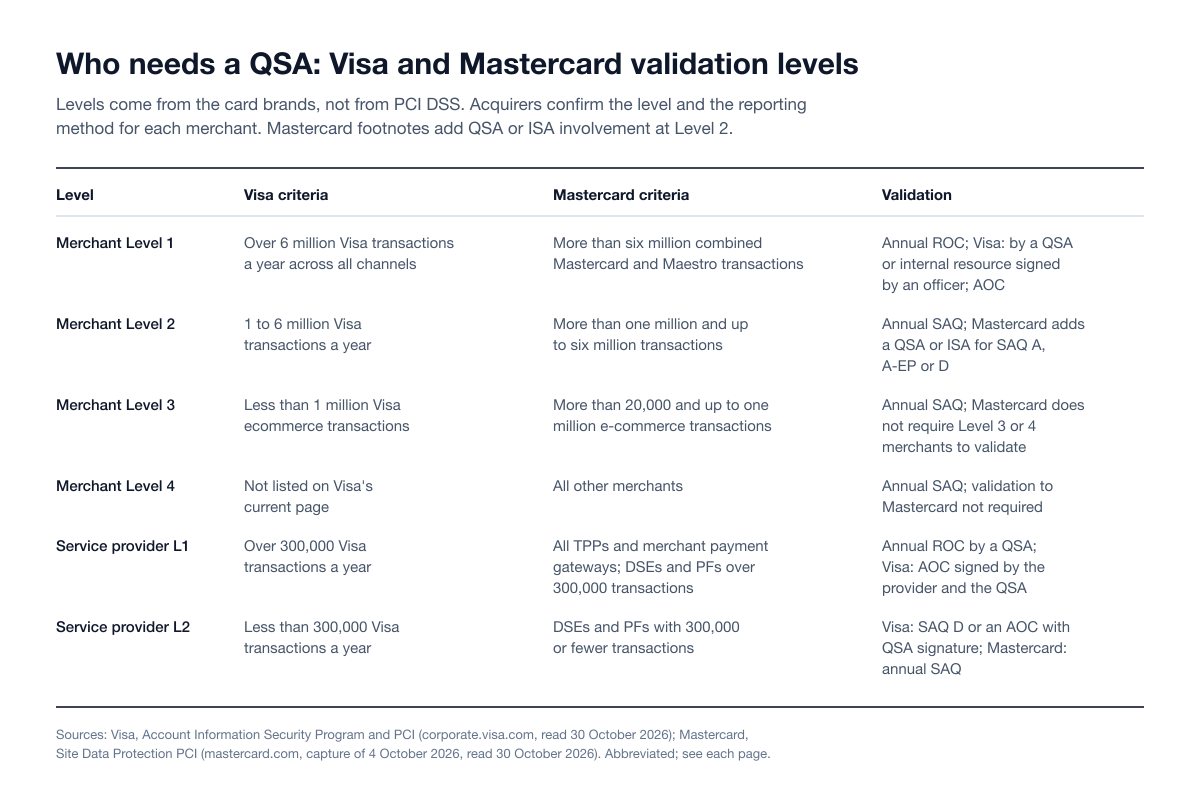
Figure 1: Visa and Mastercard validation levels for merchants and service providers, abbreviated. Sources: Visa, Account Information Security Program and PCI; Mastercard, Site Data Protection.
Visa merchants. Visa's current page lists three levels. Level 1 is "Merchants processing over 6 million Visa transactions annually across all channels or Global merchants identified as Level 1 by any Visa region", who every year file a ROC "by Qualified Security Assessor" or "internal resource if signed by officer of the company" and submit an AOC. Level 2 (1 to 6 million) and Level 3 (less than 1 million Visa ecommerce transactions) complete an annual SAQ. Visa counts volume "in one country or with one acquirer per year".
Mastercard merchants. Level 1 is "more than six million total combined Mastercard and Maestro transactions annually" or any merchant meeting Visa's Level 1 criteria, with a ROC signed by a QSA, an ISA or, unless prohibited, an executive officer. Level 2 is more than one million and up to six million. Mastercard adds that "Level 2 merchants completing SAQ A, SAQ A-EP or SAQ D must additionally engage a PCI SSC-approved QSA or PCI SSC-certified ISA for compliance validation". Level 3 covers more than 20,000 and up to one million e-commerce transactions, and Level 4 all other merchants. Mastercard measures volume over "the most recent 52-week period".
Service providers. Visa puts "VisaNet® processors or any service provider that stores, processes and/or transmits over 300,000 Visa transactions annually" at Level 1, with an annual on-site assessment and an AOC "signed by both the service provider and the qualified security assessor (QSA)". Below 300,000, Visa accepts a signed SAQ D or an AOC with a QSA signature, but "PCI DSS compliance validation by a QSA is required before a service provider can be listed on the Visa Global Registry of Service Providers". Mastercard places all third-party processors and merchant payment gateways at Level 1 with an annual ROC by a QSA.
Canadian merchants
Canadian acquirers restate the brand structure for their merchants. Moneris publishes four levels "on one card type": Level 1 over six million transactions with an annual ROC "validated with a Qualified Security Assessor (QSA)"; Level 2 over one million and under six million with an annual SAQ validated with an ISA or QSA; Levels 3 and 4 with an annual SAQ. Every Moneris level also lists an annual AOC and "Quarterly Network Vulnerability Scans by an Approved Scanning Vendor (ASV)". Moneris notes that criteria "may vary by Payment Card Network".
The PCI DSS audit process, step by step
PCI DSS v4.0.1, section 12, lists the assessment process in six steps. The two preparation steps in front of them are where most of the work sits.
Confirm your validation path. Ask your acquirer, or the customers who request your AOC if you are a service provider, for your level, whether you need a ROC or an SAQ, and which SAQ. Engage a QSA early if a ROC or QSA-validated SAQ is required.
Confirm and document scope. Requirement 12.5.2 requires the entity to document and confirm scope "at least once every 12 months and upon significant change", including all data flows for every payment stage and acceptance channel and updated data-flow diagrams per Requirement 1.2.4. Service providers do this every six months (12.5.2.1). The standard calls this "the first step in preparing for a PCI DSS assessment".
Confirm the scope of the assessment with the assessor. This is PCI SSC's step 1. "For each PCI DSS assessment, the assessor validates that the entity accurately defined and documented the scope."
Perform the assessment. PCI SSC's step 2. The assessor tests each applicable requirement using three methods defined in section 10 of the standard: examine evidence, observe actions or systems, and interview personnel.
Complete the report. PCI SSC's step 3: the ROC on the PCI SSC ROC Template, or the applicable SAQ.
Complete the Attestation of Compliance. PCI SSC's step 4: the AOC for merchants or service providers, "in its entirety". The standard notes that official AOCs "are only available on the PCI SSC website".
Submit. PCI SSC's step 5: send the report, the AOC and other requested documents, "such as ASV scan reports", to the requesting organization: brands and acquirers for merchants, or customers and other requesters for service providers.
Remediate if required. PCI SSC's step 6: "If required, perform remediation to address requirements that are not in place and provide an updated report."
A realistic PCI DSS audit timeline
PCI DSS sets no duration for an assessment. It sets clocks: activities that must already have happened, on schedule, by the time the assessor looks. The calendar below is Stingrai's planning recommendation for a first Report on Compliance at a mid-market merchant or service provider, built around those clocks. It is a planning aid, not a PCI SSC rule; your QSA's fieldwork plan and your scope decide the real dates.
When (before fieldwork) | What to finish | Requirement clock it serves |
|---|---|---|
Six months or more | Validation path confirmed with the acquirer; QSA engaged; scope and data-flow diagrams confirmed | 12.5.2 (12 months), 12.5.2.1 (six months for service providers) |
Four to six months | Gap assessment against all 12 requirements, including the requirements that became mandatory on 31 March 2025 | All applicable requirements |
Three to four months | Internal, external and segmentation penetration tests completed, so fixes and the repeat test land before fieldwork | 11.4.2, 11.4.3, 11.4.5 (12 months), 11.4.6 (six months), 11.4.4 retest |
Every quarter, year round | Internal scans and ASV external scans, with rescans until passing | 11.3.1 and 11.3.2 (every three months) |
One to two months | Evidence pack assembled: policies, targeted risk analyses, logs, change records, TPSP monitoring, training records | 12.3.1, 12.8.4, 12.6 and others |
Fieldwork | Examine, observe and interview sessions with the assessor | Section 10 testing methods |
After fieldwork | ROC or SAQ and AOC completed and submitted; remediation and reassessment if anything is not in place | Section 12, steps 3 to 6 |
Two timing rules in the standard matter most for a first audit. An activity required every three months "must have been performed at least four times during the previous year at an interval that does not exceed 90-92 days" in years after the initial assessment. For an initial assessment, PCI DSS does not require four passing ASV scans within 12 months if the most recent scan passed, scanning procedures are documented, and vulnerabilities were corrected and rescanned (Requirement 11.3.2 applicability notes).
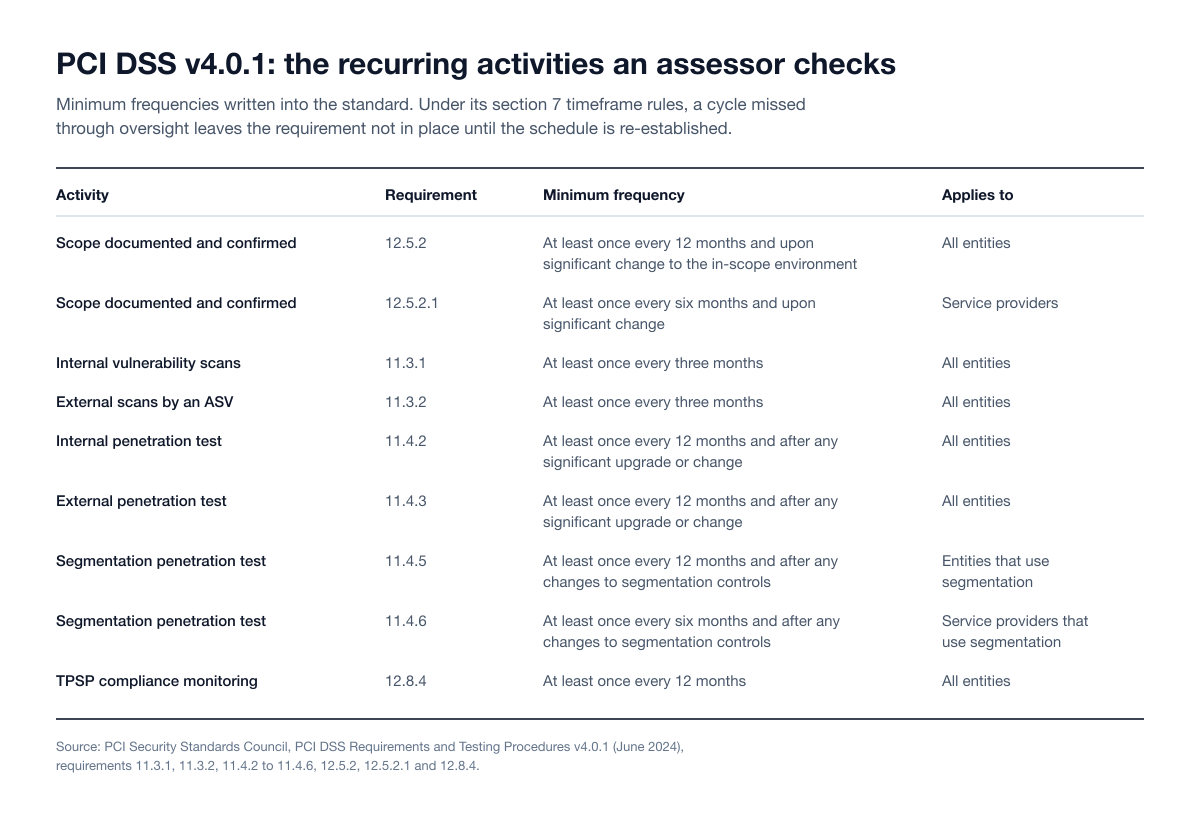
Figure 2: Recurring PCI DSS v4.0.1 activities and their minimum frequencies. Source: PCI SSC, PCI DSS v4.0.1 Requirements and Testing Procedures.
PCI DSS audit requirements: what the QSA tests
The 12 requirements, by goal
The assessor works through every applicable requirement in the standard's 12 principal requirements, grouped under six goals in Table 1 of PCI DSS v4.0.1.
Goal | Principal requirement (PCI DSS v4.0.1 wording) |
|---|---|
Build and Maintain a Secure Network and Systems | 1. Install and Maintain Network Security Controls. 2. Apply Secure Configurations to All System Components. |
Protect Account Data | 3. Protect Stored Account Data. 4. Protect Cardholder Data with Strong Cryptography During Transmission Over Open, Public Networks. |
Maintain a Vulnerability Management Program | 5. Protect All Systems and Networks from Malicious Software. 6. Develop and Maintain Secure Systems and Software. |
Implement Strong Access Control Measures | 7. Restrict Access to System Components and Cardholder Data by Business Need to Know. 8. Identify Users and Authenticate Access to System Components. 9. Restrict Physical Access to Cardholder Data. |
Regularly Monitor and Test Networks | 10. Log and Monitor All Access to System Components and Cardholder Data. 11. Test Security of Systems and Networks Regularly. |
Maintain an Information Security Policy | 12. Support Information Security with Organizational Policies and Programs. |
How the assessor tests
Section 10 of the standard defines three testing methods. Examine: "The assessor critically evaluates data evidence", such as documents, screenshots, configuration files and audit logs. Observe: "The assessor watches an action or views something in the environment." Interview: "The assessor converses with individual personnel." Every defined-approach requirement has testing procedures built from these methods, so evidence that is easy to examine and staff who can explain their process shorten fieldwork.
An assessor will not accept a "Not Applicable" answer on trust either. FAQ 1473 says the assessor "must first confirm through testing that the requirement is truly not applicable to that environment".
Defined approach, customized approach and compensating controls
PCI DSS v4.0.1 allows two ways to meet and validate a requirement. The defined approach follows the written requirement and testing procedure. The customized approach lets an entity meet a requirement's stated objective another way; the standard says it "is intended for risk-mature entities that demonstrate a robust risk-management approach to security", and the assessor derives the testing. Under the defined approach, an entity with a documented constraint may use compensating controls, which "on an annual basis" must be documented by the entity, validated by the assessor and included with the ROC.
The requirements that became mandatory on 31 March 2025
PCI DSS v4.0 introduced future-dated requirements, each carrying the note that it "is a best practice until 31 March 2025, after which it will be required and must be fully considered during a PCI DSS assessment". Audits in 2026 test them in full. Among those most likely to surface gaps:
5.4.1: "Processes and automated mechanisms are in place to detect and protect personnel against phishing attacks."
6.4.3: "All payment page scripts that are loaded and executed in the consumer's browser are managed", with a method to confirm each script is authorized and to assure its integrity.
8.4.2: "MFA is implemented for all non-console access into the CDE."
10.4.1.1: "Automated mechanisms are used to perform audit log reviews."
11.3.1.1: internal scan vulnerabilities not ranked high-risk or critical are "addressed based on the risk defined in the entity's targeted risk analysis".
11.6.1: "A change- and tamper-detection mechanism is deployed" to alert on unauthorized changes to payment page HTTP headers and script contents.
12.3.1: each targeted risk analysis the standard calls for is documented.
12.5.2.1: service providers confirm scope every six months.
E-commerce merchants on SAQ A should note one change. In January 2025 PCI SSC removed 6.4.3, 11.6.1 and 12.3.1 from SAQ A and added an eligibility criterion that merchants "confirm their site is not susceptible to attacks from scripts that could affect the merchant's e-commerce system(s)", effective 31 March 2025. The Council adds that the change does "not remove or diminish the underlying requirements within PCI DSS".
Where the annual penetration test fits: Requirement 11.4
Requirement 11.4 of PCI DSS v4.0.1 reads: "External and internal penetration testing is regularly performed, and exploitable vulnerabilities and security weaknesses are corrected." It sits under principal requirement 11, so a full Report on Compliance assesses it. Its sub-requirements set what the assessor checks:
11.4.1, methodology. A defined, documented and implemented methodology with nine elements: industry-accepted approaches; "coverage for the entire CDE perimeter and critical systems"; testing from both inside and outside the network; testing to validate segmentation and scope-reduction controls; application-layer testing for at least the vulnerabilities in Requirement 6.2.4; network-layer testing of network components and operating systems; review of threats and vulnerabilities from the last 12 months; a documented approach to the risk of exploitable findings; and "retention of penetration testing results and remediation activities results for at least 12 months".
11.4.2 and 11.4.3, internal and external tests. Each is performed "at least once every 12 months", "after any significant infrastructure or application upgrade or change", "by a qualified internal resource or qualified external third-party", and with "organizational independence of the tester" ("not required to be a QSA or ASV").
11.4.4, correct and retest. Exploitable findings are corrected according to the entity's risk ranking under Requirement 6.3.1, and "penetration testing is repeated to verify the corrections".
11.4.5, segmentation. If segmentation isolates the CDE, it is tested "at least once every 12 months and after any changes to segmentation controls/methods", covering every method in use and confirming the controls "isolate the CDE from all out-of-scope systems".
11.4.6 and 11.4.7, service providers. Service providers test segmentation "at least once every six months", and multi-tenant service providers "support their customers for external penetration testing".
Penetration testing is not ASV scanning
Requirement 11.3.2 requires external vulnerability scans "at least once every three months" by "a PCI SSC Approved Scanning Vendor (ASV)", a company "approved by the PCI SSC to conduct external vulnerability scanning services". Those scans are a separate control. A clean ASV scan does not satisfy 11.4, and a penetration test does not replace the quarterly scans.
Which SAQs include penetration testing
Self-assessing merchants carry different parts of 11.4 depending on their SAQ. From the v4.0.1 SAQs (October 2024; SAQ A revised January 2025):
SAQ | 11.4 items included |
|---|---|
SAQ A | None |
SAQ A-EP | 11.4.1, 11.4.3, 11.4.4, 11.4.5 |
SAQ B, SAQ C-VT, SAQ P2PE, SAQ SPoC | None |
SAQ B-IP, SAQ C | 11.4.5 (segmentation, if used) |
SAQ D for Merchants | 11.4.1 to 11.4.5 (11.4.6 and 11.4.7 apply only to service providers) |
Report on Compliance (full assessment) | All of 11.4 that applies to the entity |
For the deeper treatment of scope, cadence and tester qualification, see our guide to PCI DSS penetration testing under Requirement 11.4.
How to prepare for a PCI DSS audit: checklist
PCI DSS audit preparation is mostly about having evidence that already exists, dated and complete, before the assessor asks for it.
Validation path in writing. Your level, ROC or SAQ, SAQ type, and whether a QSA or ISA must validate, confirmed by your acquirer or requesting customer.
Scope package. The 12.5.2 scope confirmation, data-flow diagrams for every payment stage and channel, an inventory of in-scope system components, and the list of third-party service providers (12.8.1).
Segmentation evidence. Network diagrams, firewall and security group rules, and a segmentation penetration test that covers every method in use. Without adequate segmentation, the standard says, "the entire network is in scope".
Penetration test pack. The 11.4.1 methodology, internal and external test reports from the last 12 months, the segmentation test, and retest evidence for every exploitable finding.
Four quarters of scans. Passing ASV scan reports and internal scan results with rescans, or the initial-assessment conditions if this is your first ROC.
Targeted risk analyses. One for each requirement that calls for one under 12.3.1, including the one behind 11.3.1.1 and, if 11.6.1 checks run less often than weekly, the one behind 11.6.1.
Payment page controls. A script inventory with authorization and integrity checks (6.4.3) and a change- and tamper-detection mechanism (11.6.1) for e-commerce pages.
Identity evidence. MFA for all non-console access into the CDE (8.4.2) and access reviews.
Logging evidence. Automated audit log review (10.4.1.1) and retained logs the assessor can sample.
Policies and people. Current policies, the security awareness program (12.6.1) including phishing (5.4.1), incident response plan (12.10.1), and staff ready to be interviewed.
Third-party evidence. Current AOCs from service providers and the program that monitors their compliance at least once every 12 months (12.8.4).
A dry run. Walk a sample of requirements through examine, observe and interview before the QSA arrives.
PCI DSS audit findings: how to find gaps and remediate them
How to audit your own systems for non-compliance
The fastest way to find every gap before an assessor does is to test yourself the way the assessor will:
Start from scope, not controls. Re-run the 12.5.2 scoping exercise against reality: every payment channel, every data flow, every system that is connected to or could impact the CDE, including "backup/recovery sites and fail-over systems".
Test every applicable requirement by its own testing procedure. The defined-approach testing procedures in PCI DSS v4.0.1 say exactly what will be examined, observed or interviewed.
Check the clocks first. Missed quarterly scans, an expired annual penetration test or a segmentation test that skipped a method are the gaps that cannot be fixed by writing a document.
Test the controls, not only the paperwork. A penetration test that follows 11.4.1, including segmentation testing, shows whether controls actually isolate the CDE and resist exploitation.
Use PCI SSC's Prioritized Approach. The standard lists the Prioritized Approach for PCI DSS among the Council's resources for sequencing remediation.
Where findings come from
The structure of the standard predicts where gaps appear:
Source of findings | What it looks like | Remediation |
|---|---|---|
Scope gaps | A channel, integration or connected system missing from the scope documentation | Re-run 12.5.2, update data-flow diagrams (1.2.4), bring the system in or segment it and test the segmentation (11.4.5) |
Missed clocks | A quarter without a passing ASV scan, or no penetration test after a significant change | Document the process, re-establish the schedule and perform the activity, as section 7 of the standard requires |
Penetration test gaps | Methodology missing one of the nine 11.4.1 elements, no application-layer testing, no repeat test | Update the methodology, test the missing layer, retest every corrected finding (11.4.4) |
Requirements mandatory since March 2025 | No script inventory, no tamper detection, MFA only at the perimeter, manual log reviews | Implement 6.4.3, 11.6.1, 8.4.2 and 10.4.1.1, with a targeted risk analysis where 12.3.1 applies |
Third parties | Expired or missing service provider AOCs | Collect current AOCs and run the 12.8.4 monitoring program |
Best practices for remediating PCI DSS audit findings
Rank by risk. Requirement 6.3.1 has vulnerabilities "assigned a risk ranking based on industry best practices and consideration of potential impact"; fix critical and high-risk items first.
Fix, then prove the fix. For penetration test findings, 11.4.4 requires that "penetration testing is repeated to verify the corrections". For scans, rescan until passing.
Do not report future work as done. PCI DSS requirements "are not considered to be in place if controls are not yet implemented or are scheduled to be completed at a future date".
Use compensating controls only for real constraints, documented annually and validated by the assessor.
Ask for reassessment. "After any open or not-in-place items are addressed by the entity, the assessor will reassess to validate that the remediation is completed", and the entity provides an updated report (section 12, step 6).
Keep the records. 11.4.1 requires penetration testing results and remediation results to be retained for at least 12 months, which is also the evidence the next audit starts from.
How much does a PCI DSS audit cost?
PCI SSC publishes no price for an assessment. One QSA company, SecurityMetrics, publishes planning figures: "a qualified security assessment from a PCI-certified QSA costs on average around $15,000"; a very large enterprise should "expect to pay $70,000+ in total costs", including an onsite audit of "around $40,000" and penetration testing of "around $15,000"; and a small business "should cost from $300 per year". These are one vendor's published estimates, not a market survey, and its own figures vary with environment.
The cost of not validating is set by the brands. Visa states that if a merchant or service provider "does not comply with the PCI DSS or fails to rectify a security issue, Visa may assess a non-compliance assessment to the issuer or acquirer" (Visa).
For the testing line of the budget, Stingrai's Hybrid Pentest is US$6,800 for one web application and associated APIs, with a human-validated report and an attestation letter (pricing). Internal and external network tests, segmentation testing and multi-application scopes are quoted through Get a Quote, and our penetration testing cost guide and cost calculator cover the drivers.
Where Stingrai fits in your PCI DSS audit
Stingrai is a CREST-accredited penetration testing company, accredited for both Penetration Testing and AI-Enabled Penetration Testing, offering fully human-led and hybrid (human penetration testers plus AI agents) penetration tests, delivered by experienced penetration testers who are also world-class security researchers and bug bounty hunters, with OSCE³, OSWE, OSEP and CREST CRT certifications across the team. Founded in Toronto, Canada in 2021, it is trusted by companies from startups to enterprises to meet audit requirements for SOC 2, ISO 27001, CMMC, PCI DSS and HIPAA, with engagements across web, API, mobile, AI and LLM, cloud, network, Active Directory and social engineering penetration tests and red team engagements.
For a PCI DSS audit, Stingrai's testing produces the Requirement 11.4 evidence your QSA examines:
Internal and external penetration tests (11.4.2, 11.4.3) of the CDE perimeter, critical systems and the network and application layers, by an organizationally independent external firm, every 12 months and after significant change.
Segmentation testing (11.4.5, 11.4.6) of every segmentation method in use, annually for merchants and every six months for service providers.
Retesting (11.4.4) of remediated findings, included, so the repeat test the standard requires is in the same record.
A methodology that follows PTES, NIST, OSSTMM and OWASP and maps to PCI DSS Requirement 11.4, with two named penetration testers from a team holding OSCE³, OSWE, OSEP, CREST CRT and CISSP certifications on every human-led engagement.
Findings as they are confirmed. Every finding is posted to the PTaaS portal with a proof of concept and prioritized remediation guidance, with Jira and Slack integration, so fixing starts during the test. Every human-led and hybrid report ships with an attestation letter.
Engagements run as one-time annual tests or continuous programs. For a payment application, the Hybrid Pentest pairs Snipe, Stingrai's autonomous agent for web applications and associated APIs, with certified penetration testers working together throughout; see web application penetration testing and internal and external network penetration testing.
Frequently Asked Questions
What is a PCI DSS compliance audit?
A PCI DSS compliance audit is an assessment of an organization's cardholder data environment against every applicable requirement of PCI DSS v4.0.1, the current version of the standard. A Qualified Security Assessor, an Internal Security Assessor or the organization itself performs it, and the result is documented in a Report on Compliance or a Self-Assessment Questionnaire plus an Attestation of Compliance on PCI SSC's official forms.
Who needs a PCI DSS audit by a QSA?
The payment brands and acquirers decide, not PCI DSS. Visa requires an annual Report on Compliance from Level 1 merchants processing over 6 million Visa transactions a year, filed by a QSA or by an internal resource if signed by an officer. Mastercard sets Level 1 at more than six million Mastercard and Maestro transactions and requires Level 2 merchants completing SAQ A, SAQ A-EP or SAQ D to engage a QSA or ISA. Visa Level 1 service providers, above 300,000 Visa transactions a year, need an annual on-site assessment with an AOC signed by the service provider and the QSA.
What are the PCI DSS audit requirements?
The audit covers the 12 principal requirements of PCI DSS v4.0.1, from network security controls (Requirement 1) to organizational policies and programs (Requirement 12), plus the appendices that apply to the entity. The assessor tests each applicable requirement by examining evidence, observing systems and processes, and interviewing staff. Requirements that were future-dated, such as 6.4.3, 8.4.2, 10.4.1.1 and 11.6.1, have been mandatory since 31 March 2025.
What are the steps of the PCI DSS audit process?
PCI DSS v4.0.1 lists six steps: confirm the scope of the assessment, perform the assessment, complete the report (ROC or SAQ), complete the Attestation of Compliance, submit the documents and any requested ASV scan reports to the requesting organization, and remediate and provide an updated report if required. Before those steps, the entity confirms its validation path with its acquirer and documents its scope under Requirement 12.5.2.
How long does a PCI DSS audit take?
PCI DSS sets no duration for the assessment itself, but it sets clocks that must already be met: scans every three months, penetration tests every 12 months and after significant change, and scope confirmation every 12 months (every six months for service providers). For a first Report on Compliance, Stingrai recommends starting about six months before fieldwork, with penetration tests finished three to four months ahead so fixes and the required retest are complete.
How do I prepare for a PCI DSS audit?
Confirm your validation path with your acquirer, document and confirm scope under Requirement 12.5.2, run a gap assessment against all 12 requirements, and complete the time-bound activities first: four quarters of scans, internal and external penetration tests, segmentation testing and retests. Then assemble the evidence pack of policies, targeted risk analyses, logs, service provider AOCs and training records, and rehearse the interviews.
Is there a PCI DSS certification?
No. PCI SSC FAQ 1220 states that the only documentation recognized for PCI DSS validation are the official forms on the PCI SSC website, and the Council says any other certificate is not an official verification of PCI DSS compliance. A PCI DSS validation ends in a Report on Compliance or a Self-Assessment Questionnaire plus an Attestation of Compliance.
How can I audit my systems to identify all areas of PCI DSS non-compliance and prioritize remediation?
Re-run the Requirement 12.5.2 scoping exercise against every payment channel and connected system, then test each applicable requirement using its own testing procedure in PCI DSS v4.0.1. Check the time-bound activities first, because missed scans or penetration tests cannot be fixed with documentation, and commission a penetration test that covers the nine 11.4.1 elements, including segmentation. Prioritize remediation by the risk ranking your Requirement 6.3.1 process assigns and use PCI SSC's Prioritized Approach to sequence the work.
What are the best practices for remediating PCI DSS audit findings?
Rank findings by risk under Requirement 6.3.1 and fix critical and high-risk items first. Prove every fix: Requirement 11.4.4 requires the penetration test to be repeated to verify corrections, and failed scans need passing rescans. Never report a control scheduled for a future date as in place, use compensating controls only for documented constraints, and ask the assessor to reassess so the report can be updated.
Does a PCI DSS audit require a penetration test?
Yes, for any entity assessed against the full standard. Requirement 11.4 states that external and internal penetration testing is regularly performed and exploitable vulnerabilities and security weaknesses are corrected, with internal and external tests at least once every 12 months and after significant change, and segmentation tests where segmentation is used. Among self-assessment questionnaires, SAQ A-EP, SAQ B-IP, SAQ C and SAQ D include parts of 11.4, while SAQ A includes none.
How much does a PCI DSS audit cost?
PCI SSC publishes no price, and the fee depends on the organization's size and environment. SecurityMetrics, a QSA company, publishes an average of around US$15,000 for a QSA assessment and US$70,000 or more in total costs for a very large enterprise, including an onsite audit of around US$40,000 and penetration testing of around US$15,000. Stingrai's Hybrid Pentest is US$6,800 for one web application and associated APIs.
What is the difference between a ROC, an SAQ and an AOC?
A Report on Compliance documents detailed results from an entity's PCI DSS assessment, completed by the assessor on PCI SSC's ROC Template. A Self-Assessment Questionnaire documents an eligible entity's own self-assessment results. The Attestation of Compliance is the official PCI SSC form a merchant or service provider uses to attest to the results documented in the ROC or SAQ, and it is submitted to the brands, acquirers or customers that request it.
Related reading
PCI DSS penetration testing: Requirement 11.4 explained (2026)
Pentest evidence auditors accept for SOC 2, ISO 27001, PCI DSS and CMMC
References
PCI Security Standards Council. Payment Card Industry Data Security Standard: Requirements and Testing Procedures, v4.0.1. June 2024. https://www.pcisecuritystandards.org/document_library/. The standard: scope, assessment process (section 12), testing methods (section 10), timeframes (section 7) and every requirement quoted here.
PCI Security Standards Council. FAQ 1473: What is the role of compliance-accepting entities and assessors in determining the applicability of PCI DSS requirements for merchant and service provider PCI DSS assessments? https://www.pcisecuritystandards.org/faqs/1473/. Brands and acquirers set validation and reporting methods.
PCI Security Standards Council. FAQ 1220: Are compliance certificates recognized for PCI DSS validation? https://www.pcisecuritystandards.org/faqs/1220/. Only official PCI SSC forms count.
PCI Security Standards Council. Beware of PCI DSS Compliance Certificates. 2 September 2025. https://blog.pcisecuritystandards.org/beware-of-pci-dss-compliance-certificates. The Council provides no certificates or logos.
PCI Security Standards Council. Important Updates Announced for Merchants Validating to Self-Assessment Questionnaire A. 30 January 2025. https://blog.pcisecuritystandards.org/important-updates-announced-for-merchants-validating-to-self-assessment-questionnaire-a. SAQ A changes effective 31 March 2025.
PCI Security Standards Council. PCI DSS v4.0.1 Self-Assessment Questionnaires. October 2024 (SAQ A revised January 2025). https://www.pcisecuritystandards.org/document_library/. Source of the 11.4 coverage by SAQ.
PCI Security Standards Council. PCI Data Security Standard (PCI DSS), Merchants and About Us pages. https://www.pcisecuritystandards.org/standards/pci-dss/. QSA and ISA roles, small merchant validation, founding members.
Visa. Account Information Security (AIS) Program and PCI. https://corporate.visa.com/en/resources/security-compliance.html. Visa merchant and service provider levels, validation and non-compliance assessments.
Mastercard. Site Data Protection (SDP) Program and PCI. https://www.mastercard.com/us/en/business/cybersecurity-fraud-prevention/site-data-protection-pci.html. Mastercard merchant and service provider levels and footnotes.
Moneris. PCI Data Security. https://www.moneris.com/en/support/compliance-and-security/pci-data-security. A Canadian acquirer's merchant levels and validation requirements.
SecurityMetrics. How Much Does PCI Compliance Cost? Gary Glover. Read 30 October 2026. https://www.securitymetrics.com/blog/how-much-does-pci-compliance-cost. A QSA company's published cost estimates.
Stingrai. Plans and Pricing. https://www.stingrai.io/pricing. Fixed prices for one web application and associated APIs.
Talk to Stingrai
Planning your PCI DSS audit and need the Requirement 11.4 penetration tests and segmentation testing done before fieldwork? Get a Quote or book a free discovery call.